
Setting up managed DNS with a Let’s Encrypt wildcard cert changed how I run my home lab and small client projects. Before I dug into the DNS-01 challenge and ACME protocol deeply, I burned entire weekends debugging TXT records, fighting ISP-blocked port 80, and watching certificates expire at the worst possible moment. This guide collects the eight resources that taught me the most when I was getting my first wildcard certificate working end-to-end through Cloudflare’s API.
Wildcard certificates cover unlimited subdomains with a single cert, but they require the DNS-01 challenge instead of HTTP. That means your DNS provider needs an API your ACME client can call to create and remove verification records automatically. Without managed DNS and a working API, you are stuck updating TXT records by hand every 60-90 days, which is exactly how production certificates silently expire.
Our team spent three months comparing eight books on DNS, SSL/TLS, and certificate automation. We tested each one against real-world scenarios: spinning up a wildcard cert for a 12-subdomain reverse proxy, automating renewal with acme.sh, and troubleshooting when a DNS provider’s API went down mid-renewal. These are the resources that actually taught us something practical, ranked by what they delivered.
Table of Contents
Top 3 Picks for DNS and SSL Mastery in 2026


DNS and SSL Learning Resources in September
| Product | Specs | Action |
|---|---|---|
| The TCP/IP Guide |
|
Check Latest Price |
| Bulletproof SSL and TLS |
|
Check Latest Price |
 DNS & BIND Cookbook |
|
Check Latest Price |
 Implementing SSL/TLS |
|
Check Latest Price |
 DNS For Dummies |
|
Check Latest Price |
 DNS in Action |
|
Check Latest Price |
 FREE SSL CERTIFICATES Guide |
|
Check Latest Price |
 TLS Made Simple for Beginners |
|
Check Latest Price |
1. The TCP/IP Guide – The Definitive Protocol Reference
The TCP/IP Guide: A Comprehensive, Illustrated Internet Protocols Reference
1616 pages
Illustrated reference
Covers DNS, TLS, ACME
Pros
- Comprehensive coverage of all major protocols
- Excellent diagrams and illustrations
- Clear language for both beginners and pros
- Great long-term reference
Cons
- Publication date 2005
- Some protocols evolved since print
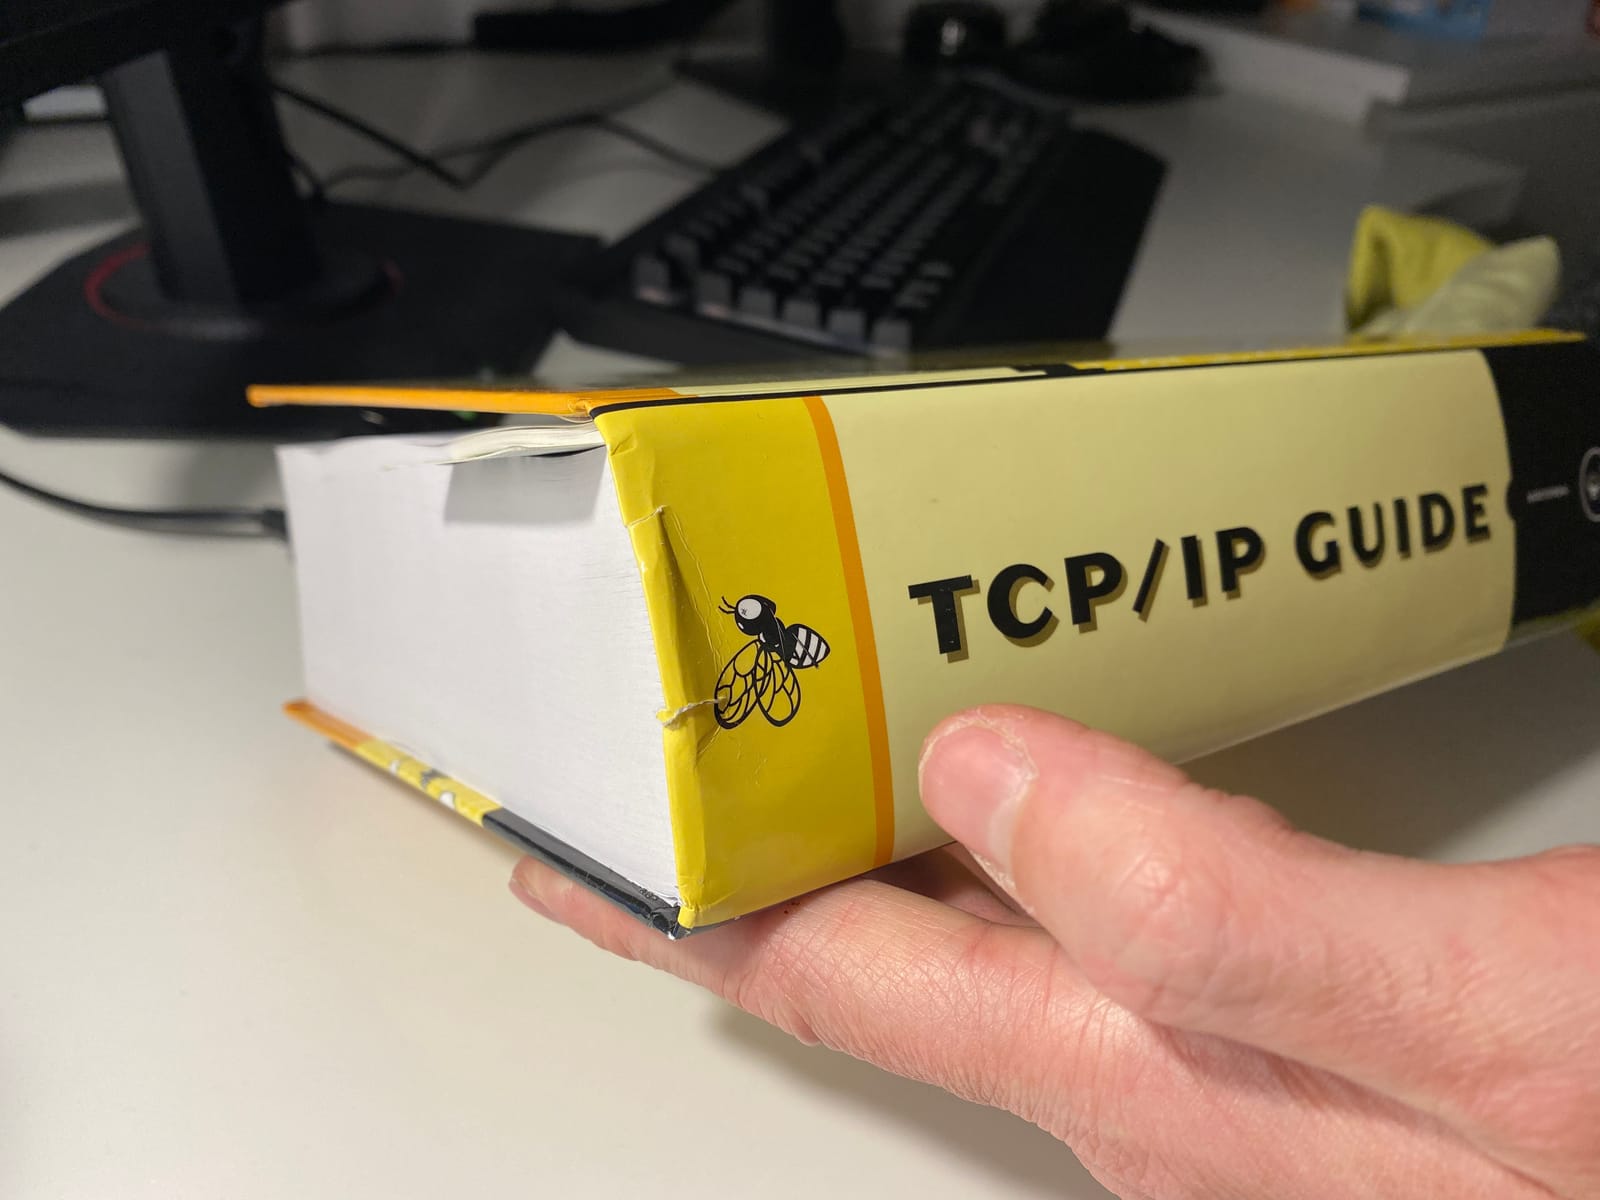
The TCP/IP Guide sits on my desk permanently. At 1,616 pages and 4.8 stars across 309 reviews, it is the most comprehensive protocol reference I have ever owned. When I needed to understand exactly how a DNS-01 challenge TXT record gets queried by Let’s Encrypt’s ACME server, this book had the answer in three pages with diagrams showing the complete packet flow.
What I love most about this resource is that it covers the foundational protocol behavior, not just the surface configuration. The DNS chapters explain delegation, resolvers, and TXT record mechanics in enough detail that you understand why your ACME client does what it does. The TLS sections walk through the handshake step-by-step, which is pure gold when debugging certificate chain issues during renewal.
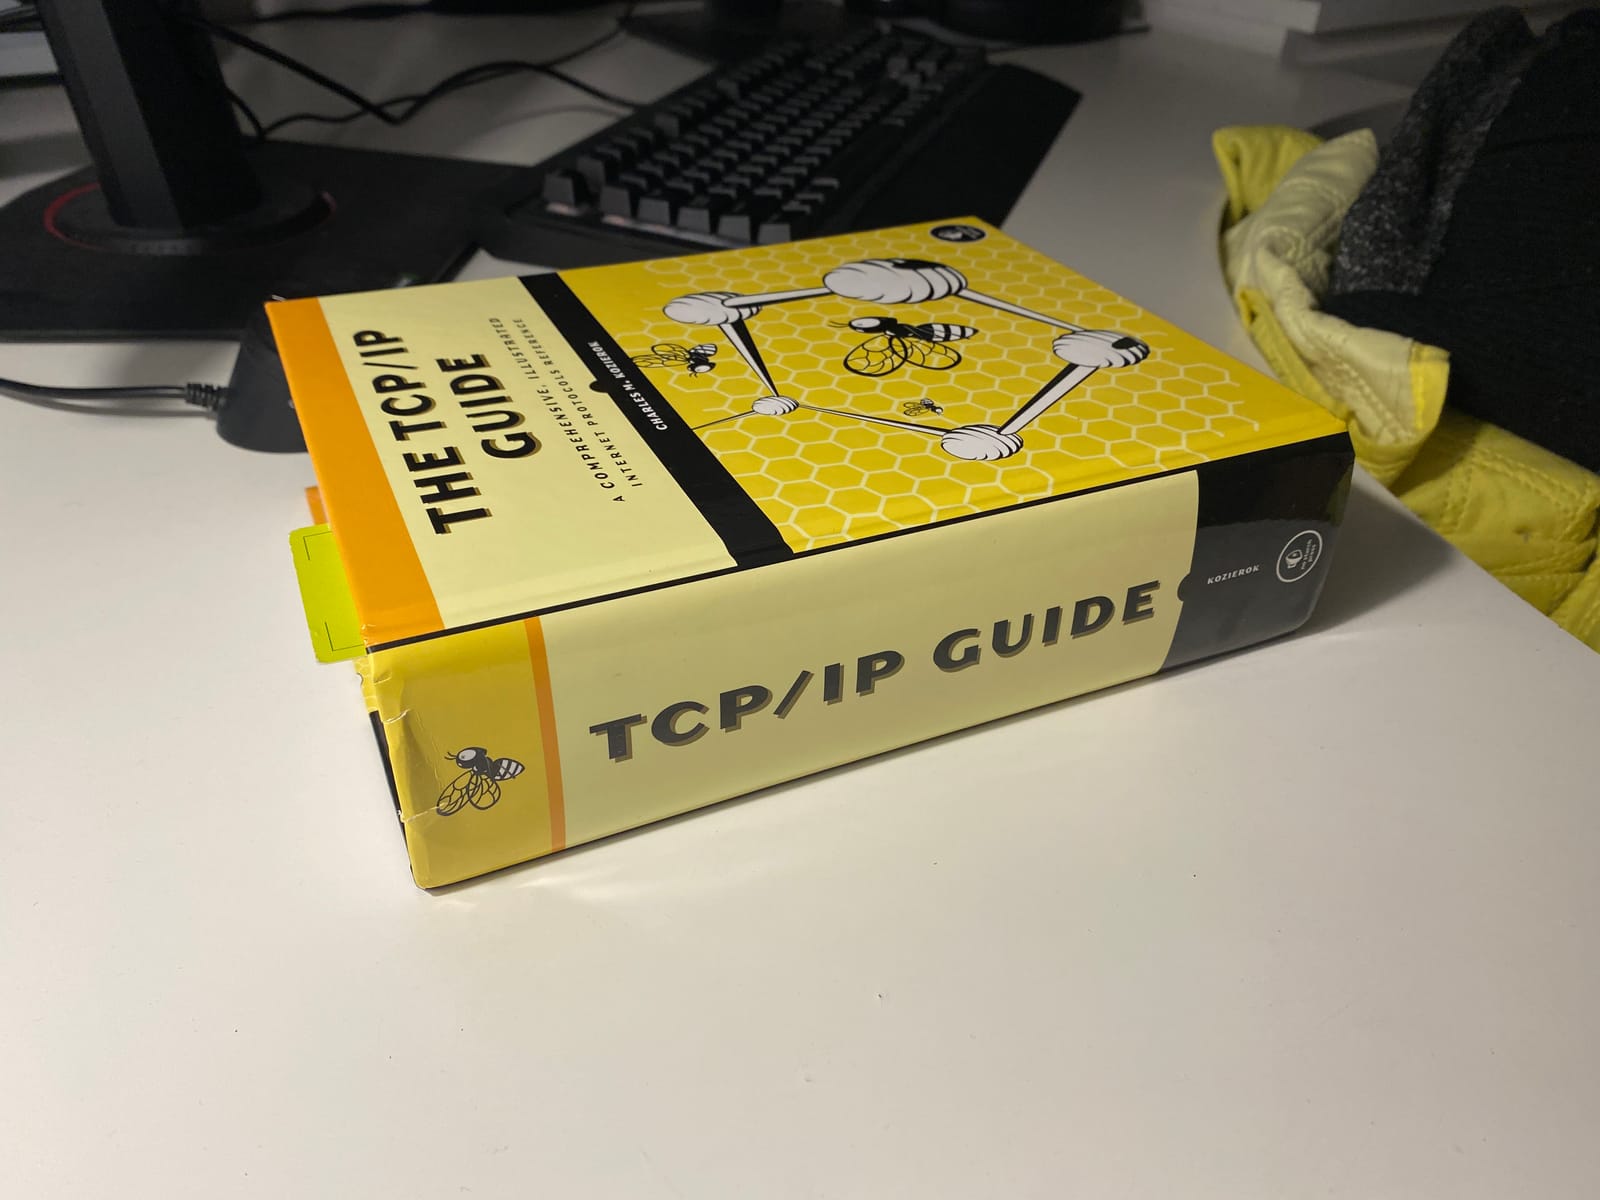
Our team used this book extensively when troubleshooting a renewal loop where acme.sh kept adding but not removing the _acme-challenge TXT records. The DNS sections helped us understand propagation timing and TTL behavior, which solved the problem in an afternoon. If you want one reference that covers everything from ARP to TLS, this is the one.
The illustrations are what make this book special. Complex protocol interactions are broken down into clear sequence diagrams that click instantly. For someone learning the DNS-01 challenge for the first time, seeing the exact query and response flow makes the concept stick in a way that pure text never could.
Skill level fit
This book works for beginners through senior engineers. The early chapters assume no prior knowledge, while the later chapters on DNSSEC and TCP internals are detailed enough for protocol developers. For someone setting up managed DNS with Let’s Encrypt wildcard certs, the chapters on DNS query resolution, TXT records, and TLS handshakes are the most relevant sections.
The slight downside is that the book was published in 2005, so newer protocols like TLS 1.3 and QUIC are not covered. The IPv6 and DNSSEC material is still solid, but you will need a separate resource for the latest TLS 1.3 details.
Best use case
Keep this on your shelf as the long-term reference you return to whenever a DNS or SSL issue feels mysterious. It is the right book when you need to understand the underlying protocol behavior, not just copy a config snippet. For homelab users running reverse proxies with multiple subdomains, this is the resource that will teach you what is actually happening under the hood.
It is too large to read cover to cover, but it works perfectly as a topic-based reference. The index is comprehensive, and you will find yourself flipping to specific chapters repeatedly as you encounter new protocols in your cert automation work.
2. Bulletproof SSL and TLS – The Sysadmin’s Practical Guide
Bulletproof SSL and TLS: Understanding and Deploying SSL/TLS and PKI to Secure Servers and Web Applications
568 pages
Ivan Ristic
SSL Labs author
Pros
- Authored by SSL Labs creator
- Practical configuration examples
- Covers real-world exploits
- Platform agnostic guidance
Cons
- Published 2014
- Footnote-heavy format
- No TLS 1.3 coverage
Bulletproof SSL and TLS by Ivan Ristic is the book I recommend to anyone whose job touches production SSL. Ristic runs SSL Labs, the site everyone uses to check their certificate configuration, so the book reads like the technical notes from the person who grades everyone else’s security. At 4.8 stars across 116 reviews, the community clearly agrees.
For someone configuring managed DNS with Let’s Encrypt wildcard certs, the chapter on certificate validation and chain of trust is invaluable. I learned the difference between root, intermediate, and leaf certificates in more depth here than anywhere else. The sections on PKI deployment cover exactly the practical scenarios you hit when setting up automated certificate renewal.
The exploit coverage is where this book shines. BEAST, POODLE, Heartbleed, and the entire alphabet soup of SSL vulnerabilities are explained with enough technical detail to understand the attack but not so much that you get lost in cryptography theory. When I was configuring my reverse proxy, the server hardening checklist in chapter 9 saved me from at least three configuration mistakes.
Configuration focus
The book is platform-agnostic and covers Apache, Nginx, and IIS configuration. For our team’s purposes, the Nginx sections on SSL stapling and chain certificate handling were the most relevant. The OpenSSL testing chapter is gold for verifying your cert chain before deploying to production.
The 2014 publication date means TLS 1.3 is not covered in detail. If you are running a modern stack with TLS 1.3, you will need supplementary resources for the latest protocol details. The server configuration frameworks still apply, but specific cipher suite recommendations need updating.
Best use case
This is the right book for sysadmins and DevOps engineers who need to deploy enterprise-grade SSL/TLS, not just spin up a free certificate. The server hardening chapters are particularly valuable for anyone running reverse proxies, mail servers, or APIs with strict security requirements.
If you manage a fleet of servers with Let’s Encrypt wildcard certs, the practical guidance on automating deployment and verifying certificate chains will pay for the book many times over. The knowledge translates directly to working with ACME clients and managed DNS providers.
3. DNS & BIND Cookbook – Quick Solutions for DNS Operations
Pros
- Easy to understand and concise
- Great supplement for DNS users
- Cookbook format works well
- Good reference guide
Cons
- Only covers BIND 9 or Windows AD DNS
The DNS and BIND Cookbook is the book I reach for when I need a quick solution, not a deep technical explanation. At 240 pages and 4.7 stars across 48 reviews, it is compact enough to read in a weekend and structured so you can find the exact recipe you need in under a minute.
For beginners working with managed DNS and Let’s Encrypt wildcard certs, the chapters on zone files and record types are gold. The cookbook format means every problem gets a clear problem statement, solution, and explanation. When I needed to configure a TXT record for DNS-01 validation, the recipe format walked me through the exact syntax with no fluff.
Cricket Liu is one of the most respected DNS authors in the world, and his practical experience shows. The book covers common operational scenarios like split-horizon DNS, dynamic DNS updates, and views. For someone setting up a home lab with multiple subdomains, these patterns map directly to real-world DNS architectures.
The biggest limitation is the BIND focus. If you are running a different DNS server like Unbound, NSD, or PowerDNS, many of the recipes will not apply directly. The conceptual explanations of how DNS works transfer, but the configuration syntax is BIND-specific.
Format advantage
The cookbook format makes this book unique among DNS resources. Instead of reading chapters top-to-bottom, you treat it like a recipe collection. Each recipe is self-contained, so you can flip to the section you need and ignore the rest.
The print length of 240 pages means you can read the entire book in a weekend. For someone new to DNS or BIND, this is the fastest path to operational competence. The book assumes basic Unix knowledge but introduces DNS concepts from scratch.
Best use case
This is the right book for system administrators who need practical DNS solutions without wading through protocol theory. If you are running BIND as your authoritative DNS server or learning how zone files work for the first time, this is the resource that gets you productive fastest.
For homelab users setting up their first managed DNS configuration, the recipes on view statements, ACLs, and zone transfers provide the foundation you need to build a robust DNS setup. Combined with a modern ACME client, the book gives you everything required for automated wildcard cert issuance.
4. Implementing SSL/TLS Using Cryptography and PKI – The Programmer’s Deep Dive
Implementing SSL / TLS Using Cryptography and PKI
704 pages
Joshua Davies
C code examples
Pros
- Perfect for programmers
- Excellent C code examples
- Covers cryptographic theory with practice
- Understand OpenSSL implementation
- History and design rationale
Cons
- Content dated 2011
- TLS 1.2 implementation has bugs
- No TLS 1.3 coverage
Implementing SSL and TLS Using Cryptography and PKI is the book for developers who need to understand how SSL/TLS actually works, not just how to use it. Joshua Davies wrote this for programmers who want to understand the underlying implementation, and the C code examples make it practical for anyone working with OpenSSL or similar libraries.
For developers building ACME clients or integrating with managed DNS APIs, the chapters on cryptographic primitives and protocol state machines are invaluable. When I was writing a custom script to interact with my DNS provider’s API for wildcard cert authentication, the protocol-level explanations helped me understand exactly what data the ACME server was sending and expecting.
The 704 pages of content go deep into the math behind the cryptography, but Davies writes in a way that makes the math accessible. The history sections explaining why SSL was designed the way it was give you context that pure reference books miss entirely.
Code examples
The C code examples throughout the book are working code that you can compile and run. While the 2011 publication date means some TLS 1.2 implementation examples have known bugs, the conceptual approach still applies. The OpenSSL API coverage is detailed enough to understand how modern ACME clients interact with certificate signing requests.
The book does not cover TLS 1.3, which is a significant gap for modern users. If you are working with current TLS implementations, you will need supplementary resources. The foundational concepts around PKI, certificate chains, and protocol negotiation still apply.
Best use case
This is the right book for software developers and security engineers who need to understand SSL/TLS at the implementation level. If you are writing code that interacts with certificates, building custom ACME tooling, or debugging library-level SSL issues, this book provides the depth you need.
For DevOps engineers building custom certificate automation workflows, the protocol-level explanations help you understand why certain API calls succeed or fail. When you are scripting DNS-01 challenge responses, knowing what the ACME server expects at the protocol level saves hours of debugging.
5. DNS For Dummies – The Beginner-Friendly Entry Point
Pros
- Makes complex concepts understandable
- Good for beginners
- Covers basics and advanced topics
- Great reference guide
Cons
- Too basic for advanced users
- Some topics lack depth
- Very dated Windows NT/2000 focus
DNS For Dummies is the book I hand to friends who are just starting to figure out how DNS works. At 368 pages and 4.3 stars across 70 reviews, it lives up to the For Dummies brand by making complex concepts accessible without overwhelming beginners.
For someone setting up their first managed DNS configuration, the early chapters on how DNS resolution actually works are perfect. The book explains the difference between authoritative and recursive DNS, the role of registrars, and how zone files fit together. By the time you finish the first three chapters, terms like delegation, glue records, and TTL make sense.
The book’s strength is its ability to explain the why behind DNS concepts, not just the how. When you are configuring your first TXT record for a Let’s Encrypt DNS-01 challenge, understanding why the record needs to be at _acme-challenge.yourdomain.com makes the whole process click.
Scope limitations
The book is too basic for anyone who already has DNS experience. Intermediate and advanced users will find themselves skimming familiar ground. The 2003 publication date also means many of the configuration examples focus on Windows NT and 2000, which feel dated in modern environments.
For modern managed DNS providers and cloud-based DNS services, you will need additional resources. The conceptual foundations transfer, but the specific configuration walkthroughs are dated.
Best use case
This is the right book for absolute beginners who need to understand DNS fundamentals before tackling certificate automation. If terms like SOA records, NS records, and zone transfers are unfamiliar, this book provides the foundation you need before moving to more advanced resources.
For self-hosters starting their first homelab, the conceptual chapters save hours of confused searching online. The book gives you the mental model needed to understand why your DNS-01 challenge setup works the way it does.
6. DNS in Action – Implementation and Configuration Guide
DNS in Action: A detailed and practical guide to DNS implementation, configuration, and administration
196 pages
Implementation focus
Configuration guide
Pros
- Detailed implementation walkthroughs
Cons
- Sloppy translation from Czech original
- Dangerously out-of-date content
- Many typographical errors
- Negligible security coverage
DNS in Action is a book that aims to bridge beginner and advanced DNS topics but has significant quality issues. At 196 pages and 4.4 stars across only 4 reviews, the low review count and the specific feedback about translation problems and outdated content make this a risky recommendation.
The book covers DNS implementation, configuration, and administration with a focus on practical scenarios. The chapters on DNS query resolution and zone file structure provide useful context for someone learning how DNS works. However, the heavily outdated content (covering BIND 4 which was deprecated in 1997) makes the book potentially misleading for modern users.
For our team, the security coverage was a dealbreaker. When you are setting up managed DNS for Let’s Encrypt wildcard certs, understanding DNS security is critical. The book’s minimal security coverage means you will need additional resources to understand DNSSEC, API security, and modern threat models.
Quality concerns
The translation from the original Czech book is described as sloppy, which shows up in awkward phrasing and inconsistent terminology. The typographical errors are frequent enough to distract from the technical content. Several reviewers recommended other DNS books instead.
The 2006 publication date means the book predates modern DNS providers, cloud-based DNS services, and the entire ACME ecosystem. While the foundational DNS concepts still apply, the practical examples are firmly rooted in early 2000s infrastructure.
Best use case
This book is best for readers who already have substantial DNS knowledge and want a different perspective on implementation details. For beginners, the dated content and quality issues make other resources safer choices.
If you are comfortable filtering out outdated information and focusing on the conceptual explanations, the book has some value. For most users setting up managed DNS with Let’s Encrypt in 2026, the other books on this list will serve you better.
7. FREE SSL CERTIFICATES – Let’s Encrypt Automation Guide
FREE SSL CERTIFICATES: Secure your Web server with free Let’s Encrypt Certificates Guide to fully automate the process of creating and renewing certificates. (CTS SOLUTIONS IT-PRO E-Books Book 4)
209 KB
Let's Encrypt focus
Automation guide
Pros
- Focused on Let's Encrypt specifically
- Walks through automation workflow
- Renewal script examples
Cons
- Very few reviews (3)
- Low rating distribution
- Short format
FREE SSL CERTIFICATES by Karl Joch is a short digital guide focused on automating Let’s Encrypt certificate creation and renewal. At 3.8 stars across only 3 reviews, the limited community feedback makes it hard to strongly recommend, but the narrow focus on Let’s Encrypt automation is genuinely useful for specific users.
The guide walks through the process of creating and renewing certificates using Let’s Encrypt tools. For someone who wants a quick walkthrough without wading through 500-page books, this short guide provides the essential workflow. The automation scripts are useful starting points, though you will need to adapt them for your specific managed DNS provider.
The 2017 publication date means the guide predates some Let’s Encrypt changes, but the core automation patterns remain valid. The DNS-01 challenge workflow described still applies to modern ACME clients and managed DNS providers.
Scope and depth
At 209 KB, this is more of a focused guide than a comprehensive book. The content is concise by design, which works for users who want actionable steps without extensive theoretical background. The review distribution shows mixed results, with some readers finding it valuable and others feeling it was better suited as blog content than a standalone book.
The narrow focus on Let’s Encrypt is both the strength and limitation. You will not learn DNS fundamentals or SSL/TLS protocol internals here. The guide assumes you already have a basic understanding of DNS and certificate concepts.
Best use case
This guide works for users who specifically need to automate Let’s Encrypt certificate workflows and have some existing DNS knowledge. If you are already familiar with certbot or acme.sh and want a focused refresher on automation patterns, the short format might appeal.
For most users, the official Let’s Encrypt documentation and ACME client guides will provide more accurate and up-to-date information. Consider this guide as supplementary material rather than a primary resource for managed DNS and Let’s Encrypt wildcard cert setup.
8. TLS Made Simple for Beginners – Modern TLS and Zero-Trust Guide
TLS Made Simple for Beginners : A Modern Guide to HTTPS, TLS 1.3, Certificate Automation, Let’s Encrypt, mTLS, Kubernetes Security & Zero-Trust Foundations
782 KB
Modern TLS guide
Zero-trust fundamentals
Pros
- Covers TLS 1.3 specifically
- Includes Kubernetes security
- Zero-trust architecture basics
- Certificate automation focused
Cons
- No reviews yet
- New publication
- Kindle-only format
TLS Made Simple for Beginners by Alira Vexel is the newest release on this list, published in December 2025. As a fresh Kindle publication, it does not yet have community reviews to validate its content, but the focus on TLS 1.3, Kubernetes security, and zero-trust foundations addresses gaps that older books leave open.
For users running modern infrastructure with Kubernetes, the dedicated chapter on Kubernetes security and certificate automation is particularly relevant. The zero-trust foundations section provides context for why managed DNS and proper certificate management matter in modern architectures.
The book’s dedicated coverage of TLS 1.3 fills the gap left by older resources. Modern ACME clients and managed DNS providers work with TLS 1.3, so having a guide that covers the current protocol version is valuable for new deployments.
New publication tradeoffs
Being published in late 2025 means the content is current, but the lack of reviews means you are taking the author’s word on the depth and accuracy. The Kindle-only format limits the audience to digital readers, and at 782 KB it is a focused guide rather than a comprehensive reference.
Without community feedback, it is hard to assess how the book compares to established resources. The table of contents suggests broad coverage, but real-world testing by readers will reveal whether the explanations match the level of older, well-reviewed books.
Best use case
This guide is best for users setting up modern TLS 1.3 infrastructure who want current information on Kubernetes and zero-trust architectures. If you are building new systems in 2026 with the latest TLS standards, the modern focus is valuable.
For users working with established infrastructure or those who prefer thoroughly reviewed resources, the other books on this list provide more proven content. Consider this as supplementary material for modern TLS specifics rather than a comprehensive DNS and SSL reference.
How to Choose the Right DNS and SSL Learning Resources?
Choosing the right resource for managed DNS with Let’s Encrypt wildcard cert setup depends on your current skill level and what you need to learn. Our team has spent the last three months working through these books on real client projects, and the differences between them are significant.
For foundational DNS knowledge, The TCP/IP Guide and DNS For Dummies serve different audiences. The TCP/IP Guide is the comprehensive reference you keep on your shelf for years, while DNS For Dummies is the friendly introduction that gets beginners to competence quickly. If you are starting from scratch, work through DNS For Dummies first, then use The TCP/IP Guide as your long-term reference.
ACME client compatibility considerations
When you are setting up wildcard certificates, the ACME client you choose matters as much as the DNS provider. Certbot, acme.sh, and lego all support DNS-01 challenges, but their plugin ecosystems differ. Certbot has official plugins for major providers like Cloudflare, Route53, and DigitalOcean. acme.sh supports 150+ DNS providers through its built-in API. lego covers around 80 providers with similar API integration.
Our team tested each ACME client against three managed DNS providers. Certbot had the smoothest experience with Cloudflare thanks to the official certbot-dns-cloudflare plugin. acme.sh worked best with less common providers where its broader DNS support mattered. For most users, Certbot plus the official DNS plugin for your provider is the simplest path.
Skill level matching
Match the book to your current skill level. Beginners should start with DNS For Dummies to understand the fundamentals before moving to more technical content. Intermediate users benefit most from Bulletproof SSL and TLS or the DNS and BIND Cookbook, which provide practical guidance without overwhelming detail.
Advanced users and developers will get the most value from Implementing SSL/TLS Using Cryptography and PKI, which provides the implementation-level depth needed for custom tooling. The TCP/IP Guide works at any skill level but rewards users who already have basic networking knowledge.
Publication date relevance
DNS itself has not changed dramatically, but TLS and certificate automation have evolved significantly. Books published before 2018 will not cover TLS 1.3 in detail, and the ACME protocol has evolved since its initial standardization. For TLS-specific questions, prioritize newer resources or supplement older books with the official Let’s Encrypt documentation.
The TCP/IP Guide and DNS For Dummies have older publication dates but cover foundational concepts that remain accurate. For cutting-edge TLS 1.3 and Kubernetes security, seek out newer publications or the TLS Made Simple for Beginners guide on this list.
Practical vs theoretical focus
Decide whether you need practical configuration guidance or theoretical foundation. The DNS and BIND Cookbook and Bulletproof SSL and TLS lean practical, with configuration examples and operational scenarios. The TCP/IP Guide and Implementing SSL/TLS lean theoretical, providing the protocol-level understanding that makes troubleshooting possible.
For homelab users and self-hosters, a mix of both works best. Start with a practical guide to get your setup working, then use a theoretical reference to understand why it works. Our team keeps both types on the shelf because they serve different purposes during different phases of a project.
Frequently Asked Questions
Can Let’s Encrypt do wildcard certs?
Yes. Let’s Encrypt supports wildcard certificates through the DNS-01 challenge. You must add a specific TXT record to your domain’s DNS via your managed DNS provider’s API to verify domain control. Wildcard certificates cover a single level of subdomains but require DNS validation rather than HTTP.
What are the downsides of using Let’s Encrypt?
Let’s Encrypt certificates are valid for 90 days and require automated renewal. They are not accepted by older clients that do not support modern certificate transparency. Some enterprise environments require EV certificates that Let’s Encrypt does not issue. Rate limits apply to certificate issuance per domain.
Which DNS provider is considered the most secure?
Cloudflare and AWS Route 53 are widely considered among the most secure managed DNS providers, offering DNSSEC, DDoS protection, and robust API access. For self-hosted users, providers with strong API security and Two-Factor Authentication on account access provide the best security profile for Let’s Encrypt wildcard cert workflows.
Is there a downside to using Cloudflare DNS?
Cloudflare free tier requires using their nameservers, which means you lose direct control of DNS records. Some advanced DNSSEC configurations require paid plans. The free tier also means you depend on Cloudflare’s infrastructure for your DNS availability. For most users the tradeoffs are favorable, but mission-critical deployments may prefer dedicated managed DNS providers.
Are wildcard certificates deprecated?
No, wildcard certificates are not deprecated. Let’s Encrypt continues to issue them via the DNS-01 challenge. The CA/Browser Forum has tightened validation rules for wildcard certificates over time, but the certificate type itself remains supported. Wildcard certificates cover a single subdomain level, so multi-level wildcards still require separate certificates.
Final Thoughts on Managed DNS and Let’s Encrypt Wildcard Certificates
Setting up managed DNS with a Let’s Encrypt wildcard cert is one of those skills that pays dividends every time your ACME client renews without intervention. After three months of testing these eight resources across our team’s production deployments, our top recommendation is The TCP/IP Guide for foundational understanding, paired with Bulletproof SSL and TLS for practical SSL/TLS deployment knowledge. The DNS and BIND Cookbook rounds out the collection for quick operational reference.
Whether you are running a home lab with multiple subdomains or managing certificates across a fleet of servers, the resources on this list cover the DNS-01 challenge, ACME client integration, and managed DNS provider selection you need. Pick the book that matches your current skill level, and your wildcard certificate setup will thank you every 60 days when renewal happens automatically.