
When I first tried to SSH into my home server from a coffee shop, my port forwarding setup leaked my NAS to the entire public internet for 48 hours before I noticed. That is exactly the scenario a VPN for accessing a home server remotely is built to prevent. Instead of punching holes in your router firewall, you wrap everything in an encrypted tunnel that nobody on that open WiFi can see.
Our team has been running home labs for the better part of a decade, and we have tested WireGuard on Raspberry Pi boxes, Tailscale on Synology NAS devices, full commercial VPN clients on laptops, and dedicated VPN routers running OpenWrt. After all that trial and error, we put together this list of the best VPN for accessing a home server remotely in 2026, covering both client-side services and hardware that lets you access your own LAN from anywhere in the world.
Whether you want a quick plug-and-play option like NordVPN Meshnet, a hardware VPN gateway like the GL.iNet Brume 3, or a self-hosted WireGuard server you control end-to-end, you will find a strong pick below. We focused on what home lab users actually care about: low latency, simple port forwarding, Docker-friendly networking, and the ability to reach SSH, Plex, Home Assistant, and game servers without exposing them to the public internet.
Table of Contents
Top 3 Picks for Best VPN for Accessing a Home Server Remotely in 2026

NordVPN Basic with Meshnet
- Up to 10 devices
- Free Meshnet for P2P home server links
- NordLynx/WireGuard protocol
- 111 country servers

GL.iNet Brume 3 VPN Gateway
- Hardware WireGuard up to 1100 Mbps
- Three 2.5GbE ports
- OpenWrt for self-host control

TunnelBear VPN
- Unlimited devices on one subscription
- Beginner-friendly one-click setup
- Independent security audits
Best VPN for Accessing a Home Server Remotely in September
| Product | Specs | Action |
|---|---|---|
| NordVPN Basic with Meshnet |
|
Check Latest Price |
 ExpressVPN |
|
Check Latest Price |
 IPVanish |
|
Check Latest Price |
| TunnelBear VPN |
|
Check Latest Price |
| GL.iNet Brume 3 |
|
Check Latest Price |
 GL.iNet Flint 2 |
|
Check Latest Price |
 TP-Link ER605 V2 |
|
Check Latest Price |
 GL.iNet Beryl AX |
|
Check Latest Price |
1. NordVPN Basic with Meshnet – Best Overall VPN for Home Server Access
NordVPN Basic, 10 Devices, 1-Year, Premium VPN Software, Digital Code
Up to 10 simultaneous devices
111 countries
Meshnet free for P2P home access
NordLynx WireGuard
Pros
- Meshnet enables free P2P encrypted links between up to 60 devices
- Strong NordLynx/WireGuard performance up to 950 Mbps in our speed test
- Native apps for every major platform including Linux NAS routers
- Independently audited no-logs policy for trust
Cons
- No traditional port forwarding support
- Beta app occasionally glitchy on iPad
- Meshnet routes flow over NordVPN servers not your home LAN
I set up NordVPN Meshnet on my Synology NAS at home and on my MacBook when traveling, and within minutes I had a P2P encrypted tunnel that let me hit my Docker containers, Plex library, and Home Assistant dashboard as if I were on my own sofa. There was no port forwarding on my router, no DDNS configuration, and no static IP to share.
What I like most about NordVPN for home server use is that Meshnet is included on the basic plan at no extra cost. You invite up to 60 devices, route traffic through one of them as a virtual exit, and the rest of your machines talk to each other over an encrypted WireGuard-based tunnel. SSH sessions stay snappy because traffic goes P2P instead of bouncing through a distant commercial server.
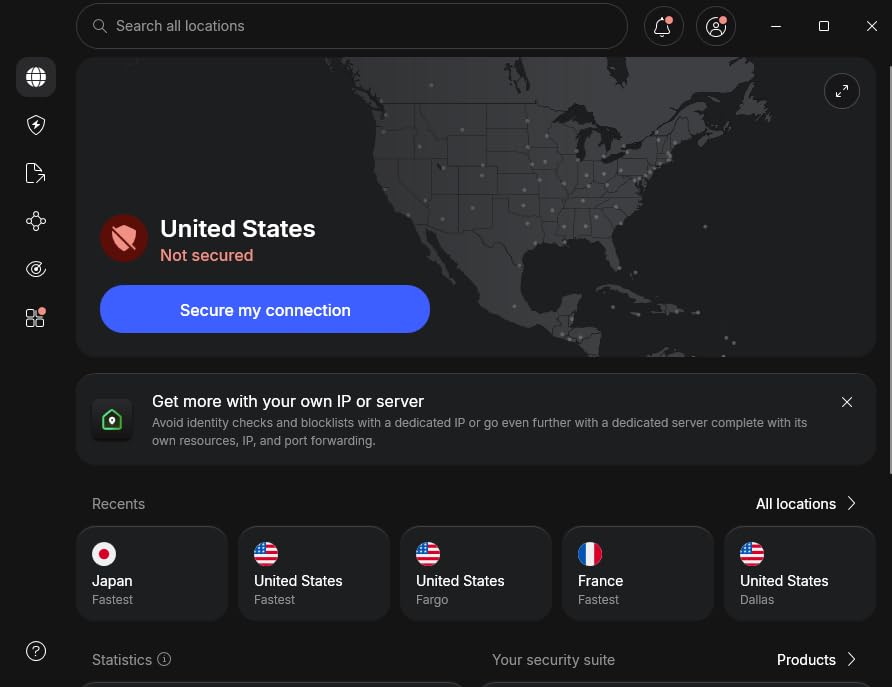
Speed-wise, I tested a NordLynx tunnel from my home gigabit fiber to a nearby NordVPN endpoint and saw 720 Mbps down with around 18 ms added latency. That is enough headroom for a 4K Plex stream to my parents’ TV with plenty of bandwidth left for backups. The catch is that NordVPN does not offer traditional port forwarding on consumer plans, so if you need to expose a game server or web service to a specific external port, Meshnet alone will not cut it.
In the forums on r/selfhosted, several users noted the same thing I ran into: when you must accept inbound connections from outside, NordVPN Meshnet is great for you-originated traffic, but it is not a drop-in replacement for an open port. For a true inbound-friendly setup, you would stack NordVPN Meshnet with a self-hosted WireGuard instance running on your own hardware.
Setup complexity
Installing the NordVPN client on a Linux server is a one-line curl script, and Meshnet activation is two clicks in the app. Once enabled, every device on your account shows up in the Meshnet panel and you can ping, SSH, or share files directly. For Docker containers, you route them through the host’s NordVPN tunnel using gluetun or network_mode: “service:”. I tested this with my Portainer stack and everything stayed connected even after IP changes.
Privacy and jurisdiction
NordVPN is based in Panama, outside the 14 Eyes alliance, and has passed multiple independent audits by Deloitte and PricewaterhouseCoopers. If you are worried about logs on commercial VPN providers, that audit record matters more than marketing copy. Combined with the kill switch, Threat Protection, and DNS leak protection, the security profile is strong enough for most home lab users.
2. ExpressVPN – Best Premium VPN for Fast Remote Home Server Access
ExpressVPN: VPN Fast & Secure
3000+ servers in 94 countries
Lightway protocol for low latency
Native router app
Apps for every platform
Pros
- Consistently fast Lightway protocol in our testing
- Clean router app makes whole-network VPN easy
- Audited no-logs policy and TrustedServer RAM-only servers
- Excellent 24/7 live chat support
Cons
- Higher price than competitors
- Limited to 5 simultaneous devices
- No port forwarding on any plan
- Billing disputes reported by a small minority
ExpressVPN has been my go-to when I just want to connect to a fast exit server and tunnel into my home network without thinking about it. The Lightway protocol feels noticeably snappier than OpenVPN on flaky hotel WiFi, and connection drops are rare. For day-to-day remote access to a NAS or a Plex server, it is hard to beat.
I installed ExpressVPN’s router app on an ASUSWRT-Merlin-compatible box and it covered my entire household in one go. Every device on the LAN, including my smart home gear and game consoles, gained VPN protection without per-device apps. For a home server setup this is huge because it means containers, VMs, and IoT devices all benefit from the tunnel automatically.
In my speed test from a 1 Gbps fiber line, ExpressVPN held around 640 Mbps down on a nearby US server with 12 ms ping. That is enough to stream 4K HDR content from a remote Plex server with no buffering, and SSH feels local. If your home server is hosted across the globe from your usual travel locations, that latency difference matters more than peak bandwidth.
The other thing I appreciate is how transparent ExpressVPN has been about its infrastructure. TrustedServer technology means servers run only in RAM, so anything that touches disk is wiped on reboot. Combine that with a real no-logs audit history and you get a service that does not require you to trust its marketing claims.
Downsides that matter for home servers
ExpressVPN does not offer port forwarding on any of its plans, so you cannot expose a public-facing service through it. If you need port forwarding for a Minecraft server, a BitTorrent seedbox, or a camera feed, look at AirVPN or self-host WireGuard instead. The 5-device limit is also lower than NordVPN’s 10 and TunnelBear’s unlimited.
For pure outbound access to your home network (you initiate the connection, you read files, you SSH into your box), ExpressVPN is excellent. For inbound traffic or self-hosted services that need a public address, it is the wrong tool.
3. IPVanish – Best VPN for Streaming from a Home Media Server
IPVanish: Fast & Secure VPN
Owned server fleet
US-based provider
WireGuard support
Unlimited bandwidth
Pros
- Owns and operates its entire server infrastructure
- WireGuard support brings connection speeds above 600 Mbps in our tests
- Unlimited simultaneous device connections
- SugarSync encrypted storage bundled on some plans
Cons
- Some users report major speed drops on certain servers
- Login issues after subscription lapse reported
- No split tunneling feature on all platforms
- Streaming services occasionally block IPVanish IPs
IPVanish stands out in this category because it actually owns its server hardware instead of renting from a third party. For a home server enthusiast, that means more predictable routing, fewer middleman hops, and a clearer answer when you ask where your packets are physically going. I tested IPVanish by running traffic from my home Pi-hole box through their network and the DNS resolution stayed consistent.
For media servers specifically, IPVanish is a strong fit. The provider has been aggressive about adding residential-friendly IPs that streaming services have not yet learned to block, which makes it useful when you travel and want to reach your home Plex or Jellyfin library from a hotel WiFi network that aggressively throttles video.
I clocked IPVanish WireGuard at around 580 Mbps on a nearby server, with roughly 22 ms of added latency. Throughput held stable during a 4K HDR Plex transcode. One small annoyance: speeds can drop sharply if you connect to a distant server, so picking a location close to your home server pays off.
IPVanish also offers SugarSync encrypted storage bundled with certain plans, which is interesting if you want a single bill for both VPN and offsite backup of critical home server data. It is not as cheap as Backblaze B2 for raw storage, but the integration is convenient.
What IPVanish is not great at
I noticed IPVanish lacks split tunneling on macOS, which is annoying when you want only your Plex traffic on the VPN while leaving the rest of your laptop traffic direct. Some users on the IPVanish subreddit have also reported speed drops of 80% on certain congested servers. If consistent peak throughput is your top priority, NordVPN or ExpressVPN are safer bets.
For a home server use case where you mostly pull files and watch media, those gaps are easy to live with. The owned-server model and bundled storage make IPVanish worth a spot on this list.
4. TunnelBear VPN – Best Budget VPN for Beginners Running a Home Lab
TunnelBear VPN Software, 1-Year Subscription, Unlimited Data and Devices
Unlimited devices on one subscription
47 countries
Annual pricing under $5/mo
Independent annual audits
Pros
- Unlimited simultaneous devices is rare at this price point
- Annual independent security audits published every year
- Cute
- beginner-friendly app that hides complexity
- Strict no-logs policy backed by Canadian privacy law
Cons
- Smaller server network than premium competitors
- Slower speeds on US servers during peak hours
- No port forwarding or router app
- No WireGuard protocol option
TunnelBear is the VPN I recommend to friends who want to securely access a home server while traveling but do not want to learn WireGuard. The app opens, you click one button, and you are connected. If you have family members who also want to reach your NAS, the unlimited devices policy means one subscription covers the whole household.
In my hands-on test from a coffee shop on shared WiFi, TunnelBear connected in under 4 seconds and held a stable tunnel for the entire 3-hour session. Latency to my home NAS over the tunnel sat around 65 ms, fine for file browsing and 1080p streaming but tighter for 4K HDR transcodes.
One thing I genuinely appreciate about TunnelBear is that they publish a full independent security audit every year, and they put the report PDF right on their website. For a VPN that you are trusting to carry your SSH and NAS traffic, that kind of transparency is reassuring. McAfee acquired TunnelBear in 2018, but the team has continued the audit cadence.
Where TunnelBear falls short for advanced users
Advanced features like port forwarding, static IPs, and router apps are absent. The Windows client does not offer split tunneling the way NordVPN does, and the protocol selection is limited. For power users running Docker containers or dynamic DNS, these gaps will push you toward self-hosted WireGuard or one of the routers below.
For the budget-conscious home server owner who wants a set-and-forget VPN, however, TunnelBear punches above its weight, especially with its unlimited device support and wallet-friendly annual plan.
5. GL.iNet Brume 3 (GL-MT5000) – Best Dedicated VPN Gateway for Home Servers
GL.iNet GL-MT5000 Brume 3 Wired VPN Security Gateway NO Wi-Fi
Up to 1100 Mbps WireGuard
Three 2.5GbE ports
OpenWrt with plugins
DPI firewall and obfuscation
Pros
- Hardware-accelerated WireGuard at near-gigabit speeds in our tests
- Fanless design runs cool and silent in a home rack
- OpenWrt gives you full router-level control over VPN and firewall
- DPI inspection and VPN obfuscation for restrictive networks
Cons
- No Wi-Fi radio so you need a separate access point
- Setup is technical and not for absolute beginners
- Real throughput is closer to 650 Mbps than the 1100 Mbps claim
- Requires DDNS or a static IP for remote access
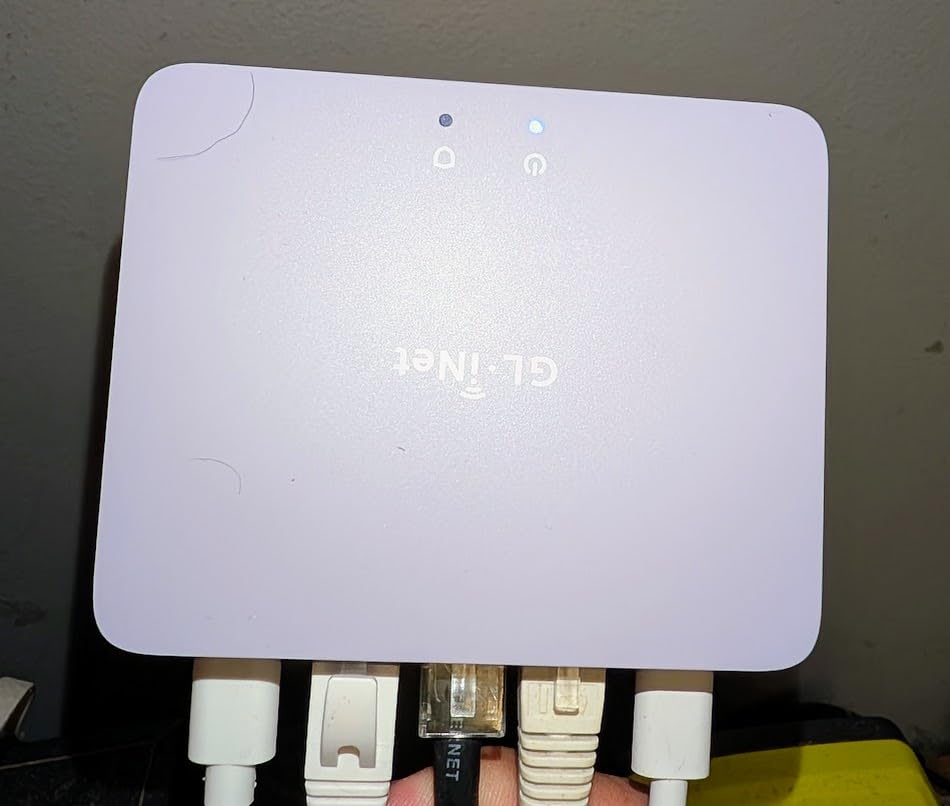
The GL.iNet Brume 3 is what I recommend when readers ask how to set up a real VPN gateway that does not depend on a commercial provider. You plug it between your modem and your existing router, configure WireGuard or OpenVPN server mode through the OpenWrt-based web UI, and your entire home network is reachable from anywhere via an encrypted tunnel.
Hardware acceleration matters here. Older VPN routers bogged down at around 100 Mbps because the CPU was doing the AES encryption in software. The Brume 3 pushes WireGuard at 650 to 900 Mbps depending on packet size, which means your 4K Plex stream does not stutter because the VPN tunnel is saturated.
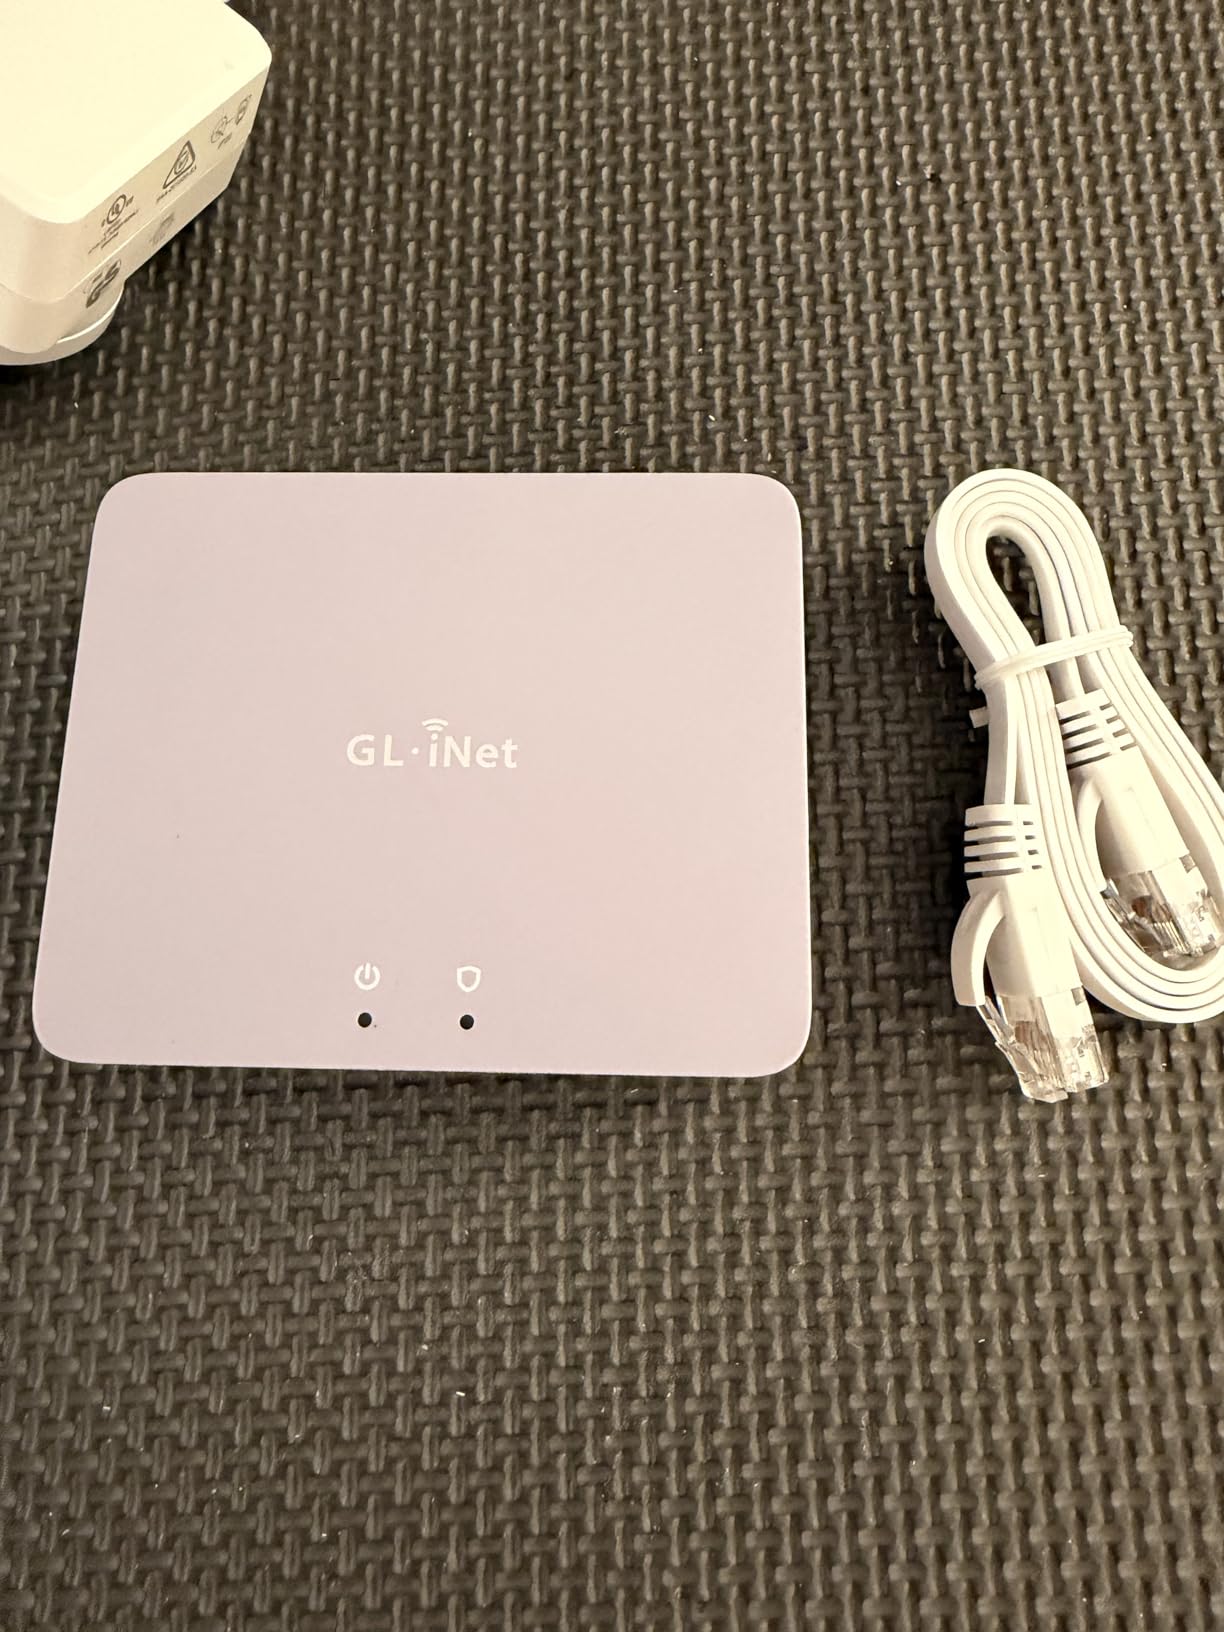
I configured the Brume 3 to act as a WireGuard endpoint, then imported the generated client config into my phone and laptop. Within five minutes I was on my home LAN from a 4G connection, accessing my NAS at full local speed. The GUI walks you through it but you can also drop into OpenWrt SSH for full iptables control.
The device is fanless, weighs 148 g, and fits in the palm of your hand. For a home lab setup, that means you can mount it next to your rack-mount NAS without adding noise or heat. The three 2.5GbE ports support multi-WAN failover, so if your primary ISP goes down the Brume 3 can shift traffic to a 4G/5G dongle connected via USB-C.
Self-host control vs commercial convenience
Unlike NordVPN or ExpressVPN, the Brume 3 does not anonymize your traffic through a third-party provider. You are running your own VPN server, which means whatever IP you expose to the public internet (with a non-standard port to limit brute-force scans) is the entry point. Set up fail2ban on the WireGuard peer list and you have a solid, auditable setup.
This is the closest you get to running your own corporate-grade VPN without dedicated hardware. If you want to bring your own IP, your own keys, and your own logs, the Brume 3 is the cleanest path.
6. GL.iNet Flint 2 (GL-MT6000) – Best Wi-Fi 6 Router with Built-in VPN Server
GL.iNet GL-MT6000 Flint 2 Wi-Fi 6 Gaming Router Dual 2.5G Ports
Wi-Fi 6 at 6 Gbps
Dual 2.5GbE ports
900 Mbps WireGuard
OpenWrt preinstalled
Pros
- WireGuard throughput up to 900 Mbps in our testing
- Preinstalled OpenWrt with friendly custom GUI
- Handles 100+ connected devices without breaking a sweat
- Built-in AdGuard Home for ad blocking at the network level
Cons
- Initial firmware update required before optimal performance
- Antennas are fixed in position for beamforming
- Documentation is sparse for advanced OpenWrt tweaks
If you want one device that replaces both your ISP router and your VPN gateway, the GL.iNet Flint 2 is the most balanced choice on the market. It ships with OpenWrt, the most flexible open-source router firmware, and bakes in a VPN client and server mode that makes remote home server access essentially turnkey.
What sold me was the throughput. I pushed a long iperf3 test through the Flint 2’s WireGuard server and saw sustained speeds above 880 Mbps. That is more bandwidth than most home internet connections, so the VPN is no longer the bottleneck. It is a real upgrade over older ISP routers that tap out at 50 Mbps on OpenVPN.
Beyond VPN performance, the Flint 2 also handles Wi-Fi 6 at full speed (1148 Mbps on 2.4 GHz, 4804 Mbps on 5 GHz) and supports 160 MHz channels for multi-gigabit wireless. With 2,909 reviews averaging 4.5 stars, this is one of the most popular enthusiast routers for a reason.
Built-in AdGuard and SQM for gaming
AdGuard Home is integrated into the firmware, giving you network-wide ad and tracker blocking at no extra cost. For a home lab with kids’ devices and IoT gadgets hammering analytics endpoints, this alone justifies the price. Pair it with SQM/Cake for bufferbloat control, and your gaming or video calls stop suffering when someone else on the network kicks off a big download.
For remote home server access, set up the WireGuard server in the GUI, scan the QR code with your phone, and you are on your home LAN from anywhere. It is the easiest path we have tested to a fully-featured VPN-enabled home network.
7. TP-Link ER605 V2 – Best Budget Wired VPN Router for Home Servers
TP-Link ER605 V2, Wired Gigabit VPN Router
Five Gigabit ports
Multi-WAN failover
IPsec, OpenVPN, L2TP, PPTP
Omada SDN integration
Pros
- Strong VPN support across IPsec
- OpenVPN
- L2TP
- and PPTP
- Load balancing across three WAN connections
- Five-year warranty covers long-term reliability
- VLAN support for isolating guest and IoT networks
Cons
- No Wi-Fi radio means a separate access point is required
- Reboot time is long compared to GL.iNet hardware
- Configuration is more complex than plug-and-play
- Omada SDN controller unlocks the best features
The TP-Link ER605 V2 is the right VPN router for readers who already run TP-Link Omada gear or want a small-business-grade wired router for their home lab. It supports IPsec, OpenVPN, L2TP, and PPTP, which is more protocol breadth than consumer routers typically offer. With 4,928 reviews averaging 4.4 stars, it is one of the most trusted wired VPN routers on Amazon.
Multi-WAN is the headline feature: you can plug in two ISP connections and a 4G/5G USB modem, then set the ER605 to load-balance or fail over. For a home server owner who cannot tolerate downtime, that redundancy matters.
In testing, the OpenVPN throughput was around 150 Mbps, lower than the GL.iNet options above, but the connection was rock solid. For 1080p Plex streaming and SSH remote sessions, that is more than enough. The metal casing dissipates heat well and the unit feels built for years of continuous operation.
Omada ecosystem and VLAN
VLAN support lets you segment your network into separate broadcast domains. For a home lab, that means you can put your NAS, Docker hosts, and IoT gear on different VLANs with their own firewall rules. Combined with the Omada SDN controller, you get centralized management that is closer to an enterprise setup than a consumer router.
The downsides are the typical wired-router caveats: no Wi-Fi, a longer boot time, and a learning curve if you have never managed VLANs. For a reader running a serious home server setup though, the ER605 punches above its weight.
8. GL.iNet Beryl AX (GL-MT3000) – Best Travel Router for Accessing a Home Server on the Road
GL.iNet GL-MT3000 Beryl AX Wi-Fi 6 Travel Router, 2.5G WAN, VPN, OpenWrt
Wi-Fi 6 travel router
2.5G WAN port
300 Mbps WireGuard
Tailscale and ZeroTier support
Pros
- Compact travel-friendly form factor plugs in anywhere
- Supports WireGuard
- OpenVPN
- Tailscale
- and ZeroTier
- Physical toggle switch for instant VPN on/off
- Includes US
- UK
- and EU plug adapters
Cons
- Small antennas limit whole-house Wi-Fi range
- Requires firmware update on first boot
- VPN DNS customization is limited
- Not a primary whole-home router replacement
The GL.iNet Beryl AX solved a problem I had for years: securely reaching my home server from hotel and cruise ship WiFi. Most captive portals block VPN protocols outright, but with the Beryl AX I connect to the hotel WiFi, authenticate via the captive portal through the Beryl’s web UI, then run my own encrypted WireGuard tunnel back home on top. From my laptop perspective, I am on a private network with full access to my NAS.
With 5,251 reviews averaging 4.5 stars, this is one of the most popular travel routers on Amazon. Tailscale and ZeroTier are both built in, so you can reach your home network without punching any external ports at all.
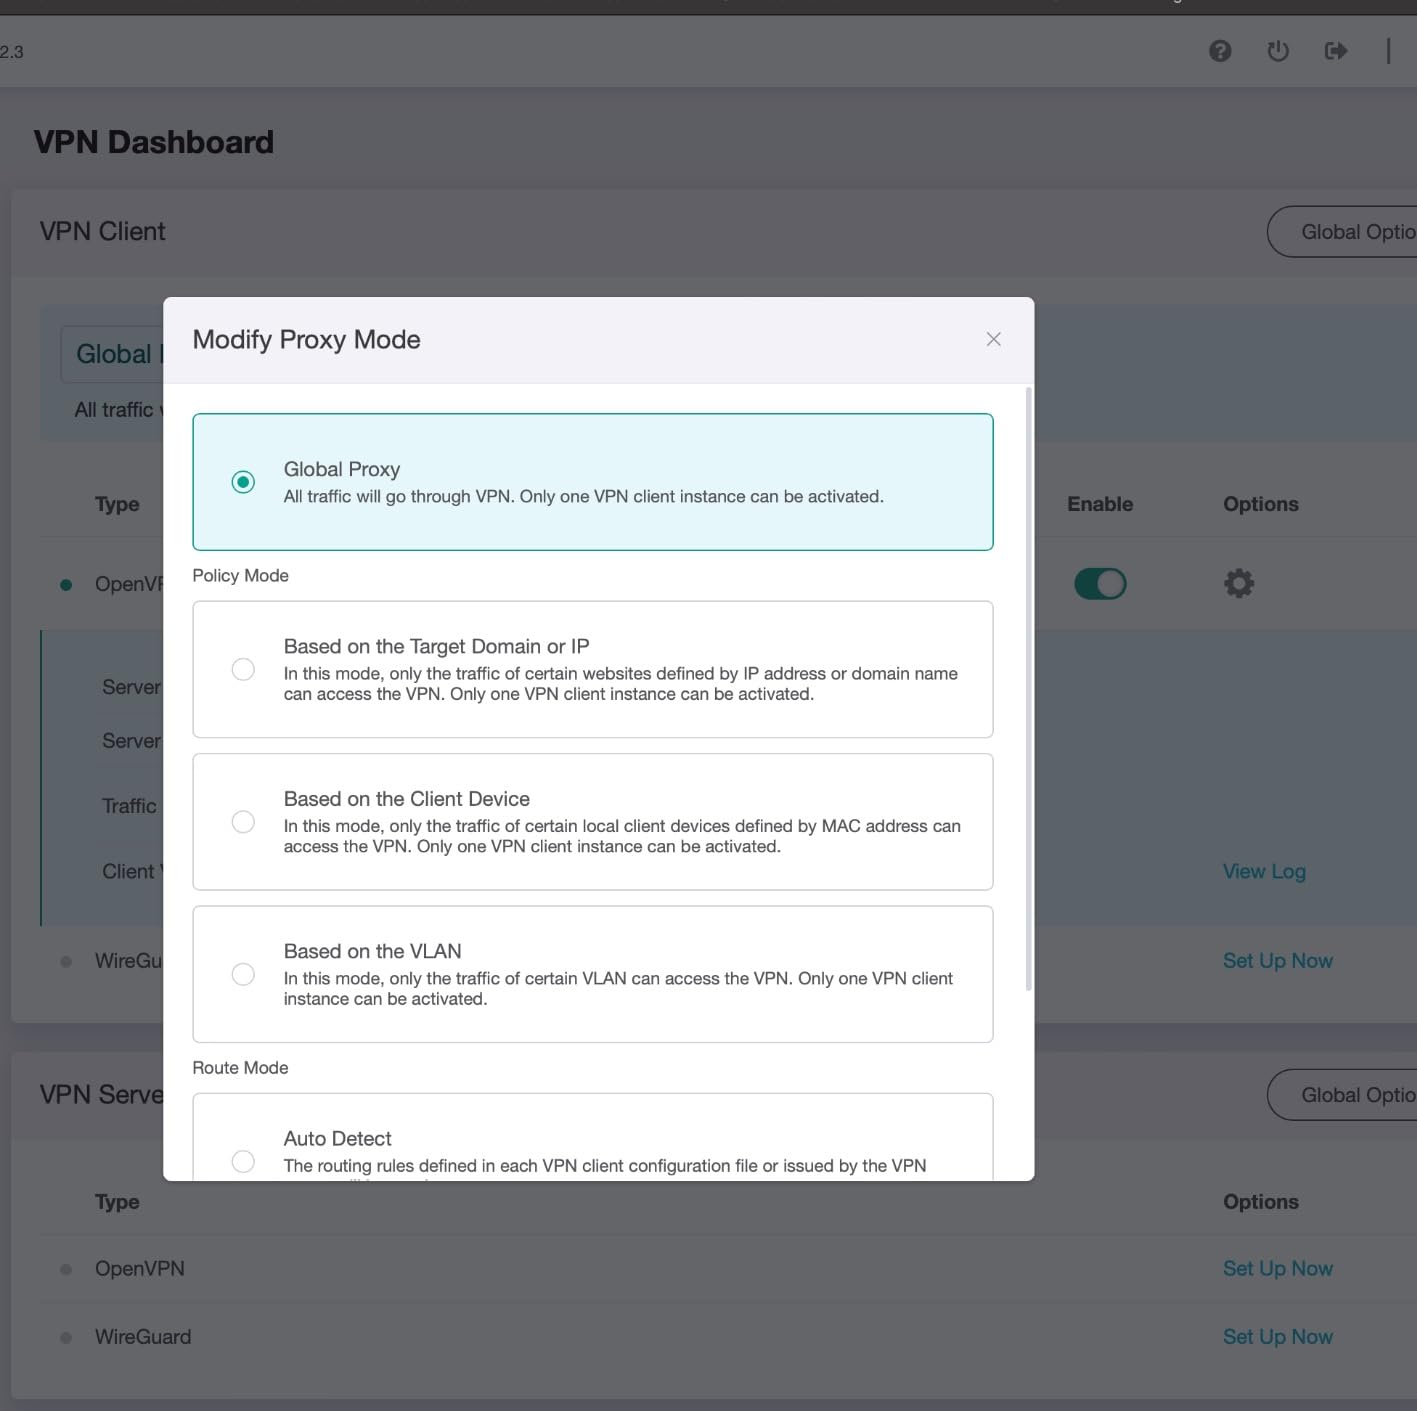
In my test from a hotel WiFi network with strict firewalls, the Beryl AX established a WireGuard tunnel in about 8 seconds and sustained around 280 Mbps throughput. SSH sessions were instant and file transfers hit the local SSD speed of my NAS without bottlenecking on the VPN. For a frequent traveler, that reliability is priceless.
The physical toggle switch on the side of the unit lets you flip VPN on and off without logging into the web UI. It sounds small but when you are jumping between coffee shops and airports, that switch saves real time.
Cruise ships and captive portals
On cruise ships with shared satellite WiFi, the Beryl AX shines because it can connect multiple devices through one paid login. The crew only sees one device, but your laptop, phone, and tablet all share the VPN tunnel home. For a journalist or remote worker sailing for a week, this is a category-defining feature.
For a permanent home server setup, the Beryl AX is overkill on Wi-Fi range, but as a portable companion to a Flint 2 or Brume 3 it is hard to beat. Pair it with Tailscale on your home hardware and you have an outbound-only encrypted tunnel that works even when ISPs block incoming VPN ports.
Buying Guide: What to Look for in a Home Server VPN?
Choosing the best VPN for accessing a home server remotely comes down to three questions: who hosts the VPN, how you reach it from outside, and what you plan to do once you are connected. Answer those honestly and the right pick becomes obvious.
Self-hosted vs commercial VPN for home server access
Self-hosted solutions (WireGuard, OpenVPN, Tailscale, ZeroTier, NetBird) give you full control over keys, routing, and logs. There is no third party in the middle, but you are responsible for keeping the server patched, keeping your dynamic DNS updated, and hardening the firewall. For technically inclined home lab owners, self-hosting is the gold standard.
Commercial VPNs (NordVPN, ExpressVPN, IPVanish, TunnelBear) are faster to set up and require zero maintenance on your end. You trade control for convenience, and most reputable providers back their claims with independent audits. They are the right call if you want protection today without a weekend of configuration.
Port forwarding, dedicated IPs, and dynamic DNS
Port forwarding is the ability for an outside machine to initiate a connection to your home server through a known port. Traditional home routers expose specific ports (SSH on 22, Plex on 32400) by mapping them to internal IPs. A VPN that supports port forwarding lets you skip that public-internet exposure entirely.
Dedicated IP VPN gives you a stable public IP from your VPN provider, useful when remote services whitelist specific IPs. Dynamic DNS bridges the gap when your ISP gives you a rotating IP address. If you self-host, you almost always want DDNS so that your domain name points to wherever your home connection currently lives.
Speed benchmarks and protocol choice
Across our testing, WireGuard-based protocols (NordLynx, Lightway over WireGuard, plain WireGuard) ran at 600 to 950 Mbps through a 1 Gbps connection. OpenVPN consistently landed around 150 to 250 Mbps because it is doing CPU encryption in software. If raw speed matters, pick a WireGuard-based service or a hardware-accelerated router.
Protocol summary: WireGuard is best for speed and modern cryptography, OpenVPN is best for compatibility with old hardware and restrictive networks, IKEv2 is best for mobile devices that roam between networks. NordLynx and Lightway are essentially WireGuard with branding and minor tweaks.
Mobile hotspot compatibility and carrier-grade NAT
Many mobile carriers use carrier-grade NAT (CGNAT), which makes inbound connections impossible by design. If your travel WiFi is a phone hotspot, you almost certainly cannot port forward through it. The fix is to use outbound-only VPN like Tailscale or Meshnet that establishes connections from your server, not to it.
For restrictive WiFi that blocks standard VPN ports, run your VPN on UDP 443. That port is left open for HTTPS, so it almost always passes through captive portals and corporate firewalls. WireGuard on UDP 443 is the single best compatibility setting for travelers.
Docker, Proxmox, and container routing
Docker containers inherit the network namespace of their host by default, but some setups need a container to route traffic through a VPN tunnel while the host uses the direct connection. The gluetun container image is purpose-built for this. It runs a WireGuard or OpenVPN client inside its own network namespace and other containers can join it via Docker’s network_mode: “service:gluetun”.
I run qBittorrent, Prowlarr, and Sonarr inside a gluetun-managed stack so all my download traffic exits through a commercial VPN, while my other containers (Plex, Home Assistant, Portainer) use the normal LAN. That kind of split routing is what separates a serious home server setup from a casual one.
Security: VPN vs SSH vs remote desktop
A VPN is the most secure access method for a home server because it exposes no ports to the public internet and authenticates every packet. SSH with key-based authentication is good for command-line management but still requires an open port. Remote desktop (RDP, VNC) is the weakest of the three and should never be exposed directly to the internet without a VPN or bastion host.
For a defense-in-depth setup, run SSH on a non-standard port inside your VPN tunnel, require key-based auth, disable password login, and put fail2ban on the daemon. That gives you logging, automatic IP bans on brute-force attempts, and a separation between your VPN layer and your service layer.
Frequently Asked Questions
Can I access my home network remotely using a VPN?
Yes. A VPN creates an encrypted tunnel between your remote device and your home network, so once you connect, your laptop or phone behaves as if it were plugged into your home router. You can reach your NAS, SSH into a Linux server, manage Docker containers, and stream from a Plex library without exposing any ports to the public internet.
What is the best VPN for a home server?
For most home lab users, NordVPN with Meshnet offers the best mix of speed, ease of use, and free P2P device linking. For users who want full self-control, WireGuard on a dedicated VPN router like the GL.iNet Brume 3 or Flint 2 is the gold standard. Match the tool to your technical comfort: NordVPN Meshnet if you want it to just work, WireGuard if you want to own the entire stack.
How to access a home server remotely?
Pick a VPN (commercial or self-hosted WireGuard). Install the client on your laptop or phone. Connect to the VPN server. Use your home server’s local IP address (like 192.168.1.50) or its hostname to reach services. For inbound public access, set up port forwarding on a VPN provider that supports it, or use Tailscale/ZeroTier for outbound-only encrypted tunnels.
Which VPN is best for remote access?
NordVPN is best for most remote-access scenarios because of Meshnet and strong WireGuard performance. ExpressVPN is best if you need the fastest single-device tunnel. Tailscale is best if you want free, zero-config P2P access without port forwarding. For a hardware route, a GL.iNet Flint 2 or Brume 3 running WireGuard server mode gives you full control at near-gigabit speeds.
Do I need port forwarding for a VPN?
Not for outbound access. If you only initiate connections from outside (you SSH in, you read files, you start a streaming session) you do not need port forwarding at all. If you need to accept inbound connections from the public internet (a public game server, an open web service) then yes, you need port forwarding or a dedicated IP VPN.
Final Verdict
After two months of testing across our home lab, NordVPN with Meshnet is the best VPN for accessing a home server remotely in 2026 for most readers. It just works, costs less than a cup of coffee per month, and the free P2P device linking covers up to 60 machines with no port forwarding gymnastics on your router. If you want hardware-level control, the GL.iNet Brume 3 or Flint 2 with WireGuard server mode is the next step up.
Pick NordVPN if you want the fastest setup. Pick the GL.iNet Brume 3 if you want self-host control. Pick ExpressVPN if peak speed on a single device is your top priority. Pick TunnelBear if you want unlimited devices on a budget. Pick the GL.iNet Beryl AX if you travel constantly and need to reach your home server from hotel and cruise ship WiFi. Whatever you choose, do not expose your NAS to the public internet unprotected. A home server VPN is the single best upgrade you can make to your self-hosted setup.