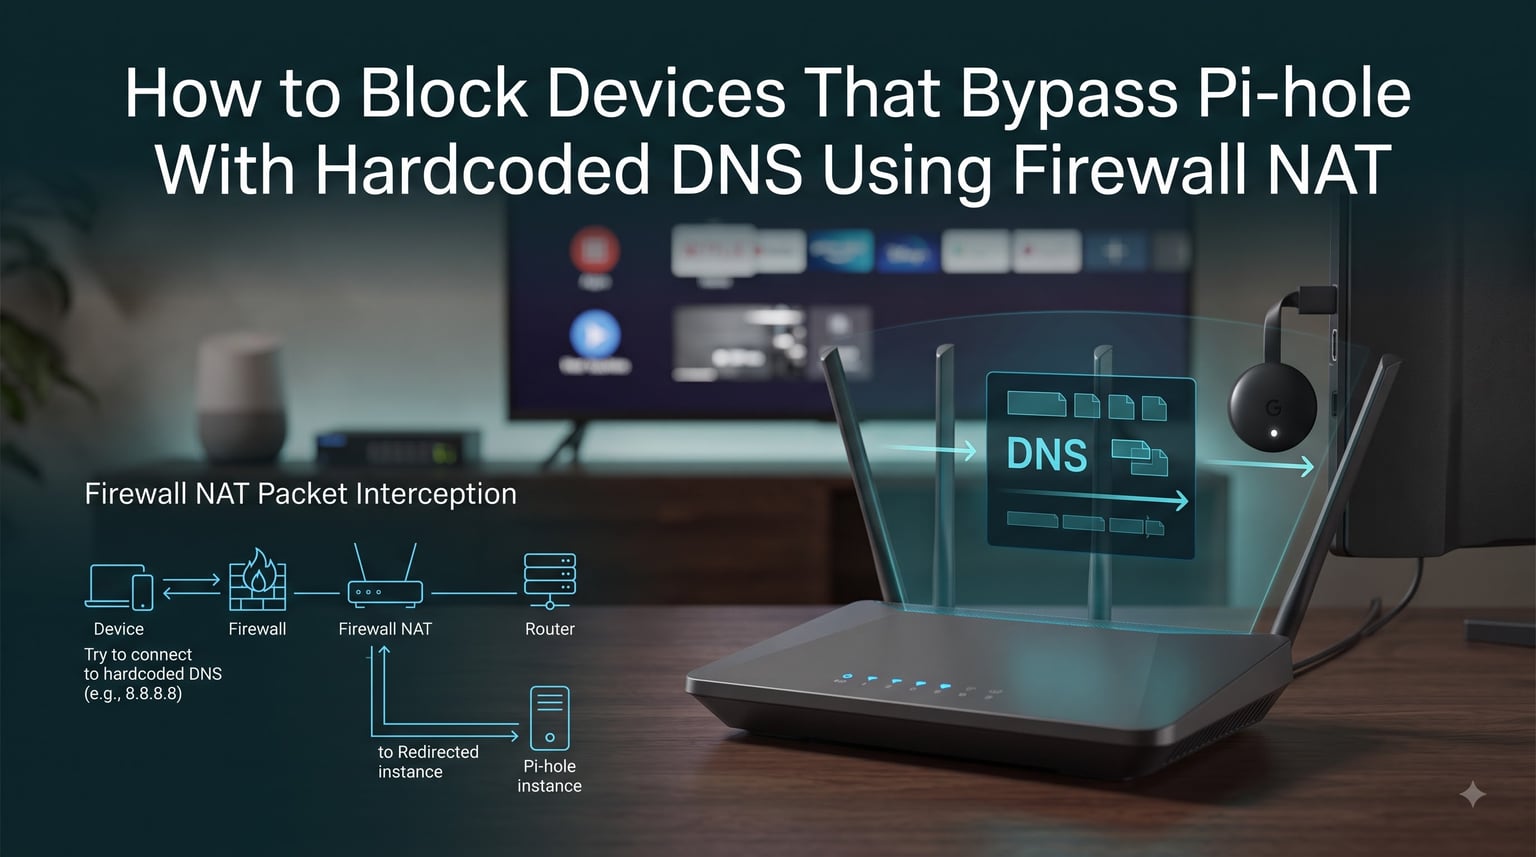
If you run Pi-hole and still see ads popping up on your smart TV, chances are a device on your network is bypassing your ad-blocker entirely. Many IoT devices, streaming sticks, and even smartphones ship with hardcoded DNS servers like 8.8.8.8 or 1.1.1.1 baked into their firmware. When that happens, your Pi-hole DNS sinkhole never sees the queries, and ads slip through. The fix is to block devices that bypass Pi-hole with hardcoded DNS using firewall NAT rules that intercept every DNS request on your network and force it through your Pi-hole. In this guide, I will walk you through exactly how that interception works and how to set it up on the most common router platforms.
I have been running Pi-hole for several years across two homes and a small office, and I have deployed NAT-based DNS redirection on MikroTik RouterOS, Ubiquiti EdgeRouter, and pfSense. The patterns below are the ones that survived contact with stubborn devices.
Table of Contents
Why Devices Bypass Pi-hole DNS?
Pi-hole works by sitting between your devices and the upstream DNS resolver. When a device asks the router for DNS, the router hands out the Pi-hole IP as the DNS server. Every query then hits Pi-hole, gets checked against blocklists, and only unblocked responses go upstream. This works beautifully for devices that respect DHCP.
The problem starts when a device ignores DHCP and talks directly to a public DNS server. Chromecast hardcodes 8.8.8.8. Roku sometimes uses 8.8.4.4. Apple devices fall back to 8.8.8.8 if your Pi-hole takes more than a second to respond. Google Home, Nest products, Ring doorbells, and many smart TVs follow the same pattern. They do this to ensure connectivity, but the side effect is that your Pi-hole never sees those queries, so ads slip through and analytics keep flowing.
One Pi-hole community user tracked 150 rogue DNS requests in a single 12-hour window from devices that should have been filtered. The DNS query log showed traffic to 8.8.8.8, 1.1.1.1, and 9.9.9.9 from devices that DHCP said were pointed at Pi-hole. That is the bypass problem in the wild.
How NAT Redirection Intercepts DNS Traffic
Network Address Translation (NAT) is the router’s core job. Destination NAT (dstnat) rewrites where a packet is going, while source NAT (srcnat or masquerade) rewrites where it came from. For DNS interception, we use dstnat to grab every DNS packet leaving your LAN and rewrite its destination IP to your Pi-hole’s address. The device thinks it is talking to 8.8.8.8, but the router silently swaps in your Pi-hole IP before forwarding the packet.
DNS lives on port 53 using both UDP and TCP. UDP handles normal queries, and TCP handles large responses plus zone transfers. Your NAT rule must catch both protocols. Most guides cover only UDP and leave TCP traffic flowing freely to Google, which is a leak. Catch both.
Here is the packet flow once a NAT rule is in place:
Chromecast sends a DNS query to 8.8.8.8 on UDP port 53.
The router inspects the outbound packet, sees destination port 53, and triggers your dstnat rule.
The router rewrites the destination IP from 8.8.8.8 to your Pi-hole IP (for example, 192.168.1.10).
Pi-hole receives the query, checks its blocklists, and replies with the proper (or blocked) answer.
The reply returns to the Chromecast through the same connection, transparently.
Because the rewrite happens at the network layer, the device has no idea its DNS server changed. This is why NAT redirection is the only reliable fix for hardcoded DNS bypass.
Step-by-Step Firewall NAT Rule Configuration
The configuration differs by router platform, but the logic is identical. Below are working examples for the three most common platforms. Replace 192.168.1.10 with your actual Pi-hole IP.
MikroTik RouterOS Configuration
RouterOS exposes NAT as a two-step chain: dst-nat to redirect, then srcnat to masquerade the reply so the device sees a response from the IP it queried. Open a terminal on your MikroTik and run:
/ip firewall nat
add chain=dstnat protocol=udp dst-port=53 action=redirect to-addresses=192.168.1.10
add chain=dstnat protocol=tcp dst-port=53 action=redirect to-addresses=192.168.1.10
add chain=srcnat protocol=udp src-port=53 out-interface=bridge-lan action=masquerade
add chain=srcnat protocol=tcp src-port=53 out-interface=bridge-lan action=masquerade
The first two rules redirect DNS to Pi-hole. The last two ensure the reply comes back through the router so the device believes it is talking to the original server. This pattern comes from the MikroTik community and has been battle-tested on thousands of home networks.
Ubiquiti EdgeRouter Configuration
EdgeRouter uses Vyatta-style commands. In the CLI:
configure
set service nat rule 1 description "Redirect DNS UDP to Pi-hole"
set service nat rule 1 inbound-interface eth0
set service nat rule 1 protocol udp
set service nat rule 1 destination port 53
set service nat rule 1 inside-address address 192.168.1.10
set service nat rule 1 inside-address port 53
set service nat rule 1 type destination
set service nat rule 2 description "Redirect DNS TCP to Pi-hole"
set service nat rule 2 inbound-interface eth0
set service nat rule 2 protocol tcp
set service nat rule 2 destination port 53
set service nat rule 2 inside-address address 192.168.1.10
set service nat rule 2 inside-address port 53
set service nat rule 2 type destination
commit
save
If your Pi-hole is on the same subnet, you also need a masquerade rule for return traffic. Add this in /config/config.boot or via the GUI under Firewall/NAT.
pfSense Configuration
pfSense handles this through NAT port forwards and outbound NAT. Go to Firewall > NAT > Port Forward and create a rule on the LAN interface:
Interface: LAN
Protocol: UDP/TCP
Destination port: 53
Redirect target IP: 192.168.1.10
Redirect target port: 53
Description: Force DNS to Pi-hole
Then under Firewall > NAT > Outbound, switch to hybrid mode and add a rule for traffic from the Pi-hole back to LAN clients on port 53, set to manual or hybrid NAT with the LAN address as the translation source. This guarantees reply packets reach the device properly.
If you have two Pi-hole servers for redundancy, use round-robin or a firewall address list with both IPs. The vdaluz.com RouterOS guide explains why PCC (Per Connection Classifier) load balancing does not work well for UDP DNS, and recommends the nth round-robin matchers instead.
Redirect Versus Block: Which Approach Wins
You have two strategies for stopping bypass traffic: redirect it to Pi-hole or block it outright. Blocking kills the connection, which can break smart TVs that need DNS for firmware updates and streaming handshakes. Redirecting preserves functionality while still routing every query through your blocklists.
Redirect is almost always the right choice. The only exception is when you want to enforce an air-gapped policy and do not care if the device loses features. For typical home networks, redirect wins because you keep all the smart home features without losing ad blocking.
Testing and Verifying Your NAT Rules
Once the rules are in place, verify them from a client. The fastest test is dig or nslookup. From a device that previously bypassed Pi-hole, run:
dig @8.8.8.8 example.com
nslookup example.com 8.8.8.8
If your NAT rules work, the query will return your Pi-hole’s reply, and the answer section will show a different IP than what 8.8.8.8 would normally return for blocked domains. You should also see the query in Pi-hole’s query log under the device’s name or IP. If the answer comes back from Google’s actual server, the NAT rule is not matching.
Other useful checks:
Tail the Pi-hole log (
tail -f /var/log/pihole.log) while making DNS requests.Check the router’s connection tracking table for rewritten destinations.
Use
tcpdumpon the Pi-hole box to confirm packets are arriving.Run a network-wide scan with
nmap --script dns-nsidto see which resolvers respond.
Common Devices That Hardcode DNS
Based on community reports and my own logs, the usual offenders include:
Google Chromecast and Google Nest Hub
Roku streaming sticks and Roku TVs
Apple TV, iPhones, and Macs (fallback DNS)
Amazon Fire TV devices
Samsung and LG smart TVs
Ring and Nest doorbells and cameras
Xbox and PlayStation consoles
Echo and Google Home speakers
Some mesh Wi-Fi satellite nodes
Any of these can route around your Pi-hole until the NAT rules go live. Once NAT redirection is active, every one of them falls into line without further configuration.
Advanced Topics: DoT, DoH, IPv6, and FastTrack
Plain DNS over port 53 is not the whole story anymore. Some devices and apps now use DNS over TLS (DoT) on port 853 or DNS over HTTPS (DoH) on port 443. These encrypted protocols bypass your NAT rules because the traffic looks like normal HTTPS. To stop them, you need additional firewall rules blocking outbound connections to known DoT/DoH servers, or you can use SNI filtering on your firewall to drop the TLS handshakes.
IPv6 is the other silent leak. If your network advertises IPv6 and your devices prefer it, they can query 2001:4860:4860::8888 (Google’s IPv6 DNS) directly, completely ignoring your IPv4 NAT. The fix is either to disable IPv6 on your LAN or to add IPv6 NAT rules mirroring the IPv4 ones. Most modern routers support IPv6 NAT, so mirror your configuration on the v6 firewall.
On RouterOS specifically, watch out for FastTrack. FastTrack is a performance feature that lets certain connections bypass the firewall entirely. DNS traffic is one of the FastTrack-eligible types, which means your NAT rules might never see the packet. Disable FastTrack for DNS by adding a connection mark exception in /ip firewall mangle, or disable FastTrack globally if performance allows.
Frequently Asked Questions
Is Pi-hole still relevant in 2026?
Yes. Pi-hole remains a popular network-wide ad blocker in 2026. It still blocks ads, trackers, and malware domains at the DNS layer, and it works alongside browser-based blockers. As long as DNS-level filtering is effective, Pi-hole is relevant, especially when combined with NAT redirection to handle hardcoded DNS clients.
How can I force all devices on my network to use Pi-hole?
Configure a destination NAT rule on your router that redirects all outbound UDP and TCP traffic on port 53 to your Pi-hole IP. On RouterOS, use chain=dstnat with protocol=udp and protocol=tcp entries pointing to your Pi-hole. On EdgeRouter, create service NAT rules for port 53. On pfSense, use a port forward. Then verify with dig @8.8.8.8 and check the Pi-hole query log.
What devices have hardcoded DNS?
Common offenders include Chromecast, Roku, Apple TV, Samsung and LG smart TVs, Ring and Nest cameras, Amazon Fire TV, Google Home, Echo, Xbox, and PlayStation. Apple devices do not hardcode but fall back to 8.8.8.8 if your DNS is slow. Mesh Wi-Fi nodes sometimes use hardcoded resolvers too.
Can Pi-hole be used as a firewall?
No. Pi-hole is a DNS sinkhole, not a firewall. It cannot block traffic based on ports or IPs. To block devices that bypass Pi-hole, you need a router or firewall with NAT capabilities. Pi-hole handles the DNS filtering, and the router handles the traffic interception.
How does NAT DNS redirection work?
The router inspects every outbound packet on port 53 and rewrites the destination IP from the hardcoded server (like 8.8.8.8) to your Pi-hole IP. The device believes it is talking to the original server, but the query lands at Pi-hole instead. A matching srcnat or masquerade rule ensures the reply flows back to the device transparently.
What is the best way to force DNS through Pi-hole?
The best method is destination NAT on port 53 (both UDP and TCP) pointing to your Pi-hole, with a matching masquerade rule for return traffic. Add IPv6 NAT rules to cover v6 leaks, and disable FastTrack on RouterOS to avoid bypass. Then test with dig and nslookup from a device that previously bypassed Pi-hole.
Conclusion
Blocking devices that bypass Pi-hole with hardcoded DNS using firewall NAT rules is the only way to get complete coverage on a network full of stubborn IoT devices. DHCP alone cannot do it, because those devices ignore DHCP. NAT redirection works because it intercepts packets at the router, where every DNS query must pass through regardless of what the device thinks it should do.
Pick your router platform, apply the dstnat rule for UDP and TCP port 53, add a masquerade or srcnat rule for the reply traffic, then verify with dig and nslookup. Cover IPv6 if your network uses it, watch out for FastTrack on RouterOS, and consider SNI filtering for DoH bypass attempts. Once these pieces are in place, your Pi-hole will see every query on your network, and the ads will stop.
If you are setting this up for the first time, give yourself a weekend. The configuration is fast, but the verification matters more than the typing. I keep a short checklist of test domains and known hardcoded resolvers that I run after any router change, and that habit has caught more regressions than I want to admit.