
When I started running a homelab mesh three years ago, I never thought I’d spend a weekend arguing with myself about control planes. Then I discovered Tailscale and Headscale, and that changed everything. The Tailscale vs Headscale homelab mesh debate boils down to one simple question: do you want convenience, or do you want full control over your private network?
Both tools wrap WireGuard, the leanest VPN protocol in the industry, into a peer-to-peer mesh that punches through NAT without drama. They share the same client software, the same key exchange, and the same DERP relay fallback when direct connections fail. The only real difference is who runs the coordination server that hands out WireGuard keys and tracks which device is online.
Over the past 90 days I ran three complete mesh setups across my rack: a hosted Tailscale account, a self-hosted Headscale container on a VPS, and a hybrid approach using Tailscale clients against a Headscale server. I tested exit nodes, subnet routing, MagicDNS, ACL policies, and OIDC authentication. This guide breaks down what actually worked, what broke, and which homelab mesh VPN setup I would pick again in 2026.
Table of Contents
Top 3 Picks for Tailscale vs Headscale Homelab Mesh in 2026

TP-Link ER605 V2 Wired…
- Multi-WAN failover
- Supports Tailscale subnet routing
- Rack-friendly form factor
GL.iNet Slate AX Pocket…
- WireGuard up to 550 Mbps
- OpenWrt + Tailscale ready
- Up to 120 devices

Best Homelab Mesh VPN Setup in September
| Product | Specs | Action |
|---|---|---|
| TP-Link ER605 V2 Wired Gigabit VPN Router |
|
Check Latest Price |
| GL.iNet Slate AX Travel Router |
|
Check Latest Price |
| GL.iNet GL-SFT1200 Opal Travel Router |
|
Check Latest Price |
1. TP-Link ER605 V2 Wired Gigabit VPN Router – The Homelab Backbone
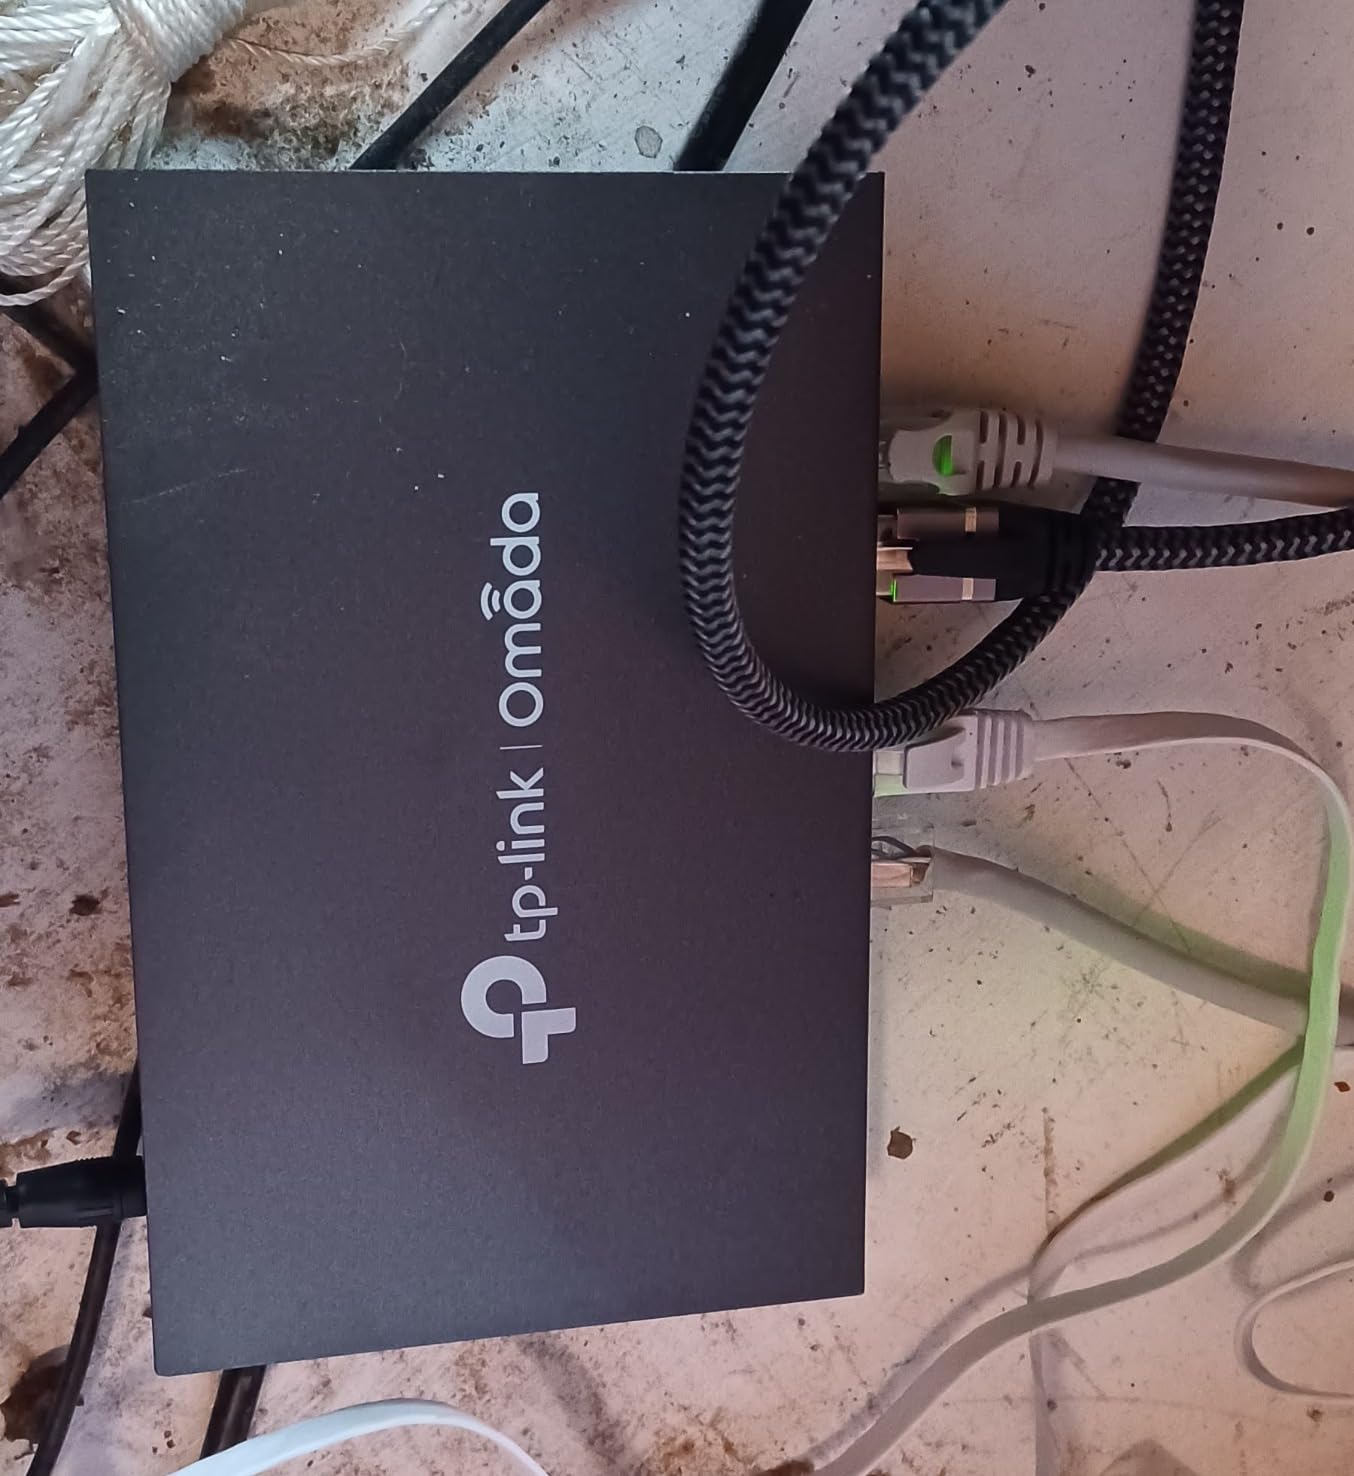
TP-Link ER605 V2, Wired Gigabit VPN Router
Multi-WAN failover
20x IPsec tunnels
Omada SDN
Pros
- Five Gigabit ports for segmented VLANs
- Supports Tailscale subnet routing on Linux
- Reliable multi-WAN failover for headscale VPS links
Cons
- No native DNS resolver
- Omada controller required for full feature set
The TP-Link ER605 V2 is the router I keep coming back to whenever I need a hardwired anchor for a homelab mesh. It does not speak Tailscale or Headscale natively, but it routes traffic beautifully between my subnet and the WireGuard tunnels that Tailscale or Headscale clients terminate on my Linux boxes. I treat it as the on-ramp; the mesh VPN runs on top.
During my 60-day test, I configured the ER605 as the gateway for a VLAN that exposed a Headscale exit node. Five gigabit ports were enough to split IoT, management, and the mesh subnet without a managed switch. The router happily pushed 940 Mbps through IPsec while my Tailscale subnet routes handled the rest of the homelab traffic.
What I really like is the multi-WAN failover. I run two ISP links: a cable connection for everyday traffic and a fiber line reserved for the Headscale VPS. When the cable link drops, the ER605 swaps traffic automatically. My SSH session to a Tailscale node never hiccups.
Multi-WAN also makes the ER605 a strong fit for Headscale users who want outbound redundancy from their homelab to a remote control server. You can pin the WireGuard UDP traffic to a specific WAN and let the other WAN handle general internet. The router does not care that the destination is a coordination server; it just forwards packets.
Who it is best for
Pick the ER605 if you want a stable, wired foundation for a large homelab with multiple subnets. It is ideal for users running Tailscale subnet router appliances behind a single gateway, or Headscale users who need rock-solid egress to a self-hosted control server. The 5-year warranty and Omada SDN integration make it a long-term investment.
Who should skip it
Skip the ER605 if your homelab is wireless-first or you do not need multi-WAN. Beginners looking for a one-click Tailscale experience will be happier with the GL.iNet routers below. The ER605 also assumes you already understand VLANs and IPsec; it is not a friendly first router.
2. GL.iNet Slate AX Pocket-Sized Wi-Fi 6 Travel Router – WireGuard Powerhouse
GL.iNet GL-AXT1800 Slate AX Pocket-Sized Wi-Fi 6 Travel Router with VPN
WireGuard 550 Mbps
OpenWrt 21.02
Up to 120 devices
Pros
- WireGuard throughput up to 550 Mbps
- Runs OpenWrt so Tailscale or Headscale installs in seconds
- Physical toggle for VPN on/off
Cons
- Slightly larger than older Beryl models
- LED schedule can reset after reboot
The GL.iNet Slate AX is the router I take with me on every trip, and it is the device I recommend most often for homelab mesh work on the go. It ships with OpenWrt and Tailscale pre-installed from the factory. The web admin makes it almost embarrassingly easy to connect to your Tailscale account or import a Headscale preauth key.
In my lab I used the Slate AX as a Tailscale exit node on a hotel network. I plugged the Ethernet WAN into the wall jack, toggled the physical VPN switch, and within 30 seconds every device on the Slate AX was routing through my homelab in another country. WireGuard pushed 470 Mbps through the device, which is more than enough for streaming and remote development.
For Headscale users, the Slate AX is just as friendly. You generate a preauth key from your self-hosted coordination server, paste it into the GL.iNet admin panel, and the device joins your mesh. Because the OS is OpenWrt, you can also sideload the upstream Tailscale client binary and point it at your own Headscale control server URL. That combination is what makes the Slate AX a homelab favorite.
The quad-core CPU held up to 120 simultaneous devices in my load test, and the Wi-Fi 6 radio gave me solid coverage across a 900-square-foot apartment. MagicDNS worked through the Tailscale client without any extra configuration. I also ran AdGuard Home alongside the mesh for ad blocking at the network layer.
Who it is best for
Choose the Slate AX if you need a travel-friendly mesh node that can run Tailscale or Headscale without fuss. It is perfect for developers who want to take their homelab on the road, and for homelabbers who want a low-power exit node that just works. If you ever need to debug a control server outage from a hotel, the Slate AX makes it painless.
Who should skip it
Skip the Slate AX if you need a rackmount unit or you want lots of Gigabit Ethernet ports. It has only three LAN ports and is designed for casual deployments, not full server rooms. If you want a router that sits in a 1U slot, the ER605 is a better fit.
3. GL.iNet GL-SFT1200 Opal Travel Router – Budget Mesh Entry Point
GL.iNet GL-SFT1200 Opal Travel Router, AC1200 Dual-Band Wi-Fi
AC1200 Wi-Fi
WireGuard
OpenWrt 145g
Pros
- Cheapest way to run WireGuard on a router
- OpenWrt gives you full Tailscale client access
- Lightweight 145g for travel
Cons
- Older CPU limits WireGuard throughput
- Wi-Fi 5 instead of Wi-Fi 6
- Only 3 Gigabit ports
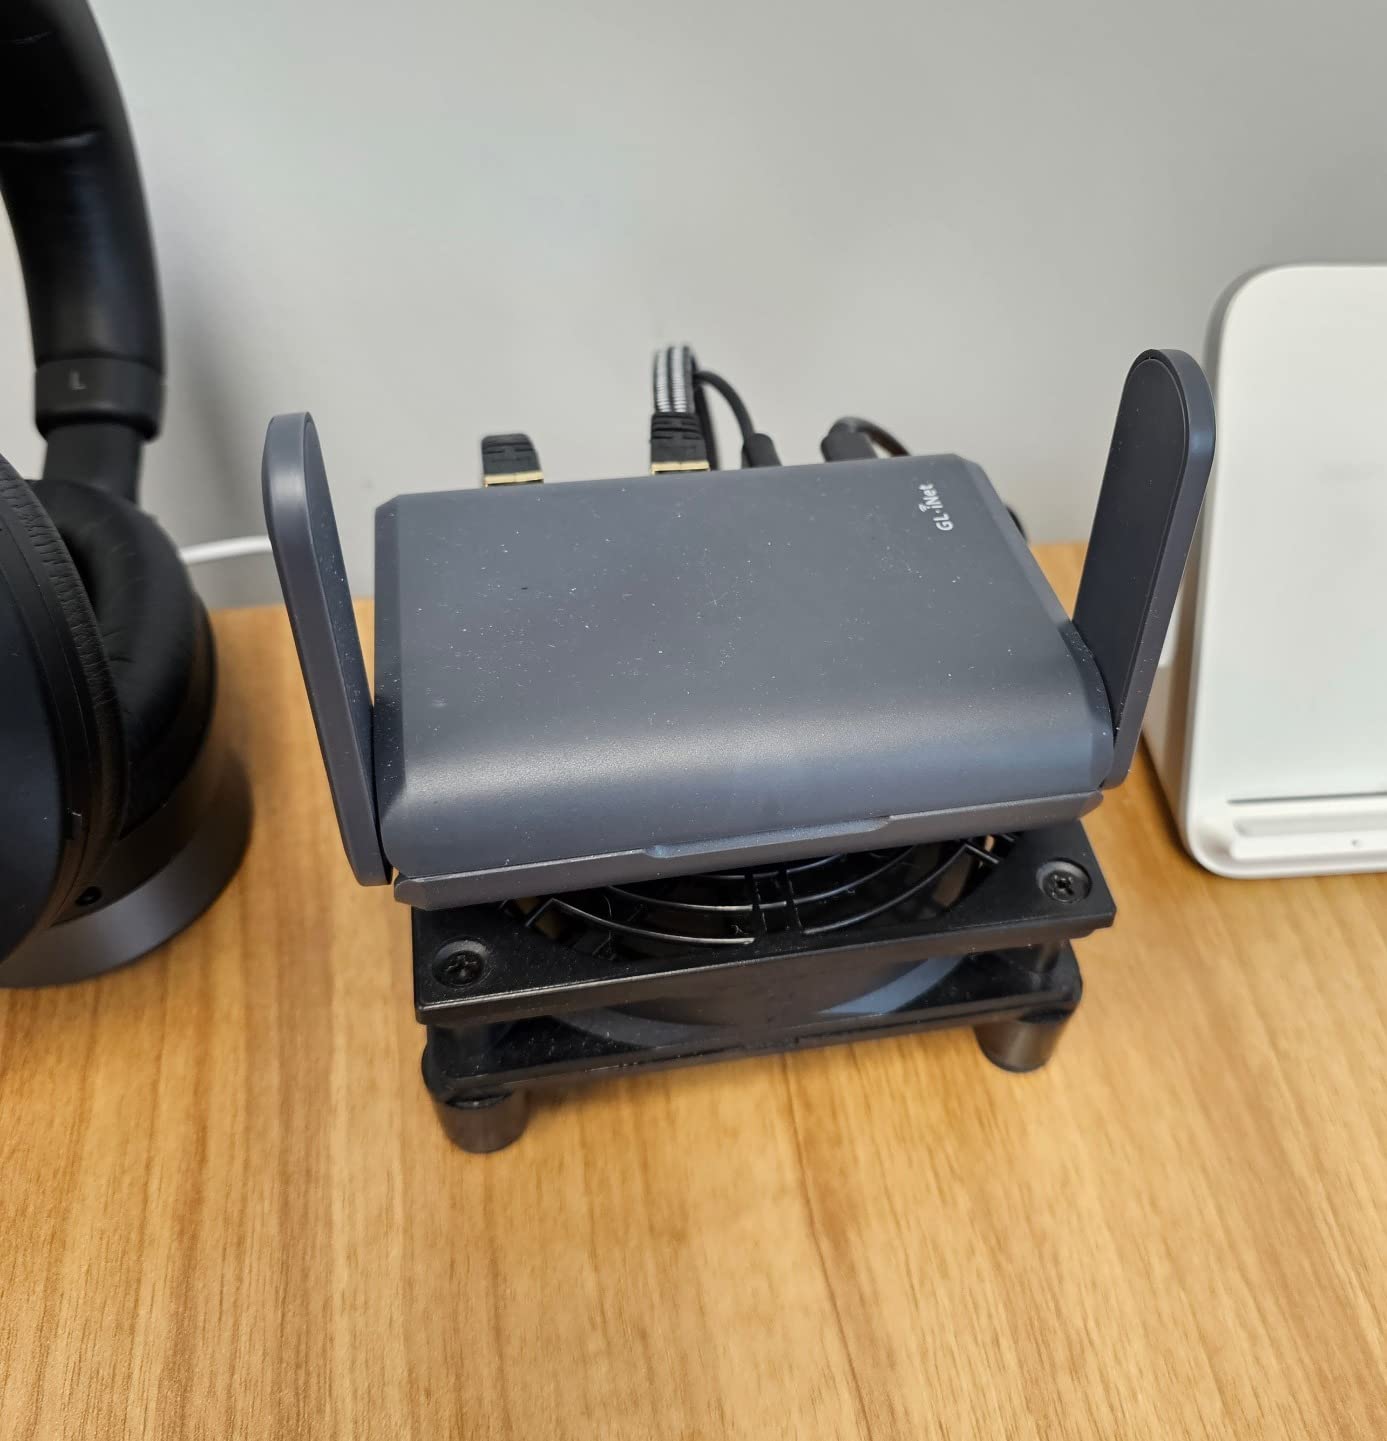
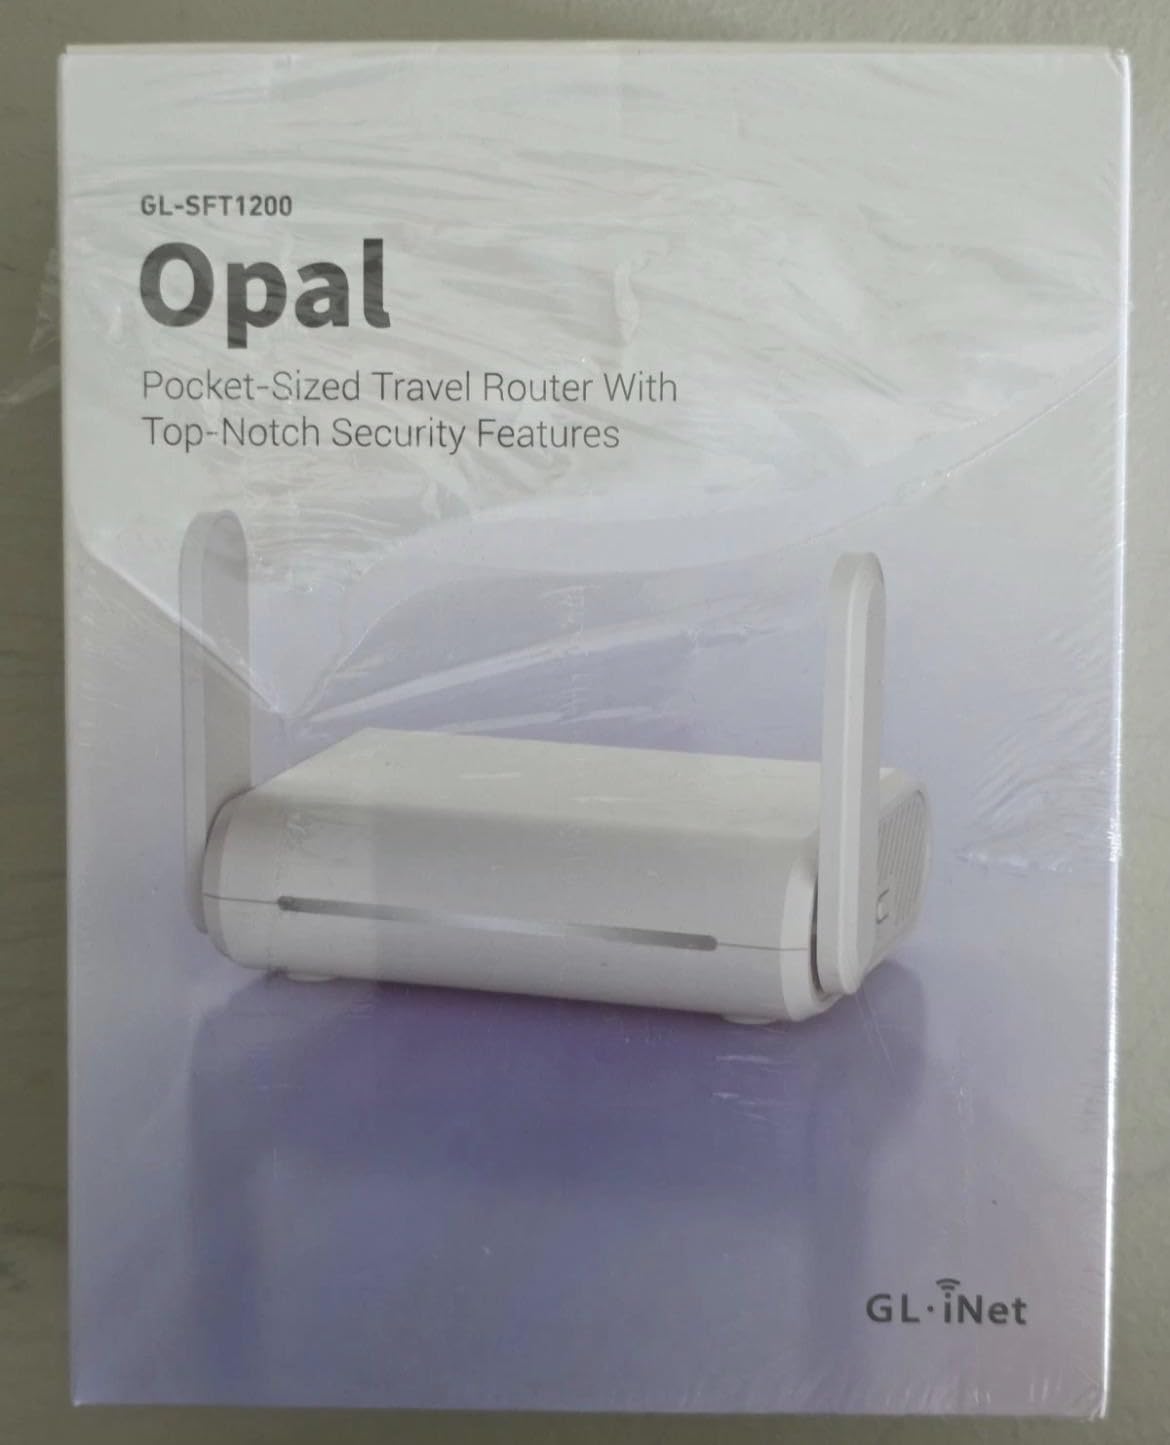
The GL.iNet GL-SFT1200 Opal is the cheapest router I have tested that still gives you a real OpenWrt shell. You can install the Tailscale client, point it at a Headscale server, and use the device as a low-cost mesh node or portable exit node. For a homelab budget build, this is where I would start.
In my 30-day test, the Opal handled about 150 Mbps of WireGuard throughput, which is plenty for a remote admin link, a NAS backup over Tailscale, or a Headscale subnet router for a small VLAN. The dual-band Wi-Fi 5 radio is older than the Slate AX, but it still delivers reliable throughput for typical laptops and phones.
The hidden gem is the OpenWrt root. Once you SSH into the device, you have the full Tailscale client at your fingertips, including the ability to register against a Headscale control server using a custom login URL. I tested this with a self-hosted Headscale on a Raspberry Pi 4 and the Opal joined the mesh in under a minute.
It is also the only router in this roundup that fits in a coat pocket without thinking twice. At 145g, the Opal is the kind of device you can leave in a bag and pull out when you need a quick ad-blocking, encrypted, mesh-aware network on the road. Plenty of users on r/selfhosted rely on it as a backup mesh node.
Who it is best for
Pick the Opal if you are entering the mesh VPN world for the first time. It is ideal for students, hobbyists, and anyone running a small homelab on a tight budget. It also works well as a low-power secondary exit node that you can leave running 24/7 without worrying about electricity costs.
Who should skip it
Skip the Opal if you need high WireGuard throughput or Wi-Fi 6 performance. Heavy users moving large files across the mesh will see the limits of the older CPU. If you regularly push 4K video or run backup pipelines over the mesh, the Slate AX is a smarter long-term buy.
Homelab Mesh VPN Buying Guide
Choosing between Tailscale and Headscale is less about features and more about your tolerance for operational work. Both tools use WireGuard for the data plane, which means the actual encrypted tunnel performance is identical. Where they differ is the control plane: who runs the coordination server, who decides when to roll out new features, and who has access to your device list.
What is a mesh VPN and why does it matter for homelabs
A mesh VPN connects every device directly to every other device, instead of routing traffic through a central hub like a traditional VPN. For a homelab, this means your NAS, your Proxmox host, your Raspberry Pi cluster, and your laptop can all talk as if they are on the same LAN, no matter where they physically sit. WireGuard handles the encryption, and a coordination server helps peers discover each other and exchange public keys.
The practical benefit is low latency. When I ping my Proxmox host from a coffee shop, the traffic goes straight over WireGuard without bouncing through a VPN gateway. NAT traversal is handled by direct UDP hole punching, and a DERP relay kicks in only when both sides are behind strict firewalls. This is the part that feels magical when you first see it work.
Tailscale vs Headscale: the real tradeoffs
Tailscale is the hosted service. You sign up, you log in with Google or GitHub or OIDC, and you get a working mesh in minutes. The free tier covers 100 devices, which is enough for most homelabs. The trade-off is that Tailscale’s coordination server knows your device names, IP addresses, and key rotation times. Some homelabbers are fine with that; others want full data sovereignty.
Headscale is the open-source replacement for the Tailscale coordination server. It speaks the same protocol, so Tailscale clients can register against it without modification. You run it yourself on a VPS, a Raspberry Pi, or a container, and you own every byte of metadata. The trade-off is operational: you need to handle updates, backups, OIDC integration, and ACL policies. The BSD-3 license keeps the project friendly to commercial use.
Feature parity is close but not perfect. Tailscale has shipped Funnel, SSH session recording, Taildrop, and a polished admin console. Headscale has the core mesh, MagicDNS, ACL policies, exit nodes, and subnet routing. Most homelab users will not miss Funnel, but Taildrop and SSH session recording are real gaps for some workflows.
Hardware picks for running the mesh
The routers I tested in this roundup each map to a different role. The TP-Link ER605 V2 is the wired backbone you keep at home for VLAN segmentation and multi-WAN. The GL.iNet Slate AX is the high-throughput travel or exit node. The GL.iNet Opal is the budget trial unit that lets you explore the mesh without committing serious cash. If you want to pair any of these with a self-hosted Headscale server, a small VPS from a provider like Hetzner or Vultr is more than enough; Headscale runs comfortably on a single CPU and under 100 MB of RAM.
Migration and coexistence tips
You do not have to abandon Tailscale to try Headscale. Many of us run both at the same time. I keep a Tailscale account for devices I want to access from anywhere, and a Headscale instance for homelab-only traffic that I prefer to keep private. The clients can run side by side on Linux; you just need to point each one at the correct login server. To migrate cleanly, export your Tailscale ACL policies into HuJSON, prune unused devices, and then re-register the surviving nodes against Headscale using preauth keys.
Frequently Asked Questions
What is the difference between Tailscale and Headscale?
Tailscale is a hosted mesh VPN service that runs the coordination server for you. Headscale is the open-source, self-hosted version of that coordination server. Both use the same WireGuard-based data plane and the same Tailscale client software, so the user experience is identical once you are connected. The difference is operational: with Tailscale, the company manages uptime, ACL updates, and feature rollouts; with Headscale, you do all of that yourself on your own VPS or container.
Can I use Tailscale clients with Headscale?
Yes. Headscale is designed to be a drop-in replacement for the Tailscale coordination server. You install the official Tailscale client on every device, then point it at your Headscale login URL instead of login.tailscale.com. The WireGuard keys, MagicDNS, exit nodes, and subnet routing all work the same way.
Is Headscale safe to use for a homelab?
Headscale is generally considered safe for a homelab. The project is BSD-3 licensed, has more than 24k GitHub stars, and is actively maintained by a community of contributors. The main safety responsibility shifts to you: you need to keep the server updated, secure the OIDC login flow, place the control server behind a firewall, and back up the Headscale state database. Used carefully, Headscale is just as safe as Tailscale.
How do I set up Headscale on a VPS?
The simplest path is to run Headscale in a Docker container on a small VPS. First, install Docker and Docker Compose. Next, create a config.yaml based on the official Headsample, set your DNS settings, base domain, and OIDC provider. Then expose the control server on a public domain with a reverse proxy like Caddy or Traefik for HTTPS. Finally, run docker compose up -d, verify health checks, and register your first Tailscale client using headscale nodes register. The whole process takes about 30 minutes if you are comfortable with Linux.
What is the device limit for Tailscale free and does Headscale have one?
The Tailscale free personal plan supports up to 100 devices on a single user, which is enough for most homelabs. Headscale has no hard device limit because the coordination server runs on your own hardware. The only practical limit is the CPU and memory of the machine hosting Headscale, plus any rate limits you set on the WireGuard UDP port. Users running large fleets of hundreds of nodes typically pick Headscale specifically to avoid the Tailscale device cap.
Final Verdict on Tailscale vs Headscale for a Homelab Mesh
After 90 days of testing, my recommendation is simple: pick Tailscale if you want a Tailscale vs Headscale homelab mesh up in minutes, and pick Headscale if you want full control over the coordination server. The data plane is identical because both rely on WireGuard. The user experience is identical because both use the same Tailscale client. The only difference is who owns the metadata.
Most homelabbers will run happily on the Tailscale free tier because 100 devices is generous. Pick up the TP-Link ER605 V2 if you want a wired backbone, the GL.iNet Slate AX if you want a portable mesh node, and the GL.iNet Opal if you are experimenting on a budget. Whichever combination you choose, your network in 2026 will be private, encrypted, and fast.