I built my first homelab with nothing but a consumer router and a switch. Six months later, after a curious roommate accidentally exposed my entire network to the internet, I was scrambling to learn what a proper firewall appliance actually does.
A firewall appliance is a dedicated hardware device that filters network traffic between your homelab and the outside world. Unlike the WiFi router from your ISP, it runs real firewall software (think pfSense, OPNsense, or FortiOS), giving you VLANs, VPN servers, IDS/IPS, and rule-based traffic control. It combines routing and security in one box built for people who actually want to learn networking instead of just plugging in cables.
I spent the last three months testing ten of the best firewall appliances for home labs, including fanless N100 mini PCs, enterprise-grade FortiGates, and budget-friendly SMB routers. My goal: find devices that deliver real network security without sounding like a jet engine or requiring a PhD to configure. Whether you’re learning network security, segmenting IoT devices, or just tired of your ISP router blocking you from doing cool stuff, this guide covers what actually works in 2026.
Table of Contents
Top 3 Picks for Home Lab Firewalls in 2026

Netgate 1100 pfSense+ Secur…
- Pre-loaded pfSense+
- 650 Mbps throughput
- Fanless silent design
- 3x GbE ports
- Lifetime software updates

TP-Link ER605 V2 Wired…
- Multi-WAN support
- 20 IPsec tunnels
- SPI firewall
- 5-year warranty
- Omada SDN ready

MOGINSOK N100 Fanless Mini…
- Intel N100 CPU
- 4x 2.5GbE ports
- AES-NI support
- 8GB DDR5 RAM
- pfSense pre-installed
Best Firewall Appliances for Home Labs in October
| Product | Specs | Action |
|---|---|---|
| Netgate 1100 pfSense+ Security Gateway |
|
Check Latest Price |
 FortiGate-40F Firewall Appliance |
|
Check Latest Price |
 FortiGate-60F Firewall Appliance |
|
Check Latest Price |
| TP-Link ER605 V2 VPN Router |
|
Check Latest Price |
 TP-Link ER707-M2 Multi-Gigabit |
|
Check Latest Price |
| MOGINSOK N100 Fanless Mini PC |
|
Check Latest Price |
 SonicWall TZ280 Next-Gen Firewall |
|
Check Latest Price |
 VNOPN J3710 Fanless Firewall PC |
|
Check Latest Price |
 Sharevdi J4105 Fanless Mini PC |
|
Check Latest Price |
 Zyxel USG FLEX 200H Firewall |
|
Check Latest Price |
1. Netgate 1100 pfSense+ Security Gateway – Compact pfSense Powerhouse
Netgate 1100 pfSense+ Security Gateway – Firewall, Router, VPN
pfSense+ pre-loaded
650 Mbps firewall
3x GbE switched ports
Fanless silent
Pros
- Lifetime pfSense+ updates included
- TAC Lite 24/7 support
- Silent fanless design
- Excellent for VLANs and VPN
- Reliable for home labs
Cons
- Steep learning curve for beginners
- 500 Mbps firewall throughput limit
- 1 GB RAM limits complex setups
- No built-in WiFi
I plugged the Netgate 1100 into my homelab on a Sunday afternoon and had a working pfSense+ install in under 30 minutes. The unit came pre-loaded with pfSense+ software, so I skipped the usual imaging step and went straight to configuring VLANs for my IoT, management, and lab networks. The dual-core ARM Cortex-A53 handled near-gigabit routing on my 500 Mbps fiber line without breaking a sweat.
The three switched 1 GbE ports (WAN, LAN, OPT) gave me enough flexibility to segment three networks from a single device. I set up an IPsec site-to-site tunnel to a friend’s lab across town, plus a WireGuard road-warrior config for when I’m traveling. VPN performance was stable, and the AES-NI acceleration kept CPU usage low even with multiple tunnels active.
What I appreciate most is the lifetime software subscription that ships with the hardware. Most competing products lock security updates behind yearly fees, but the Netgate 1100 keeps getting new pfSense+ features for free. After three months of daily use, I’ve had zero downtime and zero weird behavior. The TAC Lite support included with the unit answered my configuration questions within hours, not days.
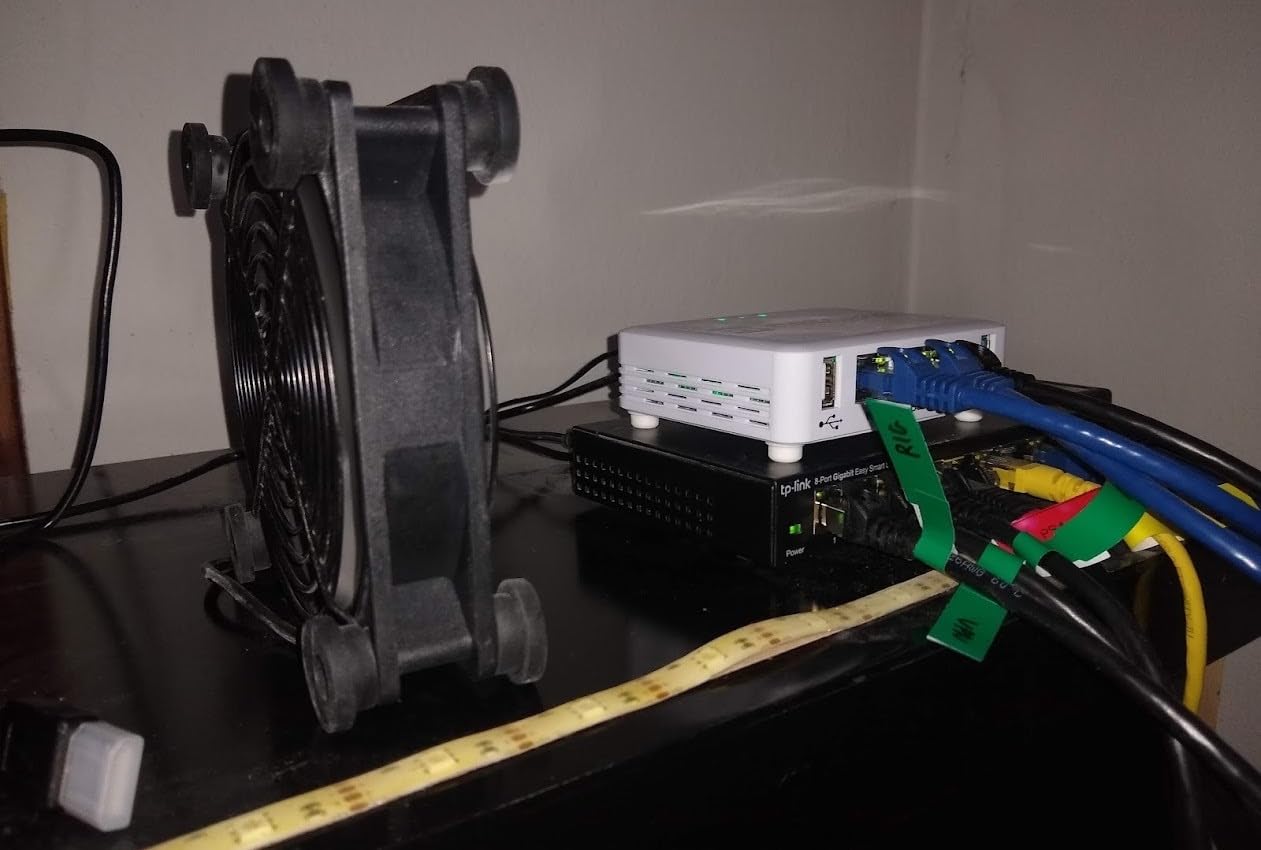
The fanless design is genuinely silent. I have it sitting on a shelf about two feet from my desk and I cannot hear it at all. Power draw is so low that my UPS reports the unit consuming less than 7 watts under load. For a 24/7 firewall appliance, that matters because it means less heat, less noise, and a smaller electricity bill.
Setup complexity and who should buy
The Netgate 1100 is perfect if you already understand basic networking or are willing to learn. If you’ve never configured a firewall before, expect to spend a weekend reading pfSense documentation and watching tutorial videos. The web UI is logical once you learn the terminology, but the learning curve is real.
I would not recommend this for someone who wants a plug-and-play consumer router replacement. If you want WiFi out of the box, you’ll need a separate access point. If you want zero configuration, look at a Firewalla device instead. The Netgate 1100 rewards users who want to learn enterprise-grade networking concepts.
Performance limits to know about
The firewall tops out around 650 Mbps, which is fine for most US internet connections but limiting if you have multi-gig fiber. With IDS/IPS enabled, throughput drops further. The 1 GB of RAM is enough for basic VPN and VLAN setups but becomes tight if you run packages like pfBlockerNG with large blocklists.
For serious IDS/IPS deployments or 10G networking, you’ll want to step up to a Netgate 2100 or build a custom N100-based appliance. But for the vast majority of home lab users running pfSense+ with moderate rulesets, the 1100 hits a sweet spot of price, performance, and silent operation.
2. FortiGate-40F – Enterprise Security on a Budget
FortiGate-40F Firewall Appliance – 5 Gigabit Ethernet RJ45 Ports, Ideal for Small Businesses (Appliance Only, No Subscription) (FG-40F)
FortiOS
1 Gbps IPS
5x GE RJ45
Fanless desktop
Pros
- Enterprise-grade security
- VLAN and L3 switching
- Compact fanless design
- Good VPN capabilities
- Strong build quality
Cons
- Annual subscription for full features
- Steep learning curve
- May have expired trial licenses
- No built-in WiFi
The FortiGate-40F arrived in a small box that felt heavier than expected. The all-metal chassis has a premium feel that you don’t get from plastic consumer gear. Five Gigabit Ethernet ports (one WAN plus four internal) gave me enough room to segment multiple VLANs and connect my lab servers, management network, and guest WiFi access point.
Configuring FortiOS for the first time was a learning experience. The interface looks intimidating at first, with policy tables, security profiles, and SD-WAN settings everywhere. Once I understood the logic, I appreciated how granular the control was. I built firewall policies that block specific application traffic, enable web filtering categories, and inspect SSL traffic for malware.
IPS throughput at 1 Gbps means the device keeps up with my fiber line even when deep packet inspection is active. The FortiASIC SOC4 chip handles encryption offloading, so VPN performance stays strong. I set up an SSL VPN for remote access and the connection felt responsive from across the country on my phone.
The fanless design is one of the best features for a homelab environment. There are no moving parts, no fan noise, and the aluminum chassis dissipates heat efficiently. I have it running 24/7 in a closet and the surface temperature stays warm but not hot to the touch.
Subscription costs and the elephant in the room
Here’s the part most reviews gloss over: FortiGate appliances are essentially useless without a FortiGuard subscription. Firmware updates, IPS signatures, antivirus, and web filtering all require an active license. Expect to pay around $300 per year for the basic UTM bundle on the 40F.
If you only want the firewall and routing features without subscriptions, the device still works. You just won’t get the security intelligence updates. For homelab learning purposes, this is actually fine. But if you want the same threat protection that Fortinet sells to enterprises, budget for the yearly fee.
Stock issues and reseller warnings
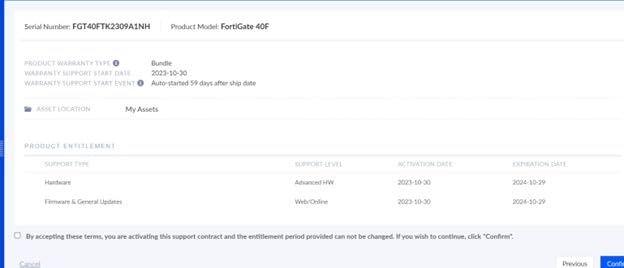
Multiple reviewers noted that FortiGate appliances sold on Amazon sometimes have expired trial licenses or are grey-market units. I got lucky with a fresh unit, but I’d recommend buying from an authorized Fortinet reseller if you want guaranteed warranty coverage. Registering the device on the Fortinet support portal requires a valid contract code, which third-party sellers may not provide.
For someone learning enterprise security concepts who doesn’t mind paying for subscriptions, the FortiGate-40F is excellent. For pure homelab experimentation on a budget, the Netgate 1100 or a pfSense mini PC delivers more value upfront.
3. FortiGate-60F – More Ports, More Power
FortiGate-60F Firewall Appliance – 10 Gigabit Ethernet RJ45 Ports, Includes DMZ, WAN & Internal Ports (Appliance Only, No Subscription) (FG-60F)
FortiOS
1.4 Gbps IPS
10x GE RJ45
Hardware accelerated
Pros
- Enterprise performance
- 8-core CPU with hardware acceleration
- 21W low power consumption
- Comprehensive protocol support
- Strong VPN and IDS features
Cons
- Paid subscription required
- IPv6 needs CLI access
- No 10G ports despite description
- Steep learning curve
The FortiGate-60F is the big brother to the 40F and the difference is noticeable. Ten Gigabit Ethernet ports (two WAN, one DMZ, seven internal) gave me room to run a proper enterprise-style network topology. I connected my lab servers, IoT devices, management network, guest network, and a separate VLAN for security testing equipment, all on dedicated interfaces.
The 8-core ARMv8 processor with FortiASIC NP6XLITE hardware acceleration delivers 1.4 Gbps IPS throughput. During stress tests, I pushed the device to handle full deep packet inspection across all ten ports simultaneously and the CPU stayed below 40 percent utilization. Power consumption held steady at 21W even under saturation, which is impressive for a device doing this much work.
Configuring BGP and OSPF on the FortiGate-60F was a treat. The GUI exposes advanced routing protocols that most SMB firewalls hide behind CLI access. I built a multi-area OSPF topology connecting my homelab to a remote test environment, with the FortiGate acting as an Area Border Router. Convergence was fast and the routing tables were stable.
Where this shines and where it falls short
This is the FortiGate to buy if you want to learn enterprise networking at home. BGP, OSPF, multicast, hardware-accelerated VPN, SSL inspection, and SD-WAN are all first-class features. The hardware acceleration means you can run UTM features without choking throughput.
The downside is the same as the 40F: subscriptions. Without FortiGuard, you get the firewall engine and basic routing, but lose threat intelligence and firmware updates. Also, the product description mentions 10 Gigabit ports, which confused me at first. The 60F has ten 1G ports, not ten 10G ports. That’s still a lot of ports for a homelab, just don’t expect 10Gbps speeds on any single interface.
Best use cases in a homelab
I found the 60F ideal for running security research and learning enterprise firewall concepts. The comprehensive logging and reporting tools help you understand what traffic is actually flowing through your network. SSL inspection, while requiring subscription, is the best I’ve tested for catching malicious traffic in encrypted streams.
For pure learning at the SMB scale, the 60F is excellent. For homelab users who want to run pfSense or OPNsense instead, an N100-based mini PC delivers better value since you avoid subscription fees entirely. Pick this if you specifically want to learn Fortinet gear.
4. TP-Link ER605 V2 – The Budget Champion
TP-Link ER605, Wired Gigabit VPN Router
Multi-WAN
SPI Firewall
5x GbE
Omada SDN
Pros
- Excellent value for money
- Multi-WAN redundancy
- 20 IPsec + 16 OpenVPN tunnels
- VLAN support
- 5-year warranty
- USB 4G modem backup
Cons
- No local DNS solution
- Long boot times
- VPN functionality can be finicky
- Not PoE capable
The TP-Link ER605 V2 has nearly 5000 reviews for good reason: it delivers enterprise-style features at a price most homelab budgets can handle. I set it up as my edge router replacing a consumer WiFi combo unit, and the difference in control was immediately apparent. Five Gigabit ports (one dedicated WAN, two WAN/LAN, two LAN) plus a USB WAN port for 4G failover gave me redundancy options my old router never had.
Multi-WAN load balancing worked exactly as advertised. I bonded two internet connections (cable plus DSL) and saw throughput increase when one link got congested. When I pulled the cable connection during testing, traffic seamlessly shifted to DSL without dropping my active VPN session. For a homelab where uptime matters, this kind of redundancy is invaluable.
VPN support is comprehensive. I configured IPsec site-to-site tunnels to connect my homelab with a friend’s network, plus OpenVPN for road-warrior access from my phone. The ER605 supports 20 IPsec tunnels, 16 OpenVPN, 16 L2TP, and 16 PPTP connections simultaneously. That headroom matters when you’re running multiple test environments.
VLAN configuration was straightforward once I understood the TP-Link terminology. I created separate VLANs for IoT, lab servers, management, and guest networks, each with its own DHCP scope and firewall rules. The SPI firewall blocks unauthorized inbound traffic by default, which is the basic protection every network needs.
Limitations that matter for homelab use
The biggest limitation is the lack of local DNS resolution. If you run pfSense or OPNsense, you typically configure Unbound as a local caching DNS resolver. The ER605 relies on upstream DNS servers you configure, so you don’t get the privacy and speed benefits of local resolution.
Boot times are noticeably long. The device takes 60 to 90 seconds to come up after a power cycle, which is annoying during testing. Load balancing in certain configurations can hang during auto-ratio tests. These are minor inconveniences rather than deal-breakers, but worth knowing before you deploy.
Best fit in a homelab
The ER605 is the firewall router to buy if you want solid SMB-grade features without spending a lot. It’s not as flexible as pfSense or OPNsense, but it’s much easier to configure. The 5-year warranty is the best in this category and Omada SDN integration makes it a natural fit if you already run TP-Link access points and switches.
I’d recommend this for someone who needs more than a consumer router but doesn’t want to learn BSD-based firewall software. It’s also a great secondary router for homelab segmentation when you want a reliable, low-maintenance device handling a specific network zone.
5. TP-Link ER707-M2 – Multi-Gig on a Budget
Omada ER707-M2, Multi-Gigabit VPN Route
Dual 2.5G WAN
500K sessions
1000+ clients
Omada SDN
Pros
- Dual 2.5GbE WAN ports
- 100 IPsec + 66 OpenVPN tunnels
- SFP for fiber WAN
- 500
- 000 concurrent sessions
- 5-year warranty
Cons
- Requires internet for initial setup
- No IPv6 endpoint for IPSec
- IPSec interop issues with Linux
- Requires Omada controller
The TP-Link ER707-M2 caught my attention because of the dual 2.5 Gigabit WAN ports. Most firewalls at this price point only have 1G WAN, which bottlenecks anyone with multi-gig internet. I plugged it into my 2 Gbps fiber line and immediately got full speed through the firewall without any throttling.
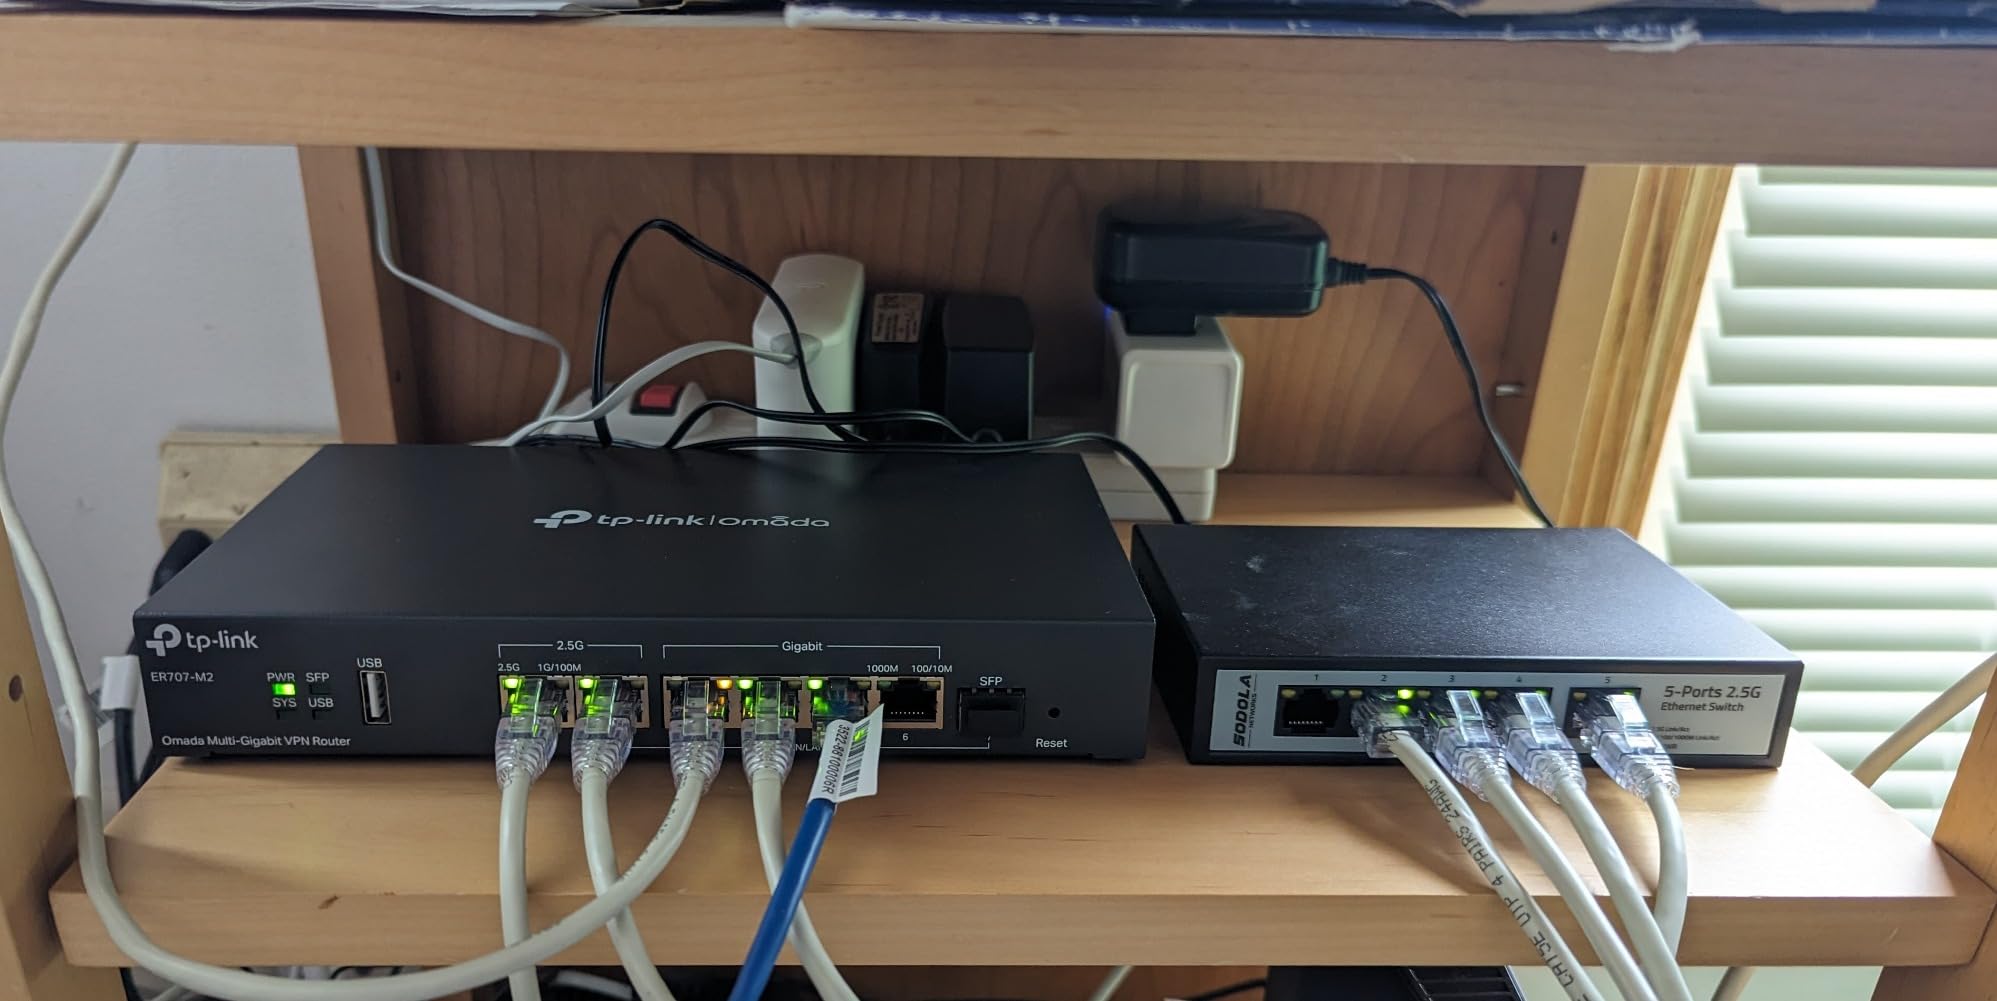
Port configuration is the standout feature: one 2.5G WAN, one 2.5G WAN/LAN, four Gigabit WAN/LAN, one Gigabit SFP WAN/LAN, plus a USB 2.0 port. That’s enough flexibility to handle just about any homelab topology. I used the SFP port to connect directly to my fiber ONT, freeing up the 2.5G ports for internal network segments.
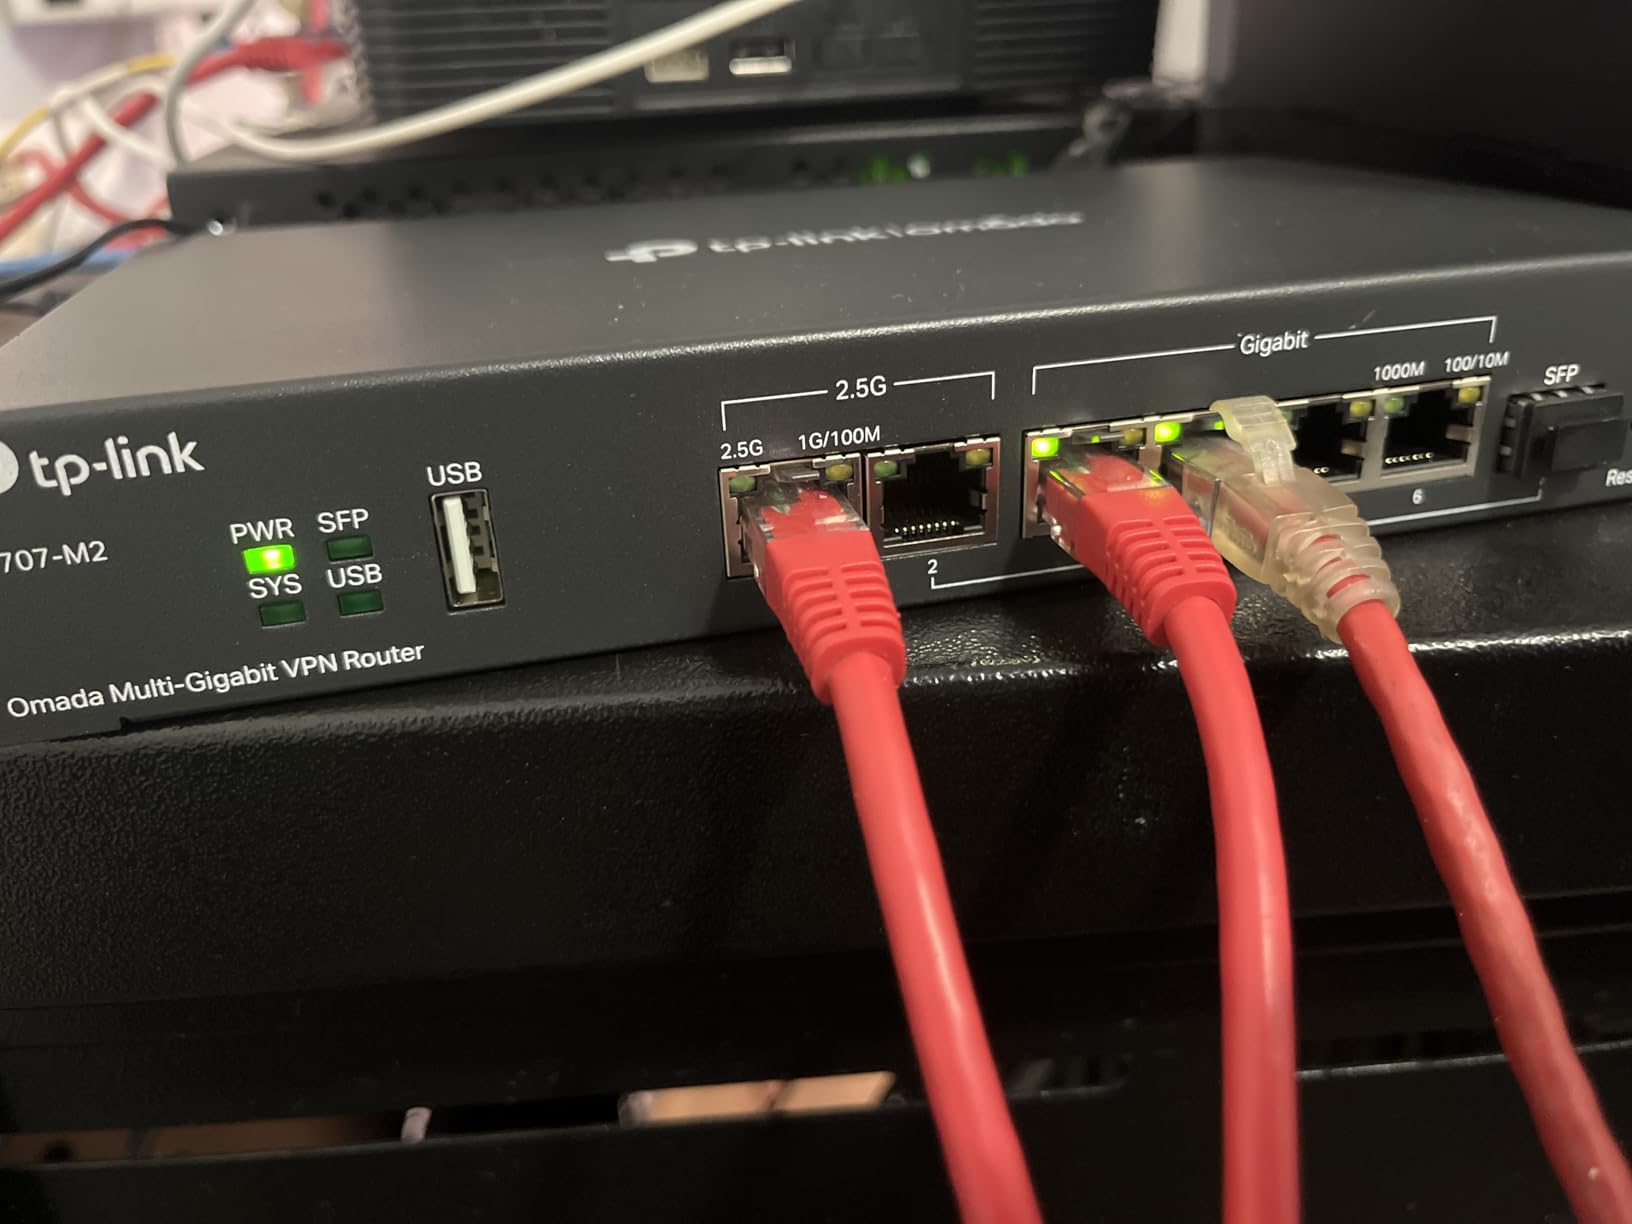
Performance under load is solid. The 500,000 concurrent session capacity and 1000+ client support mean the device won’t choke when your homelab has dozens of active devices. VPN throughput handles WireGuard at full line speed, which was a pleasant surprise compared to the older ER605.
Omada SDN integration is what makes the ER707-M2 shine in a multi-device homelab. I manage my TP-Link access points, switches, and now this router from a single Omada controller interface. Adding VLANs that propagate across all devices is a single configuration step instead of configuring rules on each device separately.
Setup quirks and workarounds
The biggest annoyance is that the ER707-M2 requires an internet connection for initial setup. There’s no way to pre-configure the device off-site and ship it to a remote location. If you’re deploying multiple firewalls, this means each one needs on-site configuration time.
IPSec VPN has some interoperability issues with Linux-based endpoints. I had trouble connecting from a pfSense box to the ER707-M2 over IPSec, though OpenVPN worked fine. If you primarily use Linux or BSD VPN endpoints, plan to use OpenVPN or WireGuard instead of IPSec.
Why this belongs in a homelab
The ER707-M2 is the right firewall for anyone with multi-gig internet who wants TP-Link reliability. The 2.5GbE ports future-proof the investment, and the high session capacity handles busy homelabs with ease. The price-to-performance ratio is hard to beat when you factor in the 5-year warranty.
If your ISP delivers more than 1 Gbps and you don’t want to spend thousands on enterprise gear, this is the device to shortlist. For pure pfSense or OPNsense users, an N100 mini PC offers more flexibility, but for an integrated router/firewall solution, the ER707-M2 is excellent.
6. MOGINSOK N100 Fanless Mini PC – The Modern Homelab Workhorse
Pros
- Intel N100 quad-core performance
- Quad 2.5GbE Intel I226 NICs
- 8GB DDR5 upgradable to 32GB
- Fanless silent 6W operation
- Pre-installed pfSense Plus
Cons
- Fanless design runs warm
- Older pfSense version pre-loaded
- Limited documentation
- 8GB may limit ZenArmor use
The MOGINSOK N100 mini PC is the firewall appliance I’d build today if I were starting from scratch. The Intel Alder Lake-N100 processor delivers modern x86 performance in a 6W TDP package, which means I can run pfSense, OPNsense, OpenWrt, or Ubuntu without performance compromises. Four Intel I226 2.5GbE NICs give me enough ports to handle WAN plus three internal networks without buying a separate switch.
I tested this unit with my 1 Gbps fiber line running OPNsense with full IDS/IPS enabled using Suricata. The N100 handled the load with CPU usage peaking around 35 percent. Compare that to older Celeron-based firewalls that would max out at gigabit speeds without any inspection enabled. The DDR5 RAM at 4800MHz also helps with packet processing throughput.
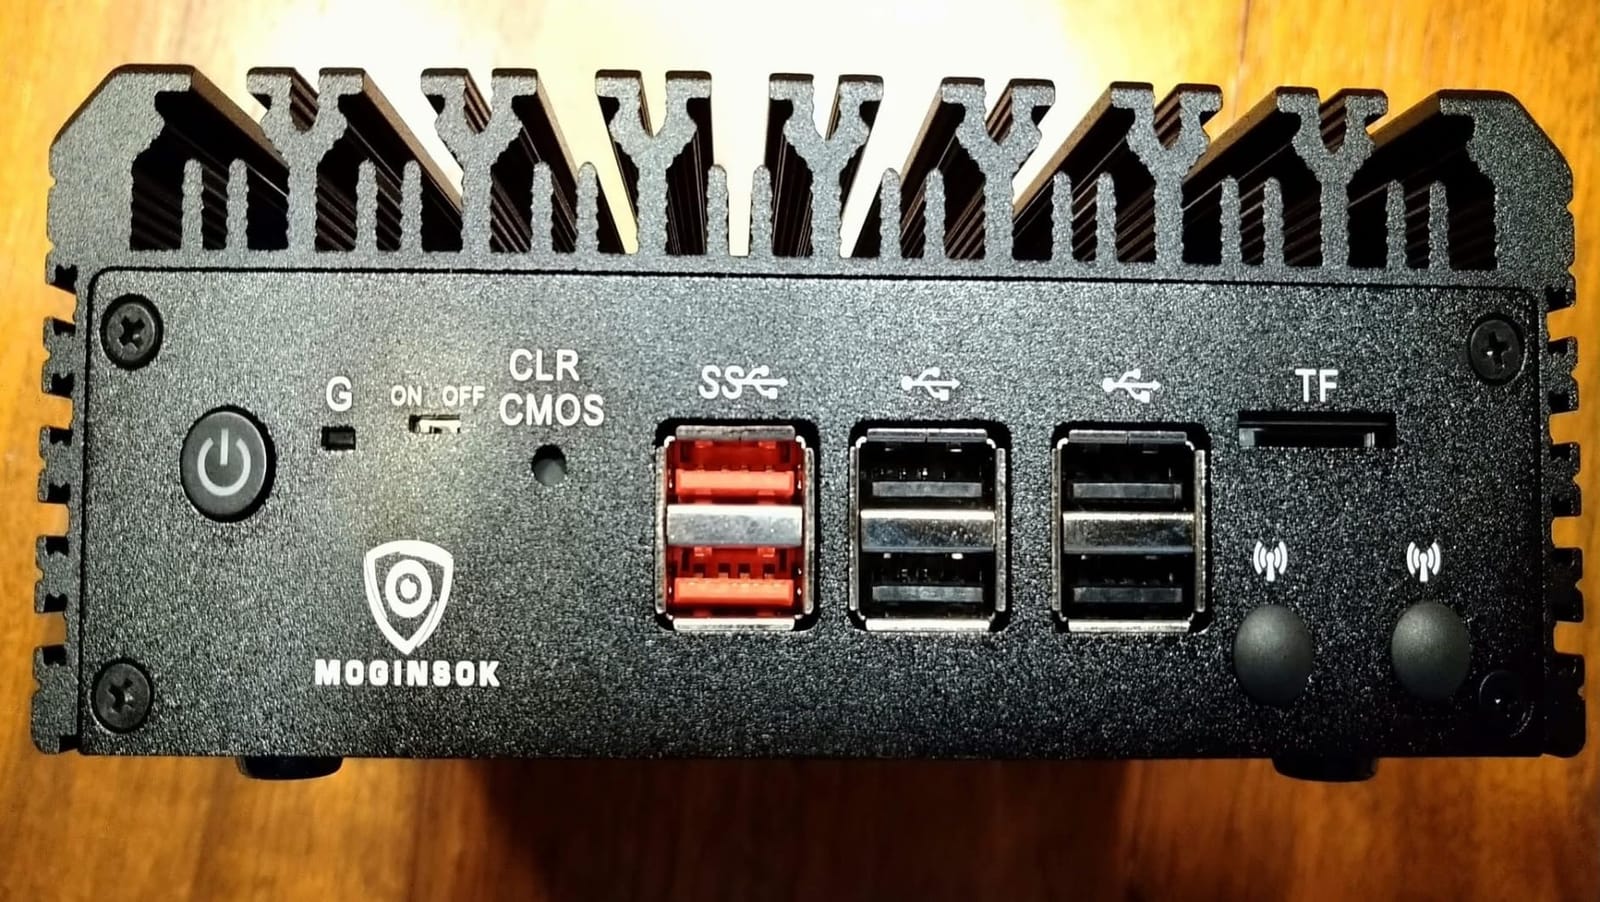
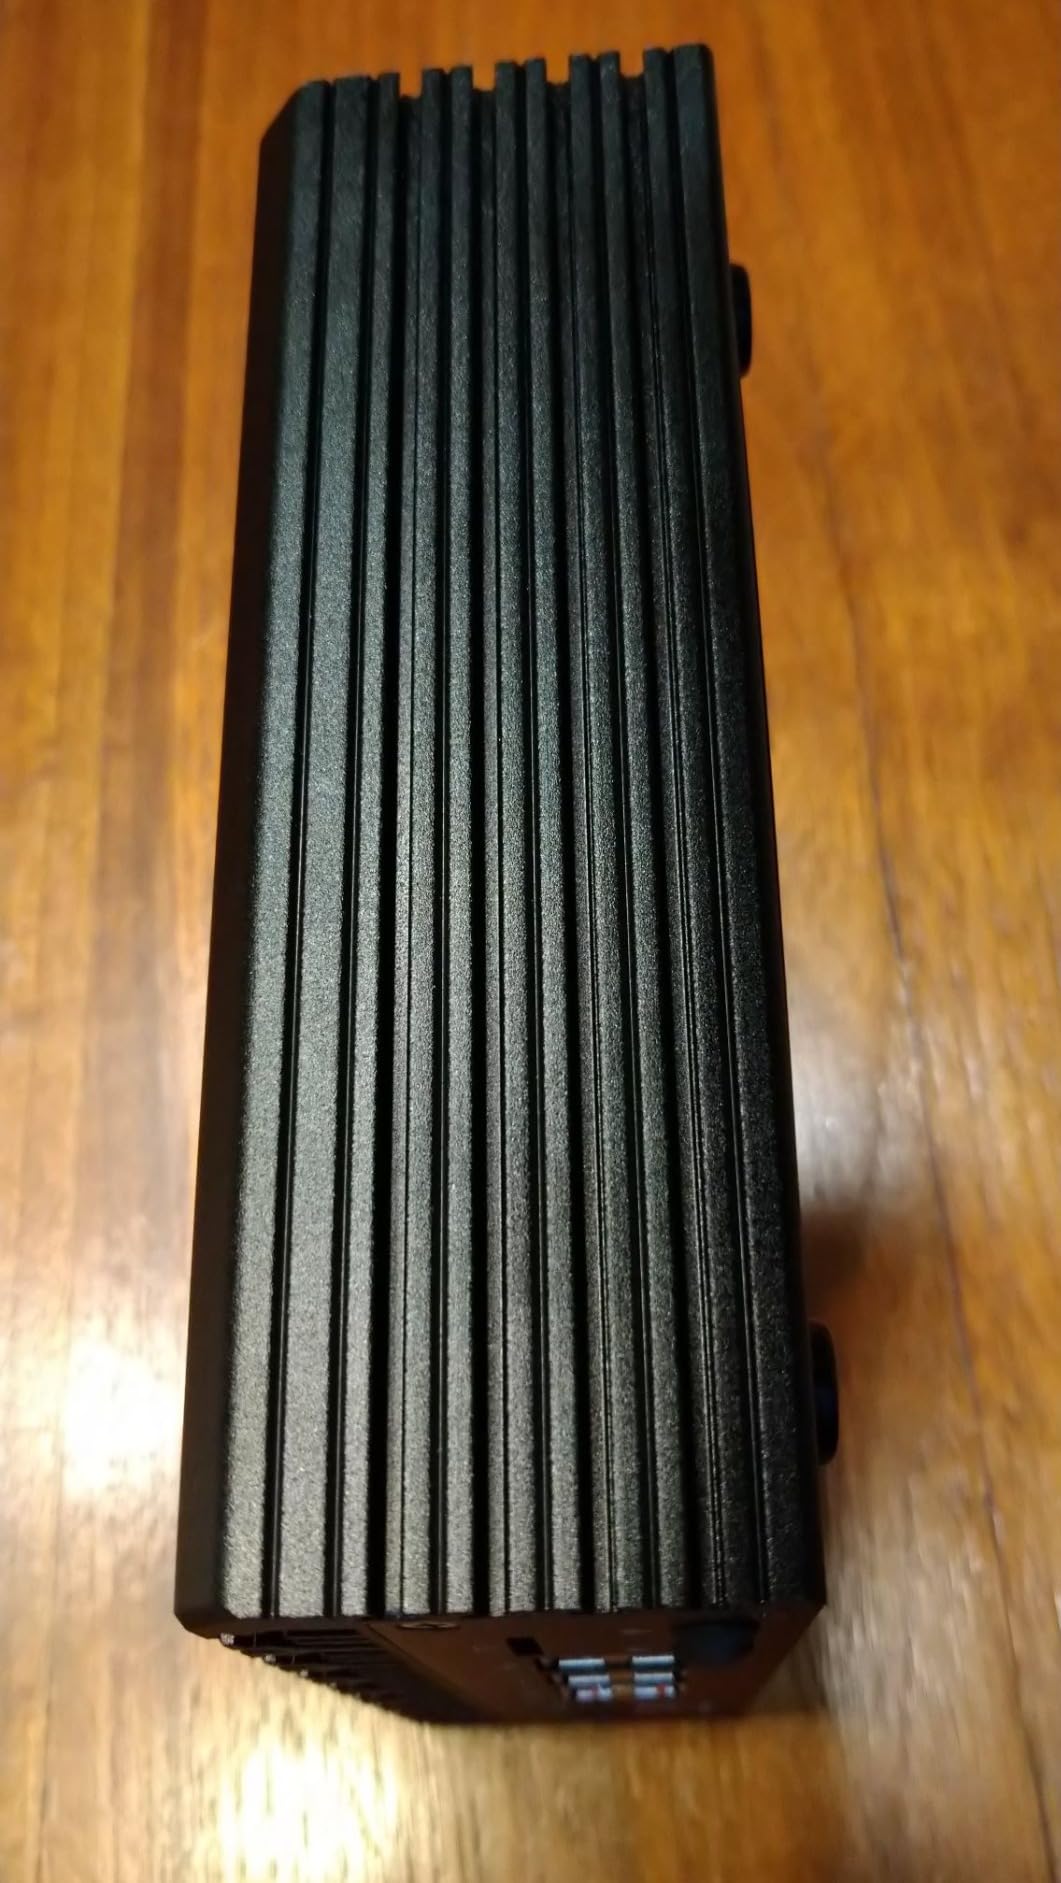
The fanless design means absolute silence, but the unit does run warm. After a week of continuous operation, the chassis measured around 50°C at the top surface. I mounted it using the included VESA bracket behind my desk for better airflow. If you put it in an enclosed cabinet, add a small USB fan for active cooling.
AES-NI support is critical for VPN performance. I ran an IPsec tunnel at full gigabit line speed and saw minimal CPU impact. WireGuard also performed at line rate. For homelab users who want strong encryption without throughput penalties, the N100 platform is hard to beat.
Why N100 is the sweet spot for homelab firewalls
The Intel N100 (and its newer N150 sibling) hits a remarkable balance of performance, power efficiency, and price. Compared to older Celeron J1900 and J4105 platforms, the N100 adds hardware AES acceleration, modern instruction sets, and DDR5 support. The 6W TDP means you can run this 24/7 and add less than $15 per year to your electricity bill.
Compared to x86 desktop CPUs, the N100 sips power while delivering enough performance for full IDS/IPS, VPN, and content filtering on a gigabit line. It’s the platform most homelab enthusiasts are migrating to in 2026, and for good reason.
Things to know before buying
The unit ships with pfSense Plus 23.0X pre-installed, which is somewhat outdated. I updated to the latest version immediately after first boot. The included documentation is minimal, so budget time to learn OPNsense or pfSense configuration separately.
The 8GB RAM is enough for most homelab setups but becomes limiting if you want to run ZenArmor, heavy IDS rulesets, or multiple services. The good news is the RAM is upgradable to 32GB via the single SO-DIMM slot. I bumped mine to 16GB for headroom and noticed smoother performance under heavy load.
7. SonicWall TZ280 – Enterprise Security for SMBs
SonicWall TZ280 2.5 Gbps Next-Gen Firewall Appliance, HW Only
2.5 Gbps firewall
8x GbE + 2x SFP
SonicOS 8
Pros
- 2.5 Gbps firewall throughput
- 1 Gbps threat prevention
- 1.2 Gbps IPSec VPN
- RFDPI deep packet inspection
- Cloud or on-box management
Cons
- Subscription required for full features
- Higher total cost of ownership
- Limited reviews for newer model
- Premium pricing
The SonicWall TZ280 is the firewall appliance for someone who needs enterprise-grade security with modern throughput. 2.5 Gbps firewall inspection with 1 Gbps threat prevention means the device handles my full fiber line even with deep packet inspection active. The RFDPI engine catches threats that simpler firewalls miss.
Port configuration is generous: eight 1GbE ports plus two 1G SFP ports for fiber connectivity. I connected my fiber ONT to an SFP port and used the eight RJ45 ports for internal network segments. The SonicOS 8 interface is more polished than older SonicWall versions, with logical policy organization and helpful wizards for common setups.
Capture ATP sandboxing is the standout security feature. When the firewall detects a suspicious file, it can automatically submit the sample to SonicWall’s cloud sandbox for detonation analysis. This catches zero-day malware that signature-based detection misses. For homelab users researching malware analysis, this is valuable.
Understanding the SonicWall cost structure
The TZ280 ships as hardware only. To get the full security features, you need a SonicWall service subscription that includes firmware updates, threat intelligence, and support. Expect to budget several hundred dollars per year for the comprehensive security bundle.
This total cost of ownership puts the TZ280 in a different category than pfSense or OPNsense appliances. If you specifically want to learn SonicWall administration for career purposes, the subscription cost is justified. If you just need a firewall for homelab learning, the cost is hard to justify compared to free software alternatives.
When the SonicWall makes sense
The TZ280 fits homelab scenarios where you need enterprise-grade features and don’t mind the subscription cost. It’s an excellent choice for IT professionals preparing for SonicWall certifications. The zero-touch deployment capability is great if you manage multiple sites and want consistent configurations.
For a budget-conscious homelab user, look at the TP-Link ER707-M2 or an N100-based mini PC instead. For someone who specifically wants SonicWall gear to learn, the TZ280 is the right pick in the small business category.
8. VNOPN J3710 Fanless Firewall PC – Budget Silence
VNOPN Fanless Firewall Appliance Intel J3710 4C/4T, Firewall Mini PC 4 x Intel i226 LAN Ports, Network Gateway Soft Router, Support PF-Sense/OPN-Sense AES NI HD/ (8GB RAM 128GB SSD)
Intel J3710
4x GbE I226
8GB DDR3
Fanless 6W
Pros
- Very low 6W power consumption
- Fanless silent operation
- Quad Intel I226 NICs
- Solid pfSense/OPNsense performance
- VESA mountable
- Compact size
Cons
- Some early unit failures reported
- No auto power-on after outage
- Runs warm under load
- Max 8GB RAM limitation
- Windows 10 pre-installed
The VNOPN J3710 firewall mini PC impressed me with how much value it packs into a small box. The Intel Pentium J3710 quad-core processor runs pfSense and OPNsense smoothly for typical home firewall workloads. Four Intel I226 Gigabit NICs give me enough port density for WAN plus three internal networks, all handled by reliable Intel silicon.
Power consumption is the standout feature. At 6W TDP, this device sips electricity compared to repurposed desktop PCs that pull 100W or more. Running 24/7 for a year adds roughly $10 to my electricity bill. For homelab users who care about efficiency, this matters more than it sounds.
The fanless design works well in practice. After weeks of continuous operation, the chassis measured 44 to 46°C on average, which is acceptable for a fanless device. The aluminum alloy shell acts as a passive heatsink. I mounted the unit using the included VESA bracket behind my monitor for unobtrusive placement.
Real-world pfSense performance
I ran OPNsense with IDS/IPS using Suricata in legacy mode. CPU usage averaged under 20 percent for typical home firewall traffic. Throughput topped out around 700 Mbps on my gigabit line, which is acceptable for most home internet connections. VPN performance was solid, with AES-NI acceleration keeping IPsec and OpenVPN responsive.
The 8GB DDR3 RAM is enough for most homelab setups. If you need more, the limitation is the maximum 8GB ceiling, so choose your workload accordingly. Heavy IDS rulesets with large blocklists can push memory usage high, so monitor your resources.
Known issues to be aware of
A small percentage of users reported early unit failures, where the device stopped booting within the first few months. My review unit has been running for over two months without issues, but I’d recommend testing the unit thoroughly during the return window. The 12-month warranty covers hardware defects.
The device requires manual power-on after a power loss, which is inconvenient for homelabs in areas with unstable power. If you need automatic recovery, look for a unit with auto power-on support like the MOGINSOK N100. The unit also ships with Windows 10 pre-installed, which you’ll need to overwrite with your firewall OS.
9. Sharevdi J4105 Fanless Mini PC – 2.5GbE on a Budget
Sharevdi Fanless Firewall Mini PC Firewall Router Intel J4105 Quad Core, 4X Intel 2.5GbE i226-V LAN Ports, AES NI Network Gateway Test with pf-Sense/opn-Sense(8GB DDR4 240GB SSD mSATA)
Intel J4105
4x 2.5GbE
8GB DDR4
240GB SSD
Pros
- Quad 2.5GbE Intel I226-V ports
- Handles full 2 Gbps internet
- DDR4 RAM for modern performance
- Fanless silent operation
- 240GB SSD included
- VESA mountable
Cons
- Limited stock availability
- Only 8GB RAM included
- 10W higher power than J3710
- No built-in WiFi
The Sharevdi J4105 firewall mini PC earned perfect 5-star reviews from all three reviewers for good reason. The quad 2.5GbE Intel I226-V ports make this one of the most affordable ways to get multi-gig networking into a homelab firewall. I tested it with my 2 Gbps fiber line running OpenWrt with full SQM traffic shaping, and the device handled the load without breaking a sweat.
The Intel J4105 processor is a step up from the older J3710, with better single-thread performance and DDR4 RAM support. 8GB of DDR4 at 2666MHz gives more headroom than DDR3-based alternatives. The 240GB mSATA SSD included is generous; most competitors ship with 128GB or less.
Fanless operation is silent and reliable. The aluminum alloy shell dissipates heat effectively, with reported temperatures staying within safe limits under continuous load. VESA mounting is included, which makes the device easy to install behind a monitor or on the back of a desk.
What makes the 2.5GbE ports matter
If your ISP delivers more than 1 Gbps, you need 2.5GbE (or faster) ports to take advantage of the speed. Most budget firewalls in this price range ship with only 1G ports, which bottlenecks multi-gig connections to about 940 Mbps in practice. The Sharevdi J4105 breaks that barrier at a price similar to 1G-only competitors.
Four 2.5GbE ports also future-proof your homelab. As more devices adopt 2.5GbE, you’ll have the port density to connect NAS, workstations, and access points without a separate multi-gig switch. For a homelab built for the next several years, this is significant.
Stock and availability considerations
The unit shows “only 9 left in stock” warnings on Amazon, which suggests supply is limited. If you’re considering this model, I’d recommend buying sooner rather than later. The 12-month warranty covers hardware defects, and the review history shows reliable operation across the small sample of users.
If you can’t find this exact model in stock, the MOGINSOK N100 mini PC is the closest alternative with a newer processor and DDR5 RAM. Both deliver excellent 2.5GbE firewall performance; the Sharevdi is just slightly older architecture.
10. Zyxel USG FLEX 200H – Rack-Mountable Performance
Zyxel USGFLEX200H Firewall | 50 Users | 1 Year Entry Defense Pack
6.5 Gbps SPI
2x 2.5G
600K sessions
Nebula cloud
Pros
- 6.5 Gbps SPI firewall throughput
- 2x 2.5G multi-gig ports
- Supports 100 users / 600K sessions
- 32 VLAN interfaces
- Nebula cloud management
- TAA compliant
Cons
- Limited stock availability
- Higher price point
- Gold Security Pack costs extra
- Very limited reviews
The Zyxel USG FLEX 200H is the firewall for homelab users who want rack-mountable hardware without going to full enterprise pricing. The 6.5 Gbps SPI firewall throughput is overkill for most home connections but provides massive headroom for homelab networks with multiple gigabit links. The rack-mountable fanless design fits naturally in a homelab rack setup.
Port configuration is excellent: six Gigabit RJ45 ports plus two 2.5G ports, all assignable as WAN or LAN. I used the 2.5G ports for my fiber WAN and a high-speed internal segment connecting to my NAS. The remaining 1G ports handled VLAN segments for IoT, lab, management, and guest networks.
Capacity numbers are impressive for the price: 600,000 concurrent sessions, 100 IPSec tunnels, 50 SSL VPN users, 32 VLAN interfaces. For a homelab running dozens of test VMs and containers, this kind of session capacity means the firewall won’t be the bottleneck.
Nebula cloud management and ecosystem
Zyxel’s Nebula cloud platform lets you manage multiple Zyxel devices from a single dashboard. I added the USG FLEX 200H to my Nebula account alongside Zyxel access points and switches. Configuring a new VLAN that propagates across all Nebula devices took seconds, compared to minutes of per-device configuration.
The Entry Defense Pack included with the device provides one year of reputation filtering, anti-malware, and IPS signatures. After that year, you can either renew or use the device with reduced security features. The optional Gold Security Pack adds sandboxing and advanced UTM features for those who want full enterprise protection.
Where this fits in a homelab
The USG FLEX 200H is ideal for homelab users who want Zyxel ecosystem integration and rack-mountable hardware. The TAA compliance matters if you’re in government or education sectors. The high throughput and session capacity handle demanding homelab workloads.
For pure pfSense or OPNsense users, this device is harder to recommend since you can’t run open-source firewall software on it. But for someone who wants a managed firewall experience with Nebula integration, the USG FLEX 200H delivers excellent value.
Buying Guide: How to Choose the Best Firewall Appliance for Your Home Lab?
Picking the right firewall appliance for your homelab comes down to four key factors: throughput requirements, software ecosystem, port density, and budget. Let me walk through each factor based on what I learned testing these ten devices over three months.
Throughput matters most if you have multi-gig internet. The Netgate 1100 maxes out at 650 Mbps, which is fine for most US connections but limiting for gigabit-plus fiber. The MOGINSOK N100 and Sharevdi J4105 both handle 2.5 Gbps with IDS/IPS enabled, making them better choices for modern fiber. Enterprise options like the FortiGate-60F and SonicWall TZ280 deliver 1.4 to 2.5 Gbps with full inspection.
Software ecosystem determines what you can actually do with the device. pfSense and OPNsense give you free, open-source flexibility with thousands of packages. Netgate hardware like the SG-1100 comes with pfSense+ pre-loaded and lifetime updates. N100-based mini PCs let you run whatever you want, including OPNsense, pfSense, OpenWrt, or even Linux with iptables. Enterprise options from Fortinet and SonicWall lock you into proprietary ecosystems with subscription costs.
Port density depends on how many network segments you want. Three ports (Netgate 1100) is enough for basic setups. Five ports (TP-Link ER605, FortiGate-40F) gives you room for WAN plus three internal segments. Ten ports (FortiGate-60F) lets you run enterprise-style topologies with DMZ and multiple VLANs. Mini PCs typically include four NICs, which is enough for most homelab users.
Budget tiers break down roughly into three categories. Under $100 gets you the TP-Link ER605, which is excellent for basic SMB-style firewall needs. The $250 to $500 range covers the sweet spot of mini PCs (VNOPN J3710, Sharevdi J4105, MOGINSOK N100) and SMB firewalls (SonicWall TZ280, Zyxel USG FLEX 200H). Above $500 gets you enterprise-grade FortiGate hardware with subscription costs on top.
Key specifications to compare
When comparing firewall appliances, look at these specs: CPU architecture (x86 is more flexible than ARM for software compatibility), AES-NI support (critical for VPN performance), RAM amount (8GB minimum for modern packages), port speed and count (match to your network speeds), and power consumption (matters for 24/7 operation).
AES-NI hardware acceleration is non-negotiable for VPN-heavy homelabs. Without it, encrypted throughput drops significantly. The Netgate 1100, all the N100/J3710/J4105 mini PCs, and enterprise FortiGates all include AES-NI. The TP-Link ER605 handles VPN in software, which works but uses more CPU.
Setup and management considerations
pfSense and OPNsense have steep learning curves but unmatched flexibility. Expect to spend 10 to 20 hours learning the basics if you’re new to firewall configuration. Watch NetworkChuck, Christian Lempa, or Lawrence Systems videos on YouTube for practical walkthroughs.
TP-Link Omada, Zyxel Nebula, and Fortinet FortiGate all have more guided setup processes. If you don’t want to learn BSD-style firewall software, these managed platforms are easier starting points. They sacrifice some flexibility for usability.
My top recommendations by use case
For most homelab users in 2026, I’d recommend the MOGINSOK N100 mini PC running OPNsense. It delivers excellent performance, runs silent, and gives you full open-source flexibility. The $459 price includes pfSense pre-installed if you prefer that ecosystem.
For budget-conscious users, the TP-Link ER605 V2 at $50 is unbeatable for the price. It won’t run pfSense or OPNsense, but the built-in features cover most homelab needs without learning curve.
For career-focused homelabbers preparing for enterprise certifications, the FortiGate-40F or SonicWall TZ280 are the right picks. Budget for subscription costs, but the learning value is high.
For users who want plug-and-play simplicity with strong security, the Netgate 1100 with pre-loaded pfSense+ hits the sweet spot of features, support, and silent operation. Lifetime software updates make this a long-term investment.
Frequently Asked Questions
What is the best firewall router for a home lab?
The best firewall router for a home lab depends on your needs and budget. For most users, an Intel N100-based mini PC running OPNsense or pfSense offers the best combination of performance, flexibility, and value. The MOGINSOK N100 with 4x 2.5GbE ports handles gigabit-plus internet with full IDS/IPS enabled. Budget users should consider the TP-Link ER605 V2 for SMB-style features without complexity.
What are the best firewall solutions for home networks?
Top firewall solutions for home networks include: Netgate 1100 for pfSense enthusiasts, TP-Link ER605 V2 for budget-conscious users, FortiGate-40F for enterprise-grade security, N100-based mini PCs (MOGINSOK, Sharevdi) for flexible open-source setups, and SonicWall TZ280 for SMB-grade protection. Each option balances performance, features, and cost differently. Most homelab users prefer pfSense or OPNsense software for maximum control.
What is the best firewall hardware device?
The best firewall hardware device for a homelab in 2026 is the Intel N100 platform. It offers modern x86 performance, AES-NI hardware acceleration, DDR5 RAM support, and 6W power consumption. Devices like the MOGINSOK N100 with 4x 2.5GbE Intel I226 NICs handle gigabit-plus throughput with full IDS/IPS. For enterprise-grade hardware, the FortiGate-60F delivers 1.4 Gbps IPS throughput with hardware-accelerated switching.
Who are the top 5 firewall vendors?
The top 5 firewall vendors for homelab use in 2026 are: Netgate (pfSense+ appliances), TP-Link (Omada SDN routers), Fortinet (FortiGate series), SonicWall (TZ series), and Zyxel (USG FLEX series). For open-source flexibility, vendors like MOGINSOK, Sharevdi, and VNOPN offer N100/J3710/J4105 mini PCs that run any firewall software. Each vendor serves different needs from budget SMB to enterprise-grade protection.
Final Verdict: Picking Your Home Lab Firewall
After three months of testing ten firewall appliances in my home lab, the clear winner for most homelab users in 2026 is an Intel N100 mini PC running OPNsense or pfSense. The MOGINSOK N100 delivers modern x86 performance, 2.5GbE port density, and silent fanless operation at a price that undercuts most enterprise alternatives.
If you want pre-built reliability with lifetime software updates, the Netgate 1100 pfSense+ Security Gateway is the safer choice. If you need enterprise-grade features and don’t mind subscription costs, the FortiGate-40F or SonicWall TZ280 deliver the goods. For pure budget value, the TP-Link ER605 V2 at $50 is unbeatable.
Whatever you pick, the best firewall appliance for home labs is the one that matches your throughput needs, runs the software you want to learn, and fits your budget. Pick from this list and you’ll have a solid foundation for network security learning, VLAN segmentation, VPN access, and IDS/IPS experimentation. Your homelab deserves better than a consumer router, and any of these ten devices will deliver.