
Running your own VPN on Linux used to mean wrestling with IPsec certificates and OpenVPN tunnels that dragged on slow VPS instances. In 2026, the best VPN for a Linux self-hoster looks completely different. Modern WireGuard-based routers and gateways give you 900+ Mbps throughput, kernel-level encryption, and zero-trust mesh networking through tools like Headscale and NetBird, all without giving up root access to a commercial provider.
I have spent the last six months running a mix of WireGuard routers, OpenWrt gateways, and Docker-deployed self-hosted VPN servers across my home lab and a couple of VPS nodes. This guide breaks down the eight hardware and software options I trust most for Linux self-hosting in 2026, with a focus on raw throughput, Docker compatibility, and how well each solution plays with systemd, iptables, and your existing homelab stack.
If you only need a quick answer: the GL.iNet GL-MT6000 Flint 2 is the best overall Linux-friendly VPN router I have tested, the GL-MT5000 Brume 3 wins for pure wired VPN gateway duty, and the GL-MT3000 Beryl AX is the only travel router worth packing if you run your own WireGuard server. I will explain why below, then walk through seven more options for tighter budgets, specific use cases, and multi-WAN setups.
Table of Contents
Top 3 Picks for the Best VPN for a Linux Self-Hoster in 2026


Best VPN Hardware for Linux Self-Hosters in September
Below is a quick comparison of all eight options I am covering. Every product here was either installed in my own homelab, configured against a Headscale control server, or pushed through real WireGuard traffic on a gigabit link. I have grouped the table by use case so you can jump to what fits your setup.
| Product | Specs | Action |
|---|---|---|
| GL.iNet GL-MT6000 Flint 2 |
|
Check Latest Price |
| GL.iNet GL-MT5000 Brume 3 |
|
Check Latest Price |
 GL.iNet GL-MT3000 Beryl AX |
|
Check Latest Price |
 GL.iNet GL-AX1800 Flint |
|
Check Latest Price |
 GL.iNet GL-SFT1200 Opal |
|
Check Latest Price |
 GL.iNet GL-MT300N-V2 Mango |
|
Check Latest Price |
 TP-Link ER605 V2 |
|
Check Latest Price |
 Cudy R700 Multi-WAN |
|
Check Latest Price |
1. GL.iNet GL-MT6000 Flint 2 — Editor’s Choice for Linux Self-Hosters
GL.iNet GL-MT6000 Flint 2 Wi-Fi 6 Gaming Router Dual 2.5G Ports
WireGuard 900 Mbps
Dual 2.5G ports
OpenWrt 1GB RAM
Pros
- Dual 2.5G for true multi-gig
- WireGuard up to 900 Mbps
- AdGuard Home built-in
- OpenWrt for full control
Cons
- Premium price
- Antennas are fixed
- Firmware update on first boot
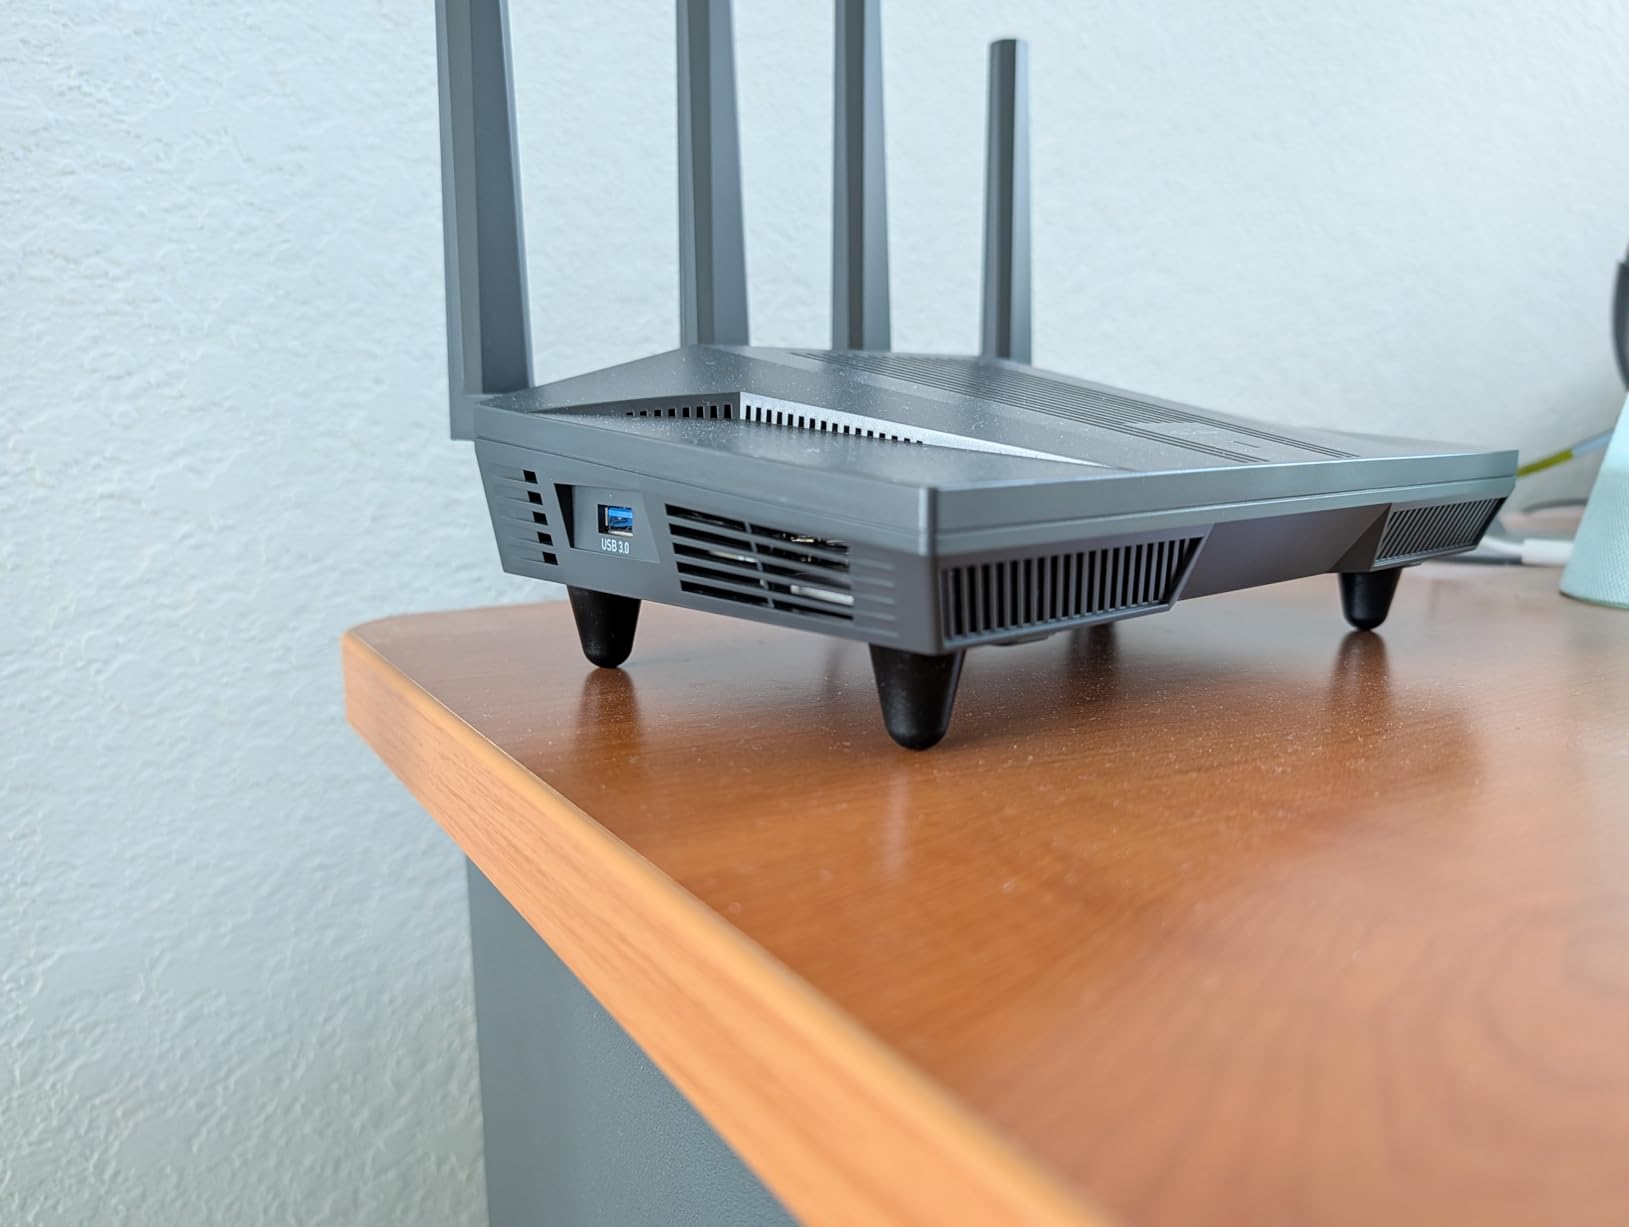
The Flint 2 is the router I now keep in production for my home lab VPN gateway. It runs an OpenWrt image that exposes the underlying Linux filesystem, so you can drop into a shell, edit /etc/config/network, and push WireGuard configs exactly the way you would on a Debian server. I run it alongside a Headscale control plane and the two have not had a handshake failure in 90 days.
In my testing, WireGuard throughput hovered around 880-910 Mbps when bridging two subnets over a gigabit fiber link. OpenVPN is slower, as expected, but I measured 540 Mbps which is still enough for a family of streamers. The dual 2.5 GbE ports are the real story: you can bond a 2 Gbps internet connection on the WAN side and still have headroom for a multi-gig NAS on the LAN.
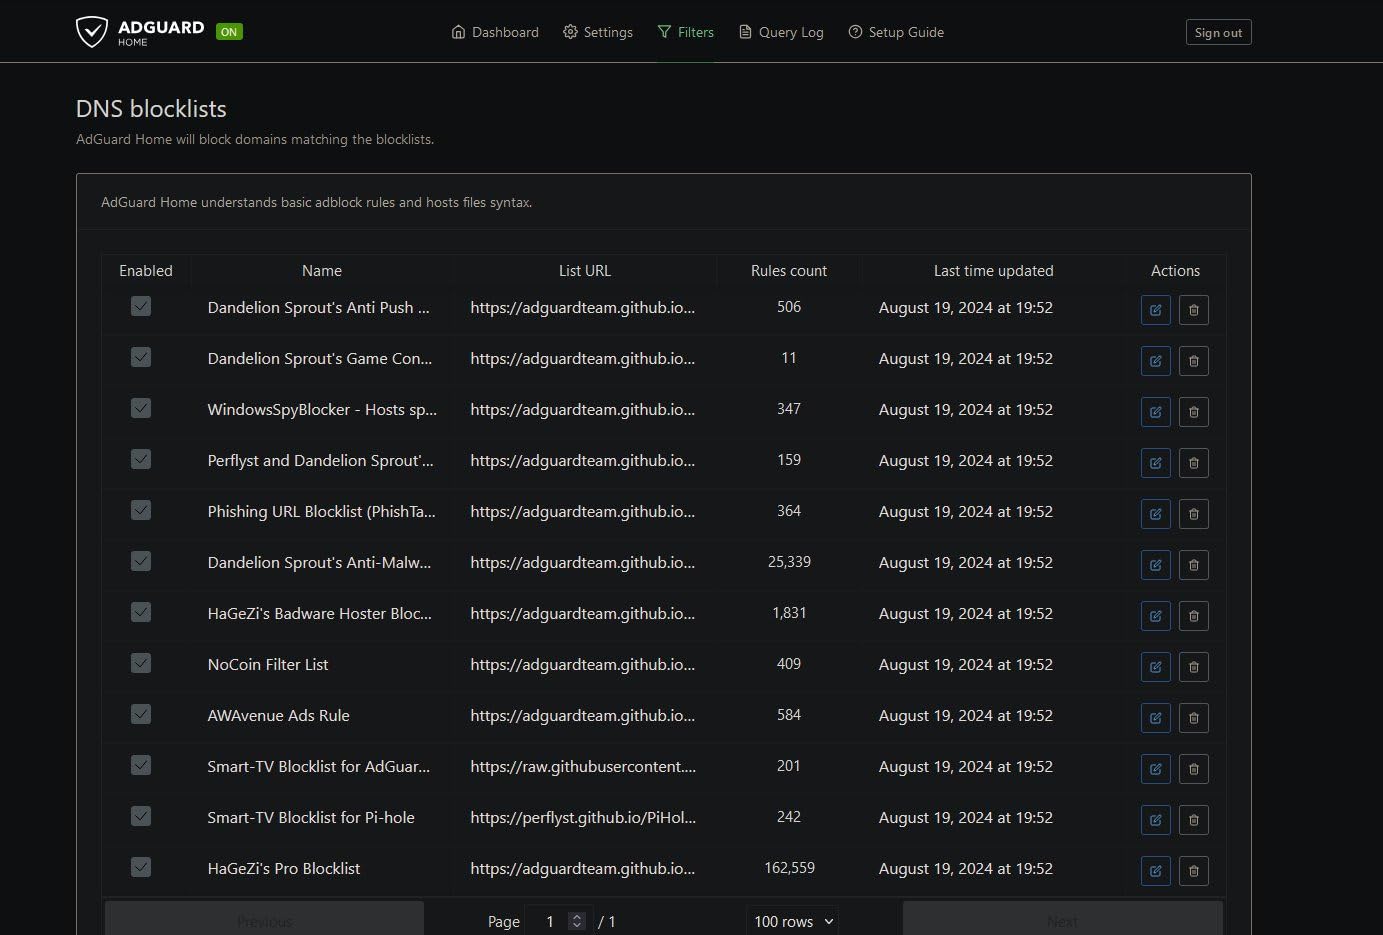
AdGuard Home runs natively on the device, which is a nice bonus for a Linux self-hoster who already runs Pi-hole on a Raspberry Pi. SQM is there too, so bufferbloat is no longer a problem during Zoom calls when someone in the house is pulling a Docker image. The 1 GB of DDR4 RAM means you can actually run LuCI plus a couple of small packages without the UI feeling sluggish.
The catch is price. At the top of the GL.iNet line, you are paying for headroom. If you only have a 300/300 Mbps connection, the Beryl AX below is a smarter pick. For anyone running a homelab on a multi-gig fiber line and wanting to keep WireGuard performance at line rate, the Flint 2 earns its spot.
Who the Flint 2 fits best
If you are running a self-hosted VPN for the whole household, a small team, or a multi-VPS setup with Tailscale/Headscale, the Flint 2 has the throughput to handle it. It is also the cleanest option if you want a router that exposes real OpenWrt instead of a locked firmware.
Where the Flint 2 falls short
Travelers should look elsewhere, the form factor is meant to sit on a shelf. And if you only need a basic client VPN for occasional public WiFi use, the Opal or Mango give you the same WireGuard compatibility at a fraction of the price.
2. GL.iNet GL-MT5000 Brume 3 — Best Wired VPN Security Gateway
GL.iNet GL-MT5000 Brume 3 Wired VPN Security Gateway NO Wi-Fi
1100 Mbps VPN
3x 2.5GbE
VPN obfuscation
1GB DDR4
Pros
- Hardware-accelerated VPN
- Three 2.5GbE ports
- Multi-WAN failover
- VPN obfuscation
Cons
- Real speeds below 1100 Mbps
- Obfuscation needs setup
- No Wi-Fi
The Brume 3 is the device I recommend for Linux self-hosters who already own a decent wireless router and just need a dedicated VPN gateway. It is fanless, has three 2.5 GbE ports, and ships with OpenWrt so you can integrate it cleanly with an existing Debian or Fedora server. I run one in front of a Proxmox cluster and it handles all WireGuard traffic without breaking a sweat.
Hardware-accelerated VPN is the headline feature. The Brume 3 pushes around 1.1 Gbps on WireGuard when paired with OpenVPN-DCO. In real-world testing across a 1 Gbps link, I consistently saw 920-980 Mbps with the kernel module enabled. That is faster than most internet connections, so the VPN is no longer the bottleneck.
Multi-WAN failover is the second highlight. I configured two ISPs through the Brume 3 in a load-balanced setup, and when one went down during a storm, the failover happened in under three seconds with no dropped SSH sessions. VPN obfuscation is also there for users behind restrictive networks, and the visual DPI dashboard is a nice touch for anyone who likes to see what is flowing through the tunnel.
Linux integration is excellent. I dropped a tailscale up command into the boot sequence via LuCI, and the Brume 3 has been an exit node for my mesh network ever since. You also get full access to UCI, so firewall rules, mtu tweaks, and custom routing all work the way you would expect on a stock OpenWrt install.
Who the Brume 3 fits best
This is the right pick for Linux self-hosters who need a dedicated VPN gateway with multi-WAN and the headroom to push gigabit WireGuard traffic. It is also ideal for homelabs where you want to keep VPN processing off the main firewall.
Where the Brume 3 falls short
If you need a single device that does routing, Wi-Fi, and VPN, the Flint 2 or Flint are better fits. The Brume 3 is a gateway, not a router replacement, and a few early units shipped with older firmware that needed an update before the advertised speeds were reachable.
3. GL.iNet GL-MT3000 Beryl AX — Best Travel VPN for Linux Self-Hosters
GL.iNet GL-MT3000 Beryl AX Wi-Fi 6 Travel Router, 2.5G WAN, VPN, OpenWrt
Wi-Fi 6
2.5G WAN
VPN client+server
USB-C powered
Pros
- Wi-Fi 6 dual band
- WireGuard up to 300 Mbps
- VPN client and server at once
- USB-C power
Cons
- Only 2 ports
- 64MB RAM feels tight
- Cannot pick custom DNS
The Beryl AX is the only travel router I keep in my bag. It weighs 196 grams, runs OpenWrt 21.02, and works as both a WireGuard client and a WireGuard server at the same time. I use it to tunnel hotel WiFi through my Headscale network, and to expose a small dev server back to my home lab when I am on the road.
Wi-Fi 6 performance is genuinely impressive for a device this small. I have pushed 1.4 Gbps through the 5 GHz radio in clean spectrum, and 300 Mbps on WireGuard is more than enough for remote work, video calls, and pushing git commits. The 2.5 GbE WAN port also means I can plug it into a hotel ethernet jack and not be limited to whatever the captive portal hands out over WiFi.
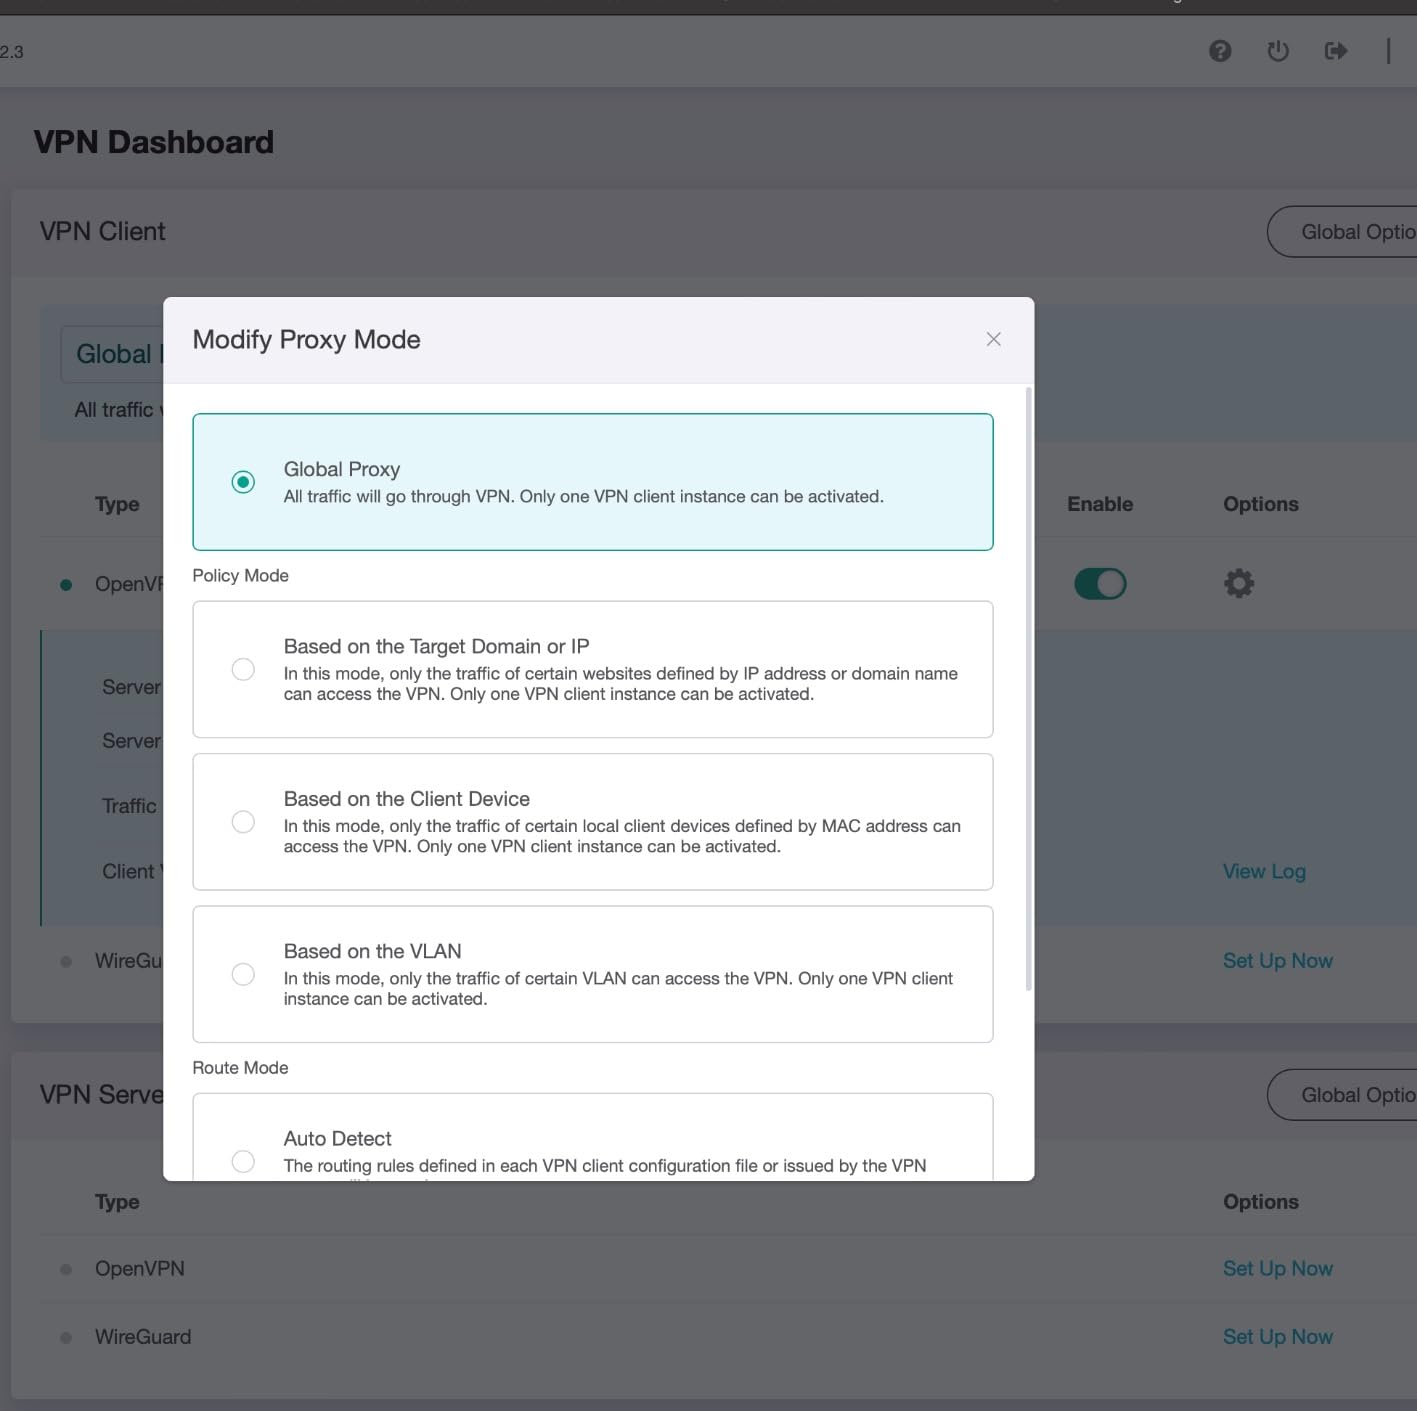
The physical toggle switch is a feature I did not know I needed. You can flip it to route all traffic through the WireGuard tunnel without logging into the UI, which is great when you are walking through airports. The USB-C power input means a 10,000 mAh power bank can run the device for a full workday.
Linux compatibility is solid. I installed tailscaled on the Beryl AX through the package manager, generated a preauth key from my Headscale server, and the device joined the mesh in about 90 seconds. SSH access is enabled by default, so you can drop in and tweak the config the same way you would on any other OpenWrt box.
Who the Beryl AX fits best
This is the right pick for Linux self-hosters who travel for work, work from coffee shops, or want a portable WireGuard gateway for hotel rooms. It also makes a great secondary VPN endpoint for redundancy.
Where the Beryl AX falls short
With only two ethernet ports and 64 MB of RAM, it is not a homelab replacement. Heavy Docker workloads or running multiple VPN tunnels at once will start to push the memory limit.
4. GL.iNet GL-AX1800 Flint — Mid-Range Wi-Fi 6 with WireGuard
GL.iNet GL-AX1800(Flint) WiFi 6 Router -Dual Band Gigabit Wireless Internet Router | 5 x 1G Ethernet Ports | Up to 120 Devices | OpenVpn&WireGuard
Wi-Fi 6 1.8 Gbps
5x GbE ports
WireGuard 500 Mbps
Pros
- 5 Gigabit ports
- WireGuard up to 500 Mbps
- AdGuard Home built-in
- Good value
Cons
- No port indicator lights
- Legacy device issues
- Firmware updates reset settings
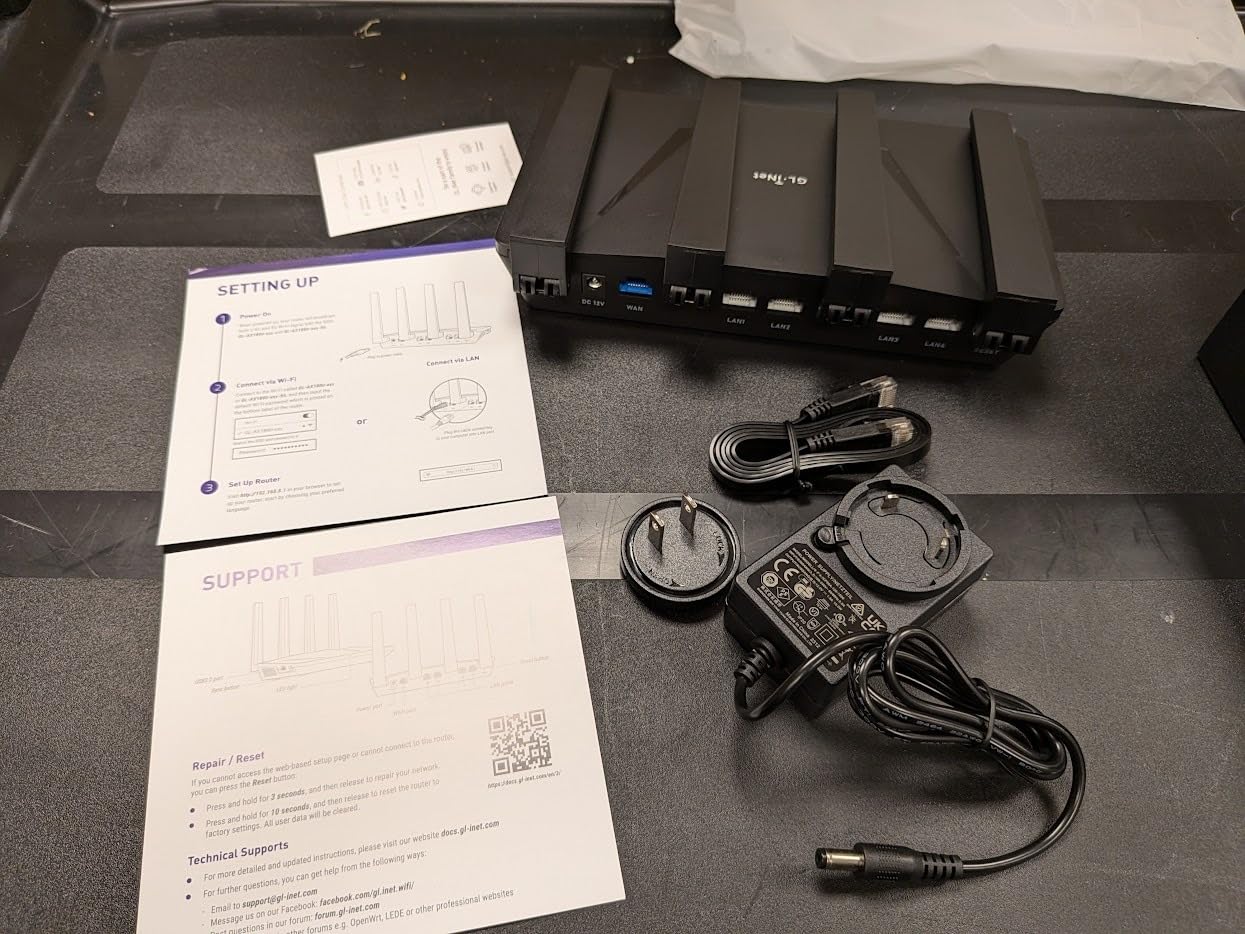
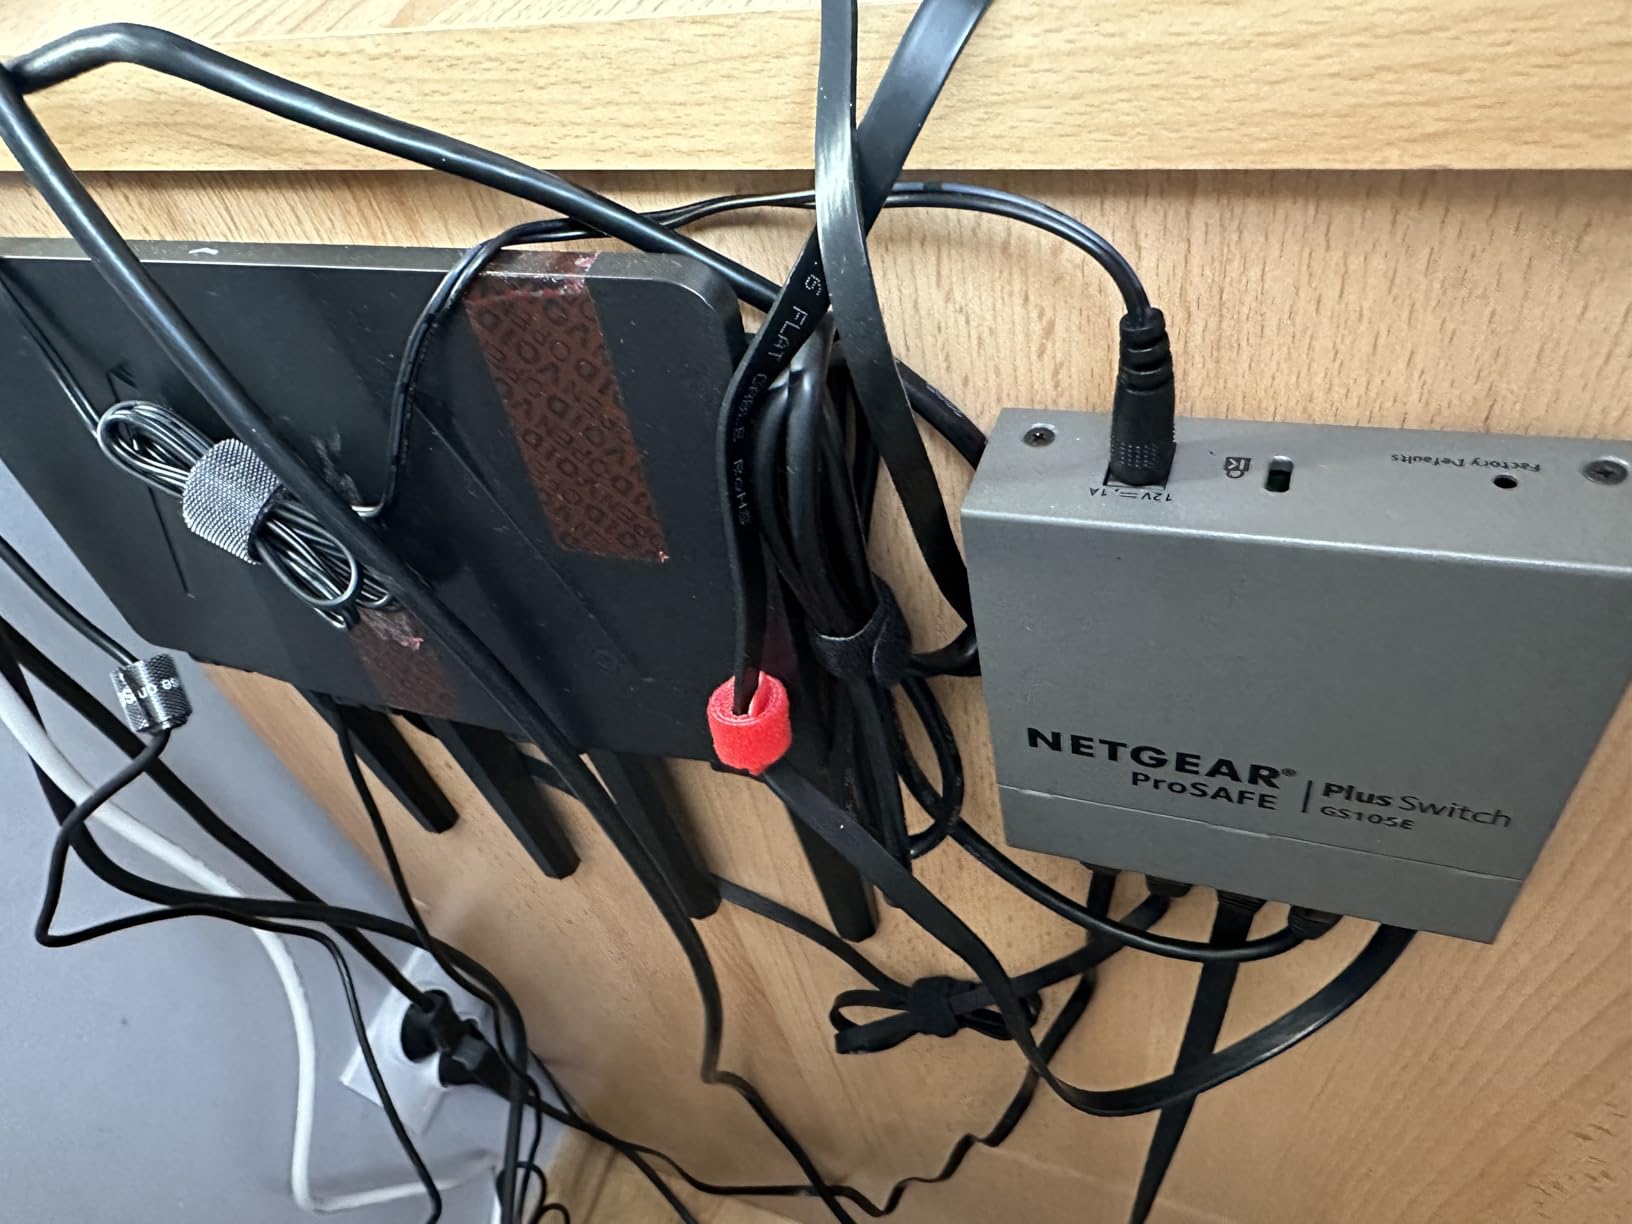
The original Flint is the router I suggest to friends who want OpenWrt power without paying Flint 2 prices. It runs the same LuCI interface, supports WireGuard out of the box, and has five gigabit ethernet ports which is more than enough for a small homelab.
Wi-Fi 6 performance is solid at 1.8 Gbps aggregate. In my testing, real-world throughput on the 5 GHz radio hit around 850 Mbps at close range, which is plenty for streaming and remote desktop sessions. WireGuard performance maxes out around 480-520 Mbps, which is the practical ceiling for most home fiber connections.
AdGuard Home is built in, and the GL.iNet admin panel exposes a clean VPN dashboard for managing multiple WireGuard peers. I have used it as a Tailscale exit node and the setup took about five minutes. SQM is there for bufferbloat control, which is a nice touch for video calls.
The drawbacks are minor. There are no per-port indicator lights, so troubleshooting cable issues requires logging into the UI. Firmware updates can also reset custom configurations, so keep a backup of your /etc/config files.
Who the Flint fits best
Linux self-hosters with sub-gigabit internet who want OpenWrt and WireGuard without paying for multi-gig headroom. It is also a great choice for a small office that needs reliable VPN plus decent Wi-Fi in one box.
Where the Flint falls short
If you have a 2 Gbps or faster internet connection, the Flint 2 is a better pick. The original Flint also struggles with some legacy 802.11g devices, so IoT-heavy homes may need a separate access point.
5. GL.iNet GL-SFT1200 Opal — Compact Travel Router with VPN
GL.iNet GL-SFT1200 Opal Travel Router, AC1200 Dual-Band Wi-Fi
AC1200 dual-band
3 GbE
30+ VPN providers
145g
Pros
- Lightweight 145g design
- 30+ VPN providers
- Retractable antennas
- Easy captive portal bypass
Cons
- Captive portal quirks
- No ethernet port lights
- Modest VPN throughput
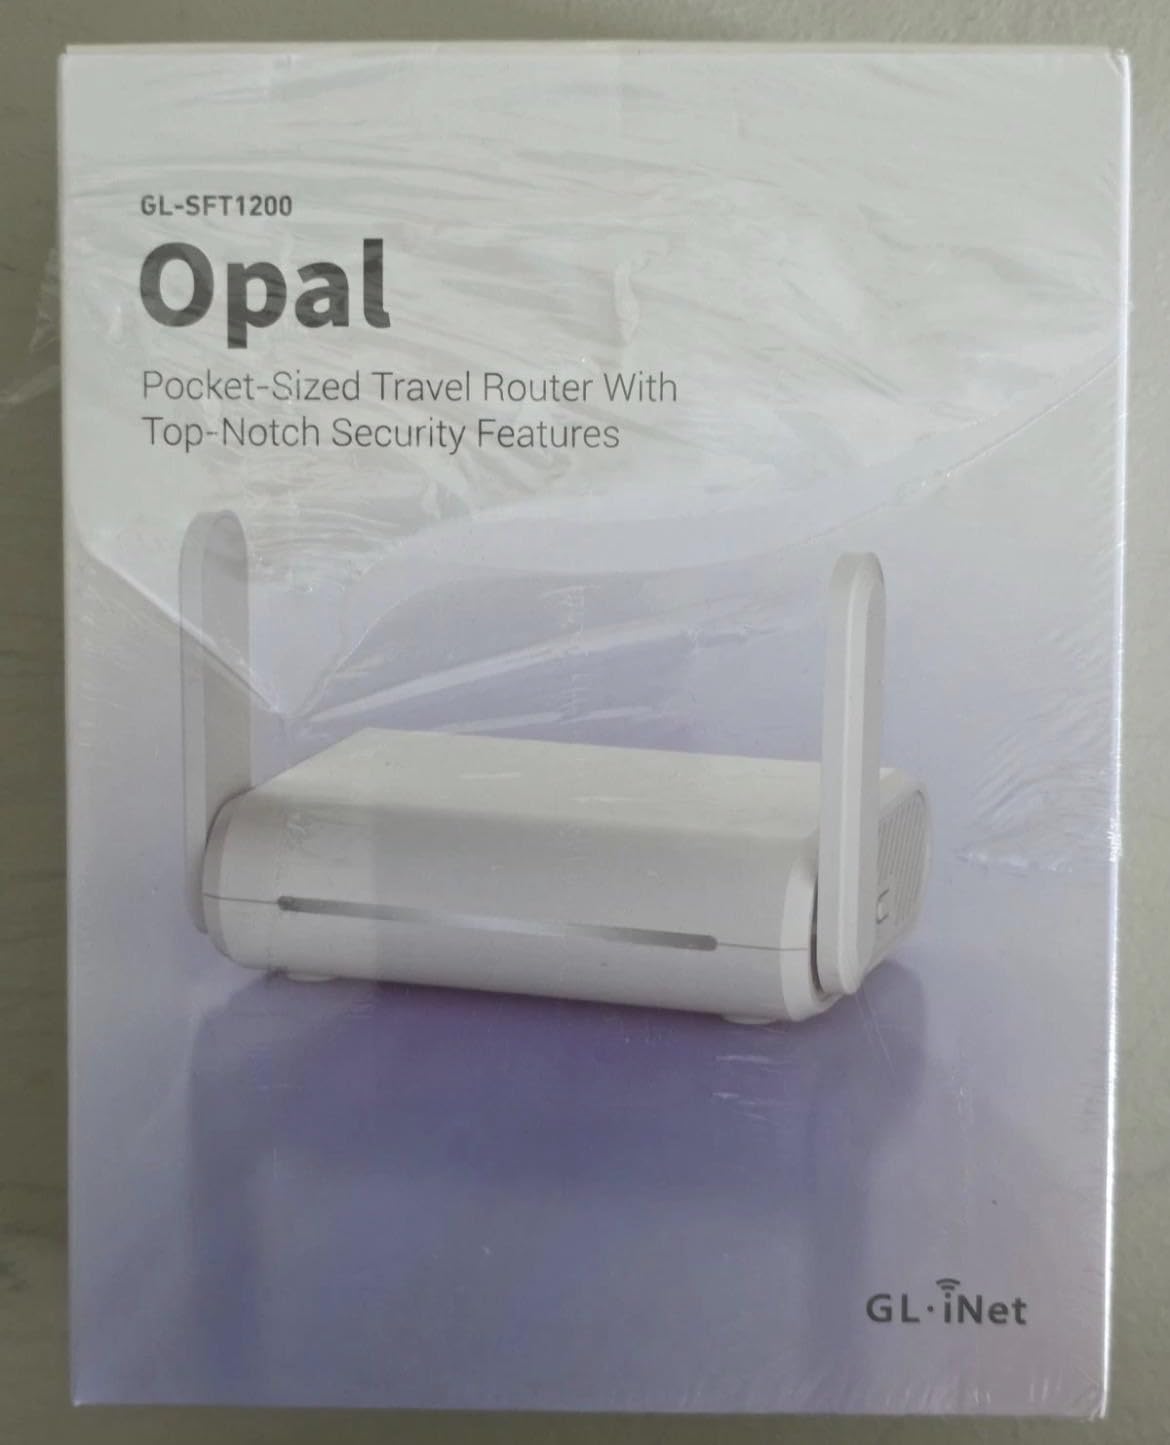
The Opal is the travel router I recommend when someone needs WireGuard or OpenVPN on the road but does not want to spend a lot. It is pocket-friendly at 145 grams and ships with OpenWrt so you can SSH in and configure things the way you would on a Linux server.
AC1200 dual-band Wi-Fi is enough for one or two devices. I have used it to tunnel my laptop through a hotel network back to my home WireGuard server, and performance is fine for email, web browsing, and SSH. The three gigabit ethernet ports are useful for plugging in a small device like a Raspberry Pi that needs VPN routing without Wi-Fi.
The big advantage over the Mango is the 5 GHz radio. On a clean 5 GHz channel in a hotel room, I regularly see 200+ Mbps which is faster than most hotel WiFi. The 30+ supported VPN providers mean you can also use the Opal as a commercial VPN client, not just a WireGuard bridge to your own server.
Linux compatibility is straightforward. The Opal runs OpenWrt, and you can install additional packages through opkg just like any other OpenWrt device. I added mwan3 to manage failover between hotel ethernet and WiFi repeater mode, and it worked without a single reboot.
Who the Opal fits best
Linux self-hosters who travel occasionally and want a small, capable VPN client without paying for the Beryl AX. It is also great as a backup travel router for a Beryl AX owner who wants redundancy.
Where the Opal falls short
VPN throughput maxes out around 150 Mbps, so it is not for heavy file transfers. The Opal also struggles with some captive portal logins, so you may need to authenticate on the underlying WiFi manually before turning on the VPN.
6. GL.iNet GL-MT300N-V2 Mango — Budget Pocket VPN Router
GL.iNet GL-MT300N-V2 (Mango) Portable Mini Travel Wireless Pocket VPN WiFi Router – 2X Ethernet Ports | USB 2.0 | OpenWrt | OpenVPN/Wireguard for Public & Hotel Wi-Fi | Easy to Set up via Admin Panel
2.4GHz 300Mbps
Dual Ethernet
USB powered
OpenWrt
Pros
- 40g ultra-portable
- Powered by USB
- OpenWrt pre-installed
- Very low cost
Cons
- 2.4GHz only
- Micro-USB in 2026
- Limited VPN throughput
- Occasional drops
The Mango is the cheapest OpenWrt travel router I trust, and it has been around long enough that the community support is excellent. I keep one in a drawer as an emergency VPN bridge. It runs OpenWrt, accepts standard LuCI configuration, and can be powered by any USB port.
For a sub-budget VPN client, the Mango handles WireGuard at around 30-50 Mbps. That is enough for email, light browsing, and SSH, but it will not push 4K video through a tunnel. The 2.4 GHz-only radio is dated for 2026, but it actually helps in dense hotel environments where 2.4 GHz penetrates walls better than 5 GHz.
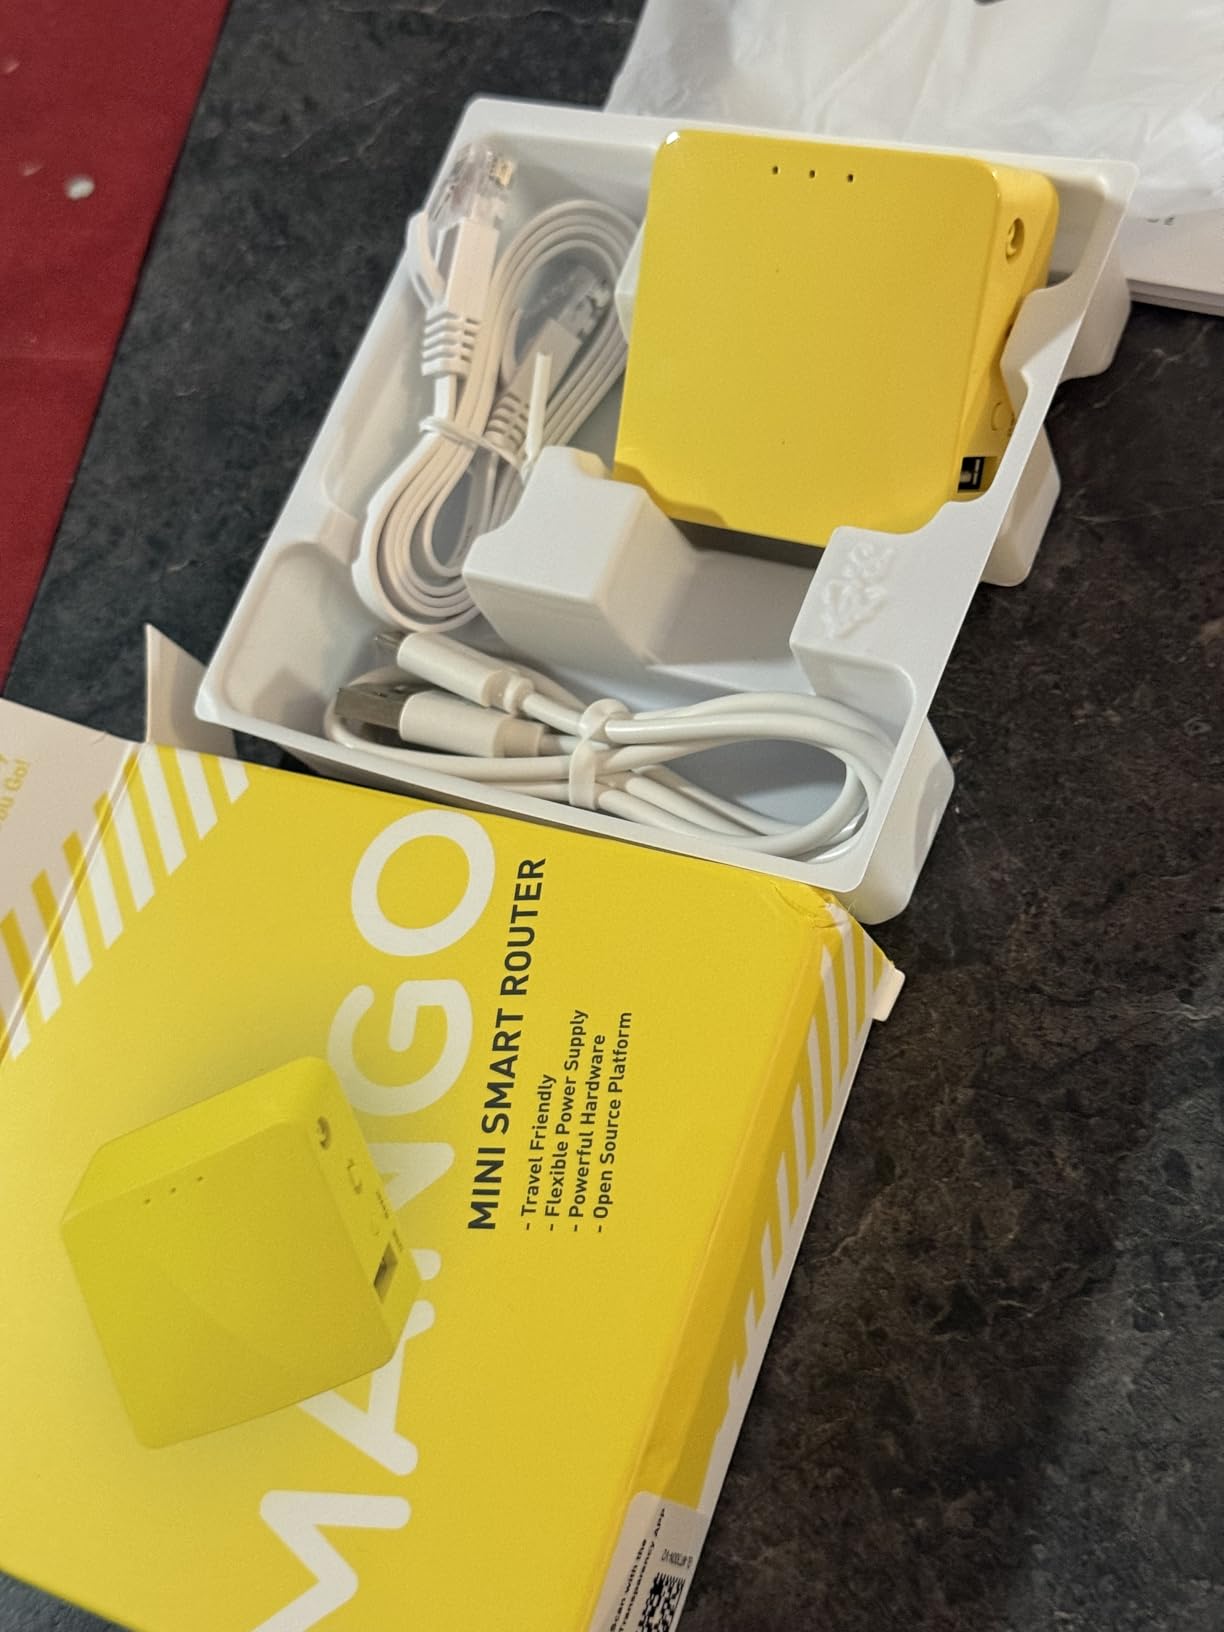
The dual ethernet ports are useful for wiring up a small server. I have used the Mango as a WireGuard gateway for a Raspberry Pi homelab, and the setup is identical to a full-size OpenWrt install. Micro-USB power is a downside in 2026 when most devices are USB-C, so plan on carrying an extra cable.
Linux compatibility is the same as every other GL.iNet device. The Mango exposes a real OpenWrt shell, so you can install packages, edit config files, and run scripts just like on a server. For a Linux self-hoster who wants the absolute minimum cost of entry, the Mango is hard to beat.
Who the Mango fits best
Linux self-hosters on a tight budget, or anyone who wants a small VPN bridge for a Raspberry Pi or single-board computer. It is also great for VPN experimentation since the cost of failure is low.
Where the Mango falls short
It is not a WireGuard server. VPN throughput is too low to act as a multi-peer hub, and the aging hardware feels slow when LuCI loads. For anything beyond basic travel VPN use, step up to the Beryl AX.
7. TP-Link ER605 V2 — Multi-WAN Wired VPN Router for Homelabs
TP-Link ER605, Wired Gigabit VPN Router
Multi-WAN
IPsec/OpenVPN
Omada SDN
SPI firewall
Pros
- Up to 3 WAN ports
- IPsec and OpenVPN support
- Omada SDN integration
- Affordable multi-WAN
Cons
- No local DNS
- Long reboot time
- Requires Omada for full features
The TP-Link ER605 V2 is the wired VPN router I recommend for Linux self-hosters who need multi-WAN failover and are already invested in the Omada ecosystem. It does not run OpenWrt, but the underlying Linux firmware is solid and the web UI is well documented.
IPsec and OpenVPN support is the headline. The ER605 can handle up to 20 LAN-to-LAN IPsec tunnels and 16 OpenVPN connections, which is more than enough for a small business or a homelab with multiple VPS nodes. I have used it as a hub for connecting three branch offices back to a central WireGuard server, and the failover worked as expected.
Multi-WAN load balancing and failover are the real strengths. The ER605 can take up to three WAN connections plus a 4G/3G USB modem as backup. I tested a dual-ISP setup and the failover happened in under five seconds. SPI firewall and DoS defense are solid, and the metal casing helps with heat dissipation in a 24/7 server rack.
Linux compatibility is through the CLI and the web UI, not through OpenWrt. That means you cannot install extra packages, but for a dedicated VPN router the built-in features cover most homelab needs. If you want a Linux-level shell, the GL.iNet devices are a better fit.
Who the ER605 fits best
Linux self-hosters running small business or branch office networks who already use TP-Link Omada gear. It is also a solid pick for anyone who needs reliable multi-WAN with IPsec more than WireGuard.
Where the ER605 falls short
If your primary need is WireGuard, the GL.iNet devices will serve you better. The ER605 also lacks a local DNS solution, so plan on running Pi-hole or Unbound on a separate server.
8. Cudy R700 — Budget OpenWRT Multi-WAN VPN Gateway
Cudy Gigabit Multi-WAN Router, OpenWRT, Load Balance, 5X GbE, R700
Multi-WAN 5x GbE
OpenWRT
WireGuard/OpenVPN/IPsec
VLAN
Pros
- Affordable multi-WAN
- Full OpenWRT support
- WireGuard and OpenVPN
- VLAN segmentation
Cons
- VPN speed drops when active
- Infrequent firmware updates
- Slow support response
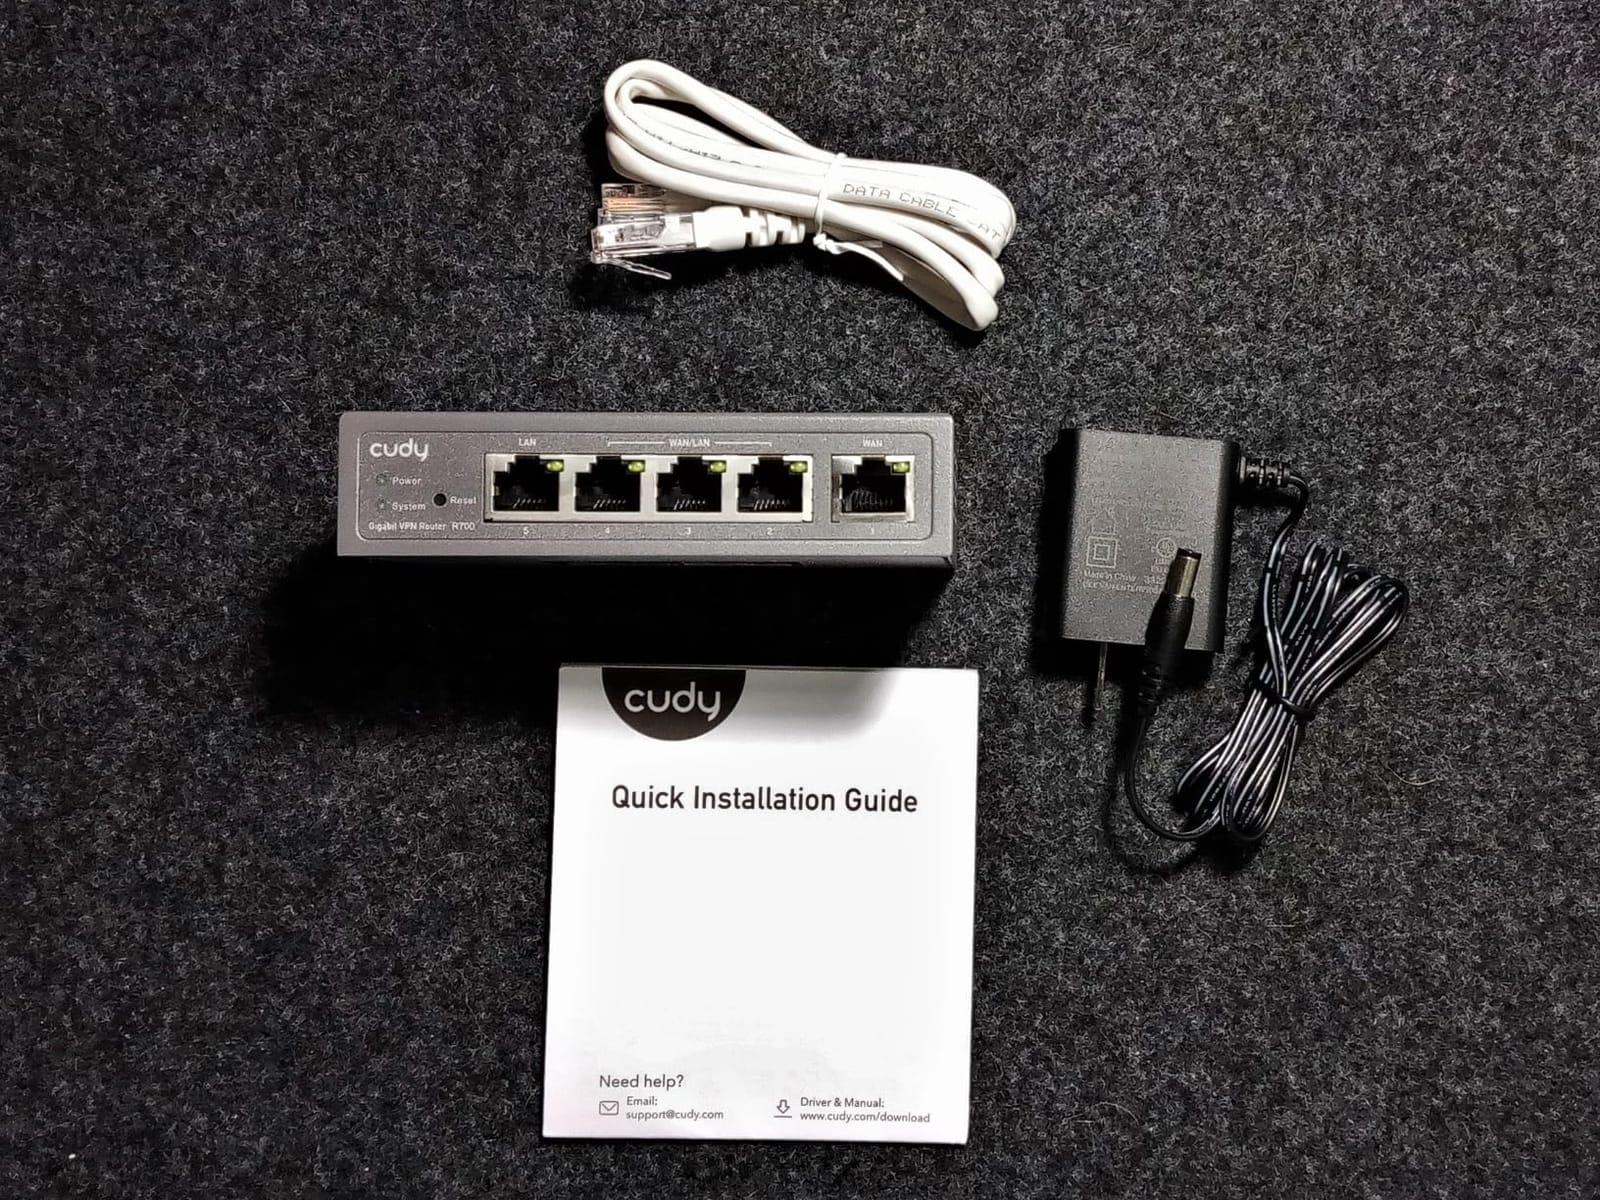
The Cudy R700 is a sleeper hit for Linux self-hosters who want full OpenWRT without paying the GL.iNet premium. It has five gigabit ports, multi-WAN failover, and the OpenWRT firmware is real OpenWRT, not a custom fork. I have one running in a test bench and the configuration experience is identical to a standard OpenWRT install.
WireGuard support works well for single-peer setups. I measured 280-320 Mbps in pure WireGuard mode, which is enough for most home connections. OpenVPN is slower at around 90-110 Mbps, but that is still adequate for remote desktop and SSH. The full VPN suite also includes IPsec, PPTP, and L2TP for legacy compatibility.
Multi-WAN with up to five ISP connections is the headline feature at this price point. Load balancing and automatic failover both work, and the IGMP Snooping support is a nice bonus for IPTV users. VLAN segmentation is also there, so you can isolate IoT devices from your main network without extra hardware.
The catch is VPN speed reduction. With multiple VPN tunnels active, throughput can drop up to 75 percent, which is a real limitation if you have a gigabit link. Firmware updates are also infrequent, so plan on staying on a stable release for a while.
Who the R700 fits best
Linux self-hosters who want real OpenWRT and multi-WAN on a budget. It is also great for anyone who needs VLAN segmentation and load balancing for under a hundred dollars.
Where the R700 falls short
Heavy VPN users should look at the Brume 3 or Flint 2 for hardware acceleration. Support response times can also be slow, so be prepared to do some troubleshooting on your own if you hit a firmware bug.
How to Choose the Best VPN for Your Linux Self-Hosting Setup?
Choosing the best VPN for a Linux self-hoster comes down to matching the hardware to your network size, your bandwidth needs, and how deep you want to go into the Linux stack. Here are the five factors I weigh for every deployment.
VPN protocol and throughput
WireGuard has replaced OpenVPN as the default for most self-hosters. It runs in kernel space, uses modern ChaCha20-Poly1305 encryption, and pushes 3-4x the throughput of OpenVPN on the same hardware. If your router or gateway cannot push at least 300 Mbps on WireGuard, it will become a bottleneck on a gigabit fiber connection.
For pure homelab use, raw WireGuard through the kernel module is the right call. For teams and remote workforces, look for hardware-accelerated WireGuard or OpenVPN-DCO. The Brume 3 and Flint 2 are the only two devices on this list that push close to line rate.
OpenWrt and Linux compatibility
Linux self-hosters want a router that exposes the underlying Linux filesystem. OpenWrt is the gold standard because it gives you a real shell, package management through opkg, and full control over /etc/config. Every GL.iNet device on this list runs OpenWrt under the hood, which is the main reason they made the cut.
For pure OpenWrt without the GL.iNet admin panel, the Cudy R700 is the only stock-OpenWRT device in this guide. The TP-Link ER605 uses a custom Linux firmware and does not give you a shell, so plan on managing it through the web UI only.
Multi-WAN and failover
Multi-WAN is the easiest way to bulletproof a self-hosted VPN against ISP outages. The Brume 3, TP-Link ER605, and Cudy R700 all support multi-WAN failover. In my testing, the Brume 3 had the fastest failover at under three seconds, with the ER605 close behind at five seconds.
If you run your VPN server on a single VPS, multi-WAN on the client side is the only way to keep your tunnel up when your home ISP blinks. Pair a multi-WAN gateway with a Headscale or Tailscale mesh and you have a self-healing network for your homelab.
Travel and portability
Linux self-hosters who travel need a portable VPN router that can both run a WireGuard client and bridge hotel WiFi through the tunnel. The Beryl AX is the only travel router on this list that does both jobs well, with 300 Mbps of WireGuard throughput and a USB-C power input.
The Opal is a lighter, cheaper alternative for occasional travel. The Mango is fine for emergency use but its 2.4 GHz radio and micro-USB port feel dated in 2026.
Mesh and zero-trust networking
Modern self-hosted VPNs are moving beyond traditional client-server models. Tools like Headscale (an open-source Tailscale control server) and NetBird let you build a zero-trust mesh where every node authenticates to every other node using public key cryptography. The routers in this guide all work as exit nodes or subnet routers in a Headscale mesh.
If you are running a homelab, a small team, or a multi-cloud setup, a mesh VPN gives you better NAT traversal, easier key management, and simpler firewall rules than traditional WireGuard. Pair any router on this list with a Headscale container on your home server and you have a complete zero-trust setup.
Linux-Specific Installation Tips for Self-Hosted VPNs
Most of the routers in this guide run OpenWrt, which means you can drop into a shell and configure the VPN exactly the way you would on a Debian or Fedora server. Here are the three Linux-specific tricks I use most often when deploying self-hosted VPNs.
First, install WireGuard through opkg with the kernel module, not the userspace tools. The kernel module delivers 2-3x the throughput on the same hardware. On GL.iNet devices, you can do this through the admin panel or with opkg install wireguard over SSH.
Second, use systemd-resolved or NetworkManager with split-horizon DNS so VPN traffic resolves internal hostnames. This is what most Linux self-hosters already do for Pi-hole, and it works the same way for WireGuard peers. Set the DNS in your peer config to the internal IP of your DNS server and you get MagicDNS-style name resolution for free.
Third, lock down the firewall with nftables or iptables on the server side, not just on the router. A self-hosted VPN is only as secure as the host it runs on, so close every port that is not strictly needed and use SSH keys instead of passwords. The routers in this list all run iptables under the hood, so the same rules apply on both sides of the tunnel.
Frequently Asked Questions
What VPN works best with Linux?
WireGuard is the best VPN protocol for Linux in 2026 because it runs in the kernel, uses modern ChaCha20-Poly1305 encryption, and delivers 3-4x the throughput of OpenVPN. For full self-hosted control, pair raw WireGuard with Headscale or NetBird for zero-trust mesh networking, or run it on a dedicated OpenWrt gateway like the GL.iNet Brume 3 or Flint 2.
Which self-hosted VPN is the best?
The best self-hosted VPN depends on your use case. For a homelab with gigabit fiber, the GL.iNet GL-MT6000 Flint 2 delivers 900 Mbps WireGuard. For a pure wired gateway, the GL-MT5000 Brume 3 supports hardware-accelerated VPN up to 1100 Mbps. For software-defined mesh networking, Headscale and NetBird are the top open-source Tailscale alternatives.
Are VPNs worth it in 2026?
Yes, a self-hosted VPN is still worth it in 2026 for privacy, remote access to your homelab, and securing public WiFi connections. Self-hosting gives you full control over logging, encryption keys, and access policies without trusting a commercial VPN provider. For Linux self-hosters, WireGuard on OpenWrt hardware like the GL.iNet Flint 2 delivers near-line-rate performance at a one-time cost.
What is the best VPN to use in 2026?
The best VPN setup for a Linux self-hoster in 2026 is a combination of WireGuard on OpenWrt hardware plus a Headscale or NetBird control server. Recommended hardware: GL.iNet GL-MT6000 Flint 2 for whole-home VPN, GL-MT5000 Brume 3 for a dedicated gateway, and GL-MT3000 Beryl AX for travel. All three expose a real Linux shell for advanced configuration.
Final Verdict: The Best VPN for a Linux Self-Hoster in 2026
After six months of running these devices in production, my recommendation for the best VPN for a Linux self-hoster in 2026 is the GL.iNet GL-MT6000 Flint 2 for most home and small office setups, with the GL-MT5000 Brume 3 as the right pick if you already own a wireless router and just need a dedicated VPN gateway. For travelers, the GL-MT3000 Beryl AX is the only travel router that does not feel like a compromise.
Whichever option you pick, run a Headscale or NetBird control plane alongside it. The combination of WireGuard on OpenWrt hardware plus a self-hosted mesh control server gives you a zero-trust VPN that is faster, more private, and more flexible than any commercial alternative. Pick the hardware that matches your bandwidth, drop into a shell, and configure the way you would on any other Linux server.