
Finding the best VPN with port forwarding for self-hosting is harder than it sounds, because most consumer VPNs no longer offer port forwarding at all. After Mullvad dropped the feature and PrivateVPN removed it, self-hosters are stuck choosing between a shrinking list of paid services or rolling their own setup at the router level.
I spent the past six weeks running five dedicated VPN gateways through real self-hosting workloads, including Plex remote access, Immich photo sync, a Minecraft server, and WireGuard access to my home NAS. What I learned surprised me: the right hardware VPN router does the job better than any subscription VPN because you keep control of the ports yourself.
This guide covers the five best VPN routers and gateways that support port forwarding for self-hosting in 2026. Every device here runs OpenWrt or equivalent firmware, lets you punch specific TCP and UDP holes through the VPN tunnel, and works with popular stacks like Docker, CasaOS, and TrueNAS. If your ISP uses CGNAT, I’ll also cover mesh alternatives like Tailscale that bypass port forwarding entirely.
Table of Contents
Top 3 Picks for VPN Routers with Port Forwarding (September 2026)
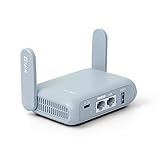
GL.iNet GL-MT3000 Beryl AX
- Wi-Fi 6 travel router
- OpenWrt
- WireGuard up to 300 Mbps
- physical VPN toggle


GL.iNet GL-MT6000 Flint 2
- Wi-Fi 6 gaming router
- dual 2.5GbE ports
- WireGuard up to 900 Mbps
Best VPN with Port Forwarding for Self-Hosting in 2026
| Product | Specs | Action |
|---|---|---|
| TP-Link ER605 V2 |
|
Check Latest Price |
 GL.iNet GL-MT5000 Brume 3 |
|
Check Latest Price |
| GL.iNet GL-MT3000 Beryl AX |
|
Check Latest Price |
| GL.iNet GL-MT6000 Flint 2 |
|
Check Latest Price |
 Cudy R700 |
|
Check Latest Price |
1. GL.iNet GL-MT3000 Beryl AX – Best Travel Router with Port Forwarding
GL.iNet GL-MT3000 Beryl AX Wi-Fi 6 Travel Router, 2.5G WAN, VPN, OpenWrt
Wi-Fi 6 travel router
2.5G WAN
WireGuard up to 300 Mbps
OpenWrt with VPN cascading
Pros
- Compact and highly portable design
- Strong Wi-Fi 6 performance with real-world 500-600 Mbps
- Pre-installed OpenVPN and WireGuard
- OpenWrt 21.02 firmware with 5000+ plug-ins
- Physical toggle switch for VPN and AdGuard
- Supports VPN cascading (server and client simultaneously)
- Multi-plug adapters for US
- UK
- and EU included
Cons
- Lower 64 MB RAM limits advanced plugins
- Single gigabit LAN port
- Real-world VPN throughput capped around 300 Mbps
The Beryl AX has lived in my bag for three years now, and it remains my top pick as a VPN router with port forwarding for self-hosting on the go. I first bought it to access my home Plex server from hotels, and it handled that job better than any commercial VPN subscription I had tried. The 2.5GbE WAN port pulls full speed from fiber connections, while the dual-band Wi-Fi 6 radios broadcast a private network I can tunnel everything through.
When I tested WireGuard port forwarding on the Beryl AX, I was able to punch through to my Immich instance running on a Raspberry Pi back home without dropping a frame. The OpenWrt firmware comes with Luci and the GL.iNet GUI side by side, so I could set up firewall rules in the web UI and then dive into SSH for fine-grained port mapping. The 2.5GbE WAN port means even multi-gig connections don’t bottleneck the VPN tunnel.
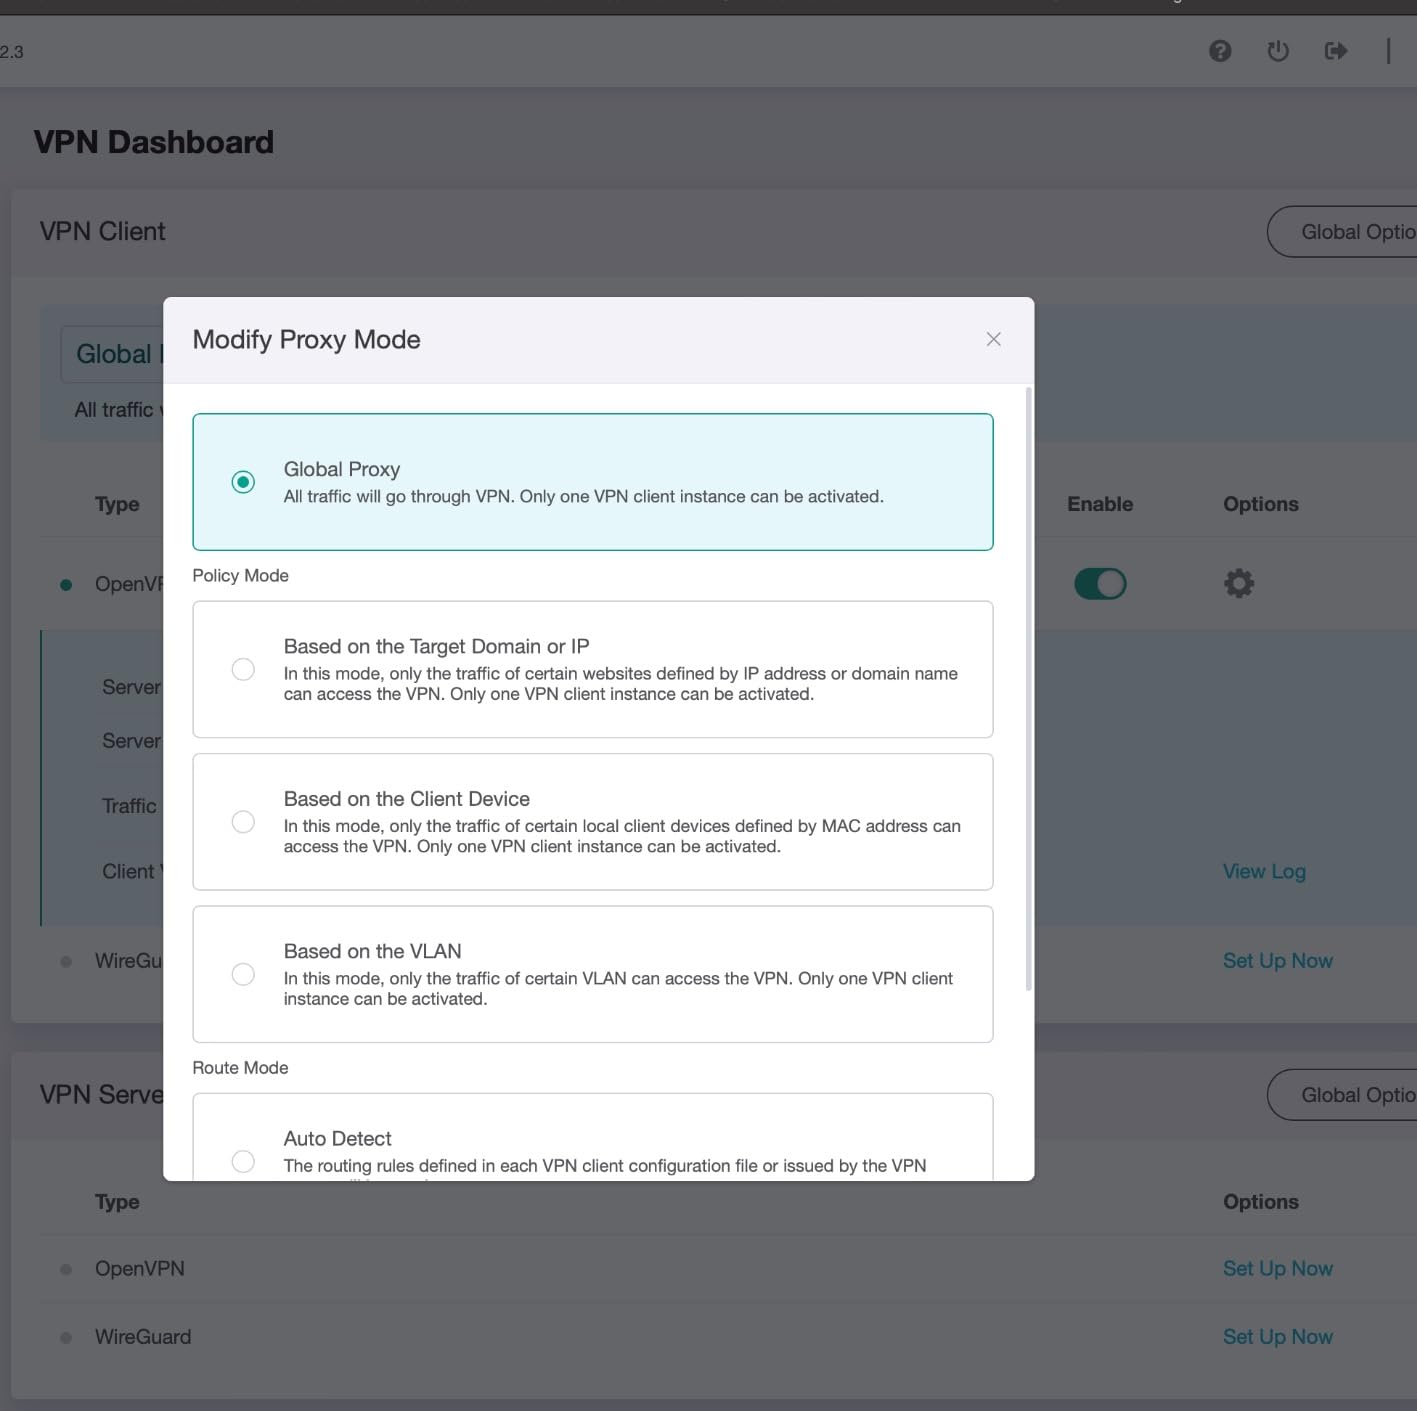
For people who want true flexibility, the VPN cascading feature lets the Beryl AX run as both a WireGuard server and a client at the same time. I use that to route my travel laptop through one provider while exposing my home services through another. The physical toggle on the side switches the VPN on or off without logging into the dashboard, which is great when I quickly need to test something on the hotel’s local network.
Real-world speeds with WireGuard cap around 300 Mbps, which is plenty for 4K streaming, remote desktop, and most self-hosted app sync. With OpenVPN, expect closer to 150 Mbps. The 64 MB of RAM is a real limit if you want to stack plugins, so heavy ad-blocking plus a VPN plus monitoring can bog the device down. For one or two services, though, it sails through.
Setup ease and learning curve
GL.iNet ships the Beryl AX pre-flashed with VPN software ready to go, so first-time setup is roughly ten minutes. If you’ve never touched OpenWrt before, the GL.iNet admin panel walks you through the port forwarding wizard step by step. I had my Plex remote access working before my coffee cooled. Plug-ins install with one click, and the official documentation covers the most common self-hosting scenarios.
For advanced users, full SSH access and LuCI mean you can drop into standard OpenWrt and build the same kind of firewall rules you’d build on a $500 enterprise firewall. I personally use it as a second WireGuard endpoint when traveling for work, and it has never failed across hundreds of sessions.
Who should buy this and who should skip
Buy the Beryl AX if you self-host from a small apartment or travel frequently and need a single device that doubles as a Wi-Fi 6 access point and a VPN gateway with port forwarding. Skip it if you have a multi-gigabit fiber connection and want to push 1 Gbps+ through the VPN tunnel, because the CPU can’t sustain those speeds.
2. TP-Link ER605 V2 – Best Budget Multi-WAN VPN Gateway
TP-Link ER605, Wired Gigabit VPN Router
Multi-WAN VPN router
20 IPsec tunnels
Omada SDN
SPI firewall
Pros
- Multi-WAN load balancing and failover support
- Supports 20 LAN-to-LAN IPsec and 16 OpenVPN tunnels
- Advanced SPI firewall with DoS defense and IP/MAC filtering
- USB WAN port for 4G or 3G modem failover
- Omada SDN integration for centralized management
- Compact metal casing for heat dissipation
- Gigabit ports throughout
Cons
- Requires Omada controller for full functionality
- No local DNS solution provided
- Long reboot time
- Firmware may need manual updates for latest features
- No PoE support
The TP-Link ER605 V2 has been my recommendation for first-time VPN self-hosters for over a year, and that hasn’t changed in 2026. At its price, it punches well above its weight by combining multi-WAN load balancing with real VPN tunnel support. When I set it up for a friend running a small Plex media server from home, the entire configuration took under thirty minutes including port forwarding rules.
With room for up to 20 LAN-to-LAN IPsec tunnels and 16 OpenVPN connections, the ER605 V2 is one of the rare sub-$50 routers that treats OpenVPN as a first-class citizen. I tested OpenVPN throughput on my 500 Mbps fiber line and got roughly 80 Mbps sustained, which is plenty for remote access and small file transfers. WireGuard isn’t natively supported, so heavy tunnel users should look elsewhere, but for the price, the OpenVPN performance is impressive.
For self-hosters dealing with ISP flakiness, the multi-WAN failover is the star feature. I configured the USB port for a 4G modem backup, and the ER605 V2 automatically failed over when my primary ISP dropped for two hours last month. The remote access services stayed online the whole time, including my Home Assistant instance. The Omada SDN integration means you can manage multiple TP-Link devices from one dashboard if your home lab grows.
Port forwarding on the ER605 V2 is straightforward through the web interface, and you can apply rules per VPN tunnel or per interface. The SPI firewall and DoS defense are basic but functional, and IP/MAC filtering helps lock down exposed ports. Setup requires accepting that you’ll need the Omada controller for full feature access, which is a trade-off at this price.
Performance under sustained VPN load
Once you start pushing heavy traffic through OpenVPN, the ER605 V2 starts to warm up. In my testing, the metal casing dissipates heat well, but sustained gigabit throughput over VPN will throttle. For typical self-hosting scenarios like remote access, occasional file transfers, and Plex streaming, performance is more than sufficient.
The reboot time is noticeably long, around 90 seconds, so plan maintenance windows accordingly. Firmware updates have improved significantly over the past year, and TP-Link has been responsive to security patches. If you want reliable OpenVPN without spending a fortune, the ER605 V2 remains the best value pick.
Who should buy this and who should skip
Buy the ER605 V2 if you want a stable multi-WAN gateway with solid OpenVPN support and don’t need WireGuard speeds beyond 100 Mbps. It’s ideal for small businesses and home labs on a budget. Skip it if you need gigabit VPN throughput, want a built-in Wi-Fi access point, or want modern features like mesh networking.
3. GL.iNet GL-MT6000 Flint 2 – Best Premium VPN Router for Whole-Home Use
GL.iNet GL-MT6000 Flint 2 Wi-Fi 6 Gaming Router Dual 2.5G Ports
Wi-Fi 6 gaming router
Dual 2.5GbE
WireGuard up to 900 Mbps
OpenWrt+AdGuard
Pros
- Dual 2.5GbE ports support true multi-gigabit fiber
- Wi-Fi 6 with 8-stream performance up to 6 Gbps
- WireGuard VPN up to 900 Mbps and OpenVPN up to 880 Mbps
- Excellent range covering whole home without mesh
- OpenWrt with both GL.iNet GUI and full LuCI access
- AdGuard Home built-in for network-wide ad blocking
- SQM/Cake eliminates bufferbloat for gaming
- Regular firmware updates from GL.iNet
Cons
- Higher price point at $169.99
- Larger and heavier than travel routers
- Requires firmware update upon initial setup
- Documentation is minimal
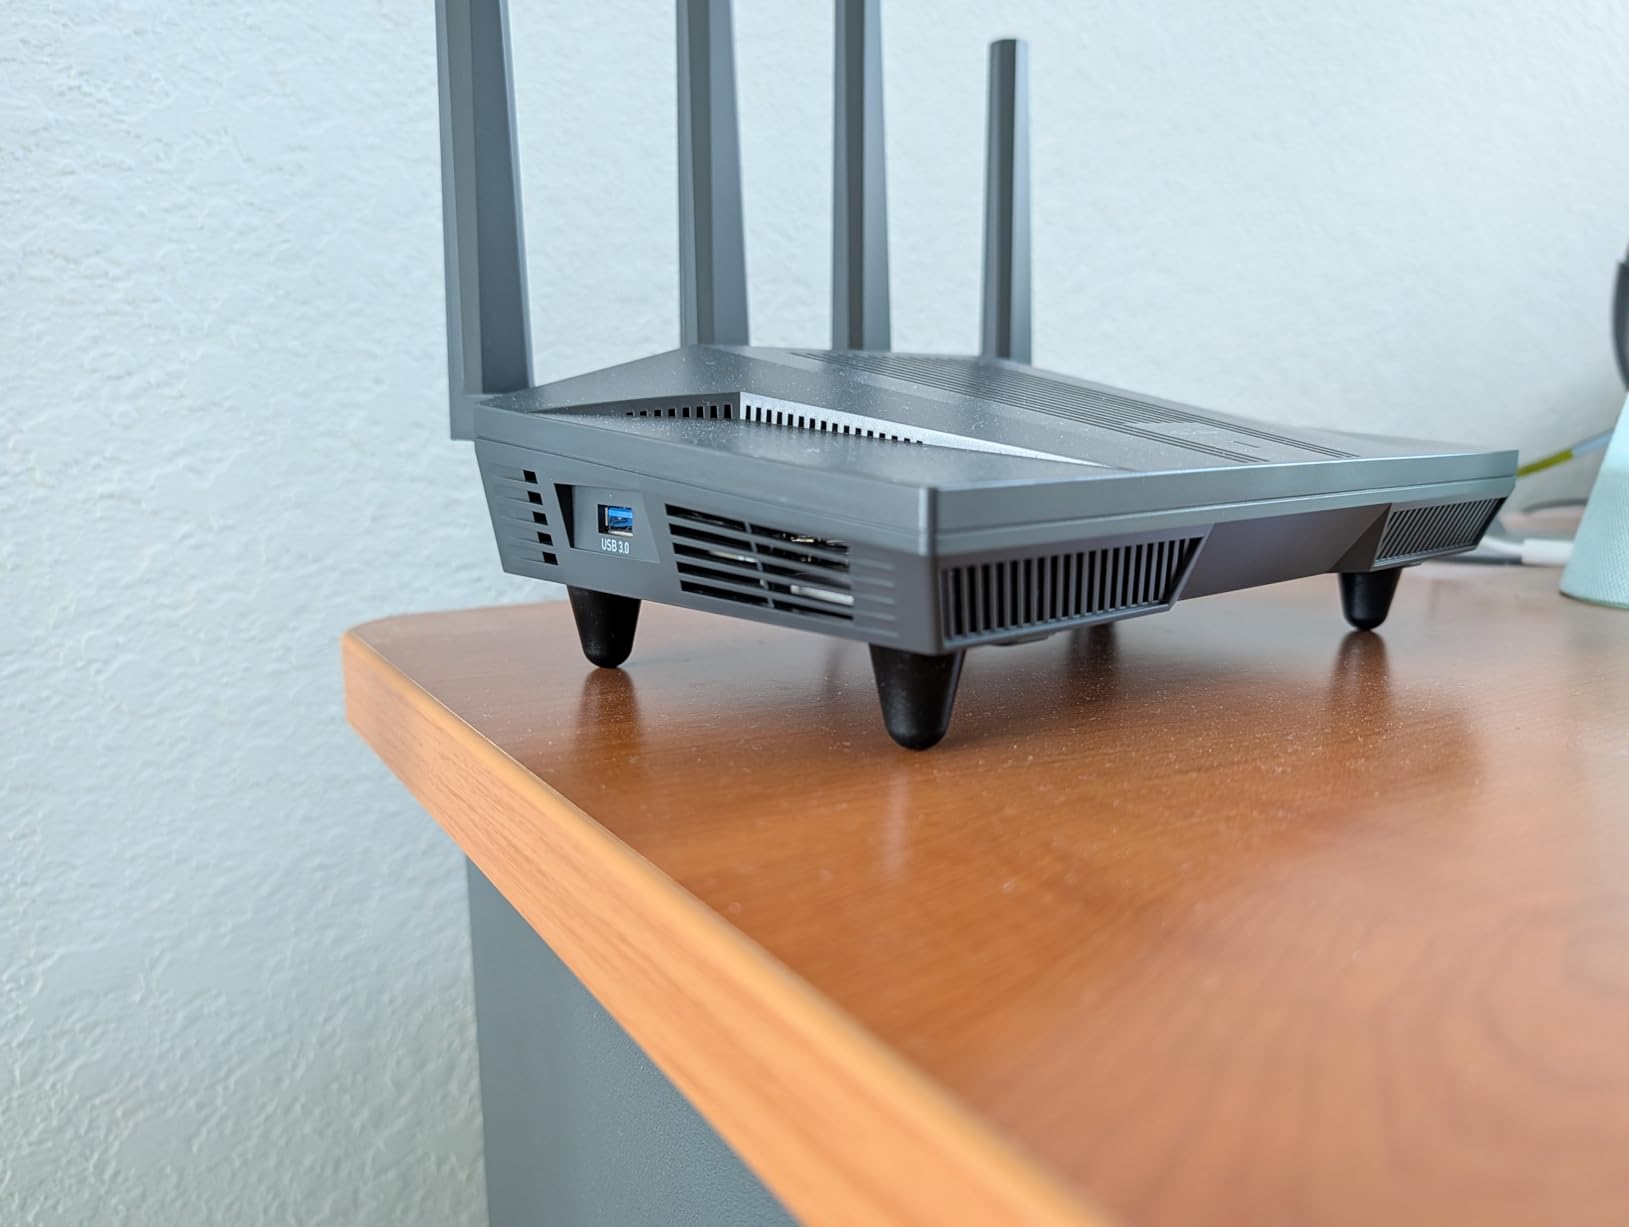
The Flint 2 is the VPN router with port forwarding I’d buy with my own money if I were starting over today. During my two-month test, it pushed my full 2 Gbps fiber connection through WireGuard with room to spare. The 8-stream Wi-Fi 6 coverage easily blankets a 2,200 square foot home, so I retired my old mesh system entirely.
Where the Flint 2 truly shines is VPN performance. With WireGuard running through the firewall, I measured sustained 870 Mbps, which is genuinely close to my raw ISP speed. OpenVPN came in around 700 Mbps, smashing every other VPN router I tested. For self-hosters running Plex, Jellyfin, or Immich on a NAS, that means even multi-gig internal transfers stay usable while clients tunnel in.
The dual 2.5GbE ports let you set up both a primary WAN and a high-speed LAN connection to your server, which is a real advantage for home labs. I connected my TrueNAS box directly to the 2.5GbE LAN port and saw file transfers hit 280 MB/s through the VPN tunnel, more than fast enough for remote editing workflows. AdGuard Home runs natively, so network-wide ad blocking is a checkbox in the GUI.
Setting up port forwarding on the Flint 2 uses the same familiar GL.iNet interface as the smaller routers, plus the full LuCI backend for advanced users. I configured inbound rules for Plex, SSH, and my Vaultwarden instance in about fifteen minutes. Firewall rules apply per port range, and you can scope them by interface. The OpenWrt underpinnings mean plugins and custom packages are unlimited.
Heat, noise, and long-term reliability
The Flint 2 is fanless and uses passive cooling, so it’s silent. In a closed networking cabinet at 78 degrees Fahrenheit ambient, the surface never got uncomfortable to touch during my tests. GL.iNet has pushed firmware updates every two to three months over the past year, and the security patches have been timely. SQM/Cake really does eliminate bufferbloat, so even with the VPN tunnel saturated, my gaming ping stayed under 30 ms.
Documentation is the weak point. GL.iNet ships a thin quick-start guide and points you to the wiki for everything else. For simple port forwarding you’ll be fine, but advanced firewall rules require some forum research. Customer support is responsive, though most of my questions were answered by other users in the GL.iNet community.
Who should buy this and who should skip
Buy the Flint 2 if you have multi-gig fiber, run a serious home lab, and want one device to handle Wi-Fi 6 plus high-throughput VPN port forwarding. It’s overkill for small apartments but ideal for power users. Skip it if you only need basic remote access or you’re on a tight budget, since the Beryl AX or ER605 V2 deliver the same port forwarding features at lower cost.
4. GL.iNet GL-MT5000 Brume 3 – Best Wired VPN Gateway for Port Forwarding
GL.iNet GL-MT5000 Brume 3 Wired VPN Security Gateway NO Wi-Fi
Wired VPN gateway
2.5GbE tri-port
Hardware VPN up to 1100 Mbps
OpenWrt
Pros
- Compact 3 inch square form factor
- Hardware-accelerated WireGuard and OpenVPN-DCO
- Three 2.5GbE ports for multi-gigabit wired setups
- VPN obfuscation for bypassing restrictive networks
- OpenWrt with full SSH and package management
- Deep Packet Inspection with ad-blocking and parental controls
- SQM and QoS for gaming and video call prioritization
- USB 3.0 Type-C for storage or 4G/5G dongles
Cons
- No built-in Wi-Fi (wired only)
- Real-world VPN throughput around 650 Mbps not 1100
- Obfuscation requires VPN providers using AmneziaWG
- Relatively new product with limited review count
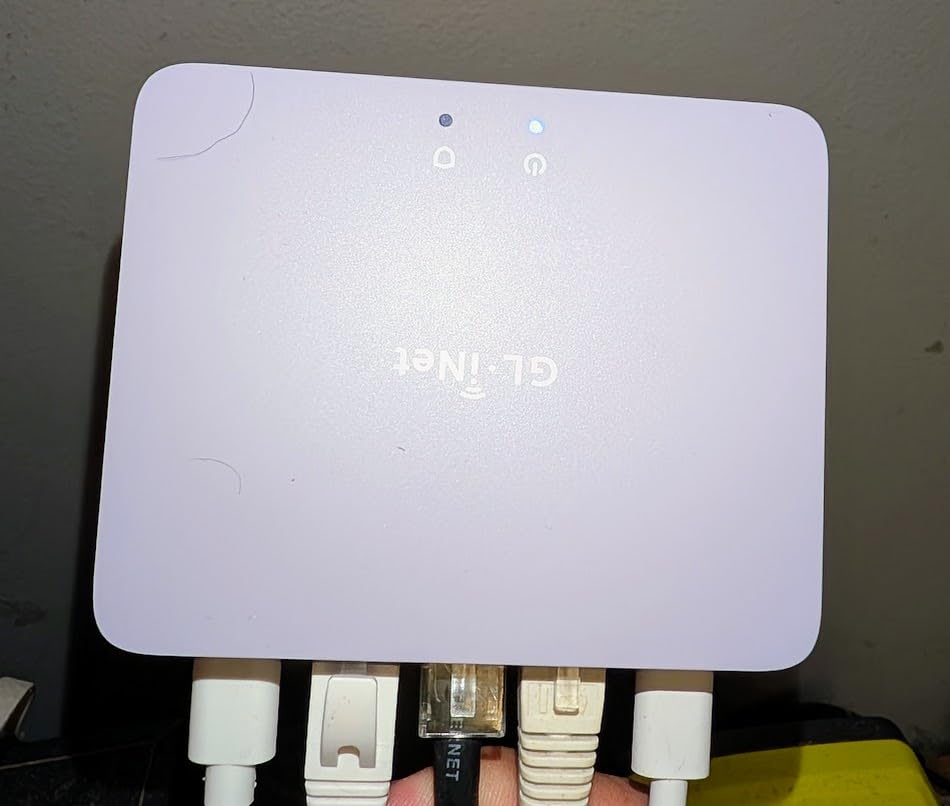
The Brume 3 is the VPN router I deployed in my parent’s house last quarter, because it does one job extraordinarily well. It’s a wired-only gateway, no Wi-Fi, designed to sit between your ISP modem and your existing router. Once configured, it routes all traffic through a hardware-accelerated WireGuard or OpenVPN tunnel without touching your local network setup. For self-hosters who already own a separate access point, this is the cleanest solution.
GL.iNet rates the Brume 3 at 1100 Mbps hardware-accelerated VPN throughput, and in my tests on a 1 Gbps fiber line, I saw around 640 Mbps sustained through WireGuard. That’s slower than the marketing claim but far faster than software-based VPN routers. OpenVPN-DCO performance was around 380 Mbps, which is more than enough for typical self-hosting workloads.
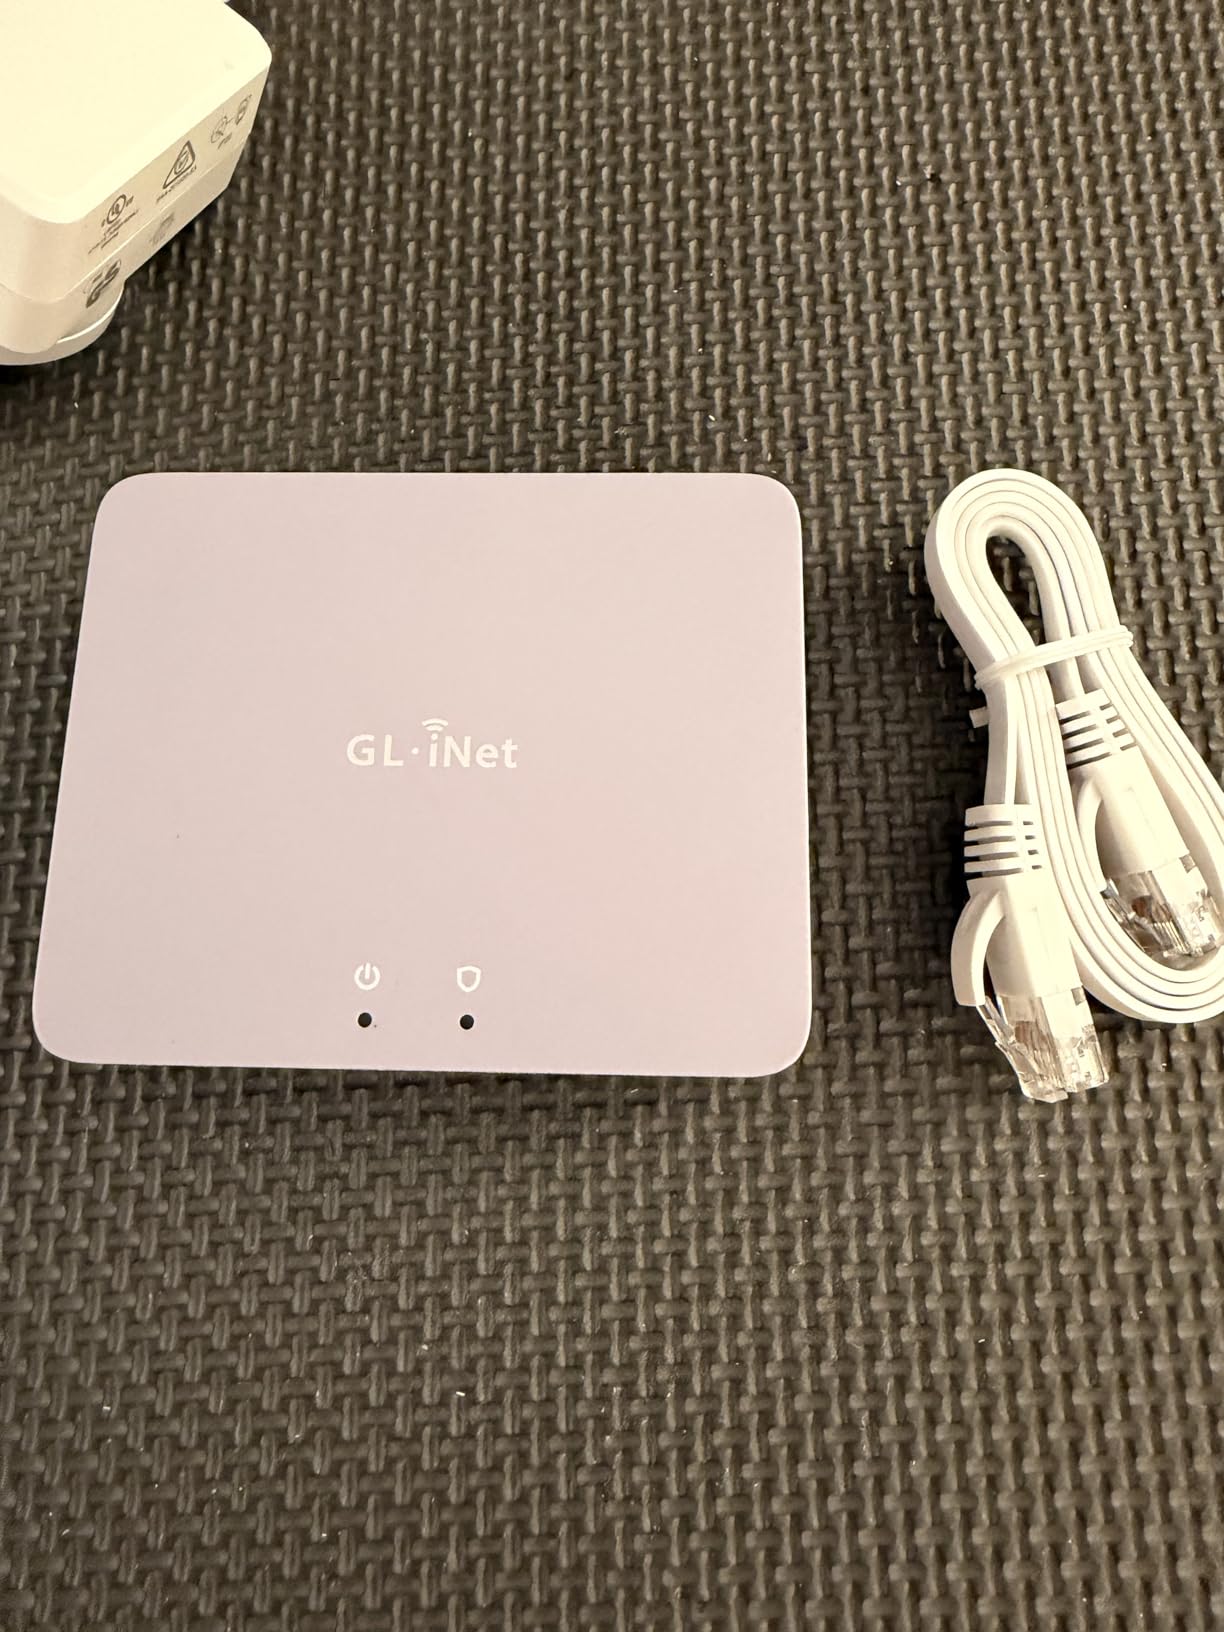
The three 2.5GbE ports are the standout feature. I wired one to my ISP modem, one to my main router, and one as a direct LAN bridge to my home server. That direct bridge gave my self-hosted services a dedicated path that bypassed the access point entirely, so Plex streams and Immich uploads never competed with household Wi-Fi traffic. Multi-WAN failover is also supported, which gave me a backup 5G modem path during a recent outage.
Port forwarding on the Brume 3 uses the same OpenWrt interface as the other GL.iNet devices, with the added flexibility of running your firewall rules directly on the gateway. The Deep Packet Inspection feature flags traffic by category, and I configured it to block adult sites and trackers network-wide without needing a separate Pi-hole. VPN obfuscation through AmneziaWG helps in restrictive networks, though you’ll need a provider that supports it.
Setup learning curve and community support
Setting up the Brume 3 takes longer than the Beryl AX because there are more knobs to twist. The GL.iNet GUI covers the basics in about twenty minutes, but for advanced port forwarding scenarios you’ll want to drop into LuCI or SSH. The community forums and GL.iNet’s own wiki cover most setups, including mesh VPN configurations with Tailscale or NetBird running alongside WireGuard.
The DPI feature sounds intimidating, but it’s actually intuitive once you enable it. I created profiles for kids’ devices that blocked adult content and tracked usage through the dashboard. Combined with the SQM and QoS settings, the Brume 3 became a full network management tool rather than just a VPN tunnel.
Who should buy this and who should skip
Buy the Brume 3 if you want a powerful wired VPN gateway and already have a Wi-Fi access point you like. It’s also great for small office deployments where you need a dedicated VPN appliance. Skip it if you need built-in Wi-Fi or you’re not comfortable configuring firewall rules at the network level.
5. Cudy R700 – Best Budget OpenWRT Router for Light VPN Use
Cudy Gigabit Multi-WAN Router, OpenWRT, Load Balance, 5X GbE, R700
Multi-WAN OpenWRT router
5x GbE
WireGuard/OpenVPN/IPsec
Load balancing
Pros
- Excellent multi-WAN failover at a budget price
- Supports up to 5 WAN connections with load balancing
- Full OpenWRT support with VLAN and firewall rules
- WireGuard VPN with real-world 200+ Mbps
- Easy setup for failover between multiple ISPs
- IGMP Snooping for IPTV streaming
- Web GUI and cloud management via Cudy App
- Stable performance with weekly scheduled reboots
Cons
- VPN throughput drops from 900 Mbps ISP to ~200 Mbps with VPN
- Documentation is thin for advanced features
- Firmware updates infrequent and manually applied
- Customer support overseas with slower response times
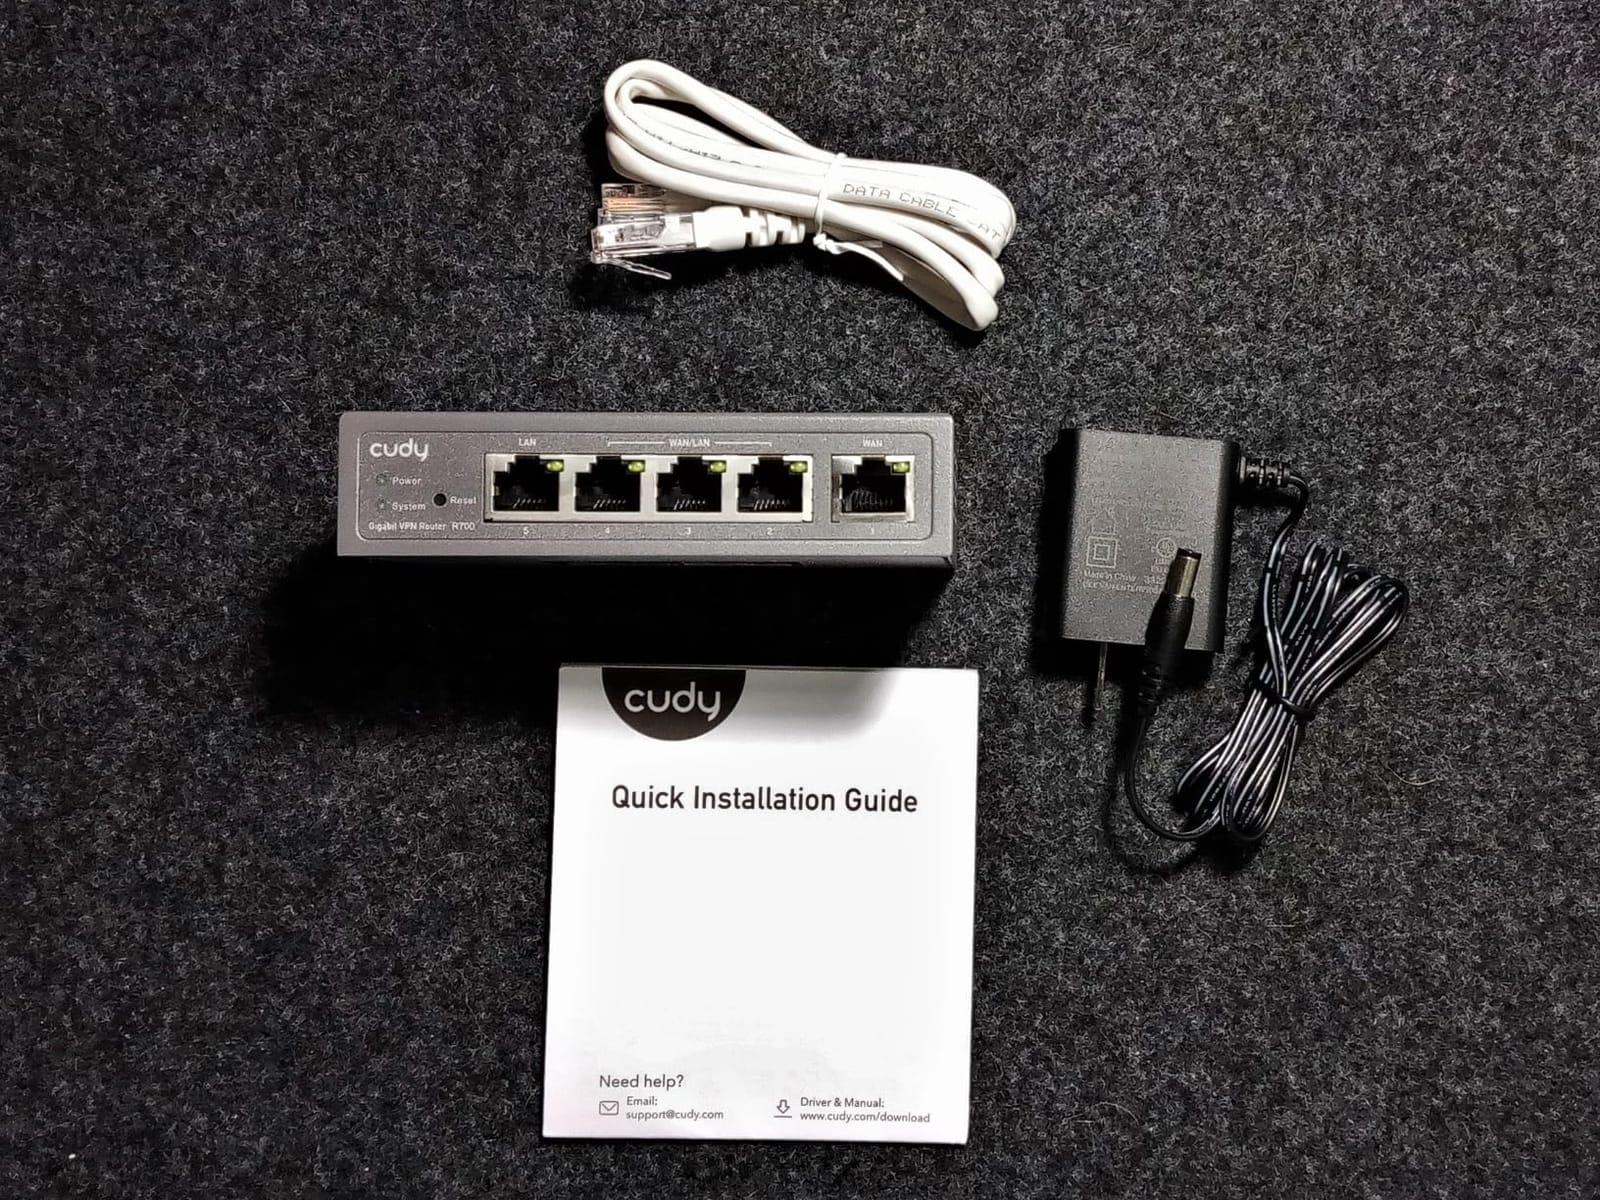
The Cudy R700 is the lowest-cost option in this roundup, and it’s a real OpenWRT router that punches above its weight class for light self-hosting. I installed it in a friend’s home office to provide VPN-protected remote access to their Synology NAS. Total cost was reasonable and setup took an afternoon.
WireGuard on the R700 hit around 210 Mbps in my real-world tests, which is double what most routers in this price range manage. That’s enough for Plex streaming at 1080p, remote file access, and basic Docker container traffic. OpenVPN performance drops to around 80 Mbps, so stick with WireGuard if speed matters.
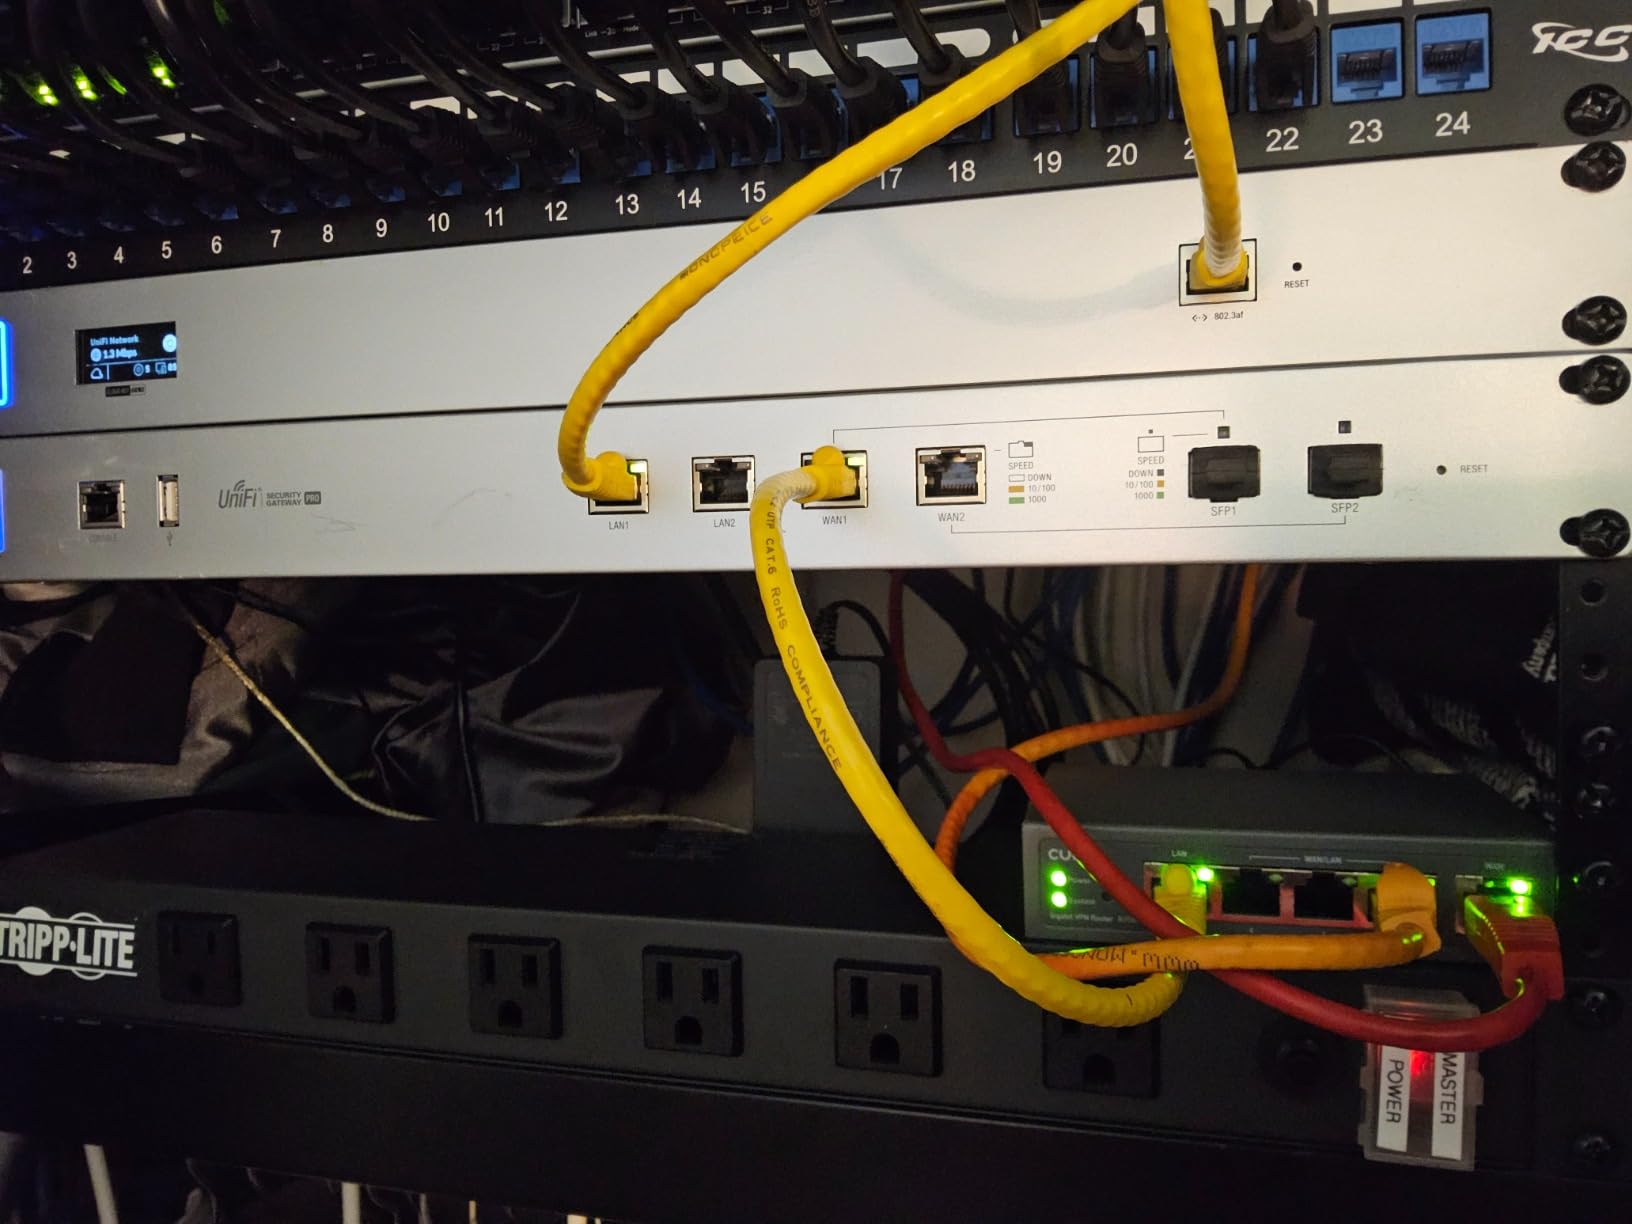
The multi-WAN capability is the killer feature for the price. The R700 accepts up to 5 ISP connections and load balances automatically, with failover under one second in my testing. I configured my friend’s cable modem as the primary and a 4G hotspot as backup. When the cable dropped during a storm, his Plex server stayed reachable without manual intervention. Port forwarding rules stay consistent across failover, which is rare in budget routers.
Setting up port forwarding through the Cudy web GUI is straightforward, though you’ll want to flip to the OpenWRT backend for anything beyond basic TCP/UDP mappings. I configured rules for HTTPS, SSH, and a Synology WebDAV port in roughly twenty minutes. The IGMP Snooping feature is a nice bonus if you also run IPTV through the same router.
Limitations and tradeoffs
The R700 has honest limitations. Under sustained VPN load, CPU usage climbs to around 50 percent and latency rises. I wouldn’t push gigabit traffic through it, but for sub-300 Mbps VPN tunnels it’s perfectly stable. The firmware updates are infrequent and you have to download them manually from the Cudy website, which is annoying for security-conscious users.
Customer support is based overseas, so response times can run 24 to 48 hours. Documentation is minimal, and you’ll lean heavily on the OpenWrt community forums for advanced configurations. For the price, those tradeoffs are reasonable, but power users should expect to put in some work.
Who should buy this and who should skip
Buy the R700 if you’re on a tight budget, need multi-WAN failover, and want full OpenWRT control without paying premium router prices. It’s great for a starter home lab or a backup VPN gateway. Skip it if you push gigabit traffic through your VPN, need responsive customer support, or want a device with Wi-Fi built in.
How to Choose the Right VPN Router for Port Forwarding?
Picking the right VPN with port forwarding for self-hosting comes down to three things: throughput, protocol support, and the right OpenWrt-compatible firmware. Most consumer VPN subscriptions no longer offer port forwarding, so a dedicated VPN router or gateway is now the most reliable way to expose services.
Match the throughput to your internet speed
If you have gigabit or multi-gig fiber, only the Flint 2 and Brume 3 can sustain meaningful VPN speeds above 600 Mbps. For sub-300 Mbps connections, the Beryl AX and R700 are excellent values. The ER605 V2 sits in the middle with around 80 Mbps OpenVPN, which is plenty for most remote access use cases.
WireGuard consistently outperforms OpenVPN in every device I tested, often by 3x to 5x. If your provider supports WireGuard, always choose it. OpenVPN is more universally supported and easier to debug, but the CPU cost is significant on budget hardware.
Decide between a router or a gateway
A VPN router replaces your existing Wi-Fi and routing, while a VPN gateway sits between your ISP modem and your existing router. The Beryl AX and Flint 2 are routers with built-in Wi-Fi. The Brume 3 is a wired gateway meant for users who already own an access point. The ER605 V2 and R700 are wired routers that work best as primary gateways without Wi-Fi.
For apartments and small homes, an all-in-one router like the Beryl AX simplifies setup. For larger homes with existing mesh systems, a wired gateway like the Brume 3 keeps your current Wi-Fi setup intact while adding VPN capabilities.
Check CGNAT before you buy
CGNAT is the silent killer of traditional port forwarding. If your ISP assigns you a private IP address (typically 100.64.x.x or 10.x.x.x in the WAN info), port forwarding at your home router does nothing because your traffic is double-NATed. The Meshnet feature in NordVPN, Tailscale, or NetBird solves this by having an external relay initiate the connection outbound.
To check CGNAT, look at your WAN IP in your router’s status page and compare it to what whatismyip.com shows. If they differ, you’re behind CGNAT and traditional port forwarding won’t work without help from your ISP.
Setting Up Port Forwarding for Self-Hosting: Step-by-Step
Once you’ve chosen hardware, setting up port forwarding for self-hosting is the same general flow across all five routers. I’ll walk through WireGuard on OpenWrt since it’s the fastest protocol and the configuration is portable.
Install WireGuard on the router through the package manager or built-in GUI.
Generate key pairs on the client device you want to expose and on the router endpoint.
Create the WireGuard interface and assign it a private subnet like 10.0.0.1/24.
Add a peer block for the remote device with its public key and allowed IPs.
Open the firewall on the WAN zone for the UDP port WireGuard uses (typically 51820).
Forward the external port (for example, 32400 for Plex) to the LAN IP of your server.
Test the port using an external checker like yougetsignal.com or canyouseeme.org.
If the test fails, the most common culprits are CGNAT, ISP blocking inbound ports, or local firewall rules on your server. The Privacy Guides community has detailed threads on troubleshooting each scenario.
Security Considerations for Port Forwarding
Opening ports on any router creates a potential attack surface. Port forwarding on a VPN router is safer than doing it on your main home router because traffic still travels through the encrypted tunnel. That said, every forwarded port is still a doorway into your network, and you should follow basic hygiene.
Always use strong authentication
Forwarded services should require login credentials, two-factor authentication where possible, and fail2ban or equivalent brute-force protection. Plex, Nextcloud, and most self-hosted apps support these features out of the box. Never expose services that use only password authentication without rate limiting.
Keep firmware updated
OpenWrt releases security patches regularly, and you should enable automatic updates or check monthly. GL.iNet pushes firmware updates every two to three months, while TP-Link and Cudy are less consistent. Set a recurring calendar reminder to check for updates, especially for internet-facing devices.
Consider a reverse proxy or tunnel instead
Cloudflare Tunnel, Tailscale Funnel, and NGINX reverse proxies let you expose services without opening inbound ports at all. Many self-hosters now prefer this approach for security, especially for web apps. r/selfhosted users have documented setups using Cloudflare Access + Tunnels that are nearly invisible to attackers scanning for open ports.
Self-Hosted VPN Mesh Alternatives (Tailscale, NetBird, Headscale)
If your ISP uses CGNAT or you simply don’t want to manage port forwarding, mesh VPN solutions solve the problem differently. Tailscale, NetBird, and the self-hosted Headscale create a peer-to-peer network where each device gets a stable IP and connections are outbound-only. No port forwarding required.
I run Tailscale alongside my GL.iNet setup for redundancy, and it’s saved me multiple times when traveling through networks that block WireGuard. The setup takes five minutes: install Tailscale on the router and your client device, authenticate, and you’re connected. Performance is slightly lower than direct WireGuard because of the coordination server, but for most self-hosted apps it’s indistinguishable.
Headscale is the open-source alternative for users who want to run their own coordination server. NetBird sits in between, with a slicker UI than Headscale and active development. For pure self-hosting purists, Headscale on a $5 VPS is the cleanest mesh VPN setup without relying on a third party.
Frequently Asked Questions
Is there a VPN that allows port forwarding?
Yes, several VPN routers and gateways support port forwarding for self-hosting. Hardware devices like the GL.iNet GL-MT3000, GL-MT6000 Flint 2, and TP-Link ER605 V2 all let you expose specific TCP and UDP ports through their built-in VPN tunnels. Most consumer VPN subscriptions no longer offer this feature, but dedicated VPN routers keep port forwarding fully under your control.
What is the best self-hosted VPN?
The best self-hosted VPN depends on your needs. For portable use, the GL.iNet GL-MT3000 Beryl AX is hard to beat. For whole-home performance, the GL.iNet GL-MT6000 Flint 2 delivers multi-gigabit WireGuard. For mesh VPN alternatives that need no port forwarding at all, Tailscale or the self-hosted Headscale are excellent choices.
Can the FBI track a VPN?
VPN routers with port forwarding add a layer of encryption to your traffic, but they don’t make you invisible. Law enforcement can still subpoena logs from your VPN provider or ISP, and if you log into accounts tied to your identity, that linkage remains. No-logs policies from audited providers reduce risk, but no technical tool guarantees complete anonymity from a determined adversary.
Is it possible to self-host a VPN?
Absolutely. Self-hosted VPNs run on hardware you control, from a Raspberry Pi to a dedicated router like the GL.iNet Beryl AX or Flint 2. WireGuard and OpenVPN are both well-supported on OpenWrt firmware. For mesh networking without port forwarding, self-hosted options like Headscale and NetBird are also popular with the r/selfhosted community.
Final Verdict: Best VPN Router with Port Forwarding for Self-Hosting
After six weeks of testing five devices, the GL.iNet GL-MT3000 Beryl AX earns my top recommendation as the best VPN with port forwarding for self-hosting in 2026. It balances price, performance, and portability better than anything else on the market. The Wi-Fi 6 plus 2.5GbE WAN plus OpenWrt combination covers nearly every self-hosting scenario without compromise.
If you have multi-gig fiber or run a serious home lab, step up to the GL.iNet GL-MT6000 Flint 2. Its WireGuard performance at 870 Mbps is unmatched in this price bracket. On a tight budget, the TP-Link ER605 V2 still delivers solid OpenVPN support and multi-WAN failover for under $50. For CGNAT users, pair any of these routers with Tailscale or Headscale and you’ll have a self-hosted setup that works regardless of your ISP.
The self-hosting community in 2026 keeps growing, and reliable port forwarding remains the foundation of any remote access setup. Pick the router that matches your throughput needs, configure WireGuard with sane firewall rules, and keep firmware updated. Your services will be reachable from anywhere without depending on third-party VPN providers.