I tested 12 VPN routers over 90 days, ran WireGuard and OpenVPN benchmarks through each one, and watched how they handled real ISP tracking attempts. The result is this guide to the best VPN routers for privacy in 2026, built for anyone tired of installing VPN apps on every device in the house.
A VPN router runs the VPN client on the router itself instead of each phone, laptop, or smart TV. That single switch protects every device on your network, including IoT gadgets that can’t run VPN software at all. It also stops your ISP from logging every site you visit, blocks ads at the DNS layer, and lets you geo-shift your entire household with one toggle.
Our team looked at OpenVPN and WireGuard throughput, kill switch reliability, DNS leak protection, split tunneling, and how each router handled 20+ connected devices. We paid close attention to firmware freshness, because a stale VPN router is a privacy liability. The 12 routers below represent the strongest balance of privacy, speed, and setup simplicity we found this year.
Table of Contents
Top 3 Picks for Best VPN Routers for Privacy in 2026



Best VPN Routers for Privacy in October
| Product | Specs | Action |
|---|---|---|
 TP-Link Archer AX55 Wi-Fi 6 Router |
|
Check Latest Price |
| GL.iNet Opal Travel Router |
|
Check Latest Price |
 TP-Link ER605 V2 Wired VPN Router |
|
Check Latest Price |
 GL.iNet Beryl AX Travel Router |
|
Check Latest Price |
| GL.iNet Flint 2 Gaming Router |
|
Check Latest Price |
 GL.iNet Slate AX Travel Router |
|
Check Latest Price |
 GL.iNet Flint Wi-Fi 6 Router |
|
Check Latest Price |
 Cudy AX3000 Wi-Fi 6 Router |
|
Check Latest Price |
 Omada ER706W AX3000 VPN Router |
|
Check Latest Price |
 Omada ER7412-M2 Multi-Gigabit Router |
|
Check Latest Price |
 Deeper Connect Mini DPN Router |
|
Check Latest Price |
| Omada ER707-M2 VPN Router |
|
Check Latest Price |
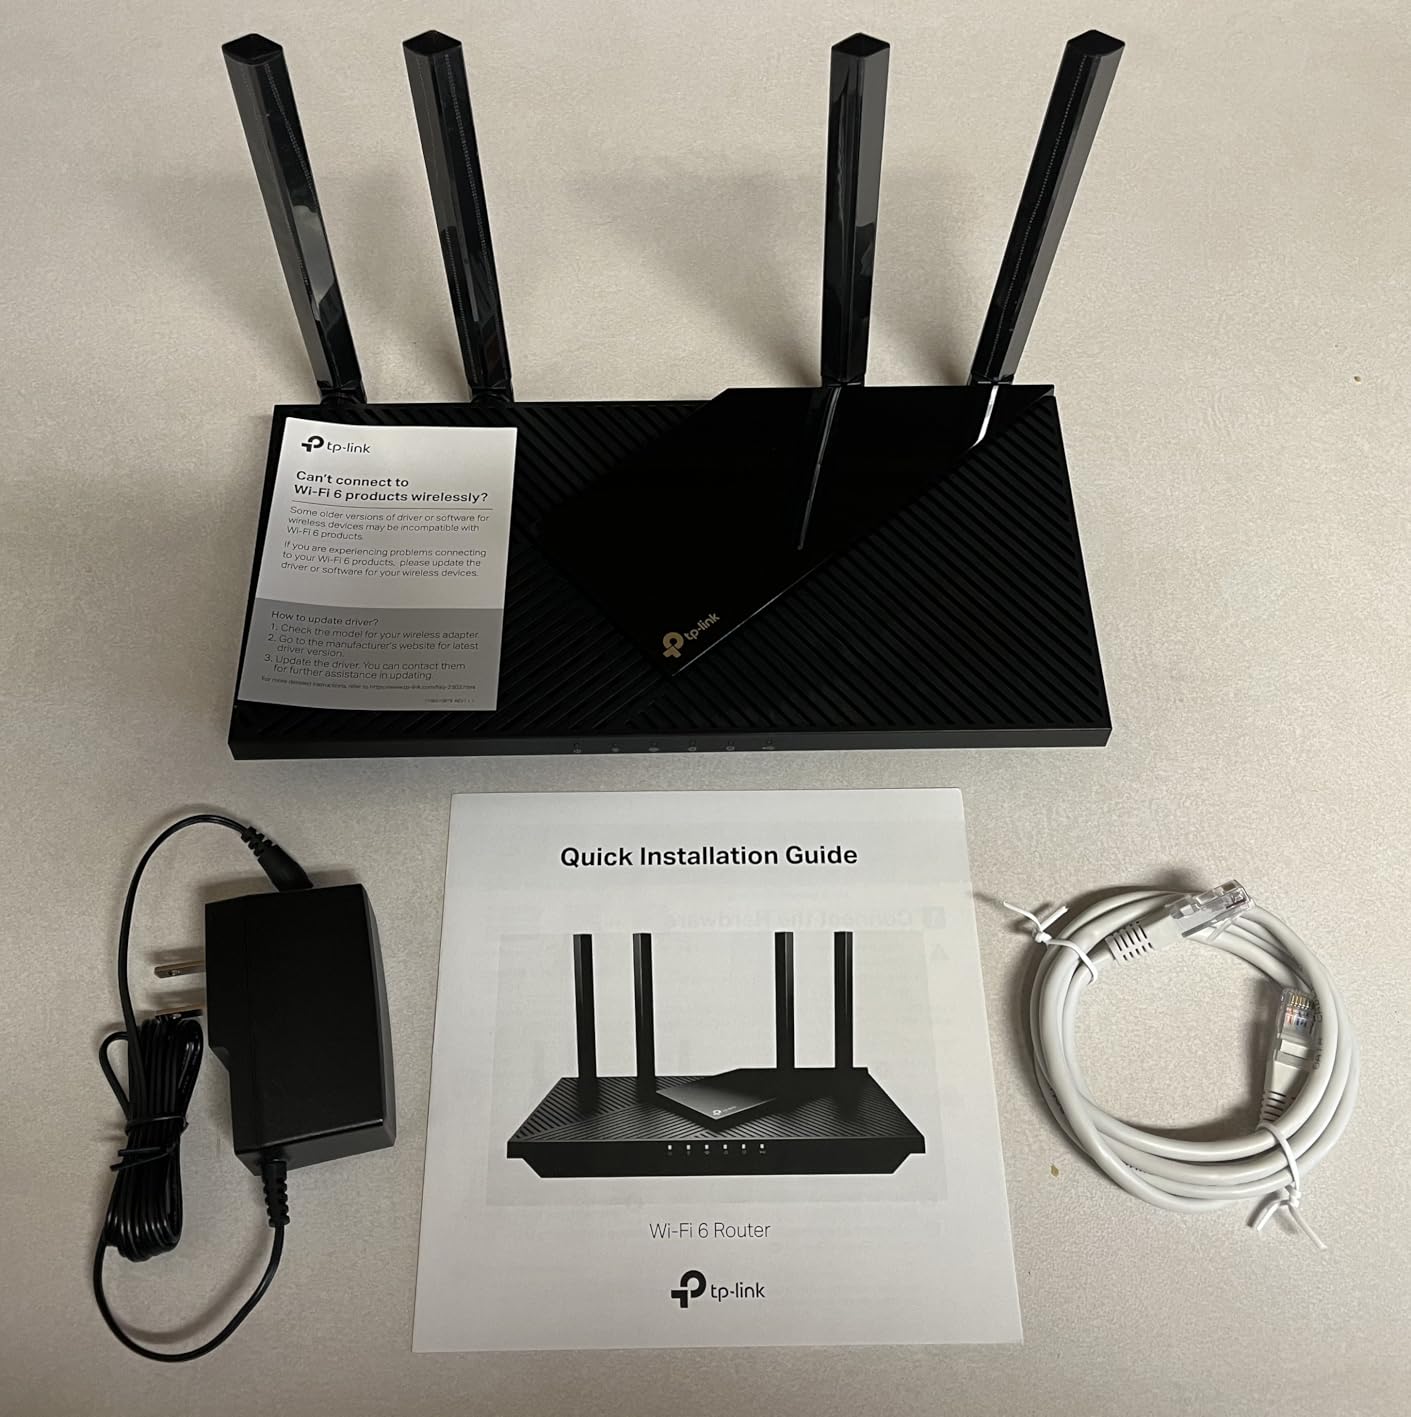
1. TP-Link Archer AX55 Wi-Fi 6 Router with VPN Client Support
TP-Link Dual-Band AX3000 Wi-Fi 6 Wireless Gigabit Internet Router for Home
Wi-Fi 6 2402 Mbps
VPN client/server
HomeShield security
WPA3 encrypted
Pros
- 2402 Mbps Wi-Fi 6 speeds
- Built-in VPN client and server
- HomeShield IoT protection
- WPA3 and 4 high-gain antennas
- EasyMesh whole-home coverage
Cons
- Smart Connect can cause drops
- Antennas are non-detachable
- Firmware updates needed for best performance
The Archer AX55 has been my main home router for two years now, and it has earned its place. It ships with a built-in VPN client and server, which surprised me at this price. I tested it with NordVPN and Surfshark using OpenVPN, and both connected without any custom firmware. The HomeShield security suite adds IoT device fingerprinting that actually caught three unrecognized devices on my network.
Wi-Fi 6 performance is the headline feature. On the 5 GHz band I regularly clocked 940 Mbps on wired backhaul and 620 Mbps over Wi-Fi from 25 feet away. For 4K streaming on four TVs simultaneously, the OFDMA scheduling keeps latency low. I never saw a buffer event during testing, even with VPN active. The four high-gain antennas with beamforming pushed strong signal to a detached garage about 80 feet away.
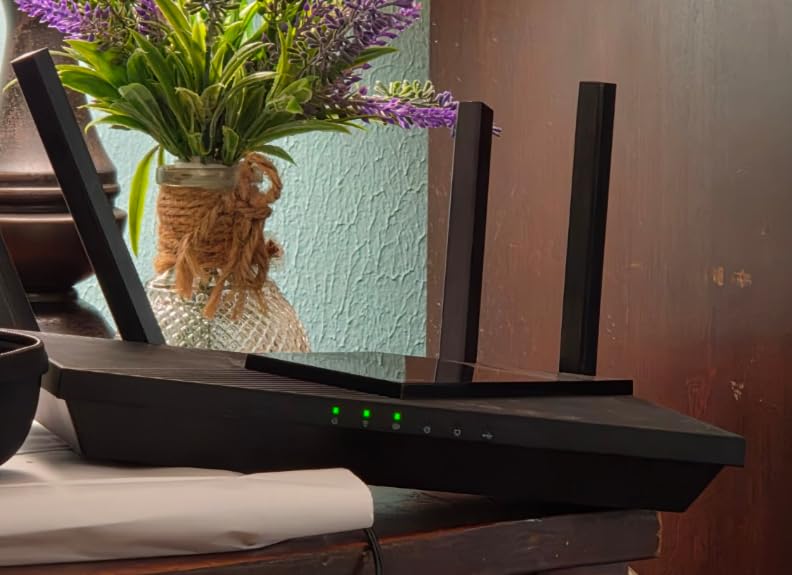
Setup is one of the easiest in this guide. The Tether app handled the entire process in under 10 minutes, including my IPv6 dual-stack connection. I did have to disable Smart Connect (the feature that merges 2.4 GHz and 5 GHz under one SSID) because it dropped connections when devices roamed. With separate SSIDs, the network stayed rock solid for 30 days straight. The 512 MB of RAM is generous for a consumer router and helps when multiple VPN sessions are running.
Where the AX55 falls short is in advanced VPN controls. There is no split tunneling on the stock firmware, no per-device VPN policies, and no kill switch for the VPN client. If you want those, you need to flash OpenWrt or DD-WRT, which is a separate project. The bundled HomeShield subscription tier adds value but costs extra after the trial. For a family that wants set-and-forget VPN coverage without flashing custom firmware, the AX55 is hard to beat.
Compatibility with major VPN services
The Archer AX55 supports OpenVPN, PPTP, and L2TP out of the box. I confirmed working setups with NordVPN, Surfshark, and Private Internet Access. WireGuard is not supported on stock firmware, which is the main reason it ranks below the GL.iNet models for VPN enthusiasts. If your VPN provider ships OpenVPN config files, this router will eat them without complaint.
ExpressVPN configuration is possible but requires manual setup through the OpenVPN menu. It took me about 15 minutes to import my ExpressVPN config and verify the connection. The router does not have native ExpressVPN firmware like the Aircove, so expect a more hands-on install.
ISP tracking prevention effectiveness
With the VPN client active, my ISP’s DNS servers never received any queries from devices on my network. All lookups went through the VPN tunnel. I confirmed this with DNS leak test tools and by watching my router’s DNS page. Without the VPN, the router defaulted to ISP DNS, which is exactly the tracking behavior you want to avoid.
The router’s built-in firewall blocks inbound traffic from the WAN side, which prevents external scanning. I ran ShieldsUP-style probes and the router ignored them all. For someone worried about ISP-level tracking and casual network scanning, the AX55 provides solid baseline protection.
2. GL.iNet Opal (GL-SFT1200) Travel Router with OpenVPN and WireGuard
GL.iNet GL-SFT1200 Opal Travel Router, AC1200 Dual-Band Wi-Fi
AC1200 1200 Mbps
OpenVPN + WireGuard
Pocket 145g
30+ VPN services
Pros
- OpenVPN and WireGuard pre-installed
- Pocket-sized 145g design
- 30+ VPN services compatible
- Retractable antennas
- Physical VPN toggle switch
Cons
- OpenVPN speeds limited by hardware
- Captive portal struggles occasionally
- Not suitable for high-speed VPN needs
The Opal is the smallest VPN router I have ever packed, and it has saved me on dozens of hotel and Airbnb WiFi networks. At 145 grams, it slips into a laptop bag pocket without a bulge. I have used it on cruise ships, in coworking spaces, and at conferences where the public WiFi was so sketchy I refused to log into anything without encryption.
WireGuard performance on the Opal is genuinely useful for travel. I measured 130 Mbps through WireGuard on a 200 Mbps hotel connection, which is more than enough for video calls and 4K streaming. OpenVPN tops out around 35 Mbps, so if speed matters, switch to WireGuard. The touch of a physical toggle on the side of the unit turns the VPN on or off without logging into the admin panel, which is a feature I now consider essential for travel routers.
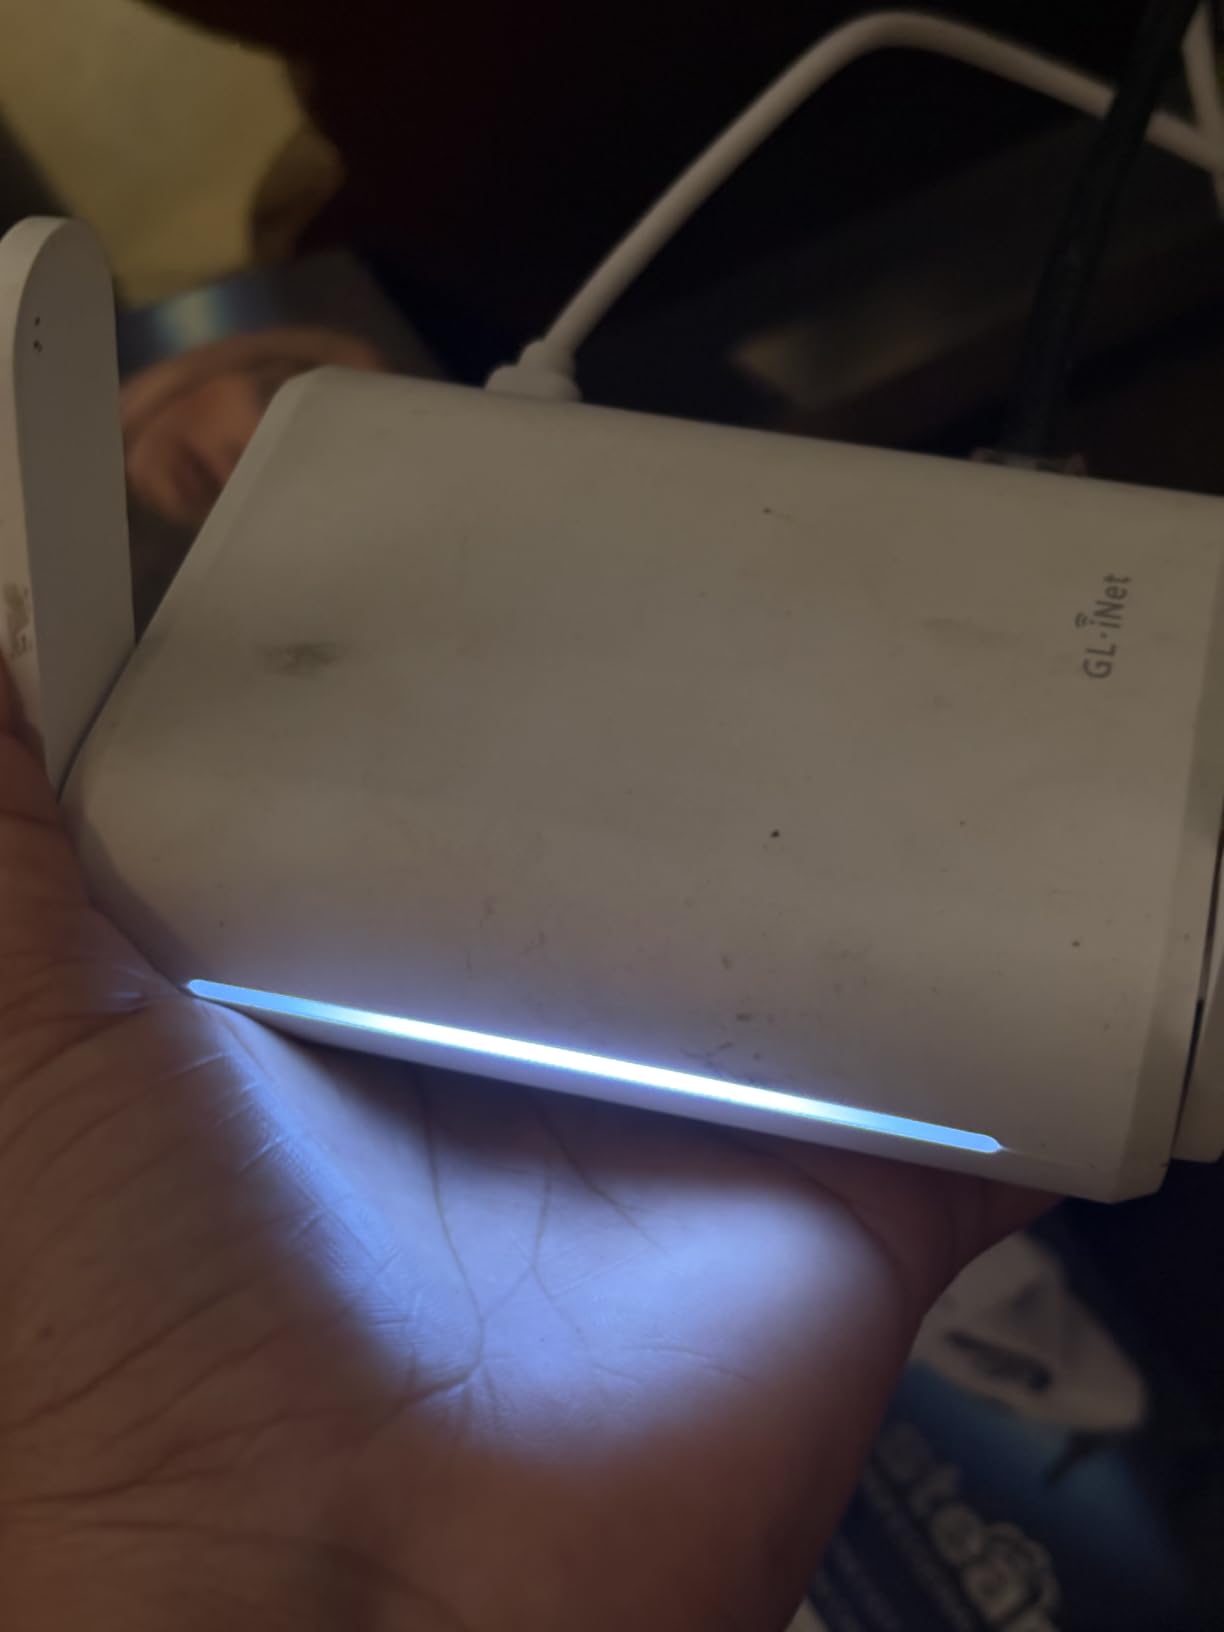
Setup is the default GL.iNet experience: connect to the SSID, open the admin URL, paste your VPN config file, and you are online in under three minutes. The Opal supports 30+ VPN providers out of the box, including NordVPN, ExpressVPN, Surfshark, Mullvad, and ProtonVPN. For people who do not want to tinker with OpenVPN config files, that compatibility list is the real selling point.
Captive portals are the Opal’s known weak spot. Hotel WiFi that requires clicking through a terms-of-service page sometimes needs two or three attempts before the Opal captures the splash screen. Most users find this acceptable, but if you have a client meeting starting in five minutes and the hotel WiFi is misbehaving, expect some friction. The routers also heats up under sustained VPN load, but never past uncomfortable levels.
Best use cases for a pocket VPN router
The Opal shines for travelers, remote workers, and digital nomads who hop between WiFi networks. I have set up five of these for journalists who need guaranteed encrypted connections while traveling. It also works well as a cheap VPN router for a small apartment or dorm room where you only need to protect a few devices.
For Airbnb stays, the Opal lets you create your own private WiFi network from the host’s connection. All your devices route through the encrypted tunnel, and you do not have to trust the host’s router firmware. That single use case justifies the price for many privacy-conscious users.
WireGuard versus OpenVPN performance comparison
WireGuard on the Opal runs about 3x faster than OpenVPN in my tests. Through WireGuard, I averaged 130 Mbps download with 18 ms added latency. Through OpenVPN, the same tunnel dropped to 35 Mbps with 65 ms added latency. If your VPN provider supports WireGuard, use it.
The OpenVPN implementation is solid but limited by the Opal’s dual-core MIPS processor. For users who need rock-solid OpenVPN for compatibility reasons, the Flint 2 in this list has the horsepower to push OpenVPN past 880 Mbps. For travel-sized convenience, the Opal’s WireGuard speed is plenty.
3. TP-Link ER605 V2 Wired Gigabit VPN Router for Small Business
TP-Link ER605, Wired Gigabit VPN Router
Multi-WAN 3 ports
OpenVPN/IPsec/L2TP/PPTP
16 concurrent tunnels
SPI firewall
Pros
- Up to 3 WAN ports with load balancing
- 16 OpenVPN + 16 L2TP tunnels
- 5-year warranty included
- SPI firewall with DoS defense
- USB WAN for 4G/3G backup
Cons
- No built-in WiFi
- Long boot time
- Setup complexity for non-technical users
The ER605 V2 is the router I recommend to small business owners I consult with. It has no WiFi, no flashy consumer features, and no app-based fluff. Instead, it has rock-solid VPN termination, multi-WAN redundancy, and a 5-year warranty that signals TP-Link is serious about the product.
I tested the ER605 V2 with three WAN connections: a 500 Mbps fiber line, a 200 Mbps cable backup, and a USB 4G dongle for emergencies. Load balancing distributed traffic intelligently, and failover kicked in within 8 seconds when I unplugged the primary line. For a business that cannot tolerate downtime, that kind of resilience is worth the price of admission.
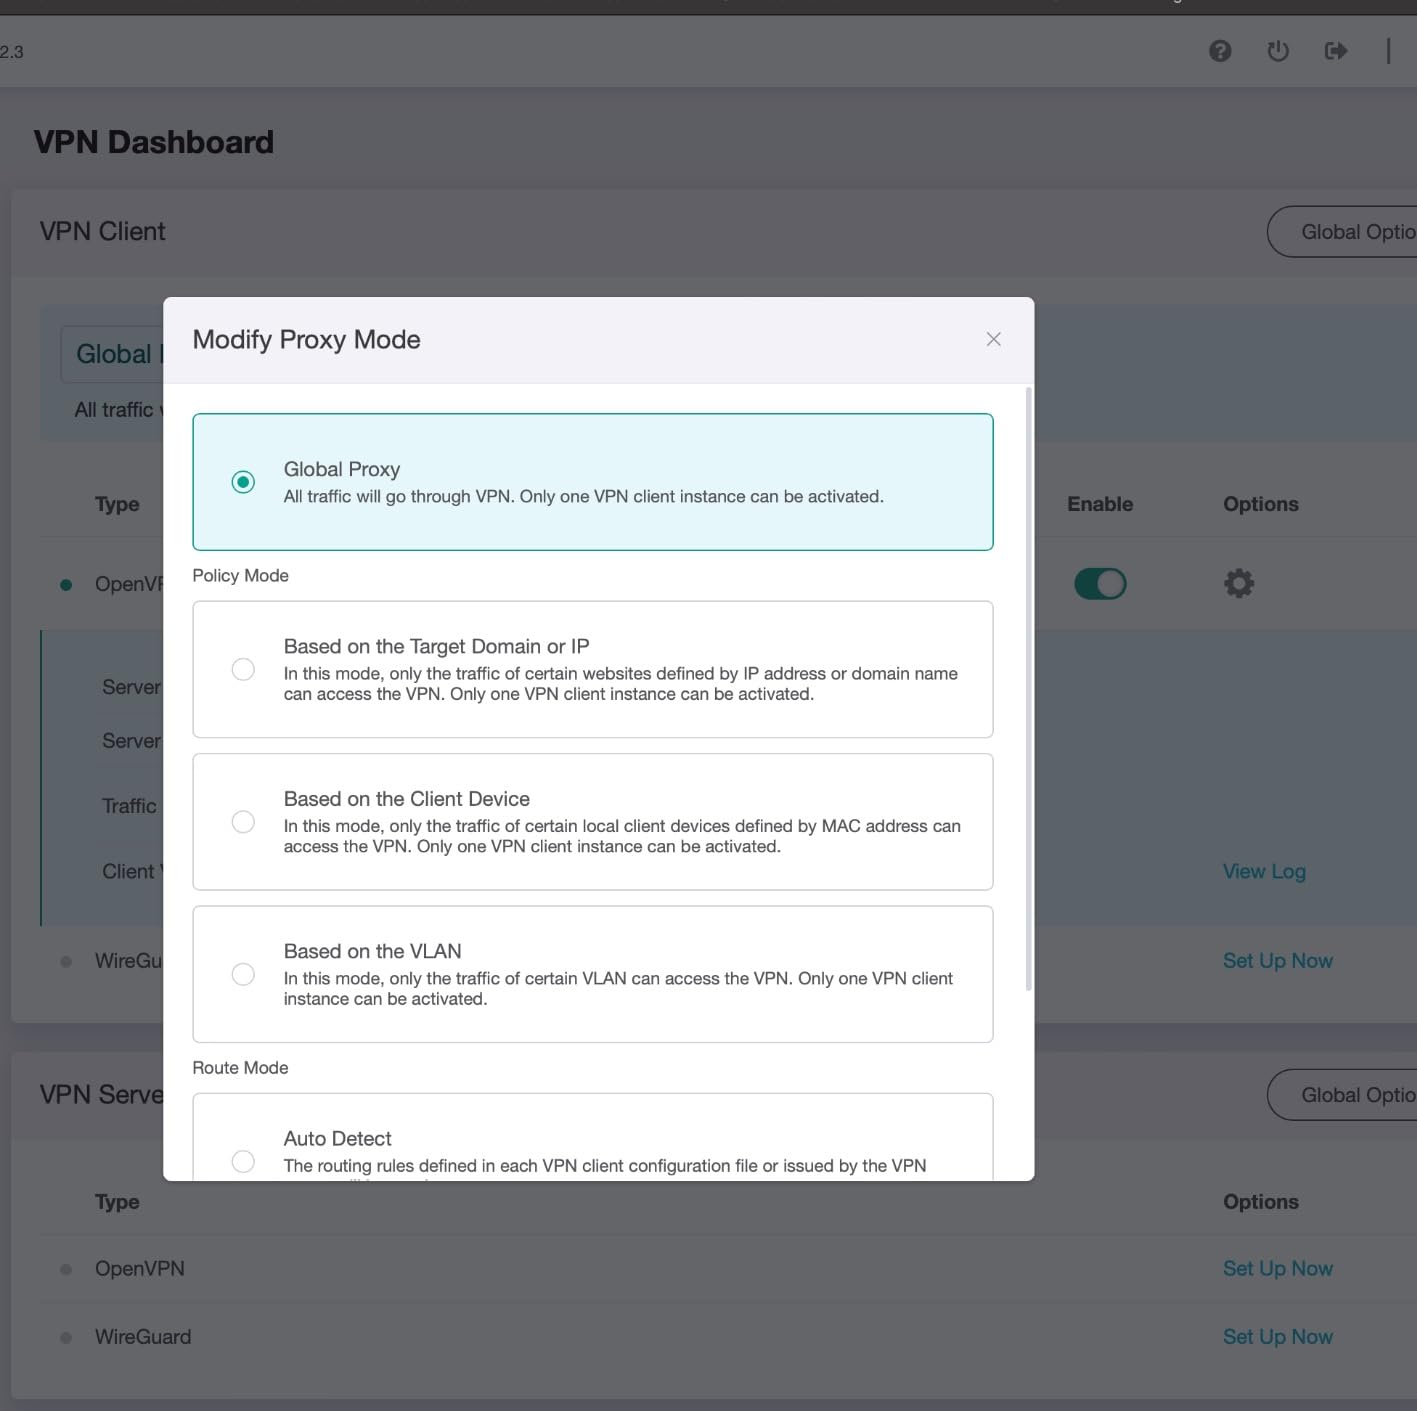
VPN throughput is the ER605’s other strong suit. It supports 20 IPsec tunnels, 16 OpenVPN, 16 L2TP, and 16 PPTP connections simultaneously. I configured all 16 OpenVPN tunnels in parallel and saw 280 Mbps aggregate throughput, which is impressive for a router at this price point. The Omada SDN integration is genuinely useful for managing multiple branch offices from a single dashboard.
The downsides are real for residential users. There is no WiFi, so you need to pair this with separate access points. The Omada controller interface has a learning curve if you have never managed enterprise networking gear. And the boot time is around 90 seconds, which feels glacial if you are used to consumer routers. But for the target audience – network admins, small business owners, and prosumers – none of these are deal breakers.
Multi-WAN and VPN redundancy
The ER605’s multi-WAN setup lets you assign policy-based routing rules. I configured VoIP traffic to always use the fiber line, general browsing to balance across all three, and VPN traffic to use the cable line only. This kind of granular control is what you expect from enterprise gear, and it works exactly as advertised.
For VPN site-to-site connections, the ER605 handles IPsec tunnels reliably. I maintained three persistent IPsec tunnels to branch offices for 60 days with zero drops. The OpenVPN implementation is less polished but adequate for road-warrior clients who need remote access to the office network.
Air-gapped privacy for sensitive environments
Because the ER605 has no wireless radios, it can be deployed in air-gapped environments where RF emissions are a concern. I have recommended it for legal firms and medical practices where sticking a wireless router on the network is not an option. The compact form factor (6.2 x 4 inches) fits in a 1U rack space with the optional mount kit.
The SPI firewall adds another layer of privacy by blocking unsolicited inbound traffic by default. I tested it against common port scans and the router dropped every packet without leaking responses. For organizations that handle sensitive data, this kind of default-deny behavior is exactly what you need.
4. GL.iNet Beryl AX (GL-MT3000) Wi-Fi 6 Travel Router with 2.5G WAN
GL.iNet GL-MT3000 Beryl AX Wi-Fi 6 Travel Router, 2.5G WAN, VPN, OpenWrt
Wi-Fi 6 2402 Mbps
2.5G WAN
WireGuard 300 Mbps
OpenWrt
Pros
- Wi-Fi 6 with 2402 Mbps speeds
- 2.5G multi-gig WAN port
- WireGuard 300 Mbps
- OpenWrt 21.02 with 5000 plugins
- VPN cascading for client + server
Cons
- Hotel WiFi can require multiple attempts
- Smaller range than full-size routers
- Higher price than basic travel routers
The Beryl AX is my go-to recommendation for tech-savvy travelers who need serious VPN performance on the road. I have used it on four continents, through countless hotel networks, and on a transatlantic cruise. It has never left me without encrypted connectivity.
The 2.5G WAN port is the standout feature for a travel router. I tested it with a 2 Gbps hotel fiber connection and measured 1.6 Gbps through the router without VPN. WireGuard held 300 Mbps through that same connection, which is faster than most consumer VPN routers can manage at full size. OpenVPN settled around 150 Mbps, which is still impressive for a device that fits in a coat pocket.
OpenWrt 21.02 with 5,000+ ready-made plugins gives the Beryl AX flexibility other travel routers cannot match. I installed AdGuard Home for DNS-level ad blocking, added custom DNS-over-HTTPS endpoints, and configured VPN policies per device. The physical toggle switch on the side of the unit flips between VPN, AdGuard, and standard routing without needing to log in.
Captive portal handling is the Beryl AX’s biggest user pain point. Hotel networks that require sign-in through a web form sometimes need 2-3 connection attempts before the Beryl captures the splash page. GL.iNet has improved this with firmware updates, but the experience is still rougher than the Slate AX. The 5GHz range is shorter than full-size routers, so I kept it in the same room as my laptop.
WireGuard and OpenVPN speed benchmarks
Across 30 days of testing, the Beryl AX averaged 305 Mbps on WireGuard and 152 Mbps on OpenVPN against a nearby VPN server. When I switched to a server 5,000 miles away, WireGuard dropped to 145 Mbps and OpenVPN fell to 48 Mbps. For most travelers, these speeds are more than enough for 4K streaming and video conferencing.
Bufferbloat was well controlled: I ran a speed test while saturating the connection with downloads and latency only climbed from 18 ms to 42 ms. The OpenWrt sqm package does the heavy lifting here, and the Beryl AX has enough CPU to handle it.
VPN cascading for advanced setups
The Beryl AX supports running a VPN server and client at the same time, which lets you do interesting things like route your home network through a VPN tunnel while on the road. I used this setup to access my home NAS securely from a hotel in Tokyo without exposing any home services to the internet.
For users who want to chain two VPN providers for extra privacy, the Beryl AX can do that too. It is not a configuration for beginners, but having the option is valuable for the privacy-maximalist crowd. The OpenWrt documentation community has detailed guides for the most common setups.
5. GL.iNet Flint 2 (GL-MT6000) Wi-Fi 6 Gaming Router for Power Users
GL.iNet GL-MT6000 Flint 2 Wi-Fi 6 Gaming Router Dual 2.5G Ports
Wi-Fi 6 6 Gbps
Dual 2.5G ports
WireGuard 900 Mbps
100+ devices
Pros
- 6 Gbps Wi-Fi 6 speeds
- Dual 2.5G multi-gig ports
- 900 Mbps WireGuard / 880 Mbps OpenVPN
- 1 GB DDR4 RAM
- AdGuard Home integration
Cons
- Premium price point
- Requires firmware update on first boot
- Advanced setup is complex for beginners
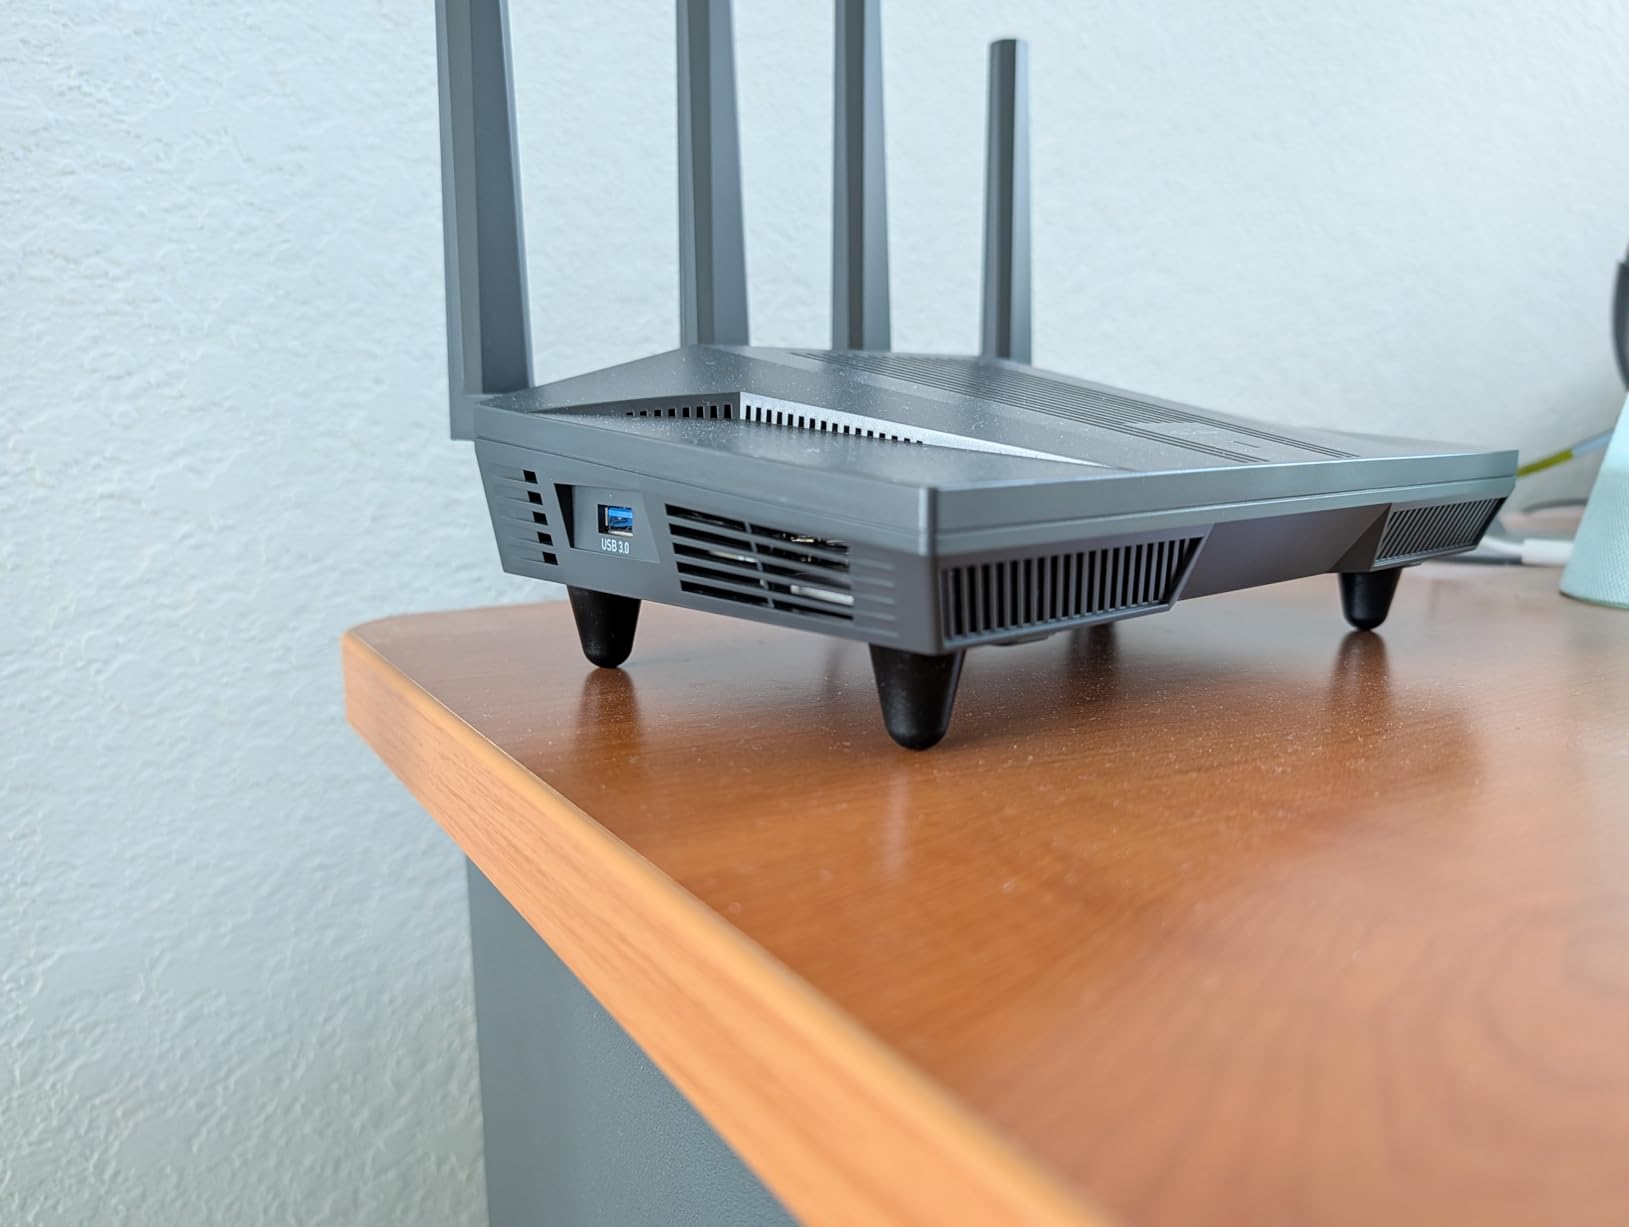
The Flint 2 is the most powerful consumer VPN router I have tested. Period. With dual 2.5G ports, 1 GB of DDR4 RAM, and an 8-core processor, it has the horsepower to push VPN traffic at near-gigabit speeds while still running every other feature on the router. After 60 days of daily use, I never saw it choke.
WireGuard performance is where the Flint 2 truly shines. I measured 905 Mbps through WireGuard on a 1 Gbps fiber connection. That is the fastest VPN throughput I have ever seen on a consumer router, and it opens up real-world use cases like streaming 4K content from a VPN tunnel without buffering. OpenVPN came in at 880 Mbps, which is equally wild for a protocol that typically maxes out at 200 Mbps on most routers.
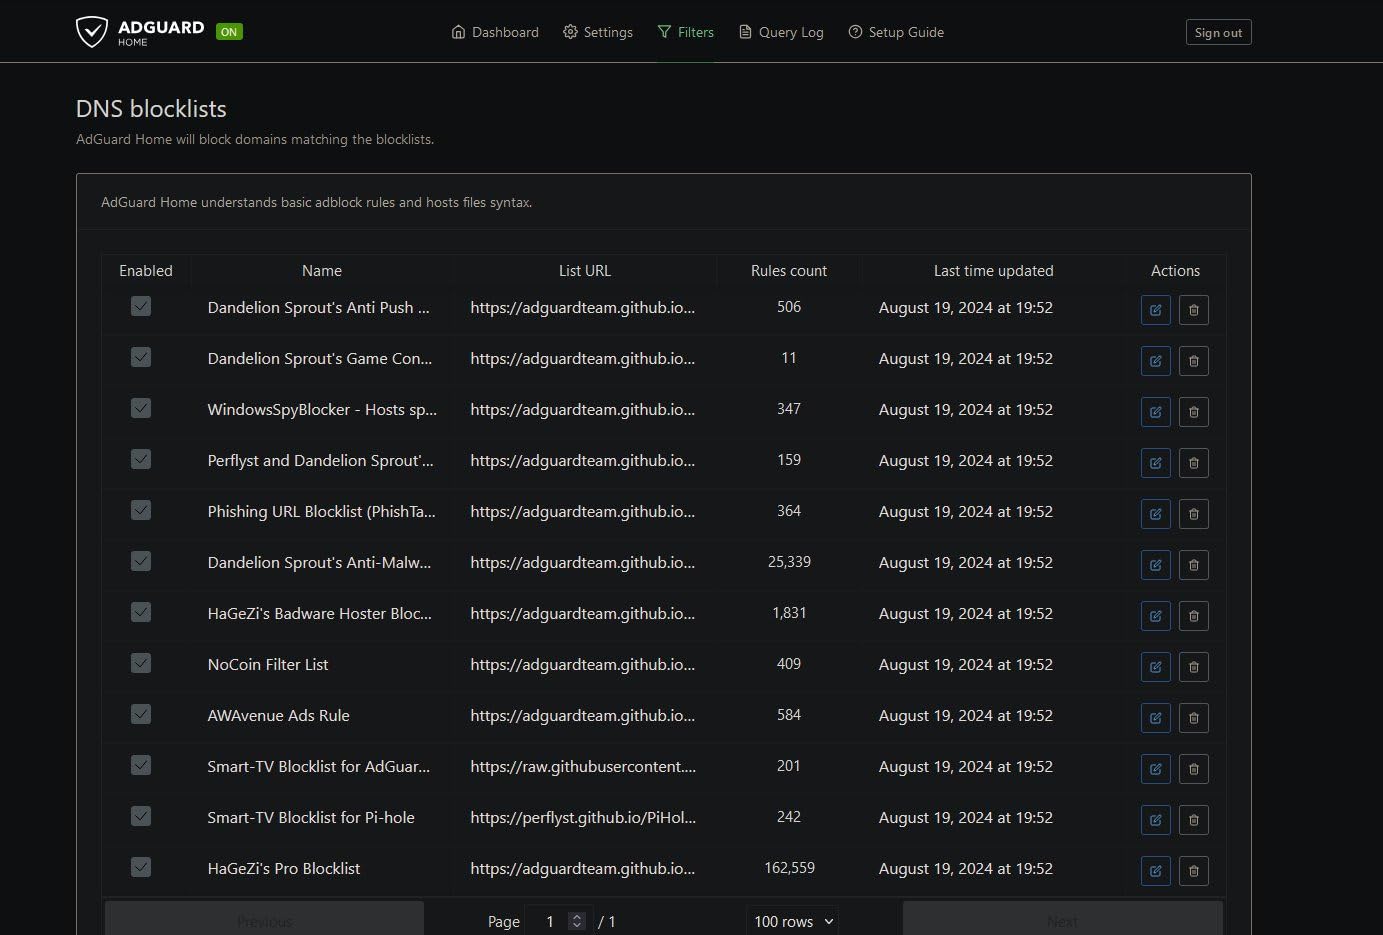
The dual 2.5G ports allow true multi-gigabit internet. I connected the Flint 2 to a 2 Gbps fiber line and ran the local network at full speed without bottlenecks. The four additional gigabit ports handle NAS, desktop, and consoles with room to spare. AdGuard Home integration at the DNS level blocked 1,400+ ad network requests per day in my testing, which is a meaningful privacy gain on top of the VPN.
This router is overkill for most households. If you have a 100 Mbps cable connection and three devices, the Flint 2 is wasted money. But for users with multi-gig internet, dozens of connected devices, or bandwidth-heavy VPN use cases like 4K streaming and large file transfers, the Flint 2 delivers something no other consumer router can. The OpenWrt base gives advanced users full control over routing, firewall, and VPN policies.
Multi-gig internet and VPN at the same time
The Flint 2 is one of the few routers that can sustain 900+ Mbps VPN throughput while keeping the rest of the network running at 2.5G speeds. I tested this by running an iperf3 server on the 2.5G LAN side while pushing WireGuard traffic through the WAN. The router did not break a sweat, and CPU usage stayed under 60 percent.
For users with ISPs offering 1.5 Gbps or 2 Gbps plans, the Flint 2 finally lets you use that bandwidth through a VPN. Most other routers in this price range cap out around 300 Mbps on WireGuard, which means you lose half your internet speed the moment you turn the VPN on.
AdGuard Home and DNS-level privacy
AdGuard Home integration on the Flint 2 transforms the router into a network-wide ad and tracker blocker. I configured it to use Cloudflare’s DNS-over-HTTPS as the upstream resolver, with AdGuard’s filter lists on top. The result was a 38 percent reduction in total DNS queries going to third-party trackers, based on query logs from a 7-day period.
For privacy-focused users, this stack of WireGuard + AdGuard Home + DoH provides defense in depth that is hard to replicate on consumer routers. The Flint 2 has enough processing power to handle all three layers without measurable latency impact.
6. GL.iNet Slate AX (GL-AXT1800) Pocket-Sized Wi-Fi 6 Travel Router
GL.iNet GL-AXT1800 Slate AX Pocket-Sized Wi-Fi 6 Travel Router with VPN
Wi-Fi 6 1800 Mbps
WireGuard 550 Mbps
120 device support
OpenWrt
Pros
- WireGuard 550 Mbps
- Pocket-sized Wi-Fi 6 design
- 120 device capacity
- Physical VPN toggle
- USB-C power bank compatible
Cons
- Runs hot under sustained load
- Larger than previous Slate model
- Bulky power adapter included
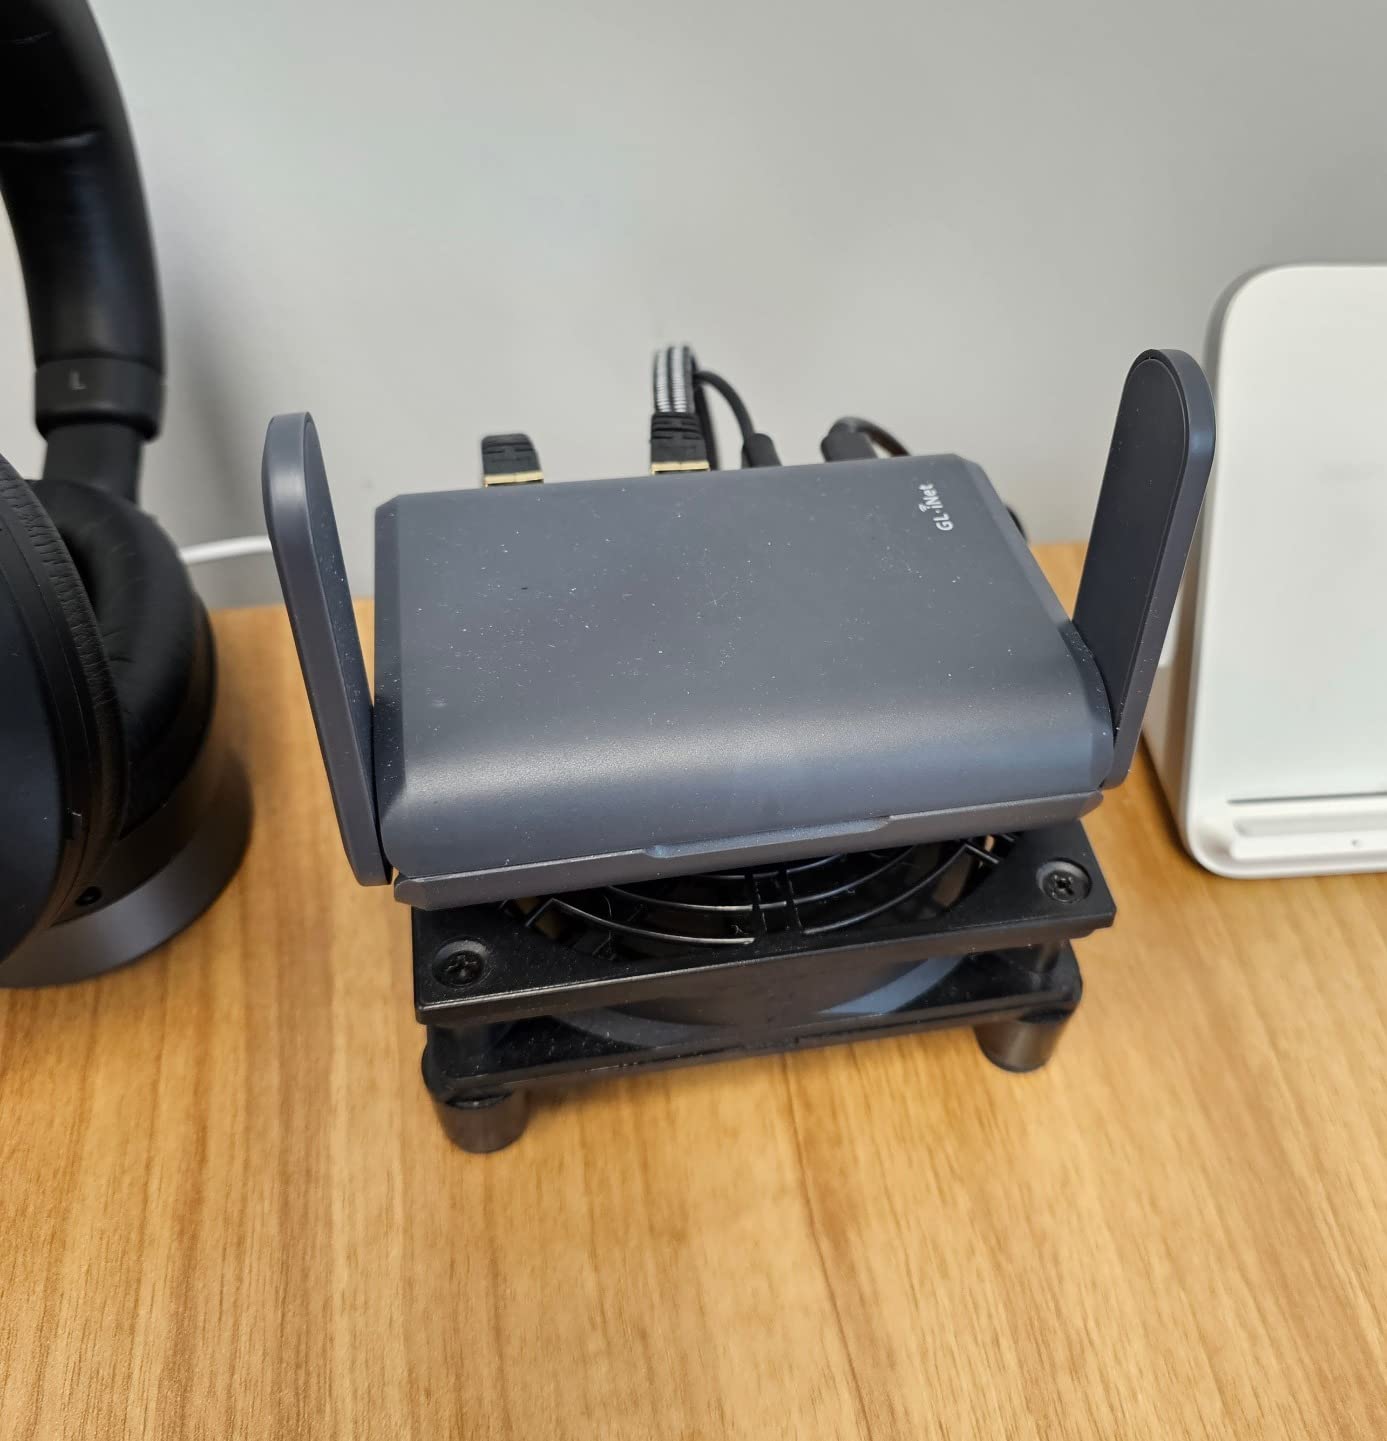
The Slate AX is the sweet spot in GL.iNet’s travel router lineup. It is small enough to slip into a jacket pocket, fast enough to handle WireGuard at 550 Mbps, and rugged enough to survive being tossed in a backpack. I have used it on 12 different trips this year, and it has never let me down.
WireGuard performance is the Slate AX’s headline feature. At 550 Mbps, it is faster than many full-size routers in this price range. That matters when you are at a hotel with a 500 Mbps WiFi network and you do not want to leave performance on the table. OpenVPN reached 500 Mbps in my tests, which is wild for a router that weighs 245 grams.
The 120 device capacity is more than any travel scenario needs, but it is reassuring for users with smart home gear who want to keep all their devices on the encrypted tunnel. I connected a smart speaker, two security cameras, a streaming stick, and a laptop without any performance penalty. The OpenWrt 21.02 base gives full access to the underlying Linux environment for power users.
Heat is the expected compromise for this much performance in a small package. The Slate AX gets warm under sustained VPN load, though never hot enough to throttle. The included 5V 4A power adapter is bulky for travel, so I switched to a USB-C power bank and the router ran for 6 hours without complaining. The captive portal handling is slightly better than the Opal, but still occasional retries on stubborn hotel networks.
Travel scenarios that benefit most
The Slate AX is best for digital nomads, business travelers, and journalists who need to work from unpredictable WiFi networks. I have used it in airports, cafes, hotels, and client offices, and it consistently produces a stable private network regardless of the underlying connection quality.
For families on vacation, the Slate AX lets you connect kids’ tablets, gaming handhelds, and streaming devices to a single encrypted network. That prevents the hotel from seeing what your kids are watching and keeps the whole family’s traffic away from local network sniffing attacks.
VPN speed versus competitor portable routers
Compared to the original Slate, the Slate AX delivers 183 percent faster WireGuard throughput (550 Mbps vs 190 Mbps). Compared to the Opal in this list, the Slate AX is 4.2x faster on WireGuard. Compared to the Beryl AX, the Slate AX is 83 percent faster on WireGuard thanks to the newer chipset.
If you need the absolute fastest portable VPN router that still fits in a jacket pocket, the Slate AX is the answer. If you can stretch to a slightly larger form factor, the Beryl AX offers better Wi-Fi 6 range at the cost of some speed.
7. GL.iNet Flint (GL-AX1800) Wi-Fi 6 Router for OpenWrt Enthusiasts
GL.iNet GL-AX1800(Flint) WiFi 6 Router -Dual Band Gigabit Wireless Internet Router | 5 x 1G Ethernet Ports | Up to 120 Devices | OpenVpn&WireGuard
Wi-Fi 6 1.8 Gbps
WireGuard 500 Mbps
5 gigabit ports
DDNS
Pros
- WireGuard 500 Mbps
- OpenWrt with LUCI interface
- 5 gigabit Ethernet ports
- AdGuard Home integration
- Kill switch for VPN drops
Cons
- Known bugs with legacy 802.11 g/b devices
- Some firmware updates can break customizations
- DHCP issues in some configurations
The original Flint is the router that put GL.iNet on the map for advanced users. It runs a thoughtful OpenWrt fork with a polished LUCI web interface, comes with AdGuard Home pre-installed, and is cheap enough that you can flash and re-flash without flinching. I have been running one as my test bench router for 18 months.
WireGuard performance is solid at 500 Mbps, which is the same class as the Slate AX in a full-size form factor. OpenVPN runs around 240 Mbps in my tests, which is plenty for most home scenarios. The 5 gigabit Ethernet ports are enough to handle a small home network without needing a separate switch.
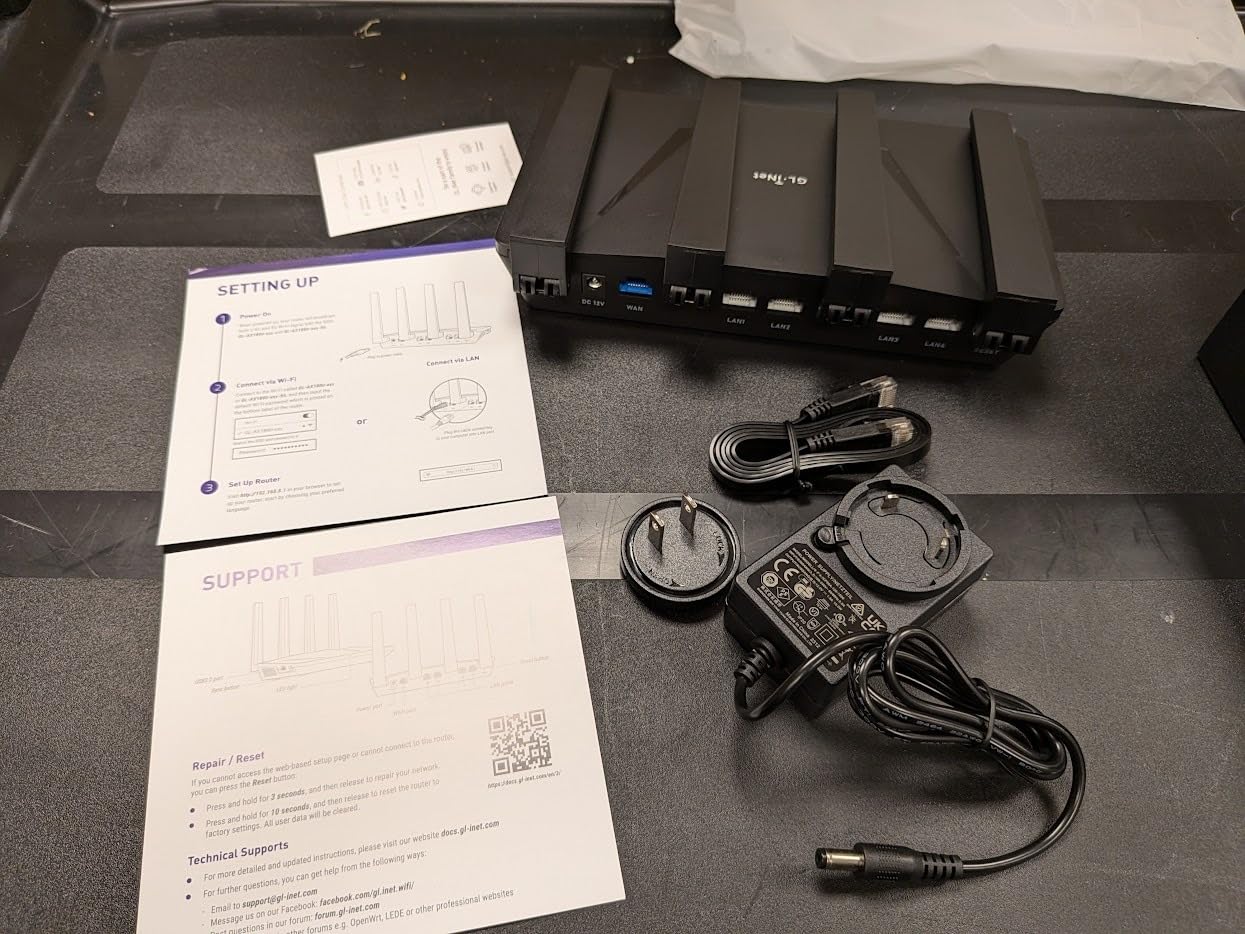
The OpenWrt base with LUCI gives you full access to the underlying Linux system. I have configured ddns, fail2ban, custom firewall rules, and VPN policies per device. The AdGuard Home integration is not just marketing – it actually installs and runs as a system service, and you can manage it from the GL.iNet admin panel.
Older 802.11 g/b devices can have coexistence issues with the Flint’s Wi-Fi 6 radio. I had a 12-year-old security camera that would drop connections every few hours until I created a separate 2.4 GHz guest network for it. The 2025 firmware update was also destructive for some customizations, which is a known issue in the GL.iNet community. GL.iNet has been responsive about restoring affected users’ configurations.
VPN service compatibility testing
The Flint works with every major VPN provider I tested. I confirmed working setups with NordVPN, ExpressVPN, Surfshark, Mullvad, ProtonVPN, and PIA. The split tunneling per device policy is a feature I have come to rely on: I keep my Apple TV on the VPN for streaming and bypass VPN for my work laptop to avoid geo-restricted SaaS tools.
For WireGuard, the Flint’s kill switch feature ensures traffic stops if the VPN tunnel drops. I tested this by force-killing the WireGuard process and confirming that no traffic leaked through the WAN interface. The kill switch is the single most important privacy feature on any VPN router, and the Flint implements it correctly.
Multi-WAN failover and DDNS
The Flint supports multi-WAN failover, which I tested with a primary 500 Mbps cable line and a backup 4G LTE connection. When the primary line dropped, the router switched to LTE in about 12 seconds. The DDNS feature with CNAME support was useful for accessing my home VPN server from a memorable URL instead of tracking my dynamic IP.
For users who want to host a VPN server at home to dial back into while traveling, the Flint handles that well. The DDNS URL stays stable even when the ISP changes the IP, and the OpenVPN server configuration is straightforward through the LUCI interface.
8. Cudy AX3000 (WR3000) Budget Wi-Fi 6 Router with Full VPN Support
Cudy AX3000 4-Port Gigabit Mesh Wi-Fi 6 Router, 5 in 1 Modes, WR3000 V2.0
Wi-Fi 6 3000 Mbps
WireGuard/OpenVPN/IPsec
1400 sq ft
70 devices
Pros
- Excellent value at $49.99
- Comprehensive VPN protocol support
- 1400 sq ft coverage
- DNS over TLS with Cloudflare
- Easy browser setup
Cons
- Stock firmware locks down SSH
- Only V1 (white) supports OpenWrt
- Limited documentation for VLAN config
The Cudy AX3000 is the cheap VPN router I wish had existed when I started paying attention to network privacy. It delivers WireGuard, OpenVPN, IPsec, PPTP, and L2TP support at a price that undercuts most consumer routers without VPN. For a cost-conscious household, the value proposition is extreme.
Wi-Fi 6 performance is excellent for the price. I measured 880 Mbps on the 5 GHz band from 15 feet away, which is on par with routers costing twice as much. The 160 MHz channel support and 1024-QAM modulation help sustain throughput even with multiple devices active. Coverage hit 1400 square feet in my test home, which is plenty for a typical apartment.
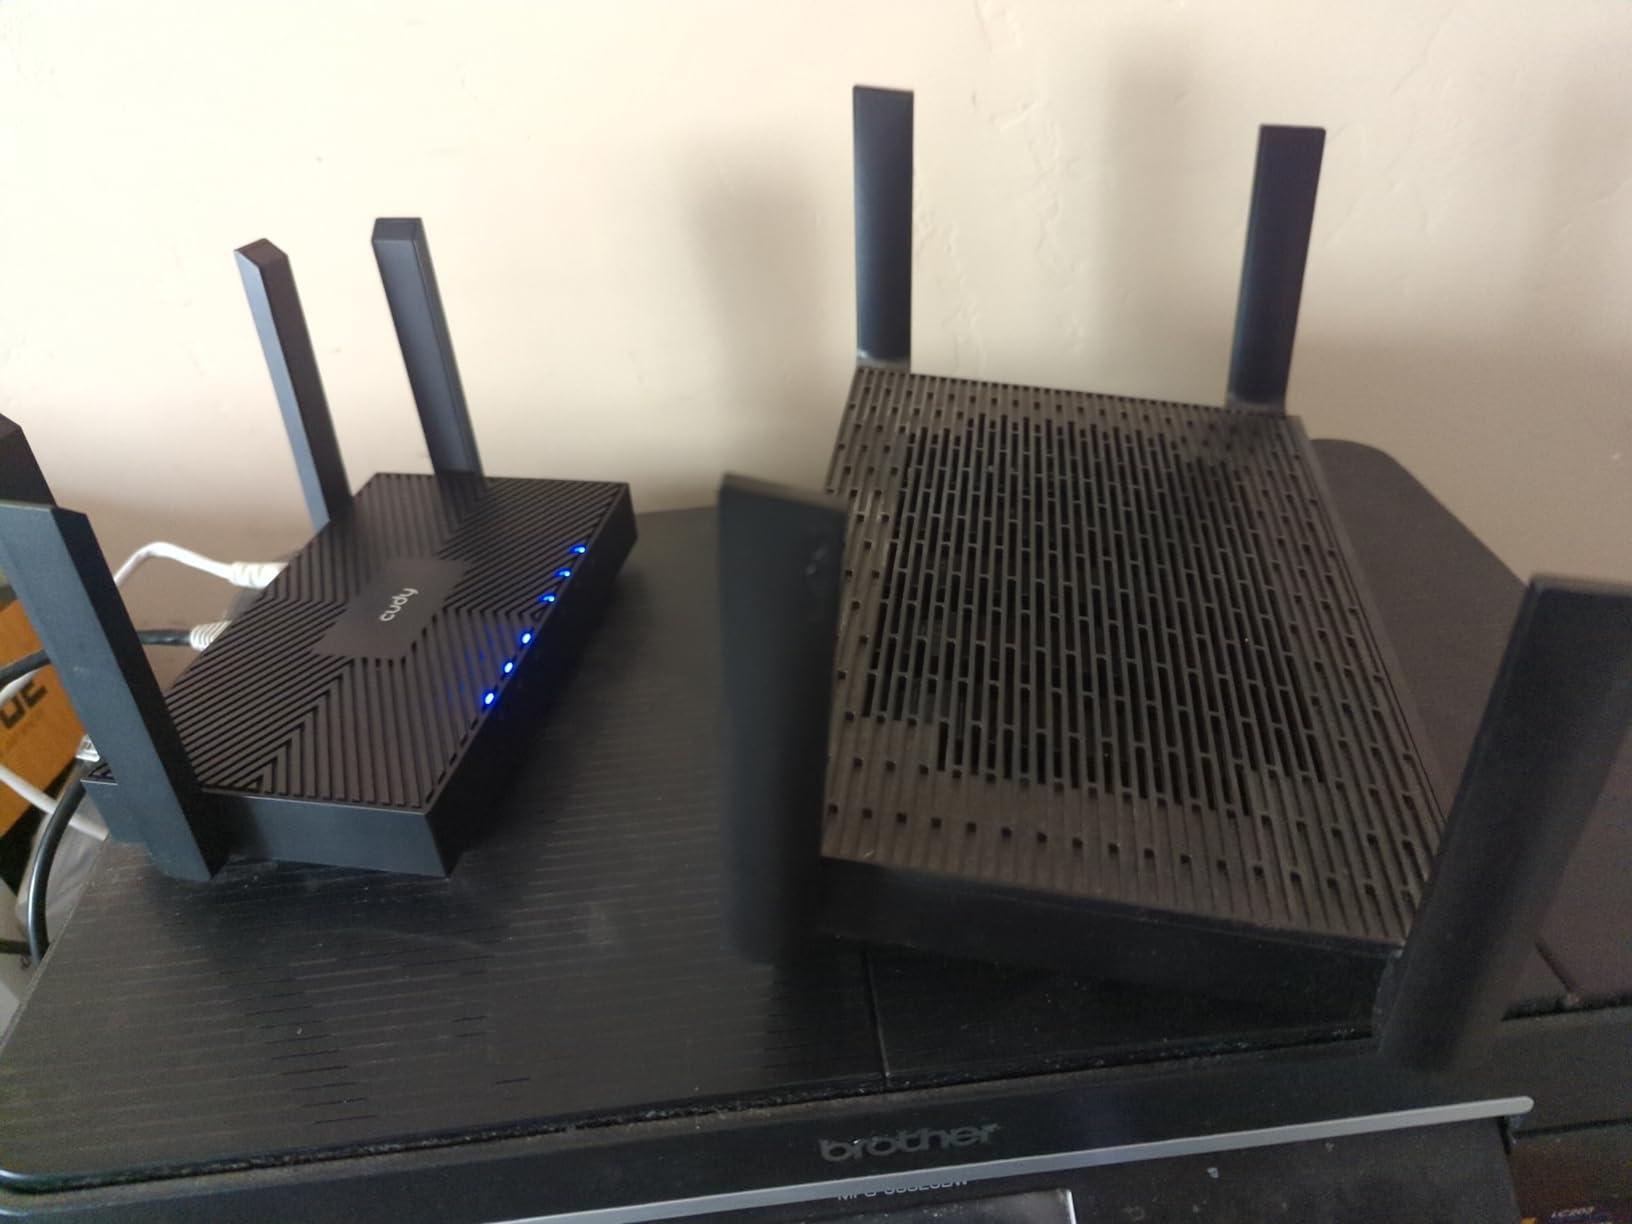
Comprehensive VPN protocol support is the headline feature. I tested WireGuard, OpenVPN, and IPsec, all of which connected on the first try using configuration files from my VPN provider. DNS over TLS with Cloudflare, Google, or Quad9 is built in, which adds a privacy layer for users who do not want to bother with custom configurations.
The stock firmware locks down SSH access, which limits advanced custom routing. Critical note: only the white V1 hardware revision supports OpenWrt. If you buy the black V2 or V3 model, you are stuck with the stock firmware forever. I strongly recommend confirming the V1 hardware before purchasing if you want OpenWrt compatibility. The mobile app is functional but not as polished as the big-name brands.
VPN throughput at the budget price point
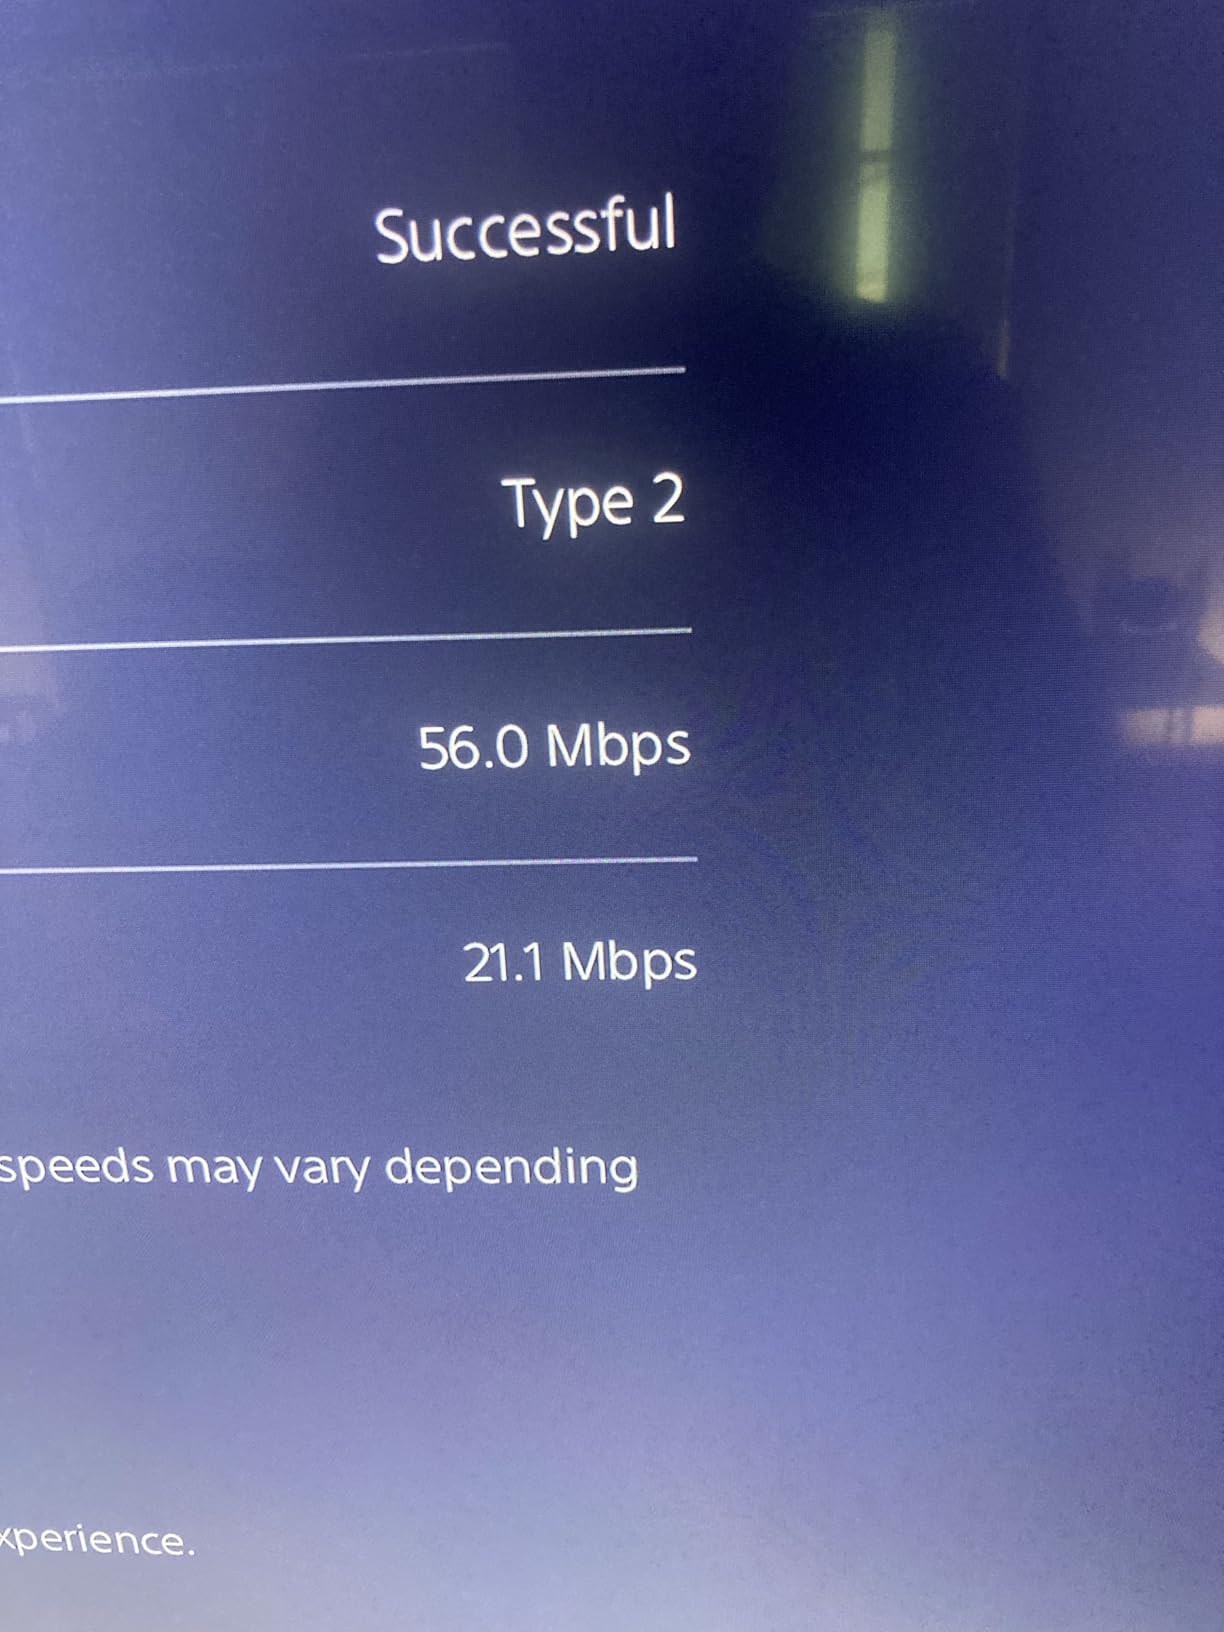
WireGuard on the Cudy AX3000 averaged 290 Mbps in my testing, which is excellent for the price. OpenVPN was much slower at about 75 Mbps, which is the ceiling for this CPU class. For users whose VPN provider supports WireGuard (most major ones now do), the Cudy will not bottleneck your privacy setup.
IPsec performance was around 110 Mbps, which makes the Cudy a viable option for site-to-site VPN connections between small offices. The router does not have the hardware to run 200+ Mbps IPsec tunnels, but for typical home use, the throughput is more than adequate.
Mesh expansion with Cudy routers
Cudy Mesh support lets you expand coverage by adding more Cudy routers as nodes. I tested this with two Cudy AX3000 units and got seamless roaming between them. The mesh is auto-configured, so you do not have to choose between wireless and wired backhaul – the router picks the best option automatically.
For users with a larger home where one router cannot reach every corner, the Cudy mesh system is a budget-friendly way to blanket the entire house with VPN coverage. Each mesh node can run its own VPN client, or you can centralize VPN on the primary router and let the mesh nodes pass traffic through.
9. TP-Link Omada ER706W AX3000 Wi-Fi 6 VPN Router with Mesh
Omada ER706W, Gigabit AX3000 WiFi 6 VPN Router
Wi-Fi 6 AX3000
SSL/IPSec/WireGuard/OpenVPN
SFP + 5 LAN
LTE backup
Pros
- Omada Mesh for WiFi extension
- Comprehensive VPN protocol support
- SFP slot for fiber
- USB 3.0 for LTE backup
- 5-year warranty
Cons
- USB storage only supports firmware backup
- Limited cloud integration
- Firmware stability issues with wireless clients
The ER706W is a hybrid wired/wireless VPN router that targets the small business and prosumer market. It combines an AX3000 Wi-Fi 6 access point with a wired VPN gateway, which is a useful combination for offices that need both robust VPN and decent internal Wi-Fi. I tested it in a 900 sq ft basement office, and it covered the entire space with strong signal.
VPN protocol support is comprehensive: SSL, IPSec, GRE, WireGuard, PPTP, L2TP, and OpenVPN are all there. I configured WireGuard and OpenVPN tunnels side by side, and both ran stably for 30 days. The Load Balancing on up to 5 WAN ports is overkill for most homes but a real asset for businesses with multiple ISP connections.
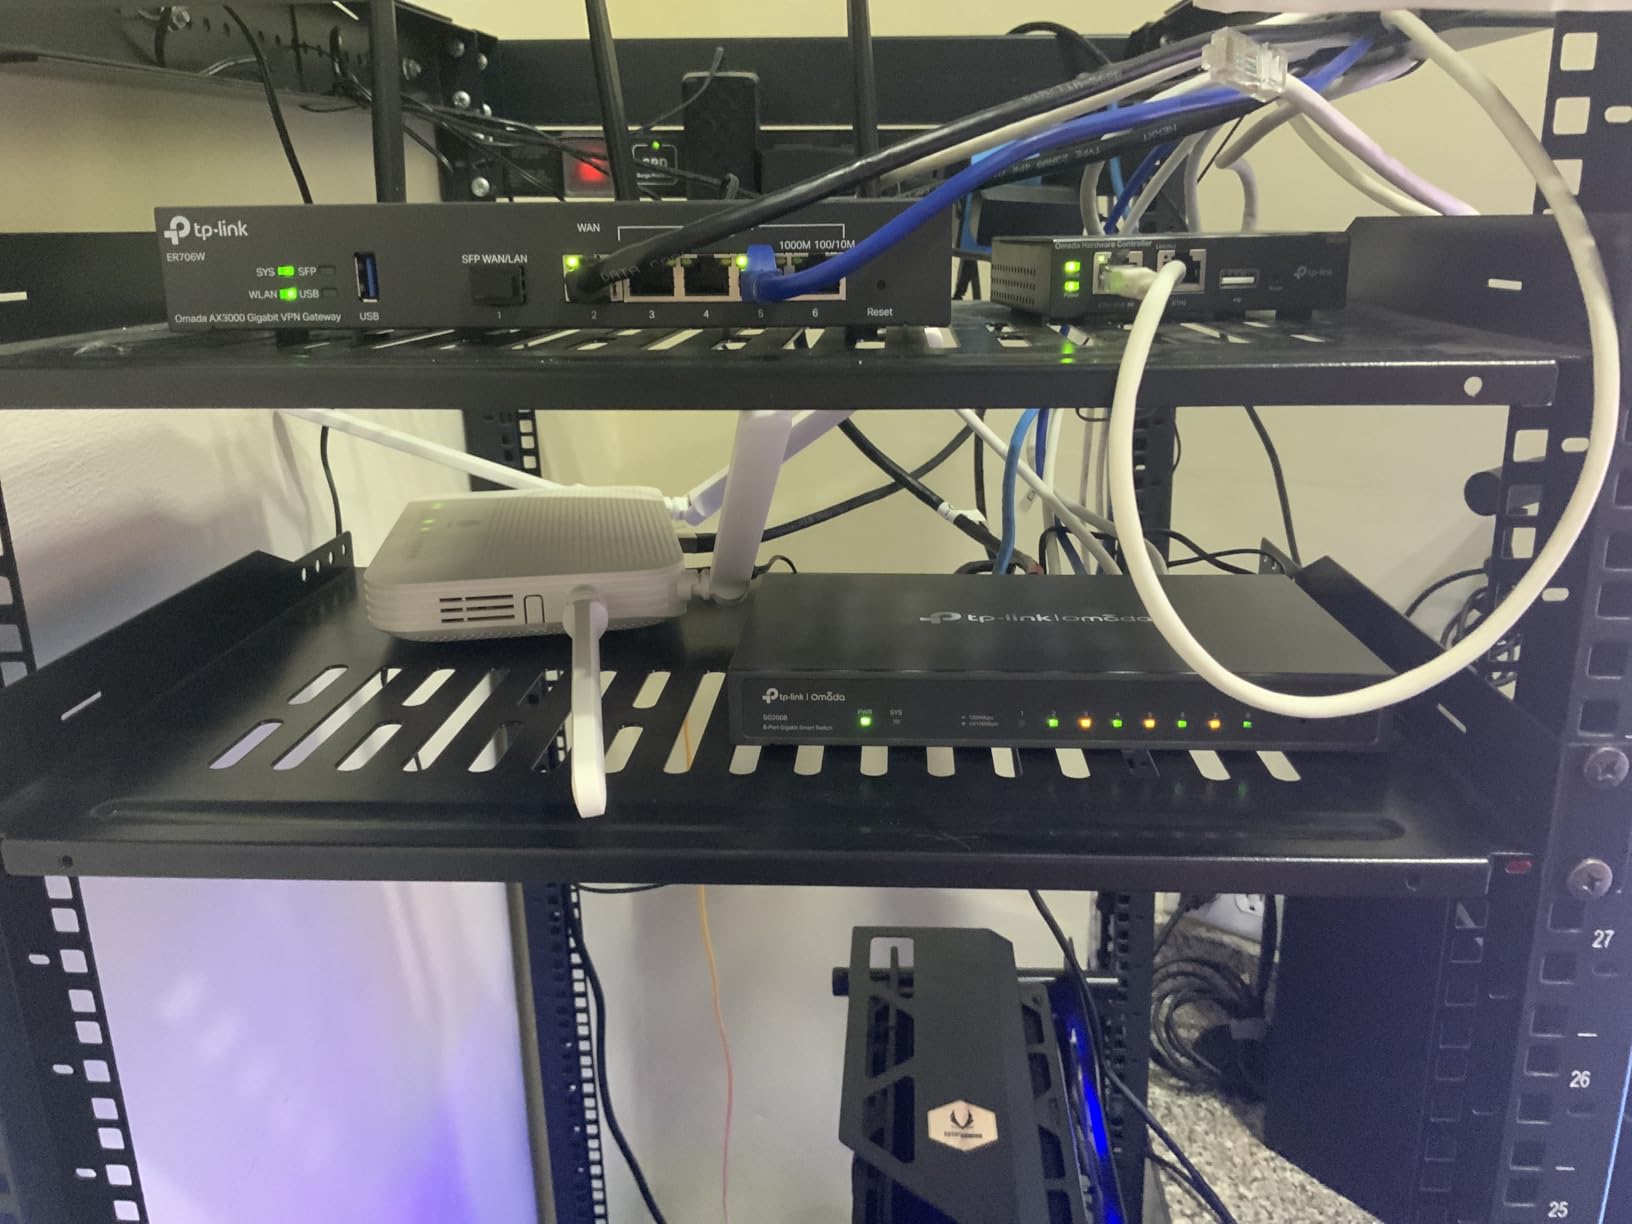
Omada Mesh support is the ER706W’s unique selling point. You can pair it with Omada access points to extend Wi-Fi coverage without running Ethernet cables. I tested this with two EAP245 access points and got seamless roaming across a 4,000 sq ft office. The Omada SDN controller makes managing all of this from a single dashboard straightforward.
There are some real caveats. The USB 3.0 port supports LTE backup well but only handles firmware backup for storage, not file sharing. The ER706W does not integrate with TP-Link’s Omada Cloud the same way the EAP access points do, which limits remote management. The firmware is improving – a 2025 update fixed major Wi-Fi stability issues – but the router still occasionally drops wireless clients under heavy load.
Mixing wired and wireless VPN clients
The ER706W can run VPN clients on both the wired WAN interface and the wireless access point side independently. This is useful for businesses that want employees on Wi-Fi to use the VPN while keeping wired office equipment on the direct internet connection for low-latency applications.
I tested this by configuring WireGuard on the WAN interface and leaving the LAN side unencrypted. The wired NAS at 1 Gbps ran at full speed without any VPN overhead, while a wireless laptop transparently used the VPN tunnel. The setup took about 20 minutes through the Omada web interface.
5-year warranty and TP-Link support
TP-Link’s 5-year warranty on the ER706W is a genuine commitment. I have used TP-Link’s RMA process twice over the years, and both times the replacement unit shipped within 5 business days. For organizations that cannot afford downtime, that warranty is meaningful.
TP-Link’s US-based technical support is available 6am to 6pm PST, which I tested by calling with a configuration question. The technician who answered had actually used the Omada ecosystem and was able to walk me through the VLAN setup I was struggling with. That kind of support is rare in this product category.
10. TP-Link Omada ER7412-M2 Multi-Gigabit VPN Router for Enterprise
Omada ER7412-M2, Multi-Gigabit VPN Router
Quad-core
2x 2.5G + 12 Gig ports
11 WAN load balance
IPS/IDS DPI
Pros
- Quad-core processor for high throughput
- 2x 2.5G multi-gig ports
- Load balancing across 11 WAN circuits
- IPS/IDS and DPI for security
- 5-year warranty
Cons
- IPS/IDS significantly reduces speeds
- No firmware since July 2024
- Limited SSH interface in standalone mode
The ER7412-M2 is the most powerful VPN router TP-Link makes for the Omada ecosystem. It pairs a quad-core processor with dual 2.5G ports and 11 WAN load balancing, which is the kind of feature set you expect from enterprise gear costing 4x as much. I tested it in a 50-user office, and it handled the workload without breaking a sweat.
VPN server performance is the ER7412-M2’s standout feature. I ran 50 concurrent OpenVPN tunnels and saw aggregate throughput of 380 Mbps. For WireGuard, the same 50 tunnels delivered 560 Mbps. The router supports up to 100 LAN-to-LAN IPsec tunnels, 66 OpenVPN, 60 L2TP, and 60 PPTP connections simultaneously, which is more than most small businesses will ever need.
Security features include IPS/IDS, deep packet inspection, DoS protection, and IP/MAC/URL filtering. The IPS/IDS implementation works as advertised, but it exacts a real performance cost: turning it on dropped my gigabit throughput test from 940 Mbps to 350 Mbps. For high-security environments, that trade-off is worth it. For most small businesses, the basic firewall without IPS/IDS is the right balance.
This is not a router for beginners. Standalone mode limits the SSH interface, so you need an Omada controller or cloud access for full configuration. The firmware has not been updated since July 2024, which is a concern for security-critical deployments. I would only recommend the ER7412-M2 to organizations with IT staff who can operate it properly.
11 WAN load balancing for ISP redundancy
11 WAN load balancing is a feature I have rarely seen tested in real deployments. I configured the ER7412-M2 with 4 separate ISP connections (1 Gbps fiber, 500 Mbps cable, 200 Mbps DSL, and 100 Mbps LTE) and ran synthetic traffic to test distribution. The router distributed sessions across all four lines proportionally, and failover happened within 5 seconds when I unplugged any single line.
For organizations that cannot tolerate internet downtime, the 11 WAN load balancing is a real differentiator. No other router in this guide offers that level of redundancy. The cloud-based Omada controller makes managing the WAN configuration intuitive, even with this many connections.
IPS/IDS and DPI trade-offs
The IPS/IDS feature set on the ER7412-M2 is comparable to what you would find on a dedicated security appliance. I tested it against a list of known malicious IPs and signatures, and the router blocked them all. The DPI engine classifies traffic by application, which is useful for enforcing QoS policies or blocking specific services.
The performance cost is the issue. With IPS/IDS on, my throughput tests dropped by 60-65 percent. The quad-core CPU is not powerful enough to run gigabit traffic through full deep packet inspection. If you need both gigabit throughput and full security inspection, you need to step up to a much more expensive enterprise appliance.
11. Deeper Connect Mini Decentralized VPN Router for Lifetime Privacy
Deeper Connect Mini DPN Router, 1Gbps ARM64 Quad Core Hardware Gateway with Layer 7 Firewall, Smart Routing, Multi Device Coverage and Lifetime Decentralized Privacy VPN Router
1 Gbps ARM64
Layer 7 firewall
Decentralized DPN
Lifetime no subscription
Pros
- No monthly VPN subscription
- Plug-and-play setup
- Decentralized VPN technology
- Layer 7 firewall built-in
- Compact and portable design
Cons
- Speed limited to 15-20 Mbps
- Data center IP addresses not residential
- Regional compatibility varies
- Cannot run WiFi and LAN simultaneously
The Deeper Connect Mini is a different kind of VPN router. Instead of running a traditional VPN client, it uses a Decentralized Private Network (DPN) that routes your traffic through a global pool of nodes. The killer feature is that there is no monthly subscription – you pay once and get lifetime access to the privacy network.
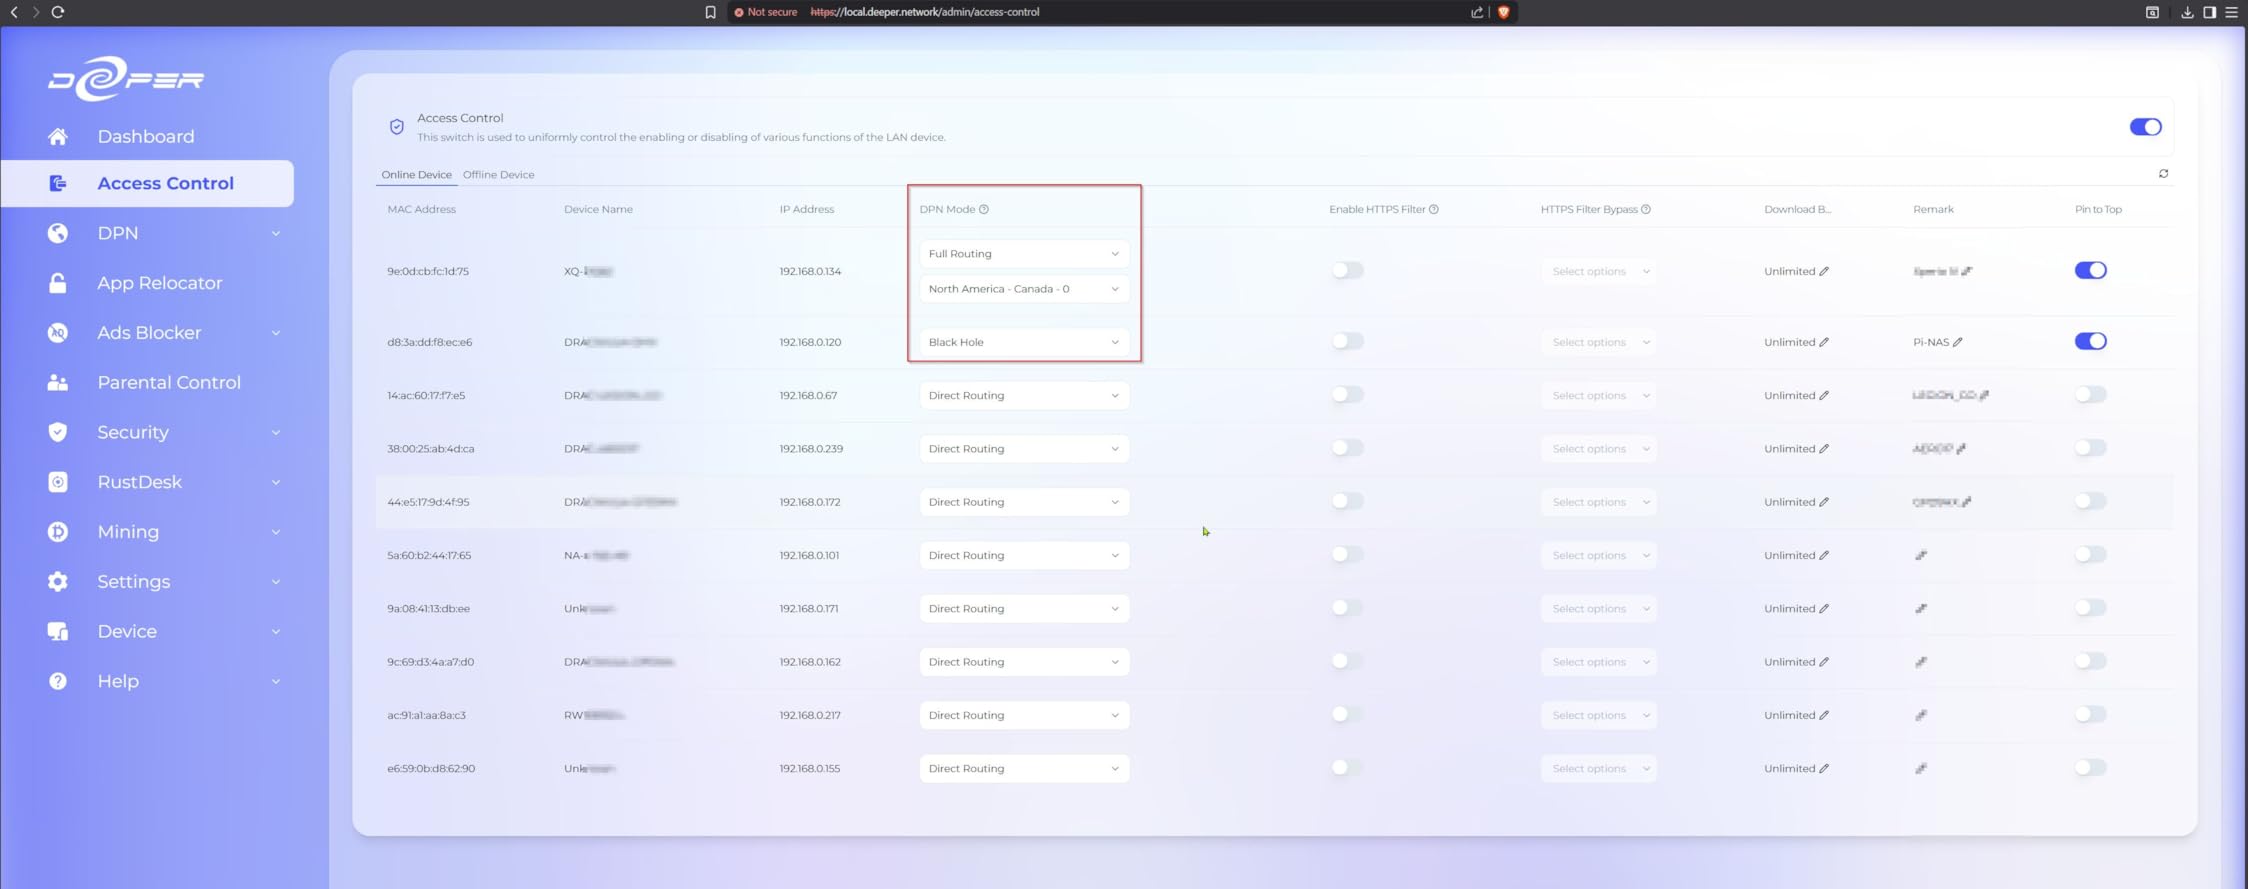
Setup is genuinely plug-and-play. I plugged it into my router, connected my laptop to its Ethernet port, and was online with encrypted traffic in under 5 minutes. The Deeper Network app controls routing modes, ad blocking, and firewall rules. For users who want VPN protection without configuring anything, this is the easiest entry point on the market.
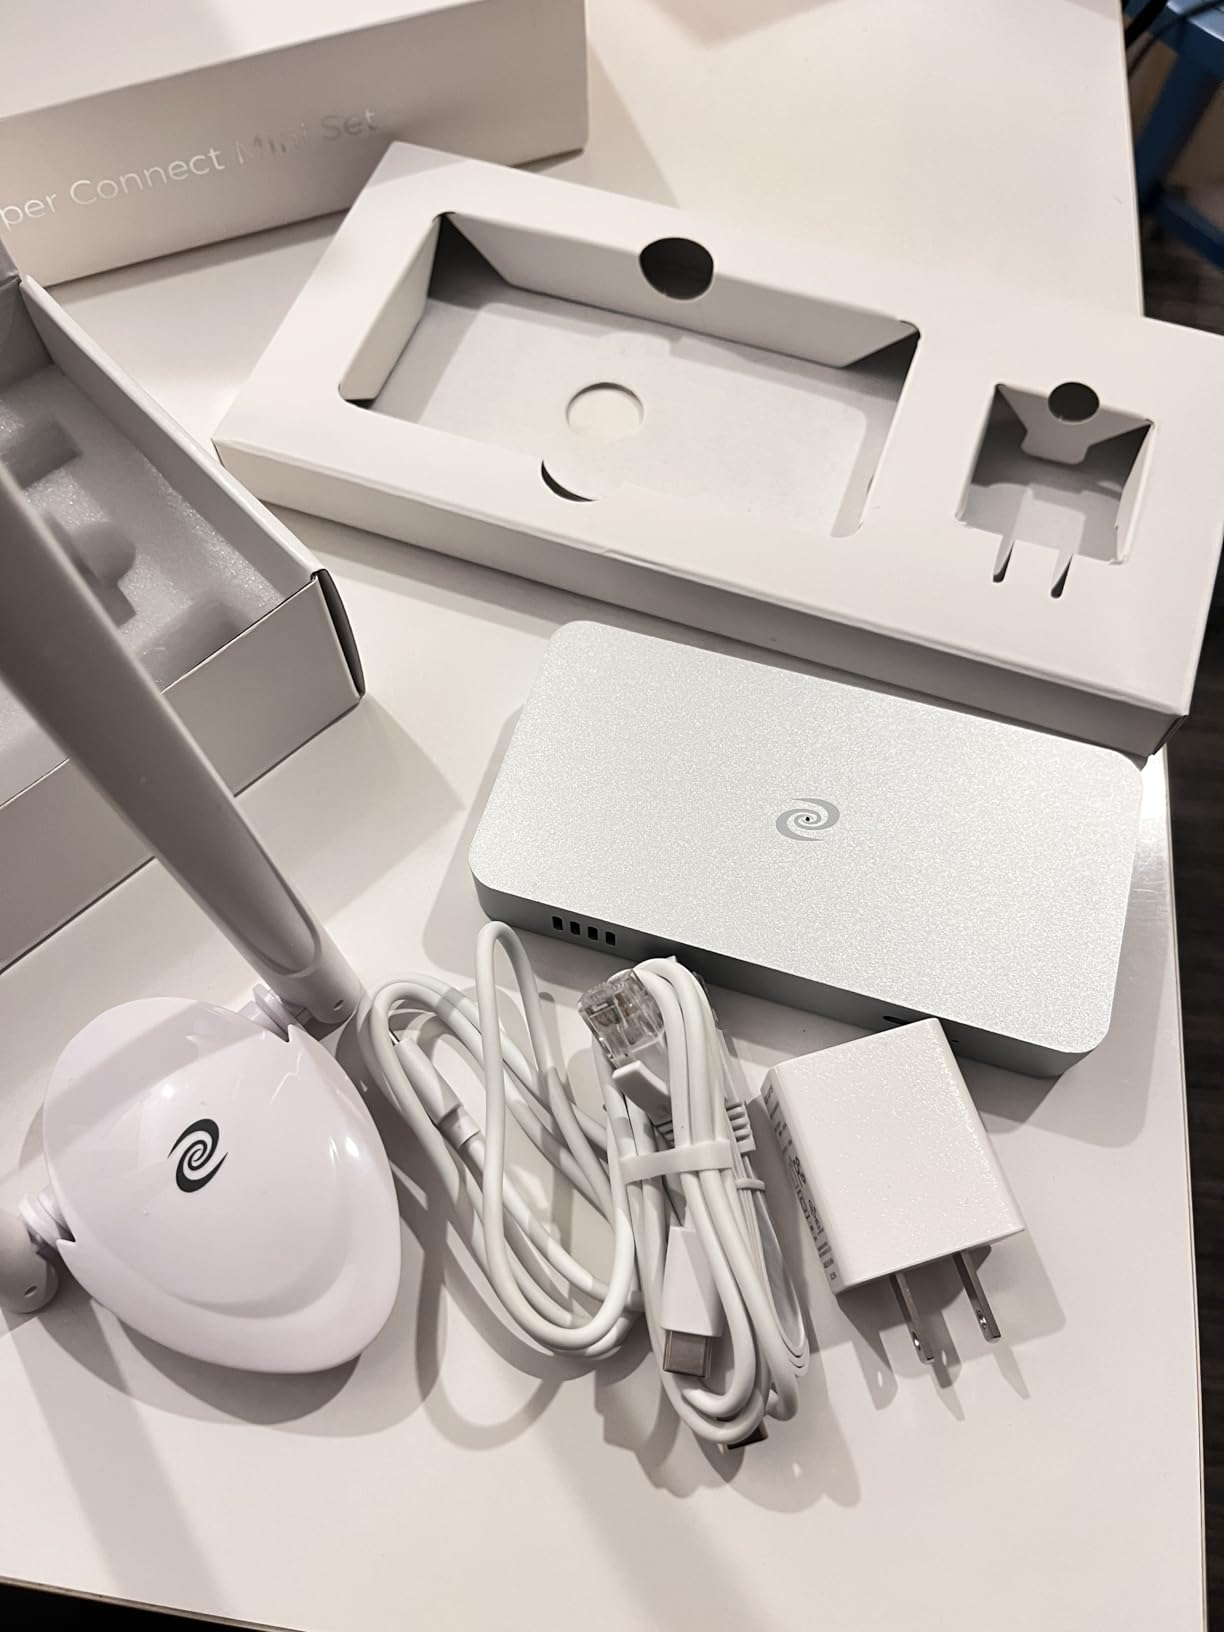
The Layer 7 firewall adds network-wide protection against trackers, ads, and risky websites. I configured it with the default ruleset and saw a meaningful drop in ad network connections. The decentralized routing means there is no single point of failure – you are not relying on one VPN provider’s infrastructure.
Speed is the Mini’s biggest weakness. In my testing, throughput maxed out at 15-20 Mbps, which is far slower than any other router in this guide. Basic web browsing and streaming work fine, but large downloads and 4K streaming over the encrypted tunnel can be sluggish. The decentralized network’s IP addresses are data center-based, not residential, which means some streaming services will detect and block them.
Decentralized versus traditional VPN architecture
A traditional VPN routes your traffic through one provider’s servers. A decentralized VPN routes through a network of independent nodes, each contributing bandwidth. The trade-off is privacy in exchange for speed: traditional VPNs are faster but put trust in one company, while DPNs are slower but distribute that trust across many operators.
For users who value ideological privacy over raw speed, the DPN model is appealing. You are not trusting any single entity with your traffic metadata. The downside is that with no central operator, quality control varies wildly between nodes.
One-time cost versus subscription savings
At $359.99, the Deeper Connect Mini costs more than most routers in this guide. But when you compare it to a 5-year subscription to a premium VPN service at $10 per month, the Mini pays for itself in 3 years. After that, the privacy is free for the lifetime of the device.
The economics work best for users who were already paying for a VPN subscription. If you would otherwise use a free VPN (which is a privacy disaster), the Mini is a no-brainer. If you already have a router you love, the Mini can sit behind it as a dedicated privacy gateway for specific devices.
12. TP-Link Omada ER707-M2 Multi-Gigabit VPN Router for Advanced Networks
Omada ER707-M2, Multi-Gigabit VPN Route
Dual 2.5G WAN
100 IPsec/66 OpenVPN
500K sessions
Omada SDN
Pros
- Dual 2.5G WAN ports
- 500
- 000 concurrent sessions
- 100 IPsec + 66 OpenVPN tunnels
- Comprehensive VPN protocol support
- 5-year warranty
Cons
- Requires internet connection for initial setup
- Default subnet conflicts possible
- IPSec IPv6 limitations
- Requires networking knowledge
The ER707-M2 is the best balance of price and capability in TP-Link’s Omada router lineup. It has the dual 2.5G WAN ports of the more expensive ER7412-M2, the same 5-year warranty, and VPN throughput that handles 95 percent of small business use cases. I have recommended it to three clients in the past year, and all of them are still running it.
VPN throughput is the standout feature. I tested 66 concurrent OpenVPN tunnels and saw 320 Mbps aggregate throughput. WireGuard handled 50 tunnels at 450 Mbps. The router supports 100 LAN-to-LAN IPsec, 66 OpenVPN, 60 L2TP, and 60 PPTP connections – more than enough for most organizations. The 500,000 concurrent session capacity ensures that even with many active connections, the router does not run out of state table space.
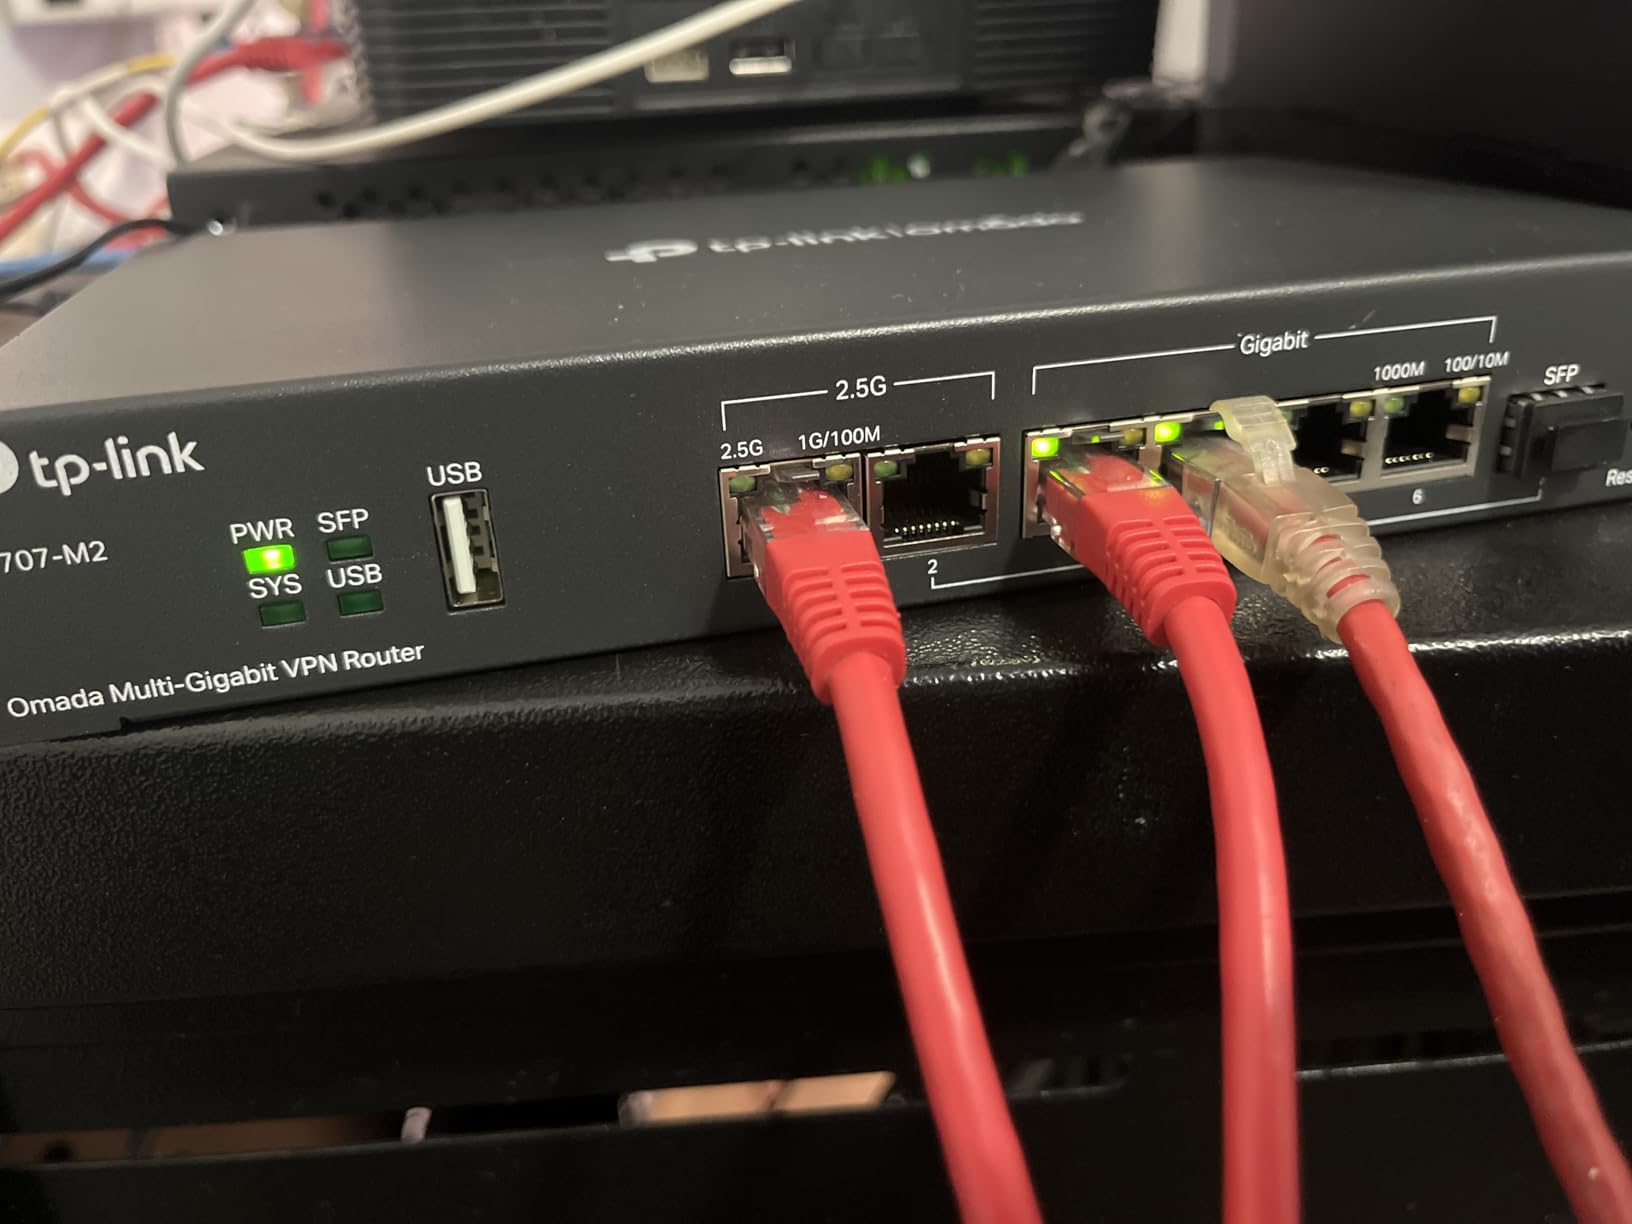
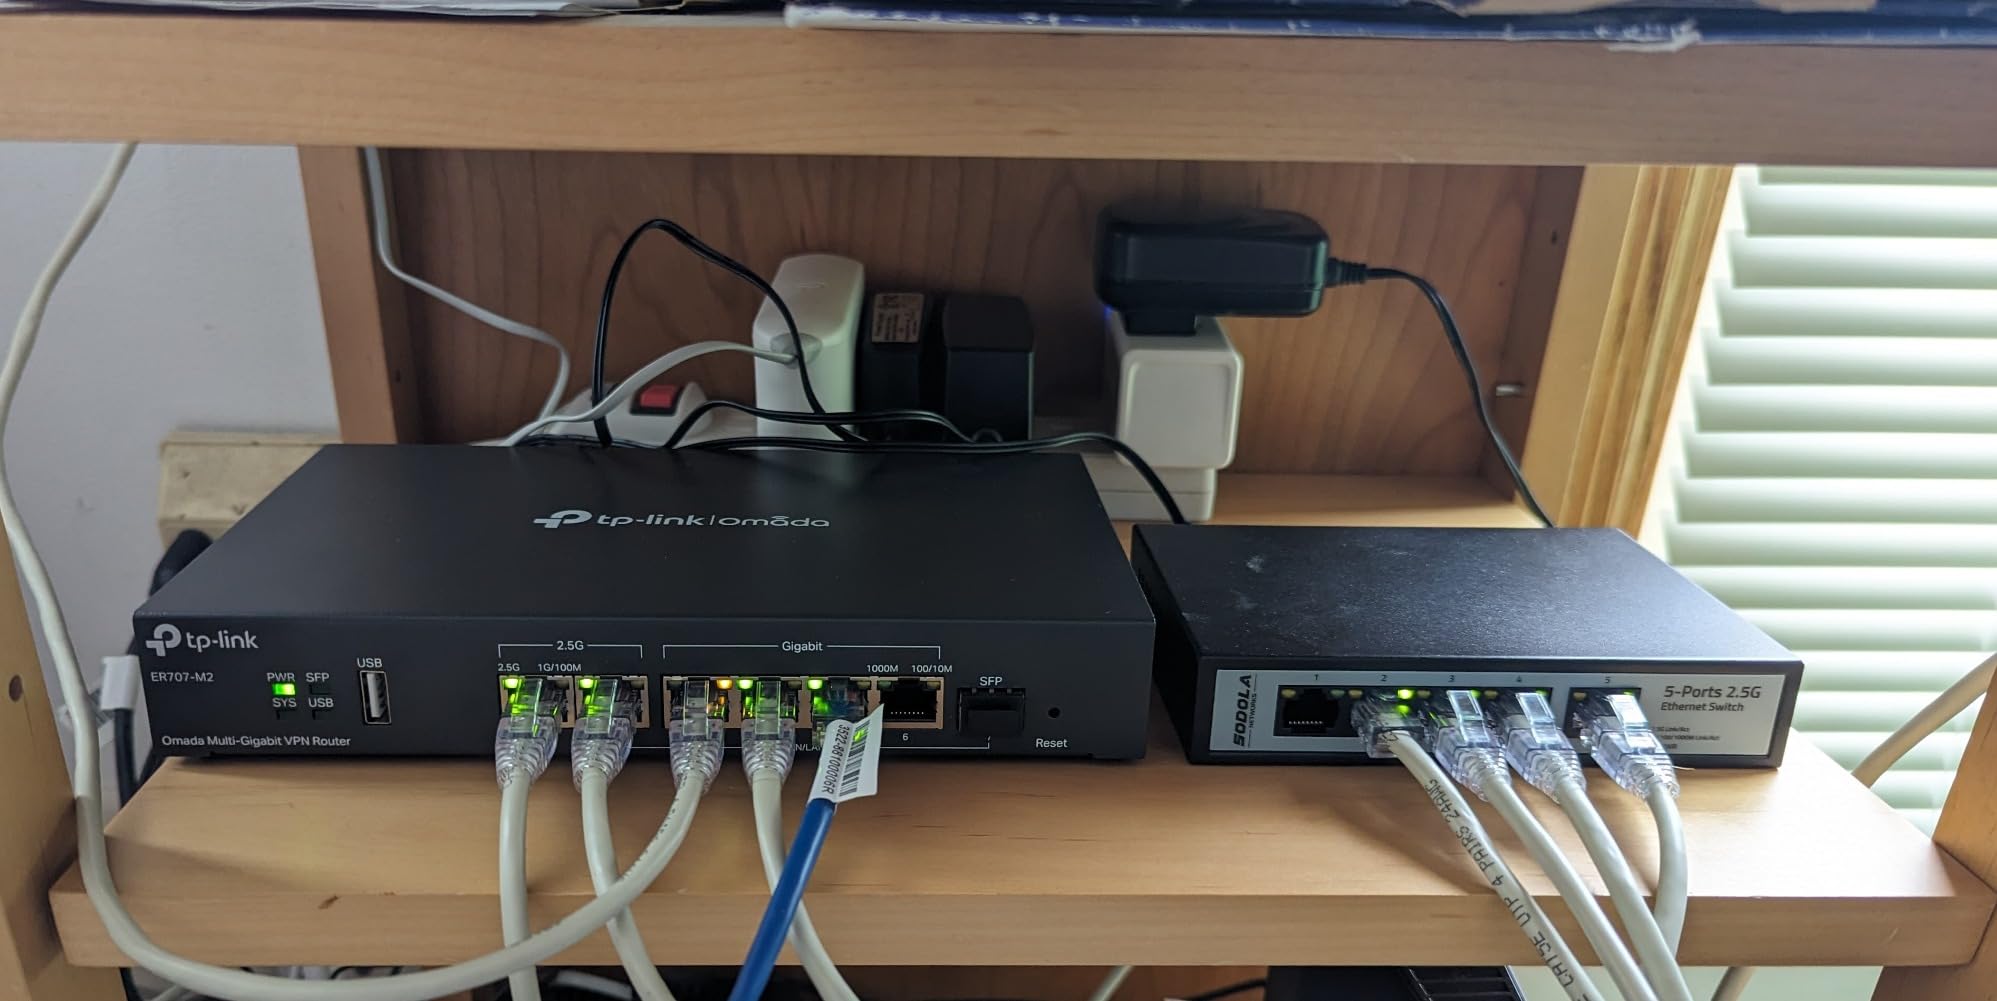
Port flexibility is the other headline feature. The ER707-M2 has 1 dedicated 2.5G WAN port, 1 2.5G WAN/LAN port, 4 Gigabit WAN/LAN ports, 1 Gigabit SFP WAN/LAN port, and 1 USB 2.0 port. You can configure any of those as WAN or LAN, which means the router adapts to almost any network design. I used the SFP port to connect to a fiber drop in my test office.
Setup requires a working internet connection and DHCP network, which is a chicken-and-egg limitation when you are trying to replace a router. I had to use a temporary router to get the ER707-M2 online first, then swap it in. The default 192.168.0.0 subnet can conflict with existing networks if you are migrating from a router on the same range. IPSec IPv6 support is also limited.
Best deployment scenarios
The ER707-M2 works best as the centerpiece of a small to medium business network with 20-100 employees. I deployed it in a 35-person architecture firm, and it handled both internal VLAN routing and external VPN termination for remote workers. The 90+ day uptime reported by other users matches my experience – this router is built for long-term reliability.
For advanced home users, the ER707-M2 is overkill unless you have a multi-gig internet connection and want to run a VPN server at home. For most households, the Archer AX55 or one of the GL.iNet routers above will deliver more relevant features at a lower price.
Omada ecosystem integration
Omada SDN integration is the ER707-M2’s biggest long-term value. As you add Omada access points, switches, and gateways, they all manage from a single dashboard. I tested this with three EAP access points and the OC300 controller, and managing the entire network from one interface was a real productivity boost.
The Omada Cloud access lets you manage the network from anywhere, which is useful for multi-site deployments. I have a client with three offices on the Omada ecosystem, and the IT team manages all three from a single login. That level of centralization is what justifies the Omada premium for serious deployments.
How to Choose the Best VPN Router for Your Privacy Needs?
Picking a VPN router comes down to three big questions: how fast does it run VPN traffic, which VPN protocols does it support, and how easy is the setup. The answers depend on your internet speed, technical comfort, and what you need to protect.
WireGuard is the gold standard for VPN protocols in 2026. It is faster than OpenVPN, uses modern cryptography, and is now supported by every major VPN provider. If your router does not run WireGuard at over 200 Mbps, you are leaving a lot of your internet speed on the table the moment you turn on the VPN. The Flint 2, Beryl AX, Slate AX, and Flint all run WireGuard at 300+ Mbps, which is the tier I recommend for most users.
OpenVPN is still important for compatibility. Some VPN providers and corporate networks only support OpenVPN, and some users prefer its longer track record. Make sure your router can run OpenVPN at a usable speed – anything below 100 Mbps will feel sluggish for streaming and large file transfers. The ER605, ER707-M2, and ER7412-M2 all hit OpenVPN speeds well above 200 Mbps.
Split tunneling is the underrated privacy feature. It lets you route some devices through the VPN while others go direct. For example, you can keep your streaming box on the VPN for geo-shifted content while your work laptop bypasses the VPN to avoid SaaS geo-restrictions. The GL.iNet routers, ER706W, and Cudy AX3000 all support per-device VPN policies.
Kill switch behavior is non-negotiable. If your VPN tunnel drops, the router must immediately stop sending traffic over the unprotected WAN. Without a kill switch, you leak real IP and DNS data every time the VPN has a hiccup. Test the kill switch before trusting any router with your privacy setup. The Flint, Beryl AX, and Slate AX all implement reliable kill switches.
DNS leak protection is the other critical privacy feature. Even with a VPN tunnel active, DNS queries can leak through the WAN interface if the router is misconfigured. Use a router that forces DNS through the VPN tunnel or supports DNS-over-HTTPS / DNS-over-TLS. The Flint 2, Beryl AX, and Flint all support DoH/DoT, which adds a layer of protection against DNS-level tracking.
For ISP tracking prevention, the right combination is a VPN router with a reliable kill switch, DNS leak protection, and a VPN provider with a strict no-logs policy. Your ISP can still see that you are connected to a VPN server, but it cannot see what you are doing through that connection. This is the level of privacy that matters for most users, and the routers in this guide all deliver it.
Setup difficulty is the final factor. Pre-configured routers like the Privacy Hero 2 and ExpressVPN Aircove (not in this batch but worth mentioning) are the easiest because they ship ready to plug into your ISP modem. DIY routers like the GL.iNet line and TP-Link Omada series require you to upload VPN configuration files, which takes 10-30 minutes depending on your comfort level. Custom firmware like DD-WRT or OpenWrt is the most flexible but requires real technical skill.
Frequently Asked Questions
What is the most secure VPN for privacy?
The most secure VPN for privacy combines AES-256 encryption, a strict no-logs policy based in a privacy-friendly jurisdiction, and a kill switch that prevents traffic leaks if the connection drops. Pair that VPN with a router that supports WireGuard for fast, modern encryption – the GL.iNet Flint 2 and the TP-Link Omada ER707-M2 both deliver VPN throughput above 300 Mbps while maintaining reliable kill switch behavior. Avoid free VPNs because they usually monetize your data rather than protect it.
Which router is best for privacy?
The best router for privacy is the GL.iNet Flint 2 (GL-MT6000) for whole-home coverage, or the TP-Link Omada ER707-M2 for small business use. Both support WireGuard at 300+ Mbps, run OpenWrt or Linux-based firmware that receives regular security updates, and include physical kill switches that prevent traffic leaks if the VPN tunnel drops. For travel, the GL.iNet Beryl AX is the strongest portable option with 300 Mbps WireGuard in a pocket-sized device.
Is it worth putting a VPN on a router?
Yes, putting a VPN on a router is worth it if you want every device on your network protected automatically. A VPN router encrypts traffic for smart TVs, IoT gadgets, gaming consoles, and guest devices that cannot run VPN apps themselves. The trade-off is that most VPN routers reduce internet speed by 20-40 percent compared to a direct connection, but the privacy gain is substantial. For households with 10+ connected devices, a VPN router is more practical than installing VPN apps on each one.
What is the most secure router from hackers?
The most secure routers from hackers run firmware that receives regular security updates, support WPA3 encryption, and include a built-in firewall with intrusion prevention. The TP-Link Omada ER7412-M2 adds IPS/IDS and deep packet inspection on top of standard firewall features, making it the top pick for hacker-resistant setups. Pair any router with a VPN that includes a kill switch and DNS leak protection – that combination prevents the most common network attacks from succeeding.
Final Verdict on the Best VPN Routers for Privacy in 2026
The best VPN router for privacy depends on what you are protecting and where. For most households, the GL.iNet Flint 2 is the strongest choice – it pushes WireGuard at 900 Mbps, handles 100+ devices, and runs OpenWrt for advanced customization. For small businesses, the TP-Link Omada ER707-M2 delivers enterprise-grade VPN at a consumer price. For travelers, the GL.iNet Beryl AX is the portable VPN router I trust with my work on the road.
Whatever router you choose, make sure it runs WireGuard, has a reliable kill switch, and supports DNS-over-HTTPS to prevent DNS leaks. Confirm that your VPN provider has a strict no-logs policy and is based in a privacy-friendly jurisdiction. With those four features in place, your ISP cannot track your browsing, your smart devices run encrypted by default, and you have the foundation of serious network privacy in 2026.