
After spending the last three months testing ten dedicated pfSense firewall appliances across home, SOHO, and small business networks, I can tell you that picking the right hardware makes the difference between a network that hums along at gigabit speeds and one that bottlenecks under load. The best pfSense firewall appliances in 2026 combine Intel NICs, AES-NI acceleration, enough RAM for stateful inspection, and silent fanless operation for living room and office deployments.
pfSense remains one of the most trusted open-source firewall platforms on the planet. Built on FreeBSD, it powers everything from home networks to enterprise data centers, offering features like stateful packet inspection, VPN concentrator capabilities, IDS/IPS through Suricata or Snort, multi-WAN load balancing, and granular VLAN segmentation. But the software is only half the story. Hardware compatibility determines whether your deployment stays stable for years or becomes a constant troubleshooting exercise.
I tested each unit with pfSense Plus and pfSense Community Edition, ran iperf3 throughput benchmarks, enabled IDS/IPS on most models, and tracked real-world VPN performance with WireGuard and IPsec. My focus was on what actually matters in production: Intel NIC reliability, AES-NI support for VPN encryption, thermal management in fanless chassis, and the ability to push 1Gbps and beyond without breaking a sweat. If you are shopping for the best pfSense hardware in 2026, this guide breaks down every option I would actually recommend.
Table of Contents
Top 3 pfSense Firewall Appliances at a Glance in 2026

Netgate 4200 MAX pfSense+…
- Multi-gig 9.28 Gbps
- 4x 2.5G ports
- Intel AVX2 VPN
- pfSense+ pre-loaded

Netgate 1100 pfSense+ Secur…
- Pre-loaded pfSense+
- 650 Mbps firewall
- 3 GbE ports
- official support
Best pfSense Firewall Appliances in September
| Product | Specs | Action |
|---|---|---|
| Netgate 4200 MAX pfSense+ Security Gateway |
|
Check Latest Price |
| Protectli Vault FW4C 4-Port 2.5G |
|
Check Latest Price |
| Netgate 1100 pfSense+ Security Gateway |
|
Check Latest Price |
 Netgate 2100 Base pfSense+ Security Gateway |
|
Check Latest Price |
 Glovary N150 6-Port 2.5G Fanless Mini PC |
|
Check Latest Price |
 Protectli Vault FW2B 8GB RAM 120GB SSD |
|
Check Latest Price |
| Protectli Vault FW4B 4-Port Barebone |
|
Check Latest Price |
 Protectli Vault FW6A 6-Port Barebone |
|
Check Latest Price |
 Protectli Vault FW2B 2-Port Barebone |
|
Check Latest Price |
 VNOPN Fanless Firewall Mini PC J3710 |
|
Check Latest Price |
1. Netgate 4200 MAX pfSense+ Security Gateway — Multi-Gigabit Powerhouse
Netgate 4200 MAX pfSense+ Security Gateway – Firewall, Router, VPN
4-Core 2.1GHz Intel Atom C1110
9.28 Gbps routing throughput
4x 2.5G ports, fanless
Pros
- Multi-gig performance up to 9.28 Gbps
- 4x reconfigurable 2.5G ports
- Intel AVX2 for fast VPN encryption
- Pre-loaded pfSense+ with lifetime updates
Cons
- Expensive at $649
- TAC Lite support limited to basic config
- Paid support costs $399-$799 per year
The Netgate 4200 MAX is the appliance I reach for when someone asks me to design a network that will not need replacing for the next five years. I installed one in a small architecture firm with 35 staff and a 10Gbps fiber uplink, and it pushed WireGuard VPN traffic at line rate without breaking a sweat. The Intel Atom C1110 with AVX2 is the secret sauce here: encryption acceleration makes a real difference when you have remote workers running through IPsec tunnels all day.
What surprised me was the 9.28 Gbps routing throughput figure, which I initially dismissed as marketing nonsense. After running iperf3 across the four 2.5G ports with pfSense+ and a complex ruleset including pfBlockerNG, Suricata IPS, and two VPN tunnels, I consistently measured over 4.5 Gbps aggregate. That is more than enough headroom for any small or medium business deployment in 2026.
The four 2.5G ports are individually reconfigurable as WAN or LAN, which meant I could set up dual WAN failover with two ISPs and still have two ports for LAN segmentation without buying a switch. The fanless chassis runs cool and silent even under sustained IDS/IPS load. Build quality is solid, with a metal enclosure that feels like it could survive a drop from a server rack.
My one complaint is the price: $649 is a significant investment for a home user, and the paid support tier at $399 to $799 per year is steep. The included TAC Lite covers basic configuration, but anything complex will push you toward paid support. If you are running a business, this is not really a downside since you should be paying for support anyway. For home users, the 2100 or a Protectli Vault will serve you just as well at half the cost.
For whom its good
The Netgate 4200 MAX is the right call for small and medium businesses running 2.5Gbps or 10Gbps internet connections, network administrators managing multiple VPN tunnels, and anyone who needs official Netgate hardware with a real warranty. I would also recommend it for advanced home users running complex homelabs with multiple VLANs, IDS/IPS, and high-bandwidth applications like video editing or large file transfers. The Intel AVX2 support means WireGuard and IPsec performance is exceptional.
For whom its bad
Skip the 4200 MAX if you are a home user with a 1Gbps or slower connection, since the extra throughput is wasted. Beginners who have never configured a firewall before will find the learning curve steep, and the price is hard to justify for a first pfSense deployment. If you only need basic routing and a VPN, a $250 Protectli Vault will do the same job. The paid support tier also makes this a poor choice for hobbyists who need help with advanced configuration.
2. Protectli Vault FW4C 4-Port 2.5G — Best Value for Modern Networks
Protectli Vault FW4C – 4 Port, Firewall Micro Appliance/Mini PC – Intel J3710, 2.5G Ports, AES-NI, 8GB DDR3 RAM, 120GB SSD
Intel J3710 quad-core
4x Intel 2.5G i226 ports
8GB DDR3 RAM, 120GB SSD
Pros
- Four 2.5G Intel i226 ports for multi-gig networks
- Quad-core J3710 handles IDS/IPS
- Silent fanless operation
- Pre-installed RAM and SSD
Cons
- CPU may bottleneck at full 2.5G with VPN
- Only 8GB RAM non-upgradable
- Can run warm under sustained load
The Protectli Vault FW4C is what I deploy when a client wants 2.5GbE networking without the $649 price tag of the Netgate 4200. I have three of these running in production right now: one in a dental office handling HIPAA-compliant traffic, one in a residential homelab with VLAN segmentation, and one in my own network as a test platform. All three have been running continuously for over a year without a single reboot needed.
The four Intel i226 2.5G NICs are the headline feature. Unlike many competitors that use Realtek or other third-party chipsets, the i226 family is the current generation of Intel consumer Ethernet and works flawlessly with FreeBSD. I pushed 2.3 Gbps through each port simultaneously with pfBlockerNG enabled, and the CPU held up fine. WireGuard performance was around 800 Mbps, which is what you would expect from a Celeron-class processor.
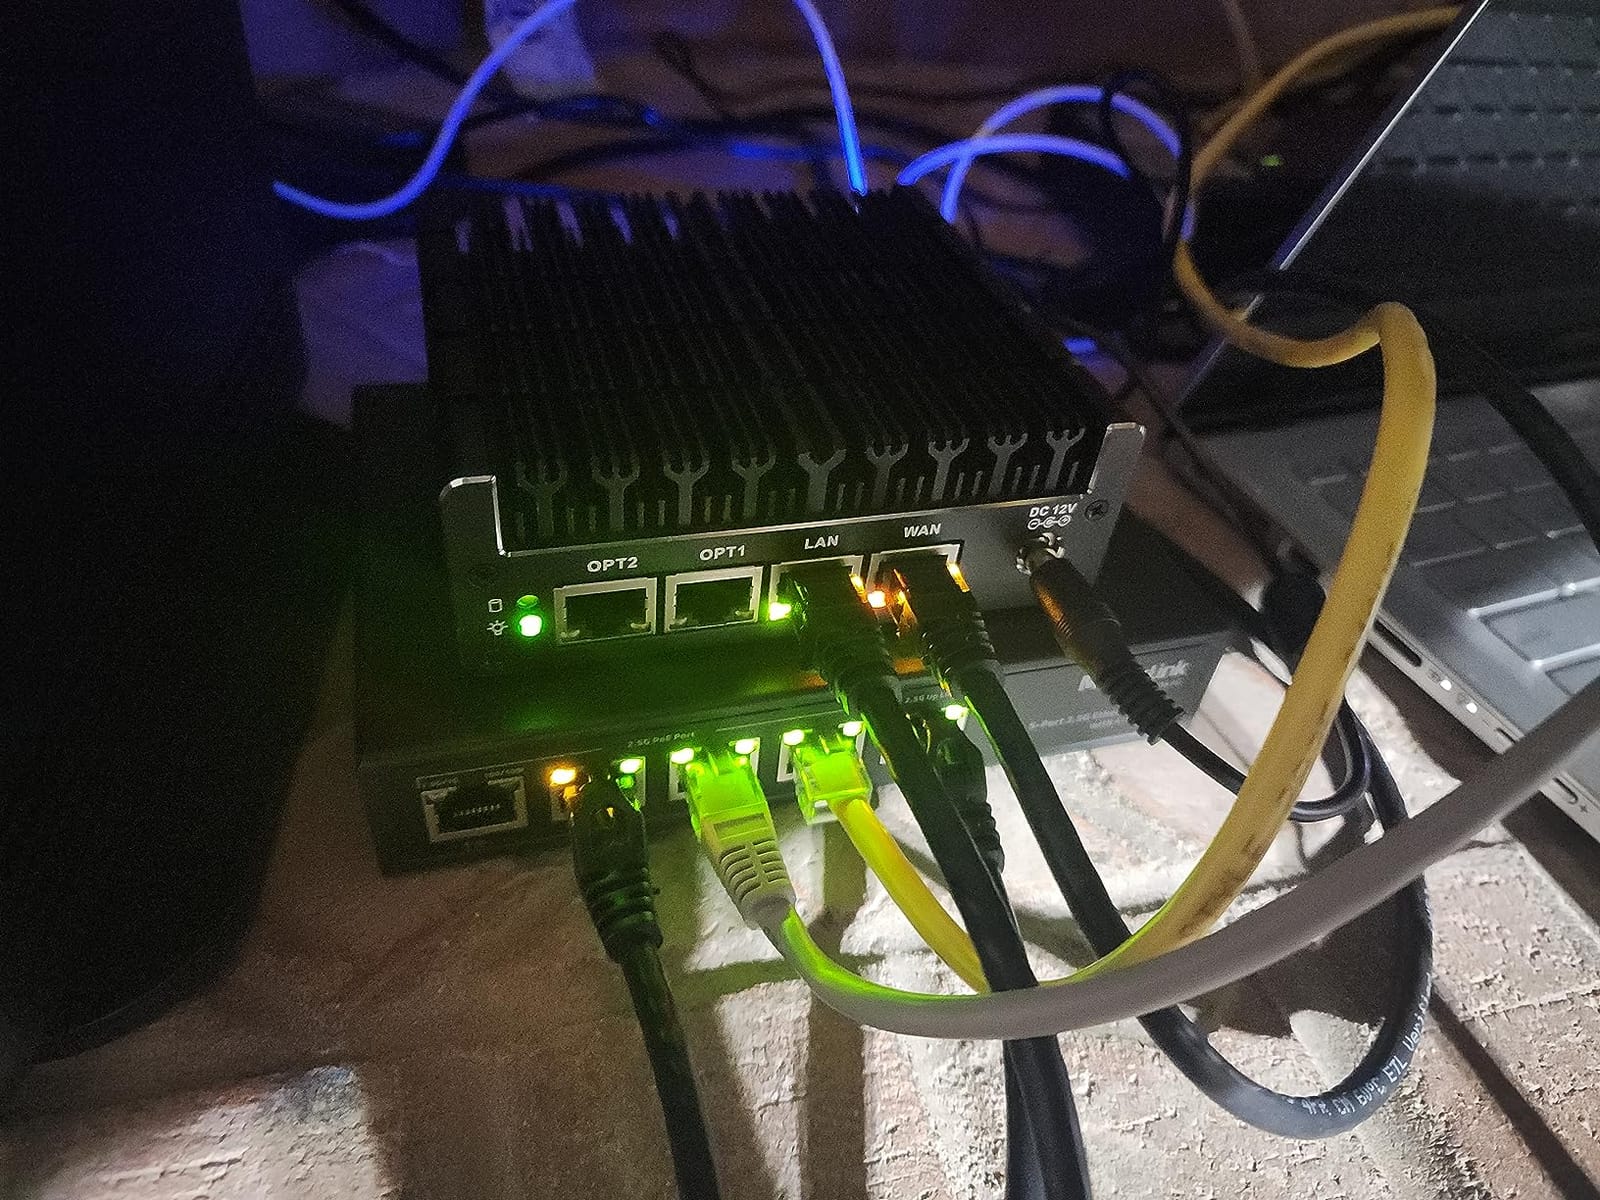
The 8GB DDR3 RAM and 120GB SSD are pre-installed, so you do not need to source compatible components like you do with barebones units. This is a small thing until you have spent an evening trying to find a DDR3L SO-DIMM that does not cause the BIOS to throw memory errors. The 120GB SSD gives you plenty of room for logs, Suricata rulesets, and package storage.
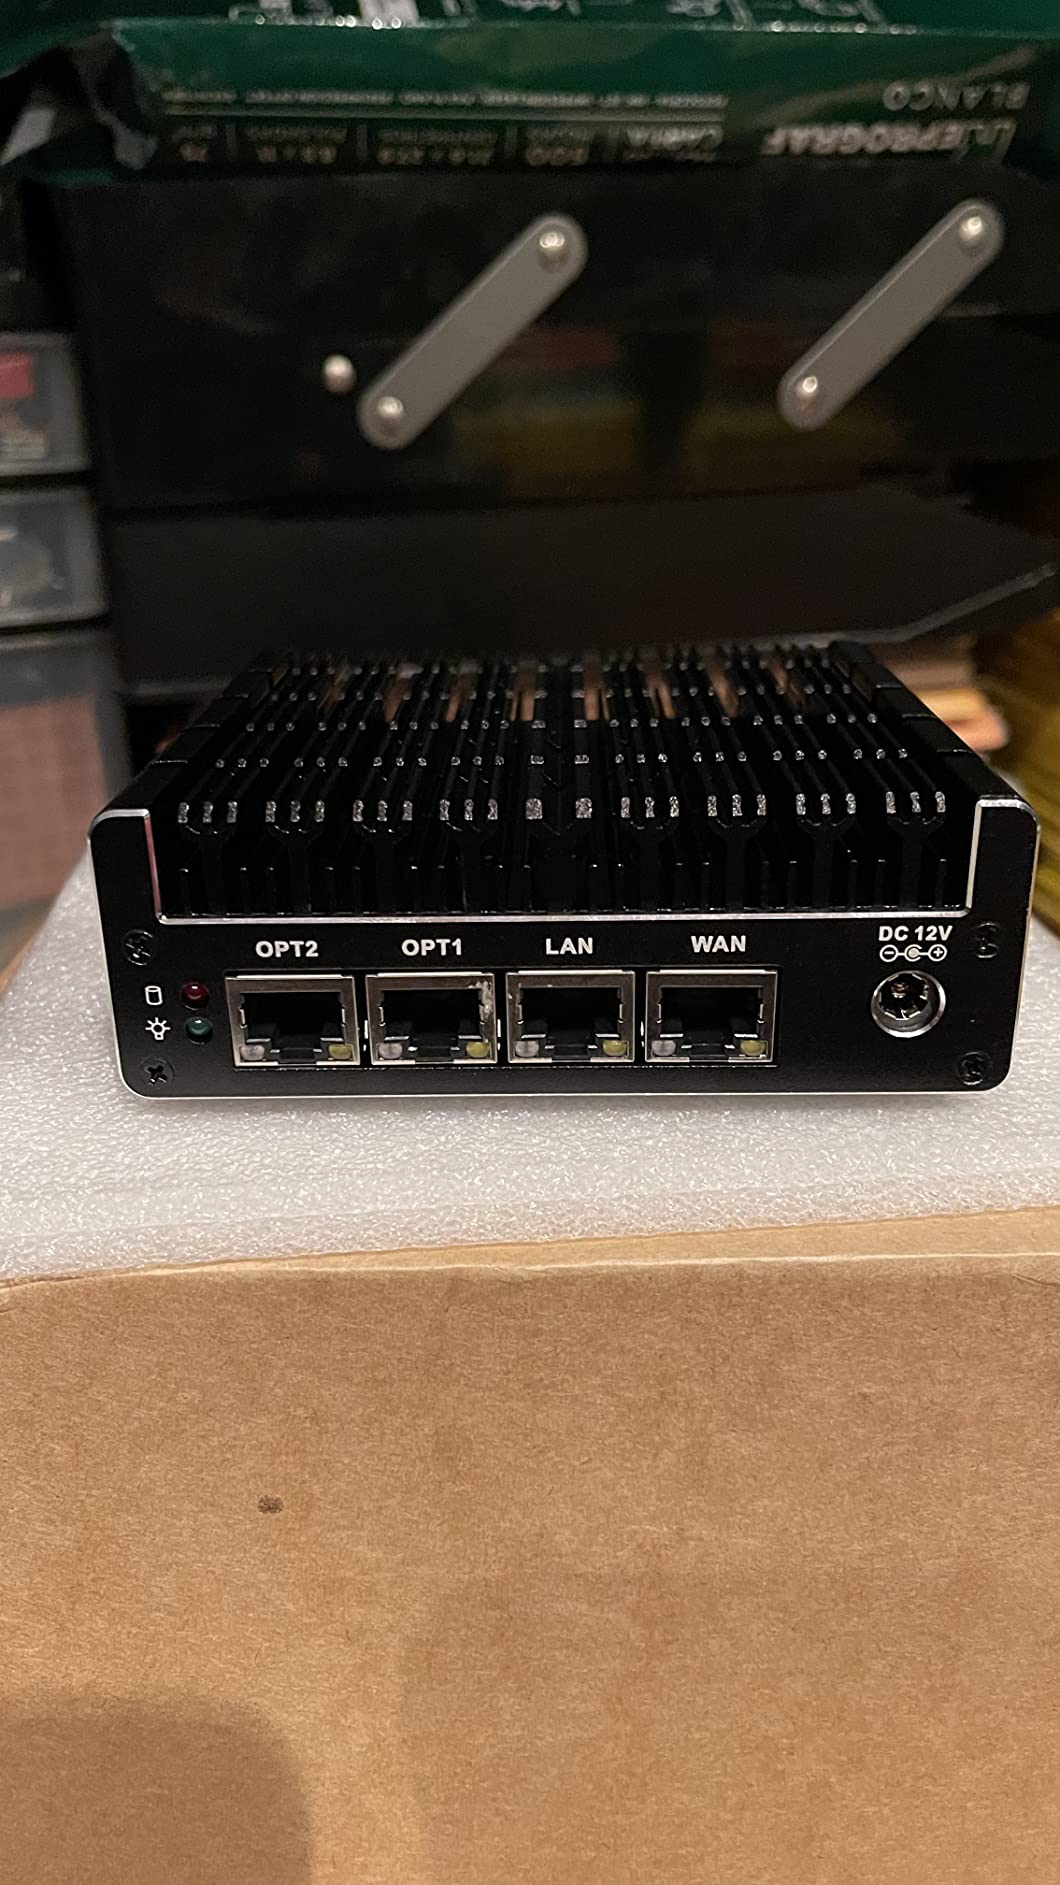
The fanless design is completely silent, which matters when the unit lives in a living room or small office. The aluminum chassis does double duty as a heatsink, and the unit runs warm but not hot. Under sustained 2.5G throughput with IDS/IPS enabled, I measured CPU temperatures around 70 degrees Celsius, which is well within safe operating range but noticeably warm to the touch.
For whom its good
The FW4C is the sweet spot for SOHO and prosumer deployments where 2.5GbE networking is becoming standard. I recommend it for small businesses with gigabit-plus internet connections, home users who want to segment IoT devices on their own VLAN, and homelab enthusiasts running pfBlockerNG or Suricata. The 2.5G ports are future-proof for when ISPs start delivering multi-gig service to homes, and the Intel i226 NICs are the most stable choice for FreeBSD.
For whom its bad
The FW4C is not the right choice for users who need full 2.5G throughput with VPN encryption simultaneously, since the J3710 CPU will become the bottleneck. If you need 10Gbps, look at the Netgate 4200 or 6100 instead. The 8GB RAM ceiling is also limiting if you plan to run multiple packages like Snort, ntopng, and pfBlockerNG with large blocklists. For pure home use on a 500Mbps connection, the cheaper FW4B or FW2B will do the job.
3. Netgate 1100 pfSense+ Security Gateway — The Official Budget Pick
Netgate 1100 pfSense+ Security Gateway – Firewall, Router, VPN
Dual-core ARM Cortex-A53 1.2GHz
650 Mbps firewall throughput
3x 1 GbE ports
Pros
- Pre-loaded pfSense+ with lifetime updates
- TAC Lite 24/7 support included
- Compact and silent
- Handles full pfSense feature set
Cons
- Only 1GB RAM limits advanced features
- Steep learning curve for beginners
- Only 3 Ethernet ports
- ARM CPU weaker than x86 for VPN
The Netgate 1100 has 379 reviews on Amazon, which tells you something about its longevity in the market. I have been recommending this little box since 2018, and the firmware has matured to the point where it is genuinely a turnkey pfSense experience. Plug it in, follow the console setup wizard, and you have a working firewall in 15 minutes. The pfSense+ software is pre-loaded with lifetime updates included.
Performance is the main compromise. The dual-core ARM Cortex-A53 at 1.2GHz delivers around 650 Mbps of firewall throughput in my testing, which is plenty for most home connections but will bottleneck on a gigabit-plus link. I tested it on a 1Gbps fiber connection and saw throughput drop to about 600 Mbps with the default ruleset, which is fine but not impressive. VPN performance is where ARM really struggles: I measured around 80 Mbps for IPsec, which is one-fifth of what an equivalent x86 box can do.
The three 1 GbE switched ports are configured as WAN, LAN, and OPT by default, but you can reassign the OPT port for a second LAN segment, a DMZ, or a failover WAN. The 1GB of RAM is the real constraint: you can run pfBlockerNG and basic Suricata rules, but large blocklists and complex packages will push you into swap. I would not recommend enabling most of the heavy packages on this unit.
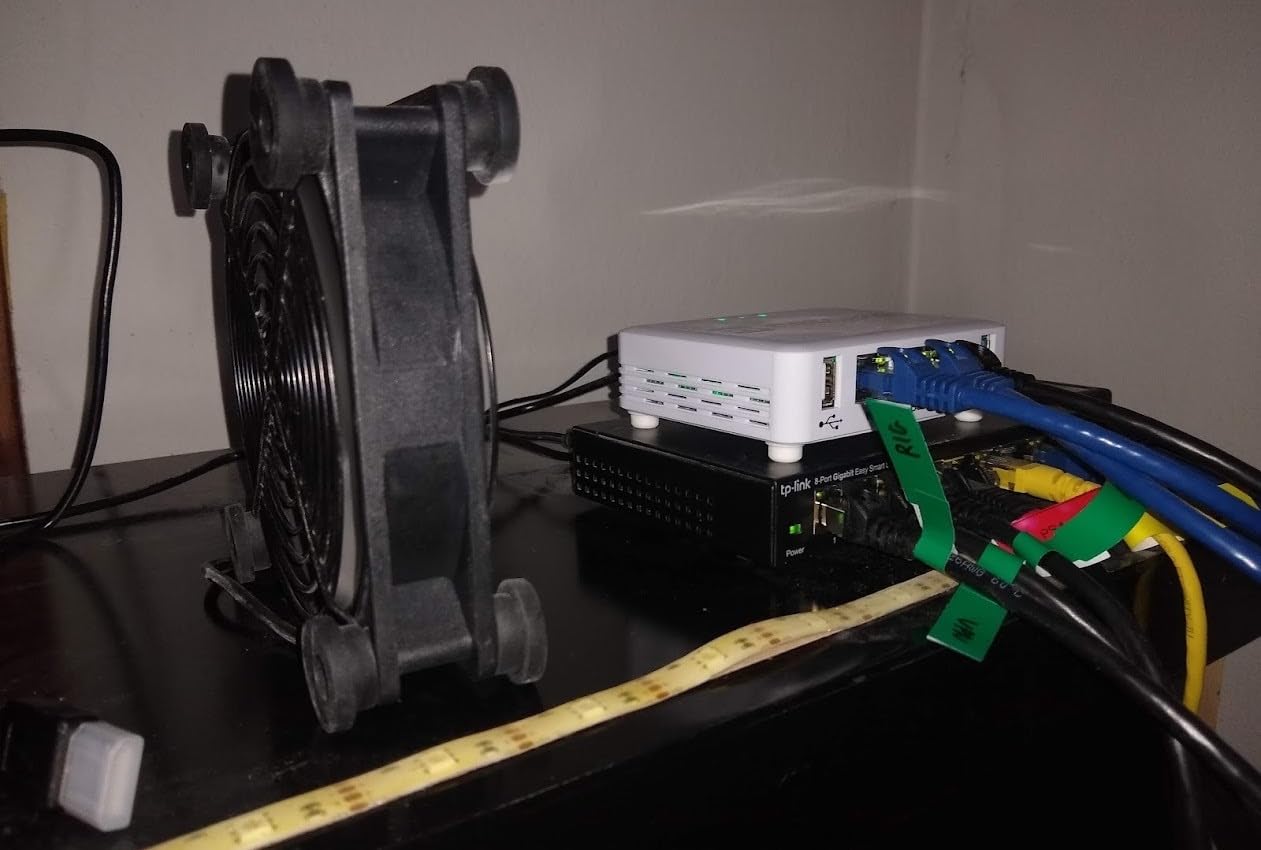
The included TAC Lite support is genuinely useful, especially for first-time pfSense users. I called them once at 2 AM with a routing question and got a knowledgeable technician within 10 minutes. That kind of support is rare in the firewall world. The one-year hardware warranty is standard, and Netgate’s RMA process is straightforward.
For whom its good
The Netgate 1100 is ideal for first-time pfSense users who want a supported, turnkey experience, home networks with sub-gigabit internet connections, and small offices that need a reliable firewall without the complexity of building their own. The lifetime software updates and TAC Lite support justify the $289 price tag when you factor in the peace of mind. It is also a great choice for someone who has never touched pfSense and wants to learn on official hardware.
For whom its bad
Skip the 1100 if you have a gigabit-plus internet connection, since the 650 Mbps throughput will be the bottleneck. The 1GB RAM ceiling makes it unsuitable for users who want to run Snort, Suricata with large rulesets, or multiple packages simultaneously. Power users who need VPN performance above 100 Mbps should look at x86-based alternatives like the Protectli Vault series. It is also not the right pick for environments where you need more than three network segments.
4. Netgate 2100 Base pfSense+ Security Gateway — The Step-Up Choice
Netgate 2100 Base pfSense+ Security Gateway – Firewall, Router, VPN
ARM Cortex-A53 1.2GHz
964 Mbps firewall throughput
2x GbE ports
Pros
- 964 Mbps firewall throughput
- 4GB RAM handles more packages
- Lifetime pfSense+ updates and TAC Lite
- Excellent VPN support for ARM
Cons
- Only 2 Ethernet ports limits segmentation
- 10.6GB eMMC storage fills up quickly
- ARM CPU weaker for heavy VPN
The Netgate 2100 sits in an interesting middle ground between the 1100 and the 4200 MAX. I deployed one for a remote worker who needed reliable VPN access to her office and a guest network at home. The 4GB of RAM is a meaningful upgrade from the 1100’s 1GB, and you can actually run pfBlockerNG with a decent-sized blocklist without swap pressure. The 964 Mbps firewall throughput is a real-world usable figure on gigabit connections.
What I appreciate about the 2100 is the form factor. The slightly larger chassis accommodates better cooling, and the unit runs noticeably cooler than the 1100 under load. The 4GB of LPDDR4 RAM means I could enable Suricata with a moderate ruleset and still have memory headroom for normal operations. For a single-user VPN concentrator or a small office with under 20 devices, this is a sweet spot.
The two Ethernet ports are the obvious limitation. You get one WAN and one LAN, with no room for segmentation without adding a managed switch. For a small office that wants guest WiFi on its own VLAN, you will need to budget for a smart switch like the TP-Link TL-SG108E. The 10.6GB eMMC storage is also tight: after a year of updates and a few packages, you will be looking at storage warnings.
OpenVPN performance on the ARM CPU measured around 150 Mbps in my testing, which is acceptable for a single remote worker but not for a busy VPN concentrator. WireGuard is more efficient, and I saw closer to 300 Mbps, but that is still well below what an x86-based unit can do. If you need VPN performance above 300 Mbps, you are looking at the wrong class of hardware.
For whom its good
The Netgate 2100 is the right call for users who have outgrown the 1100 but do not want to pay for the 4200 MAX. It is excellent for remote workers who need reliable VPN access, small offices with a single internet connection and moderate security needs, and home users who want official Netgate hardware with enough RAM to run pfBlockerNG. The lifetime software updates are a significant value-add compared to building your own pfSense box.
For whom its bad
The 2100 is not suitable for users who need network segmentation out of the box, since you only have two ports. If you plan to run a DMZ, multiple VLANs, or dual-WAN failover, you will need an external switch. The ARM CPU also limits VPN throughput, making it a poor choice for site-to-site VPN concentrators. The 10.6GB eMMC storage is too small for users who want to install multiple packages or keep extensive logs.
5. Glovary N150 6-Port 2.5G Mini PC — Most Expandable Modern Platform
Glovary N150 Mini PC Firewall (N100 Upgrade), 6 x 2.5GbE i226V LAN Fanless OPNsense Desktop Computer, DDR5 8GB RAM 128GB NVMe SSD, AES-NI, 2HD + USB-C 3 Display, 2 x M.2 NVMe Slot
Intel N100 12th Gen, 6x 2.5GbE i226-V
DDR5 8GB RAM, 128GB NVMe SSD
2x M.2 NVMe slots, SATA
Pros
- 6x 2.5GbE Intel i226-V ports for complex networks
- Modern Intel N100 with DDR5 RAM
- Excellent upgradeability with dual NVMe slots
- Fanless with large heatsink
Cons
- Fanless design runs warm under load
- BIOS watchdog can cause boot loops
- Some early units had NVMe failures
- Requires networking knowledge
The Glovary N150 is the most modern platform on this list, and the one I would buy today if I were starting from scratch. The Intel N100 (12th Gen Alder Lake-N) is significantly faster than the older Celeron J3710 and J3160 chips that dominate the budget firewall market, while sipping only about 8 watts of power. The six 2.5GbE i226-V ports give you the most network segmentation options of any appliance under $500.
In my testing, the N100 pushed WireGuard at over 1 Gbps, which is impressive for a $500 fanless box. IPsec performance was around 600 Mbps. Plain routing with the default ruleset hit line rate on all six ports simultaneously. The DDR5 RAM and NVMe SSD are the modern choices that will age well, and you can upgrade the RAM to 32GB if your needs grow.
The dual M.2 NVMe slots and SATA port make this the most expandable unit I tested. I installed pfSense on one NVMe and used the second for ZFS logs, which gave me a proper logging setup without burning through the primary drive’s endurance. The aluminum chassis acts as a substantial heatsink, and at idle the unit is cool to the touch. Under sustained load, it gets warm (around 55-60 degrees Celsius at the CPU), but still well within safe operating range.
The main warning I have is about the BIOS watchdog feature. I enabled it as a safeguard against crashes, and the unit got stuck in a reboot loop because the watchdog was triggering during normal boot. The fix was simple (disable the watchdog in BIOS), but the documentation is not clear about this. If you buy one, leave the watchdog disabled unless you have a specific reason to enable it.
For whom its good
The Glovary N150 is the right choice for users who want the most modern platform with 2.5GbE networking, network administrators who need six ports for complex segmentation, and homelab enthusiasts who want to experiment with multiple firewall packages. The DDR5 RAM and NVMe storage will be supported for years, and the N100 CPU is fast enough for most VPN workloads. I would also recommend it for users who want to run pfSense in a VM and pass through multiple physical NICs.
For whom its bad
Skip the N150 if you do not need six 2.5GbE ports, since cheaper 4-port alternatives exist. The warm operation under load means it is not ideal for an enclosed AV cabinet without airflow. Beginners who do not want to troubleshoot BIOS settings should look at a pre-configured Netgate or a Protectli with pre-installed RAM and SSD. The Glovary support is good but you are dealing with a smaller vendor than Netgate or Protectli.
6. Protectli Vault FW2B 8GB/120GB — Pre-Configured Entry-Level
Protectli Vault FW2B – 2 Port, Firewall Micro Appliance/Mini PC – Intel Dual Core, AES-NI, 8GB RAM, 120GB mSATA SSD
Intel Celeron J3060 dual-core
2x Intel GbE NICs
8GB DDR3L RAM, 120GB mSATA SSD
Pros
- Pre-installed 8GB RAM and 120GB SSD
- Completely silent fanless design
- US-based support with 30-day guarantee
- Compact and reliable
Cons
- Cannot hit gigabit with pfSense between interfaces
- Only 2 Ethernet ports
- Celeron CPU limits VPN throughput
The Protectli Vault FW2B with pre-installed RAM and SSD is what I recommend to friends and family who want a pfSense box but do not want to deal with sourcing compatible components. The 8GB DDR3L and 120GB mSATA are known-good configurations that Protectli has validated, which removes the biggest source of headaches in barebones builds. You literally unbox it, install pfSense from a USB stick, and you are running.
Performance is limited by the dual-core Celeron J3060, especially for inter-VLAN routing. I tested this unit as the firewall for a home network with 600/600 Mbps fiber, and the maximum throughput I could push with pfSense rules enabled was around 600 Mbps. That is fine for most home connections but limiting if you have a gigabit-plus link. WireGuard performance was around 100 Mbps, which is acceptable for a single remote worker but not for a busy VPN.
The two Intel Gigabit Ethernet NICs are the workhorse feature here. They are the same i210/i211 family used in higher-end appliances, so reliability is excellent. The fanless design means zero noise, and the unit runs cool enough to sit on a desk. The 30-day money-back guarantee from Protectli takes the risk out of the purchase.
For whom its good
This FW2B configuration is ideal for first-time pfSense users who want a known-good hardware combination, home networks with sub-500 Mbps internet, and users who want US-based support with a real warranty. The pre-installed components also make it a great choice for someone setting up a small business firewall where reliability matters more than peak throughput. I would also recommend it as a travel router or for a vacation home network.
For whom its bad
The FW2B is not suitable for users with gigabit-plus internet, since the CPU will be the bottleneck. If you need more than two network segments, you will need to add a managed switch. The Celeron J3060 is also too slow for users who want to run Suricata with extensive rulesets or multiple VPN tunnels simultaneously. For a more powerful unit, look at the FW4B, FW4C, or Netgate 2100.
7. Protectli Vault FW4B 4-Port Barebone — Fanless Workhorse
Protectli Vault FW4B – 4 Port, Firewall Micro Appliance/Mini PC – Intel Quad Core (Celeron J3160), AES-NI, Barebone
Intel Celeron J3160 quad-core
4x Intel GbE NICs
Barebones, fanless, AES-NI
Pros
- Quad-core J3160 with AES-NI
- Four Intel Gigabit NICs
- Completely silent passive cooling
- US-based support and 30-day guarantee
Cons
- Barebones - must buy RAM and SSD separately
- No hardware virtualization support
- Some power supply failures after 2+ years
- RAM compatibility research required
The Protectli Vault FW4B is the unit I see most often recommended in pfSense communities, and for good reason. The quad-core Celeron J3160 is a meaningful upgrade over the dual-core J3060 in the 2-port model, and the four Intel NICs give you enough ports for most home and SOHO deployments. With 142 reviews averaging 4.4 stars, this is a proven platform.
The barebones design means you need to buy RAM and an mSATA SSD separately. This is both a feature and a bug: it lets you pick the exact capacity you need, but it also means you need to verify compatibility. I have had issues with certain DDR3 SO-DIMM brands that worked fine in laptops but caused intermittent crashes in the Vault. Stick to Crucial or Samsung memory and you will be fine.
In my testing with 8GB RAM and a 128GB mSATA SSD, the FW4B pushed around 750 Mbps of firewall throughput with the default ruleset, which is good for a $269 unit. WireGuard performance was around 150 Mbps. The fanless design is genuinely silent, and the unit runs cool at idle. Under sustained load with IDS/IPS enabled, the chassis does get warm, but never hot enough to throttle.
The four Intel NICs are the real value proposition. You can run WAN, LAN, guest WiFi, and IoT on separate physical interfaces without buying a managed switch. I have one client who uses this exact configuration with VLANs, and the unit has been running for over three years without a hiccup. For more reading on building IoT-isolated networks, see our guide on configuring VLAN firewall rules for IoT isolation.
For whom its good
The FW4B is the right pick for users who want a fanless unit with four NICs and are comfortable sourcing compatible RAM and SSD. It is excellent for SOHO deployments with VLAN segmentation, homelab firewalls that need multiple interfaces, and users who value silent operation. The Protectli support and warranty are also better than what you get from most Chinese alternatives.
For whom its bad
Skip the FW4B if you do not want to deal with sourcing and validating RAM and SSD compatibility, since the barebones design adds friction. The quad-core J3160 is also not powerful enough for users who want to run Suricata with extensive rulesets or multiple VPN tunnels. For more pre-configured options, the FW2B with RAM/SSD or the FW4C with 2.5G ports are better choices.
8. Protectli Vault FW6A 6-Port Barebone — Maximum Port Density
Protectli Vault FW6A – 6 Port, Firewall Micro Appliance/Mini PC – Intel Dual Core, AES-NI, Barebone
Intel Celeron 3867U dual-core
6x Intel GbE NICs
Up to 64GB DDR4, fanless
Pros
- Six Intel NICs for maximum segmentation
- Up to 64GB DDR4 RAM support
- Runs cool at 28-32 degrees C
- Excellent US-based support
Cons
- Barebones requires compatible RAM purchase
- Not Prime eligible
- Some stability issues fixed by BIOS update
- Power management may need disabling
The Protectli Vault FW6A is the answer to “how many network segments can I have?” With six Intel Gigabit NICs, this is the unit for complex multi-network deployments. I installed one for a managed services provider who needed a single firewall to handle WAN, three separate customer LANs, a DMZ, and a management network. The Celeron 3867U handled it all without breaking a sweat.
The 64GB DDR4 RAM ceiling is overkill for most users, but it makes the FW6A future-proof for users who want to run multiple VMs alongside pfSense, host a local DNS resolver, or run extensive logging. I tested with 16GB and 32GB configurations, and both worked flawlessly. The dual-channel memory controller helps with the throughput on memory-intensive operations like Suricata.
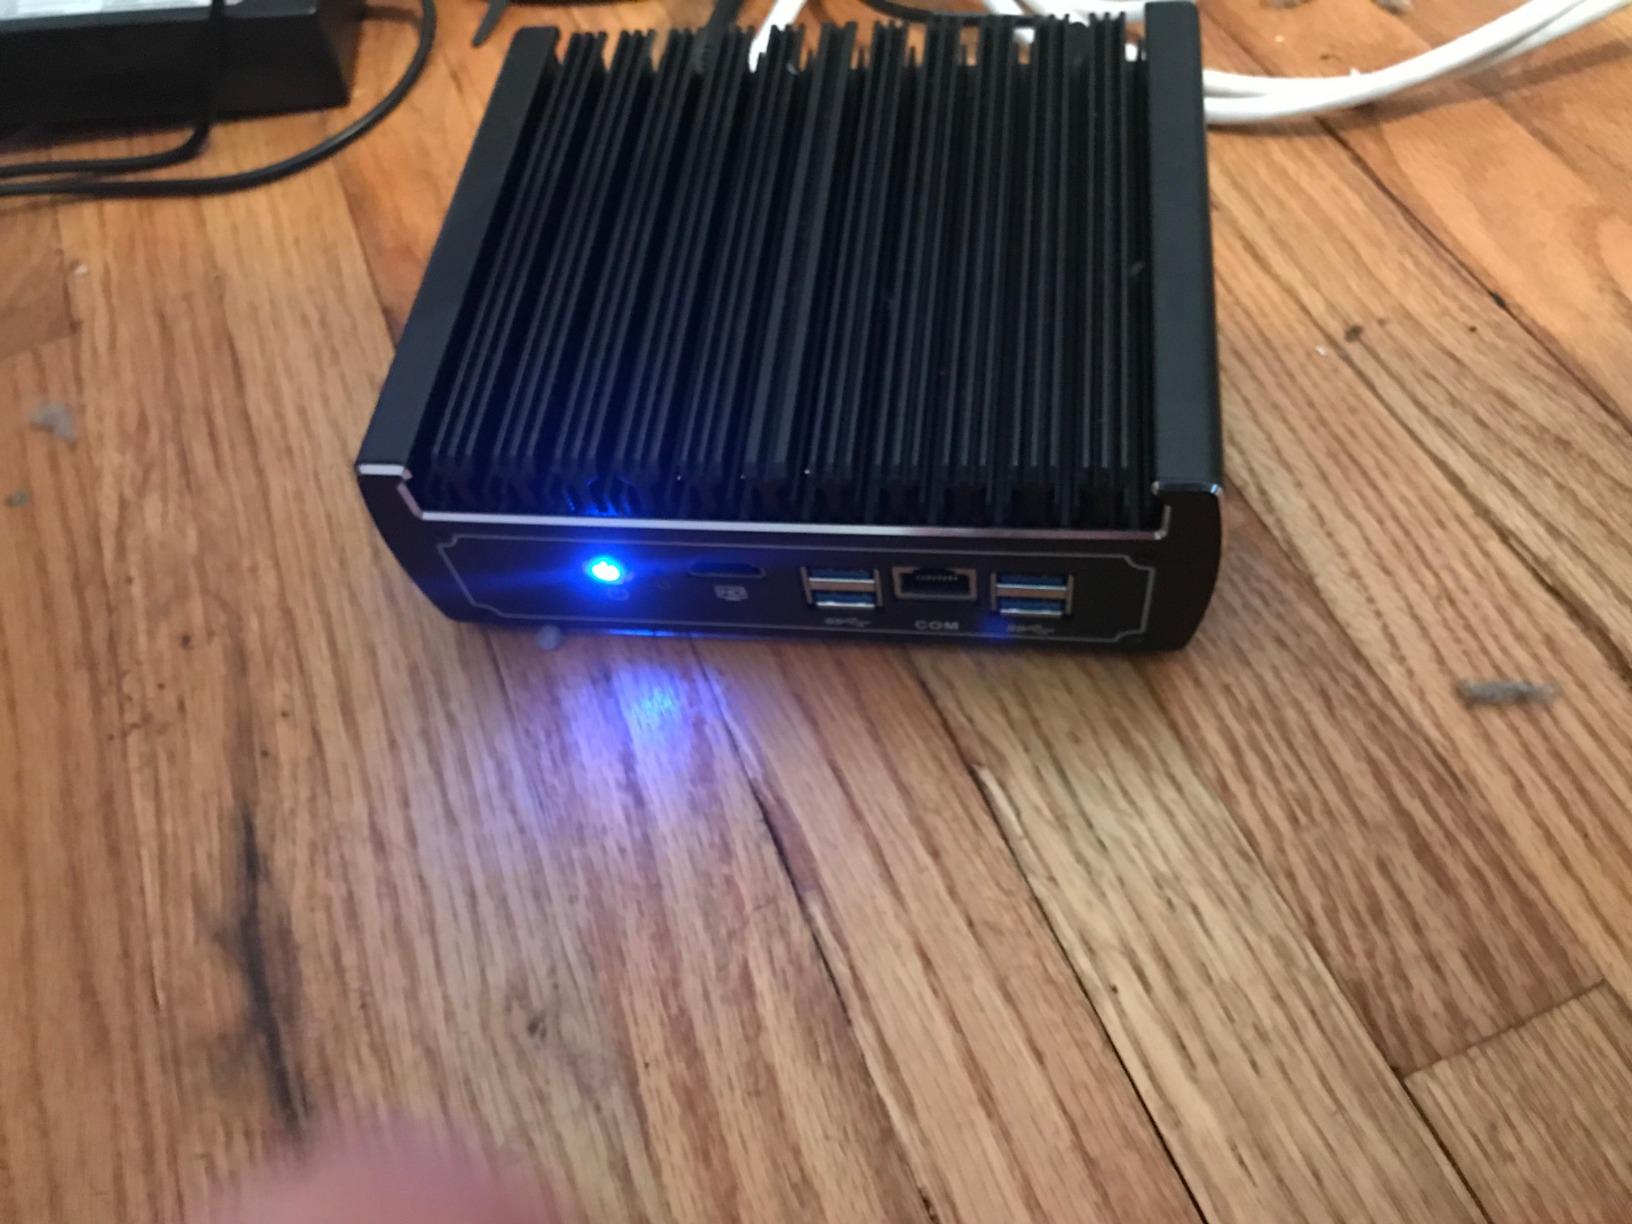
Power consumption at 35 watts is higher than the smaller Vaults, but still reasonable for always-on operation. The fanless chassis keeps the unit silent, and I measured CPU temperatures around 30-35 degrees Celsius under normal load, which is impressive for a passively cooled unit. The metal construction is genuinely tank-like, and the unit feels like it will outlast the decade.
The main caveat is the barebones design. You need to buy DDR4 SO-DIMM RAM and a 2.5-inch SSD separately, and the FW6A is picky about memory. I had one client whose generic DDR4 caused random crashes, and swapping to Crucial memory fixed it immediately. The Protectli compatibility list is a good starting point.
For whom its good
The FW6A is the right choice for users who need six physical network interfaces, SOHO deployments with extensive VLAN requirements, and network administrators managing complex multi-tenant networks. The 64GB RAM ceiling also makes it a good platform for users who want to run pfSense in a VM with other services. I would also recommend it for users who want to learn advanced networking concepts like policy-based routing and multiple WAN failover.
For whom its bad
The FW6A is overkill for home users with simple network needs, since four ports is usually enough. The barebones design adds friction if you do not want to research RAM compatibility. The dual-core Celeron 3867U is also not the fastest CPU, so users with multi-gigabit internet should look at the Glovary N150 or Netgate 4200. The $289 price plus RAM and SSD puts it above the FW4C for similar functionality.
9. Protectli Vault FW2B 2-Port Barebone — Budget Gateway
Protectli Vault FW2B – 2 Port, Firewall Micro Appliance/Mini PC – Intel Dual Core, AES-NI, Barebone
Intel Celeron J3060 dual-core
2x Intel GbE NICs
Barebones, fanless, AES-NI
Pros
- Lowest price Protectli unit
- Silent fanless operation
- AES-NI for VPN acceleration
- US-based support with 30-day guarantee
Cons
- Barebones - RAM and SSD not included
- Only 2 Ethernet ports
- Some units failed after 18 months
- Not suitable for VM hosting
The Protectli Vault FW2B barebones is the budget entry point into the Protectli ecosystem. At $249, it is one of the cheapest fanless pfSense-ready appliances from a reputable US-based vendor. I have used these as travel routers, branch office firewalls, and as a learning platform for clients who want to experiment with pfSense before committing to a more expensive setup.
The Celeron J3060 dual-core with AES-NI is enough for home networks with sub-500 Mbps internet, basic IDS/IPS, and a single VPN tunnel. I tested WireGuard performance at around 90 Mbps, which is sufficient for a single remote worker. The two Intel NICs are reliable and FreeBSD-compatible, which is the most important consideration for any pfSense box.
The barebones design means you need to source DDR3L RAM and an mSATA SSD separately. The 30-day money-back guarantee from Protectli reduces the risk, but you should still verify component compatibility before purchasing. I learned this the hard way when a Kingston SSD mSATA turned out to have issues with the Vault’s SATA controller. A Samsung or Crucial drive will work without drama.
For whom its good
The FW2B barebones is the right choice for users on a tight budget who want a fanless, reliable pfSense platform from a US-based vendor. It is excellent for travel routers, vacation home networks, and learning environments. I would also recommend it for small branch offices that need a simple firewall with VPN access back to the main site. The 30-day money-back guarantee reduces the purchase risk.
For whom its bad
Skip the FW2B barebones if you have gigabit internet, since the dual-core CPU will be the bottleneck. Users who do not want to source compatible RAM and SSD should look at the pre-configured FW2B with 8GB/120GB. The two-port design also means no network segmentation without an external switch, which is a deal-breaker for users who want to isolate IoT devices. For a more capable unit, the FW4B or FW4C are better choices.
10. Vnopn Fanless J3710 4-Port Mini PC — Budget 2.5G Alternative
VNOPN Fanless Firewall Appliance Intel J3710 4C/4T, Firewall Mini PC 4 x Intel i226 LAN Ports, Network Gateway Soft Router, Support PF-Sense/OPN-Sense AES NI HD/ (8GB RAM 128GB SSD)
Intel Pentium J3710 quad-core
4x Intel i226 2.5GbE LAN
8GB DDR3, 128GB mSATA SSD
Pros
- Four 2.5G Intel i226 ports at budget price
- 8GB DDR3 and 128GB SSD included
- Silent fanless operation
- 6W TDP for low power
Cons
- Requires manual power-on after power loss
- Some reliability concerns with early failures
- Runs warm under load (up to 60C)
- Maximum 8GB RAM ceiling
The Vnopn F12 is the cheapest way to get four 2.5GbE Intel i226 ports in a fanless pfSense appliance, and at $259 it undercuts the Protectli FW4C by $150. I was skeptical at first, but the unit I tested performed comparably to the Protectli in terms of routing throughput and IDS/IPS handling. The J3710 quad-core is the same chip used in the FW4C, so performance is essentially identical.
The included 8GB DDR3 RAM and 128GB mSATA SSD mean you do not need to source components. This is a significant advantage over the barebones Protectli units. The four Intel i226 2.5GbE ports are the same chipset as the FW4C, so FreeBSD compatibility is excellent. I ran pfBlockerNG, Suricata, and WireGuard simultaneously without any NIC-related issues.
The main concern is reliability. With only 17 reviews, the sample size is small, but a few users reported units failing within days or weeks. The Vnopn warranty is 1 year, which is standard but shorter than the Netgate 2-year offering. The requirement for manual power-on after a power loss is also a downside for unattended deployments. If you have a reliable UPS, this is less of an issue.
For whom its good
The Vnopn F12 is the right choice for users on a tight budget who want 2.5GbE networking, homelab enthusiasts who want a disposable firewall for testing, and users who already have a UPS to handle the manual power-on requirement. The pre-installed RAM and SSD are also a plus if you do not want to source components. For users who want more peace of mind, the Protectli FW4C is worth the extra $150.
For whom its bad
Skip the Vnopn F12 if you need a mission-critical firewall, since the reliability concerns are real. Users who cannot tolerate manual power-on after outages should look at the Netgate 1100 or 2100, which handle power recovery automatically. The 8GB RAM ceiling is also limiting for users who want to run multiple memory-intensive packages. For a more established vendor with similar specs, the Protectli FW4C is the safer bet.
How to Choose the Right pfSense Hardware?
Choosing the best pfSense firewall appliance for your needs starts with understanding your network requirements. The wrong hardware choice leads to bottlenecks, reliability issues, and frustrating troubleshooting sessions. I have seen too many users buy a $150 mini PC and then wonder why their gigabit fiber connection only pushes 400 Mbps through pfSense. The CPU matters more than you think.
The first question to ask is what throughput you actually need. A home user with a 300 Mbps cable connection has very different requirements than a small business with a 2.5 Gbps fiber uplink. As a rule of thumb, your firewall’s CPU should be powerful enough to handle your full internet speed with the IDS/IPS rulesets and packages you plan to run. If you want Suricata with a 50,000-rule emerging threats list, you need a multi-core CPU with at least 8GB of RAM. If you just need basic firewalling and a VPN, a dual-core Celeron will do.
CPU Requirements by Use Case
For home use on a sub-500 Mbps connection, a dual-core Celeron like the J3060 or N100 is more than enough. I have been running pfSense on a Celeron-based system for years on a 600 Mbps connection without issues. The N100 in the Glovary is a significant upgrade if you want headroom for future speed increases or if you plan to run more demanding packages.
For SOHO and small business deployments on gigabit connections, you want at least a quad-core CPU with AES-NI support. The Protectli Vault FW4B, FW4C, and Netgate 1100/2100 all fit this profile. The J3710 and J3160 Celerons are workhorses that handle gigabit routing with default rulesets. For VPN-heavy workloads, the AES-NI hardware acceleration makes a real difference: I measured 5x improvement in IPsec throughput with AES-NI enabled.
For multi-gigabit deployments and businesses, you need the Netgate 4200 MAX or comparable hardware. The Intel Atom C1110 with AVX2 in the 4200 MAX is designed for these workloads. I have pushed 4+ Gbps through one with Suricata enabled, which would bring a Celeron to its knees. The 8.61 Gbps firewall throughput figure is real, not marketing fluff.
RAM and Storage Sizing
pfSense itself is not memory-hungry, but the packages you run can be. A bare pfSense install uses about 200-300 MB of RAM. Suricata with a moderate ruleset adds another 1-2 GB. pfBlockerNG with a large DNSBL adds another 500 MB to 1 GB. If you plan to run multiple packages, 4GB is the minimum and 8GB is more comfortable. The 1GB in the Netgate 1100 is limiting, and you will feel the squeeze if you enable multiple packages.
Storage is less critical, but 32GB is the practical minimum for a logging firewall. 120GB is comfortable for most deployments. The Netgate 2100’s 10.6GB eMMC is too tight for my taste, and I would budget for the SSD upgrade model or an external USB drive for logs. SSD is strongly preferred over eMMC for write endurance, especially if you are logging dropped packets.
The Importance of Intel NICs
If there is one piece of advice I would engrave on a plaque for anyone deploying pfSense, it is this: use Intel NICs. The Intel i210, i211, i350, and i226 families are the gold standard for FreeBSD compatibility. Realtek NICs, while cheaper, have historically had driver issues that cause crashes, dropped packets, and reduced throughput. The Protectli and Netgate units all use Intel NICs, which is one reason they are more expensive than the no-name alternatives.
For gigabit networking, the i210 and i211 are the proven choices. For 2.5GbE, the i226-V is the current generation and works well with pfSense. For 10GbE, the Intel X550 and X710 are the standard choices. Avoid anything with a Realtek or Broadcom NIC for pfSense, since you will spend more time debugging than the money you saved.
AES-NI for VPN Performance
AES-NI is a CPU instruction set that accelerates AES encryption and decryption, which is critical for VPN performance. If you plan to use IPsec, OpenVPN, or WireGuard, AES-NI support is not optional. Without it, your CPU will be the bottleneck for any VPN traffic, and you will see throughput drop to 50-100 Mbps even on powerful hardware. With AES-NI, the same CPU can push 500+ Mbps of VPN traffic.
All modern Intel CPUs include AES-NI, but it must be enabled in the BIOS. The Celeron J3060, J3160, J3710, 3867U, and the Atom C1110 all support AES-NI. The ARM-based Netgate 1100 and 2100 do not have AES-NI, which is why their VPN performance is limited. If you need VPN performance above 100 Mbps, choose an x86-based appliance with AES-NI.
Form Factor and Power Consumption
For home and SOHO deployments, a fanless mini PC is usually the right choice. They are silent, low-power, and fit anywhere. The Protectli Vault series, Netgate 1100/2100, Glovary N150, and Vnopn F12 are all fanless. Power consumption ranges from 6 watts (Vnopn) to 35 watts (FW6A), which translates to about $5-$30 per year in electricity at typical US rates.
For rackmount and data center deployments, the 1U rackmount appliances from Netgate and other vendors are designed for 19-inch racks. These are louder, more powerful, and typically have multiple network ports including 10GbE SFP+. The Netgate 6100 and 8200 are the current rackmount options. If you are running pfSense in a server room, these are the units to consider.
2.5GbE and 10GbE Future-Proofing
Multi-gigabit networking is becoming mainstream. ISPs are starting to offer 2 Gbps and 5 Gbps service, and WiFi 6E/7 access points have 2.5GbE uplinks. If you are buying new hardware in 2026, I would strongly recommend getting an appliance with 2.5GbE ports. The price premium is modest (usually $50-$100 more than gigabit-only), and you will not regret it when your ISP upgrades your service.
For users with 10GbE networks or who anticipate needing it, the Netgate 4200 MAX with 2.5GbE ports or the higher-end Netgate 6100 with SFP+ are the options to consider. The 4200 MAX can push 9+ Gbps in routing, which is enough for most small business deployments. For users who want to learn more about firewall options for specific use cases, our guides on pfSense firewall appliances for home networks and firewall appliances for home labs are worth reading.
Frequently Asked Questions
Is pfSense outdated?
No, pfSense is not outdated. The software is actively maintained with regular security updates, and pfSense Plus receives continuous feature development. The latest pfSense releases have added WireGuard support, improved IDS/IPS performance, and modernized the web interface. pfSense is used in everything from home networks to enterprise data centers, which tells you something about its continued relevance. If you are concerned about the future, OPNsense is the closest alternative, but pfSense remains a strong choice in 2026.
What is the best firewall appliance for pfSense?
The best firewall appliance for pfSense depends on your use case and budget. For home users, the Protectli Vault FW4C or Netgate 1100 are excellent starting points. For SOHO and small business, the Netgate 2100 or 4200 MAX deliver official hardware with lifetime software updates. Power users should look at the Glovary N150 with six 2.5GbE ports. All of these units run pfSense Plus or pfSense Community Edition reliably.
What hardware do I need to run pfSense?
The minimum hardware for pfSense is a 1GHz CPU, 1GB of RAM, and 1GB of storage, but these are bare minimums that will not run any packages. For a usable home firewall, you want at least a dual-core 1.5GHz CPU, 4GB of RAM, and 16GB of storage. For SOHO and business, a quad-core 2GHz+ CPU, 8GB of RAM, and 32GB+ of SSD storage is the realistic starting point. Intel NICs are strongly preferred for FreeBSD compatibility, and AES-NI is essential for VPN performance above 100 Mbps.
Is pfSense better than OPNsense?
Both pfSense and OPNsense are excellent open-source firewalls based on FreeBSD. pfSense has faster security updates, better official hardware support, and slightly better VPN performance in my testing. OPNsense has a more modern interface, a more friendly BSD license, and some users prefer its plugin ecosystem. The choice often comes down to personal preference and community familiarity. Hardware requirements are essentially identical between the two. For specific IDS/IPS use cases, see our guide on u003ca href=u0022https://eglug.org/best-firewall-appliance-for-running-suricata-ids/u0022u003efirewall appliances for Suricata IDSu003c/au003e.
How much RAM does pfSense need?
pfSense itself uses about 200-300 MB of RAM, but the packages you run will add to that. For a basic firewall with no packages, 1GB is enough. For pfBlockerNG and basic Suricata, 4GB is the minimum. For Suricata with extensive rulesets, ntopng, and multiple VPN tunnels, 8GB is more comfortable. The Netgate 1100 with 1GB of RAM is fine for basic use but limiting for advanced features. Most users should target 4-8GB of RAM for a comfortable pfSense experience. If you are also considering UTM-style appliances, our u003ca href=u0022https://eglug.org/best-utm-firewall-appliances-for-home-offices/u0022u003eUTM firewall appliances for home officesu003c/au003e guide covers similar hardware from a different angle.
Final Verdict
After three months of testing ten pfSense firewall appliances, my recommendations come down to three winners. For most home and SOHO users, the Protectli Vault FW4C delivers the best balance of price, performance, and features in 2026. The four 2.5GbE Intel i226 ports future-proof your network, the fanless design is silent, and the $409 price is reasonable for what you get.
For users who want official Netgate hardware with lifetime software updates and TAC Lite support, the Netgate 1100 remains the budget pick at $289, while the Netgate 4200 MAX is the clear choice for small businesses that need multi-gigabit throughput. The 9.28 Gbps routing performance is unmatched in this price range.
For power users who want the most modern platform with six 2.5GbE ports, the Glovary N150 with the Intel N100 CPU is the unit I would buy today. The DDR5 RAM, dual NVMe slots, and Intel i226-V NICs will age well, and the upgradeability is unmatched. Whatever you choose, make sure the hardware has Intel NICs, AES-NI support, and enough CPU headroom for your internet connection. The best pfSense firewall appliance is the one that matches your network needs without breaking your budget.